This document explains how to implement Monosign with Postiz, the open-source social media scheduling tool. It covers Single Sign-On. Postiz supports single sign-on through its Generic OAuth provider, which works with any OpenID Connect (OIDC) compatible identity provider. Before you continue, it is better to start with the Postiz documentation.
This configuration is done with the self-hosted Postiz container image (ghcr.io/gitroomhq/postiz-app:latest) running with the official Docker Compose file of Postiz. If your Postiz version or deployment type is different, please check the Postiz documentation.
Postiz supports OAuth 2.0 / OpenID Connect only. SAML is not available in Postiz.
Monofor has no responsibility to do Postiz configurations. If you need support please contact the Postiz community or your Postiz support provider.
📑 Instructions
This documentation contains 5 main steps for integration.
-
Creating an application on Monosign
-
Configuring the OIDC/OpenID settings on Monosign
-
Configuration Single Sign-On for Postiz
-
Assign a user to the Postiz application
-
Sign In Test
1- Creating an Application on Monosign
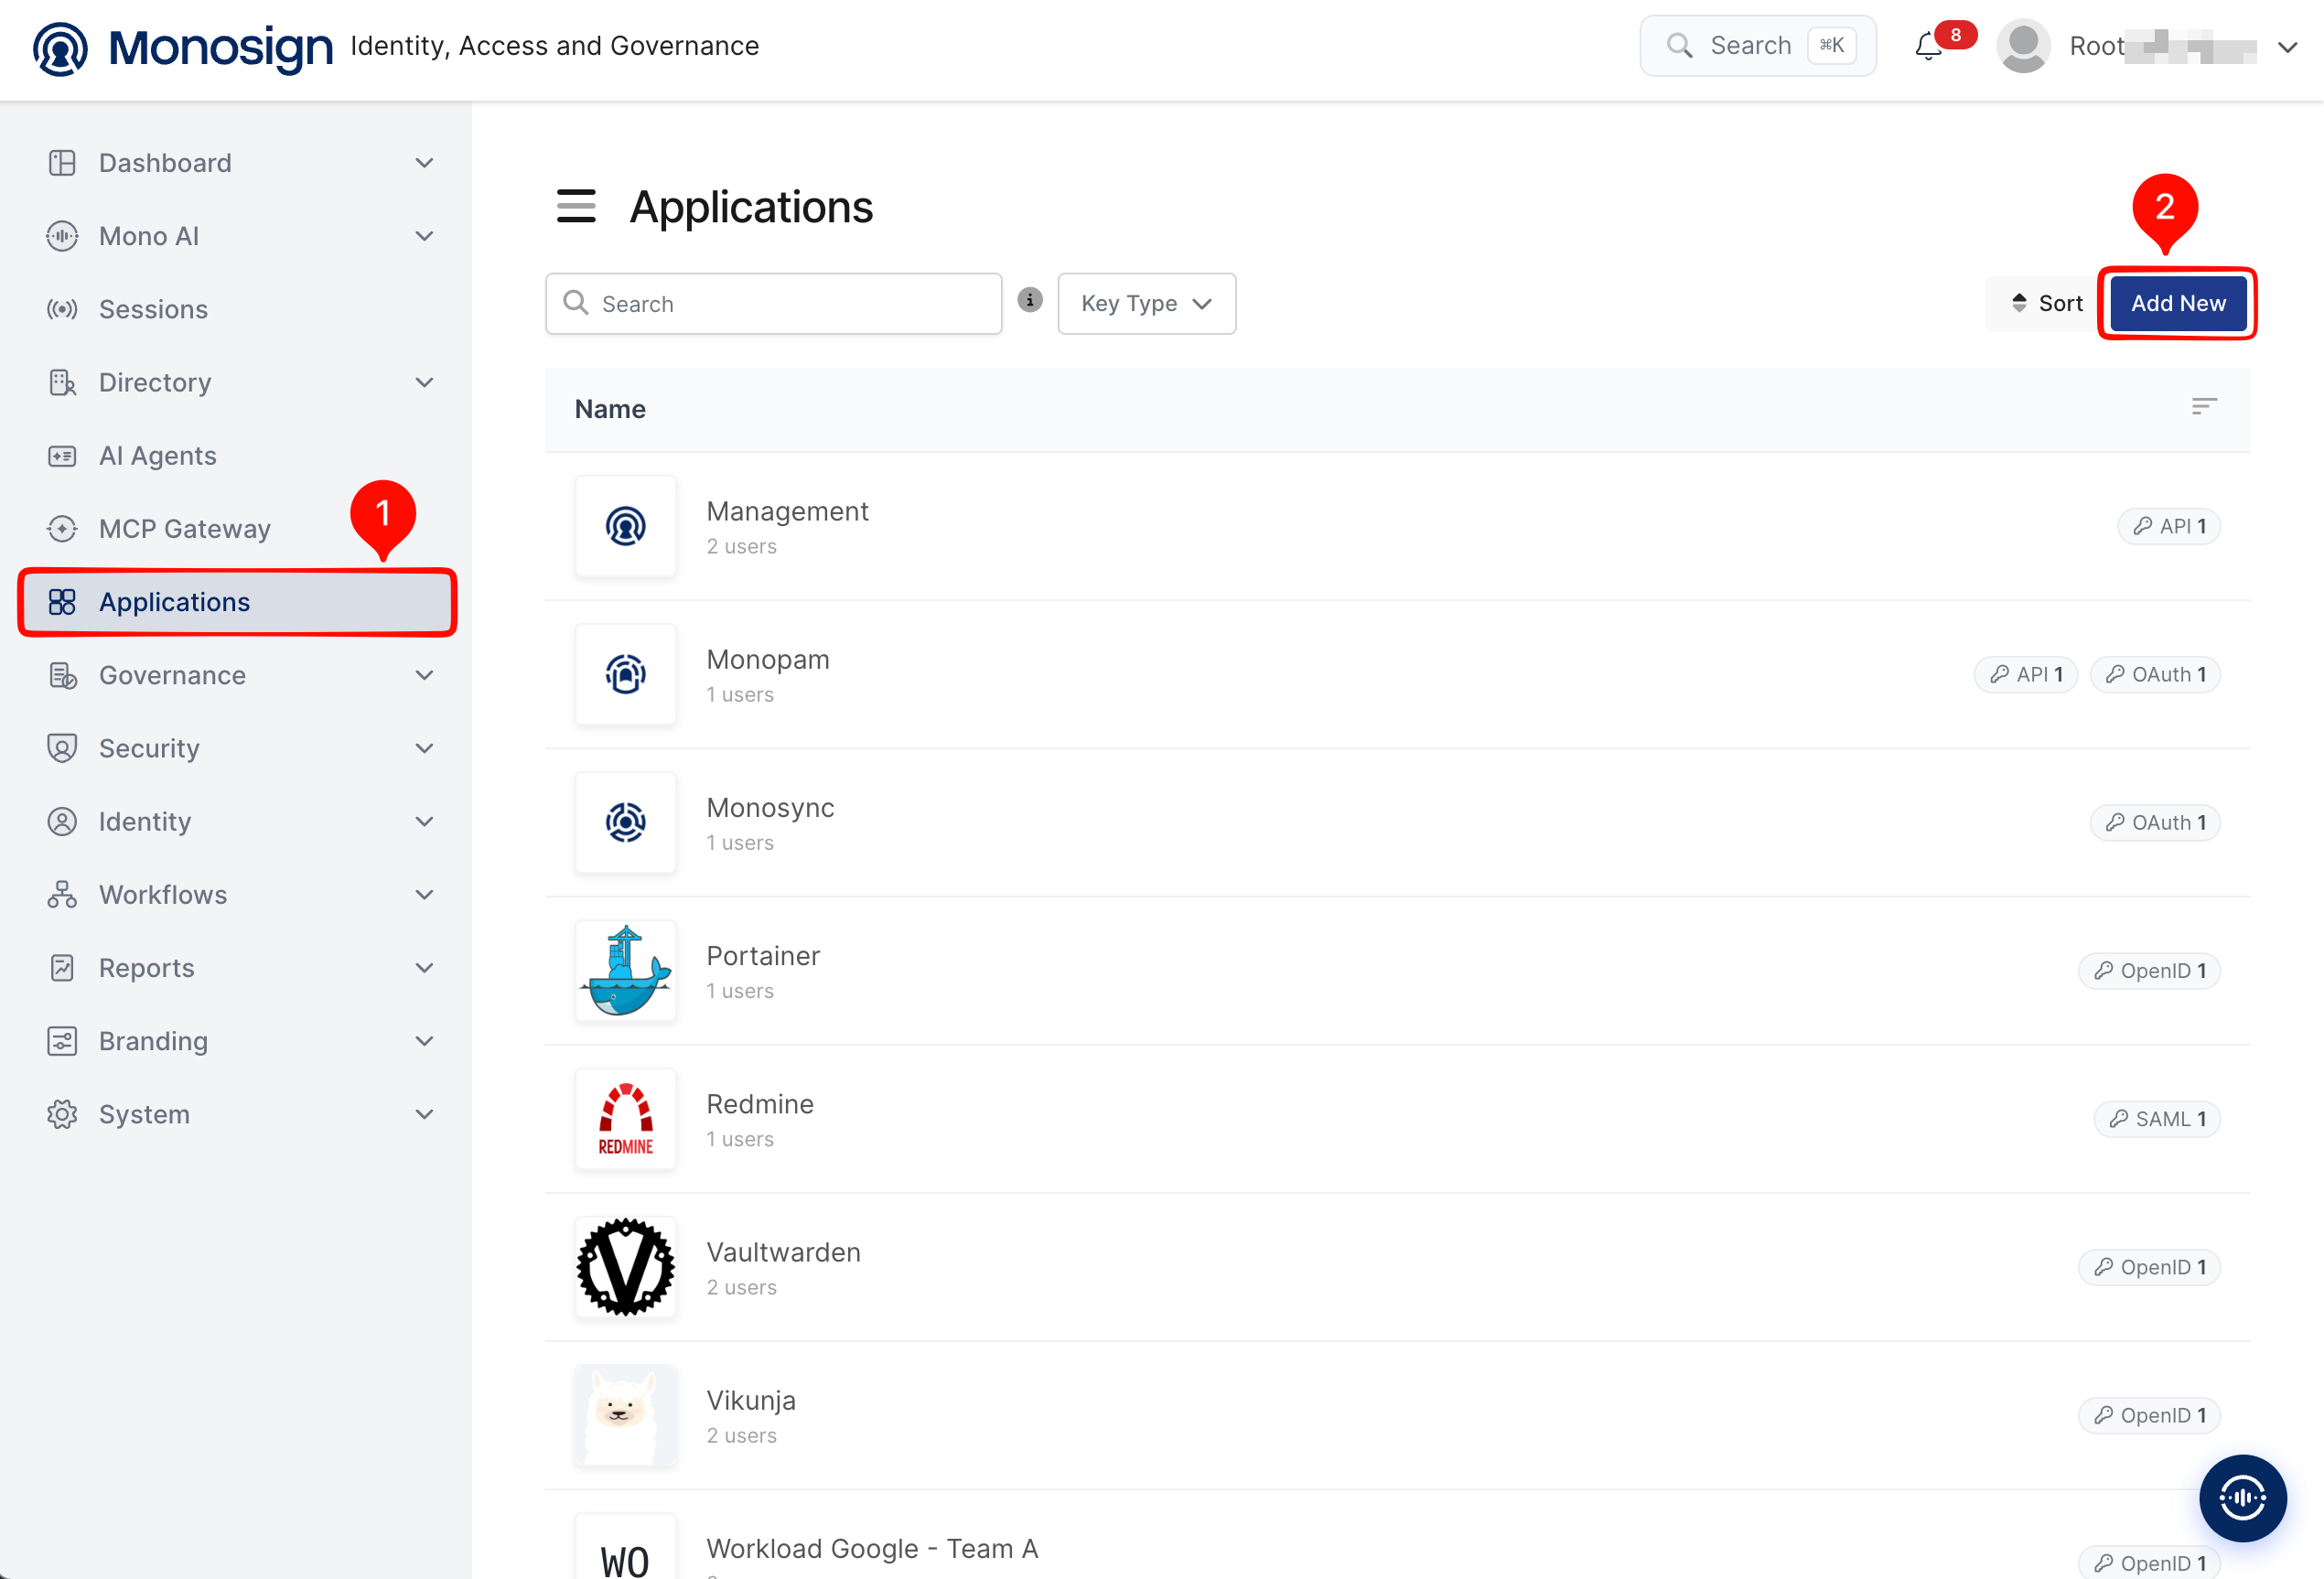
Create your application on Monosign first. Open the Applications page from the left menu and click Add New.
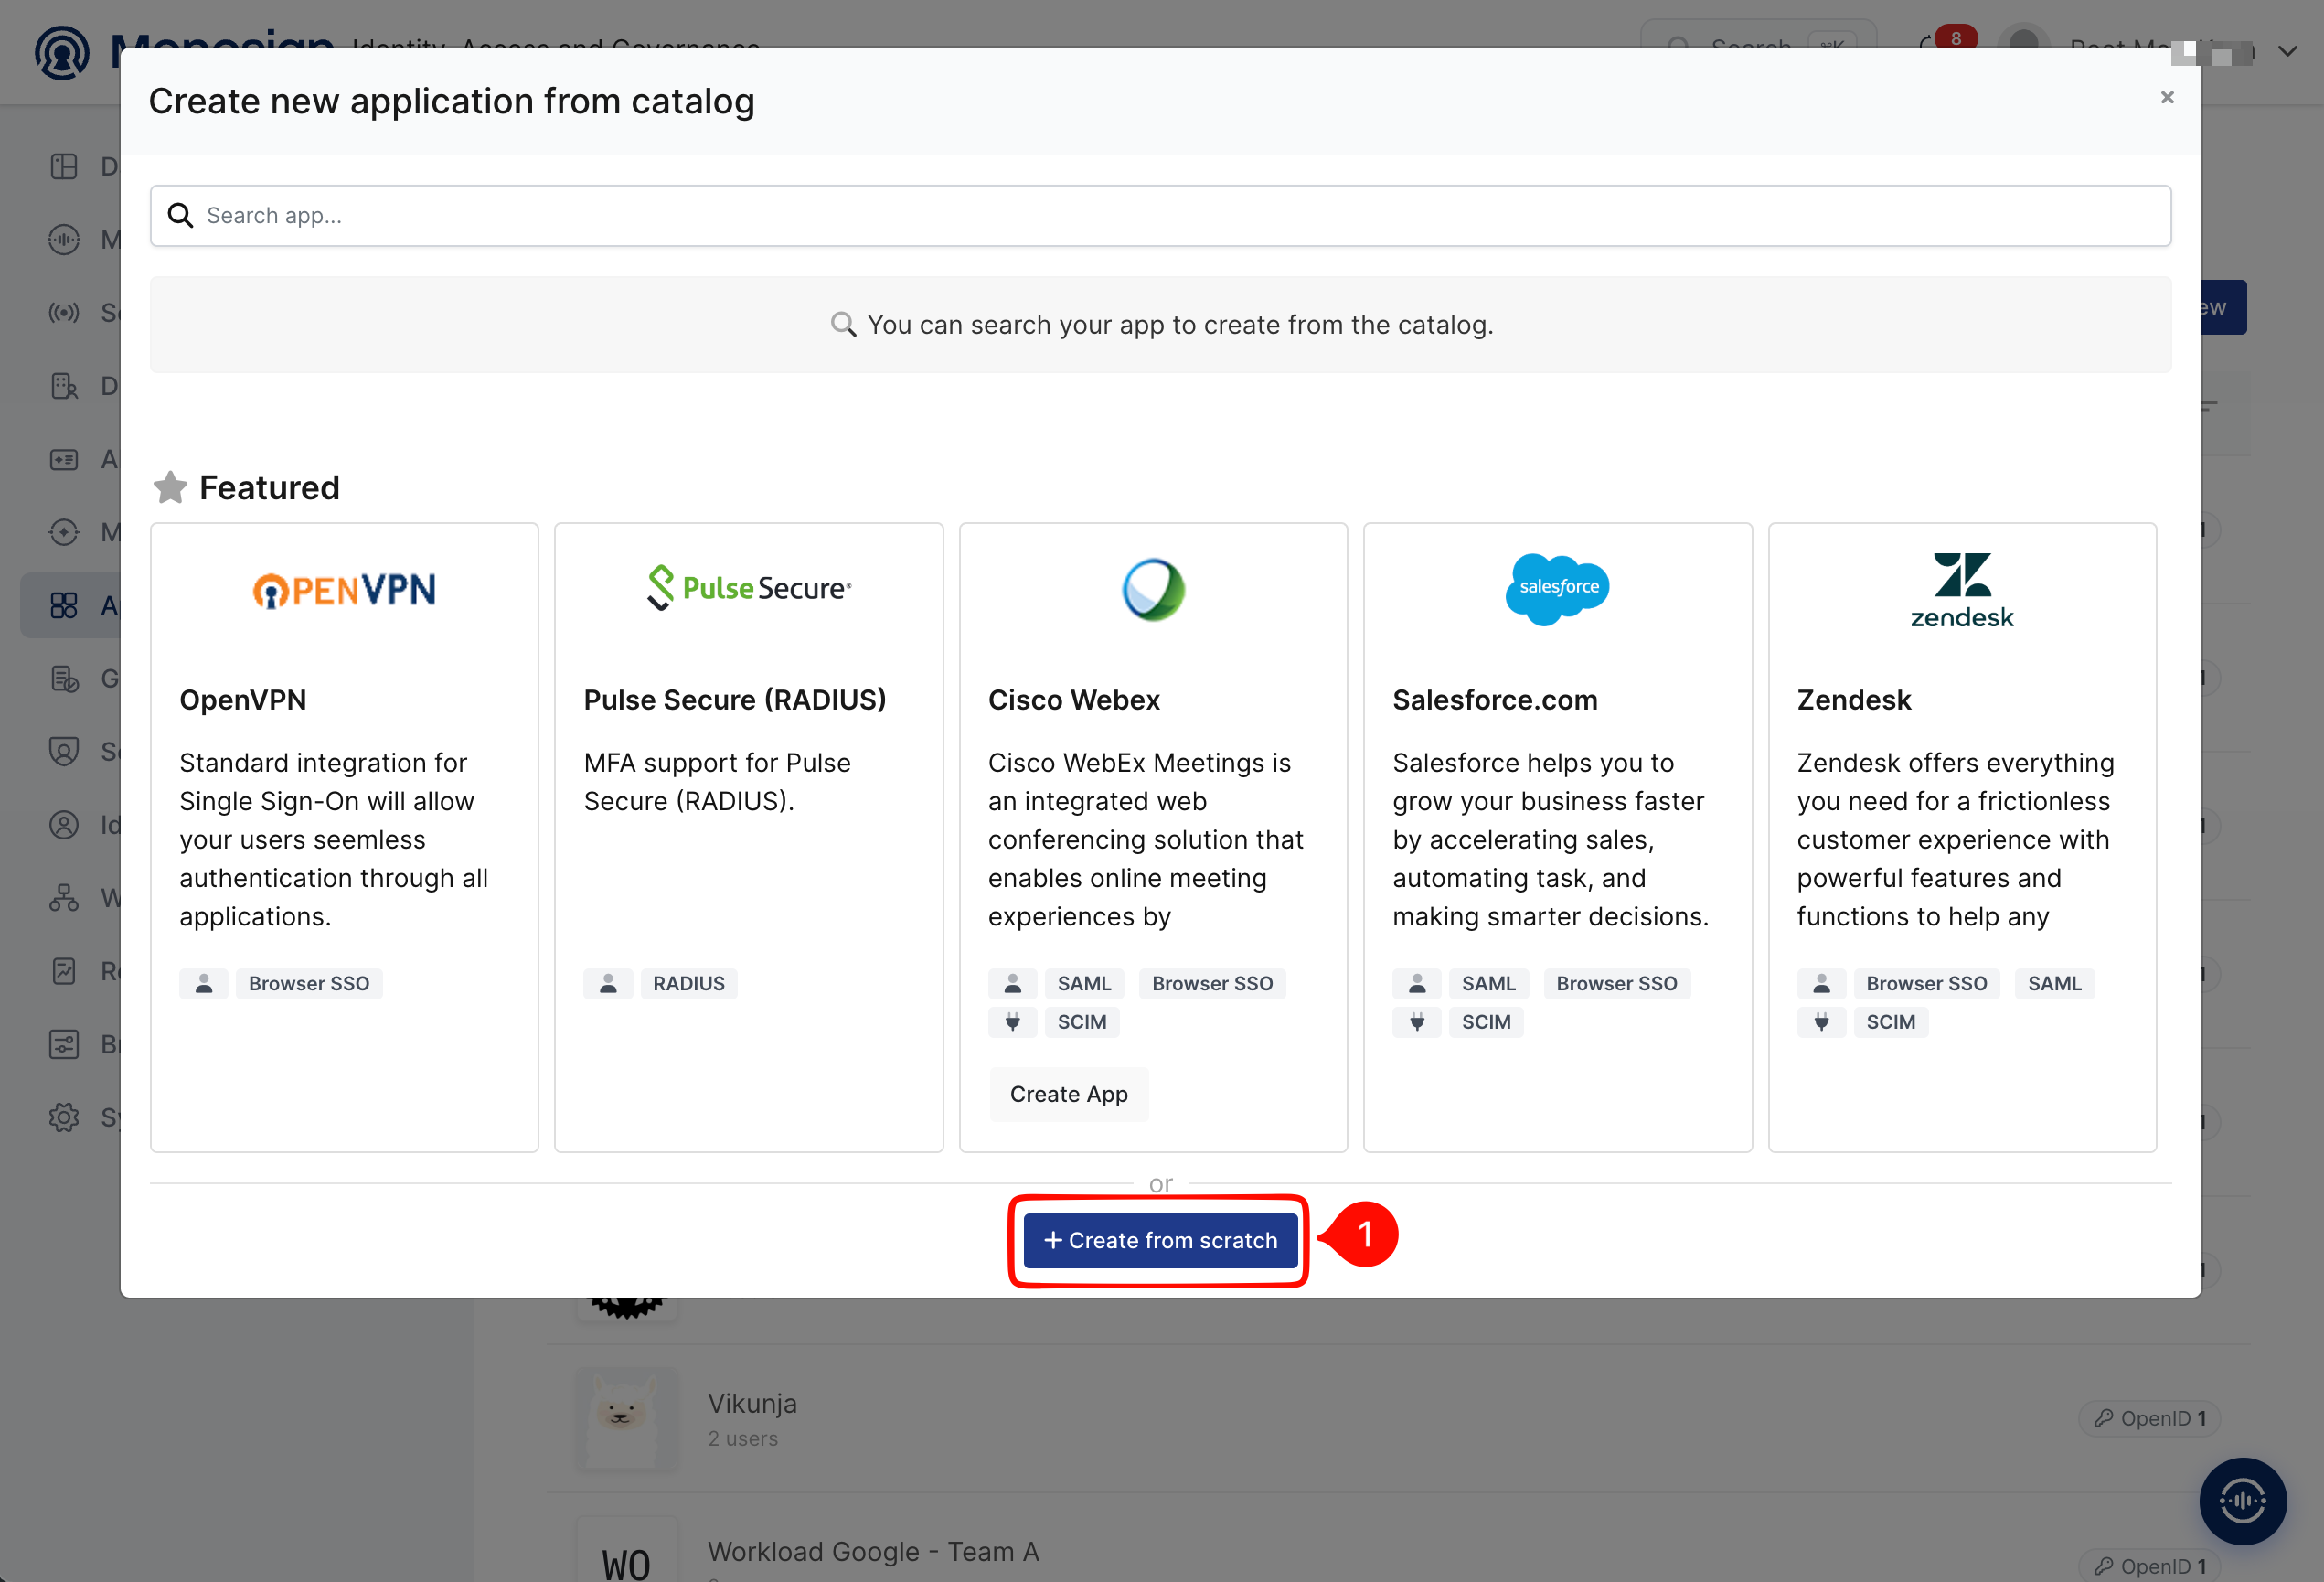
Postiz is not in the application catalog, so click Create from scratch.
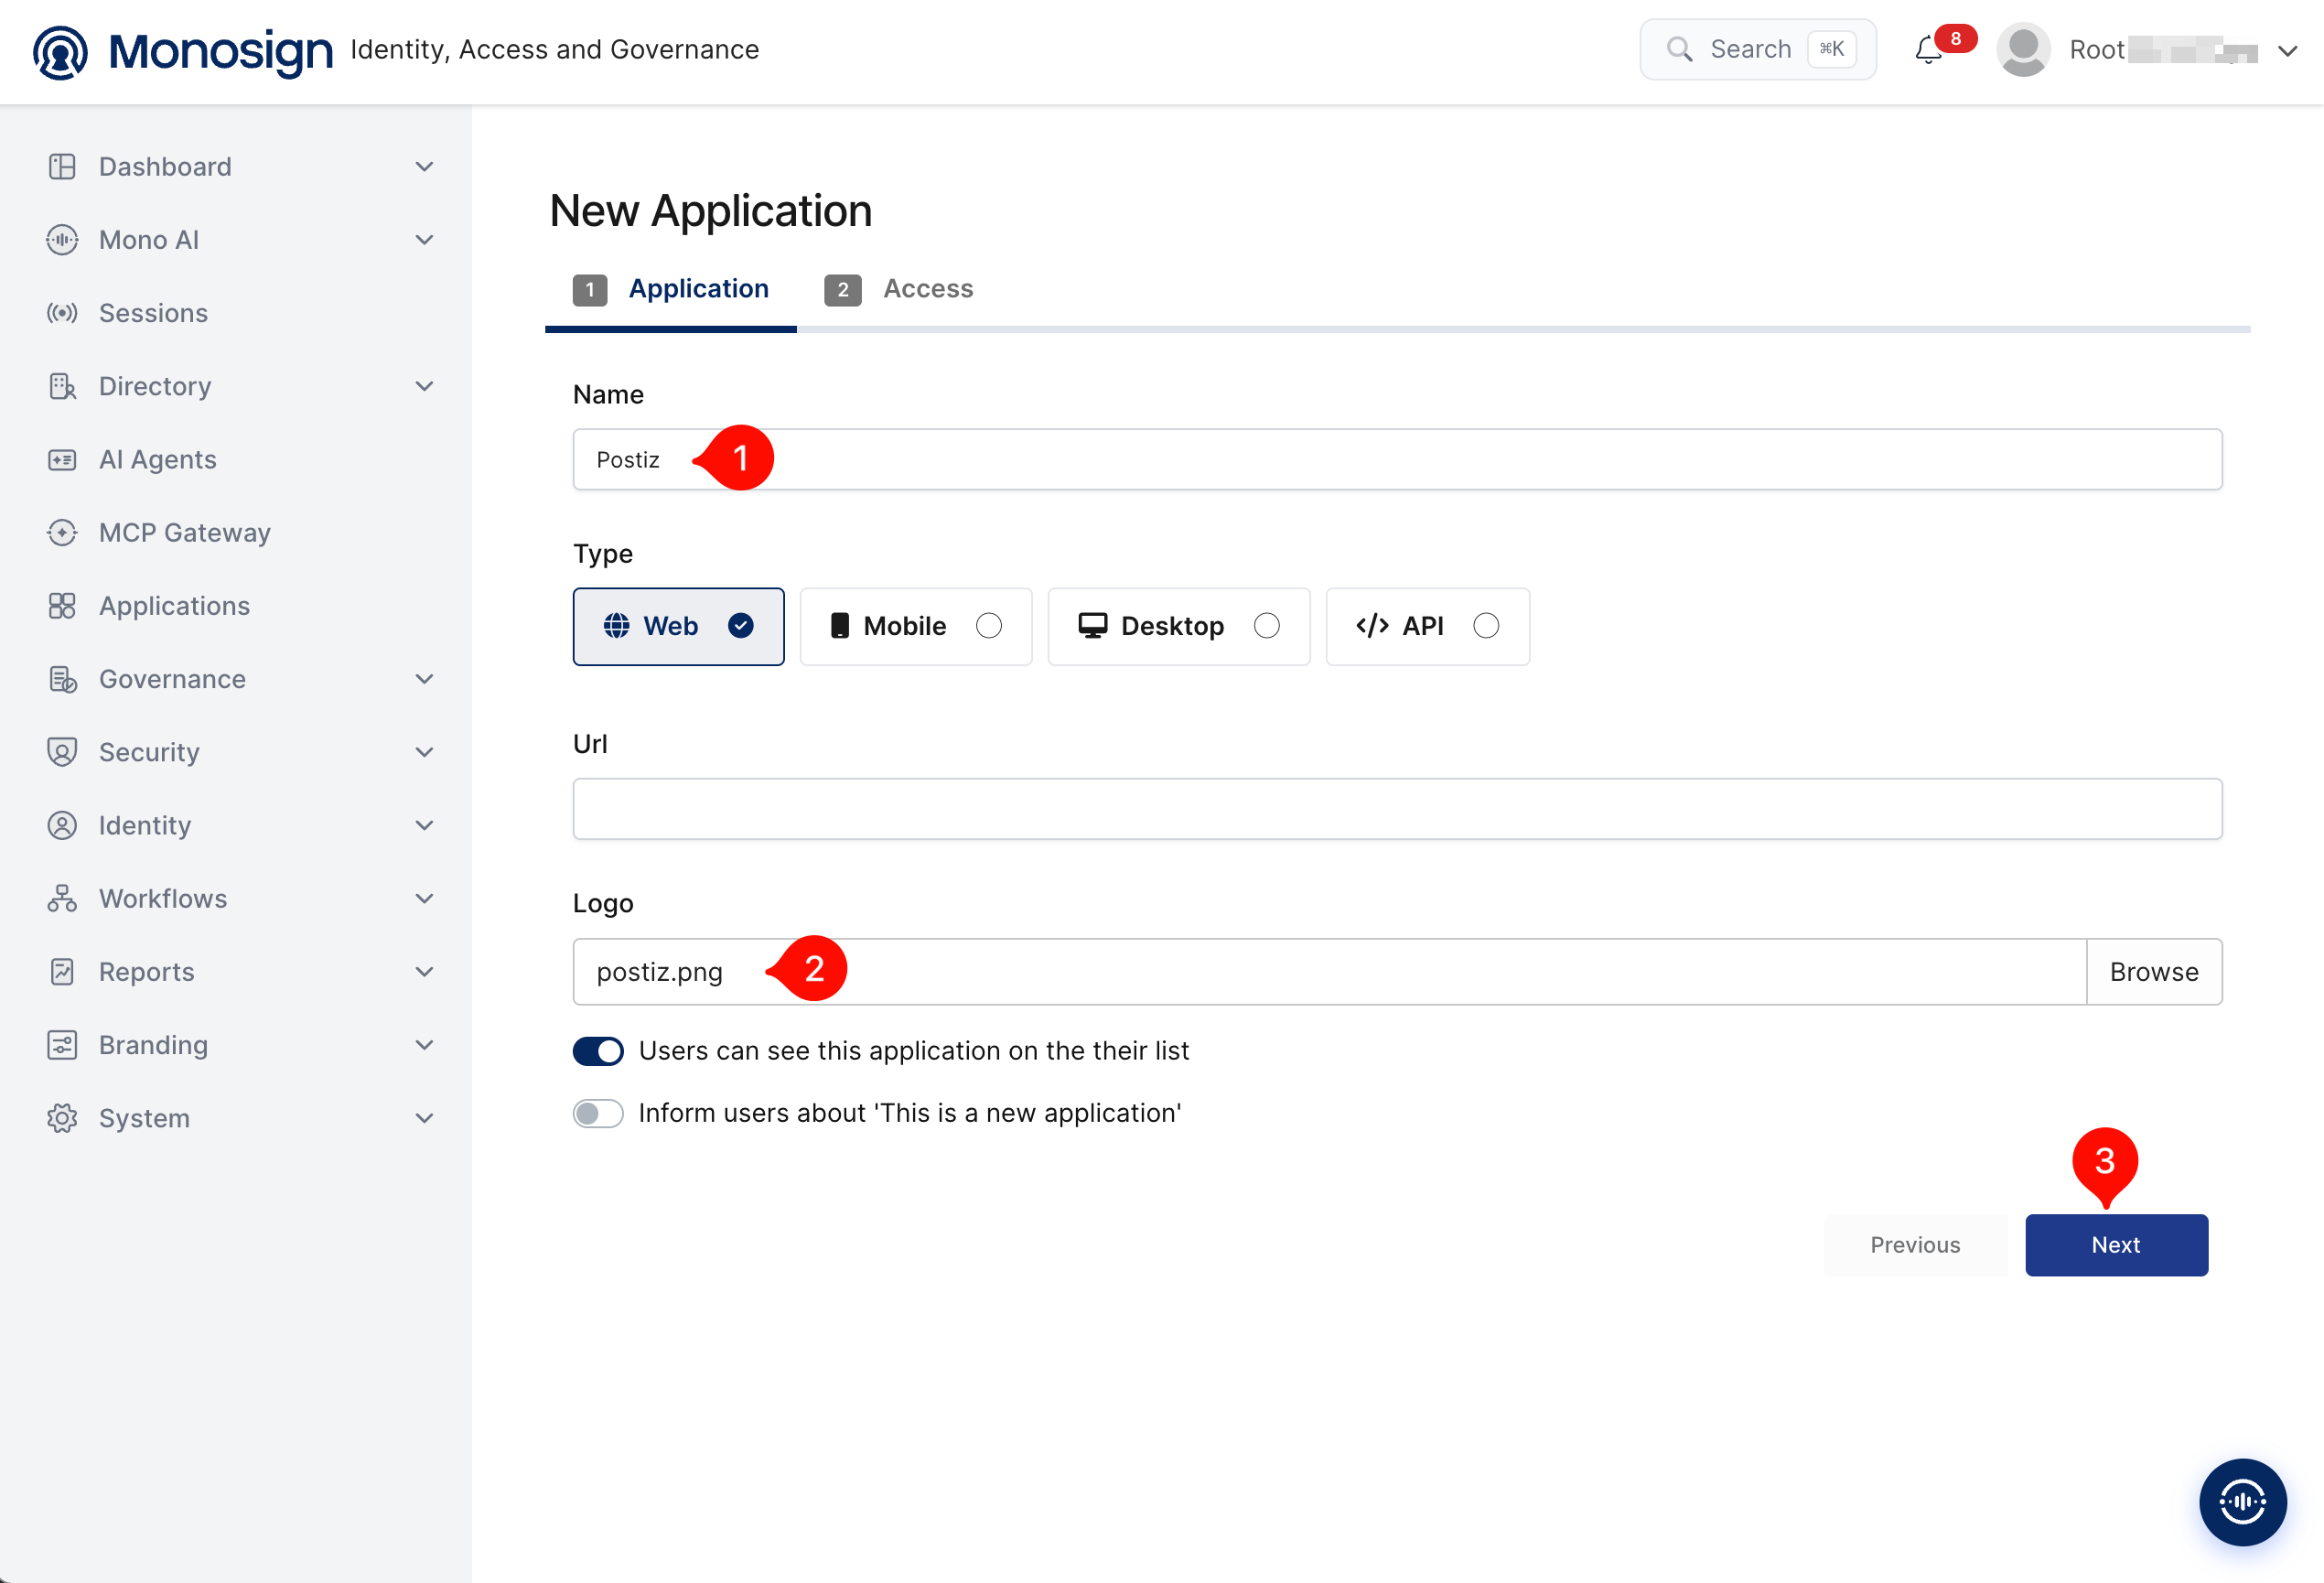
Fill in the application details on the Application tab and click Next.
|
Property |
Value |
Description |
|---|---|---|
|
Name |
|
Name of the application shown to users on the Monosign portal and on the Monosign sign-in page. |
|
Type |
|
Postiz is accessed through a web browser. Options: Web, Mobile, Desktop, API. |
|
Url |
Optional |
Leave empty or enter the Postiz address (for example |
|
Logo |
|
Optional. Browse and upload a logo; it is also shown on the Monosign sign-in page. |
|
Users can see this application on their list |
|
Displays the application on the user portal. |
On the Access tab define who can reach the application and click Create Application.
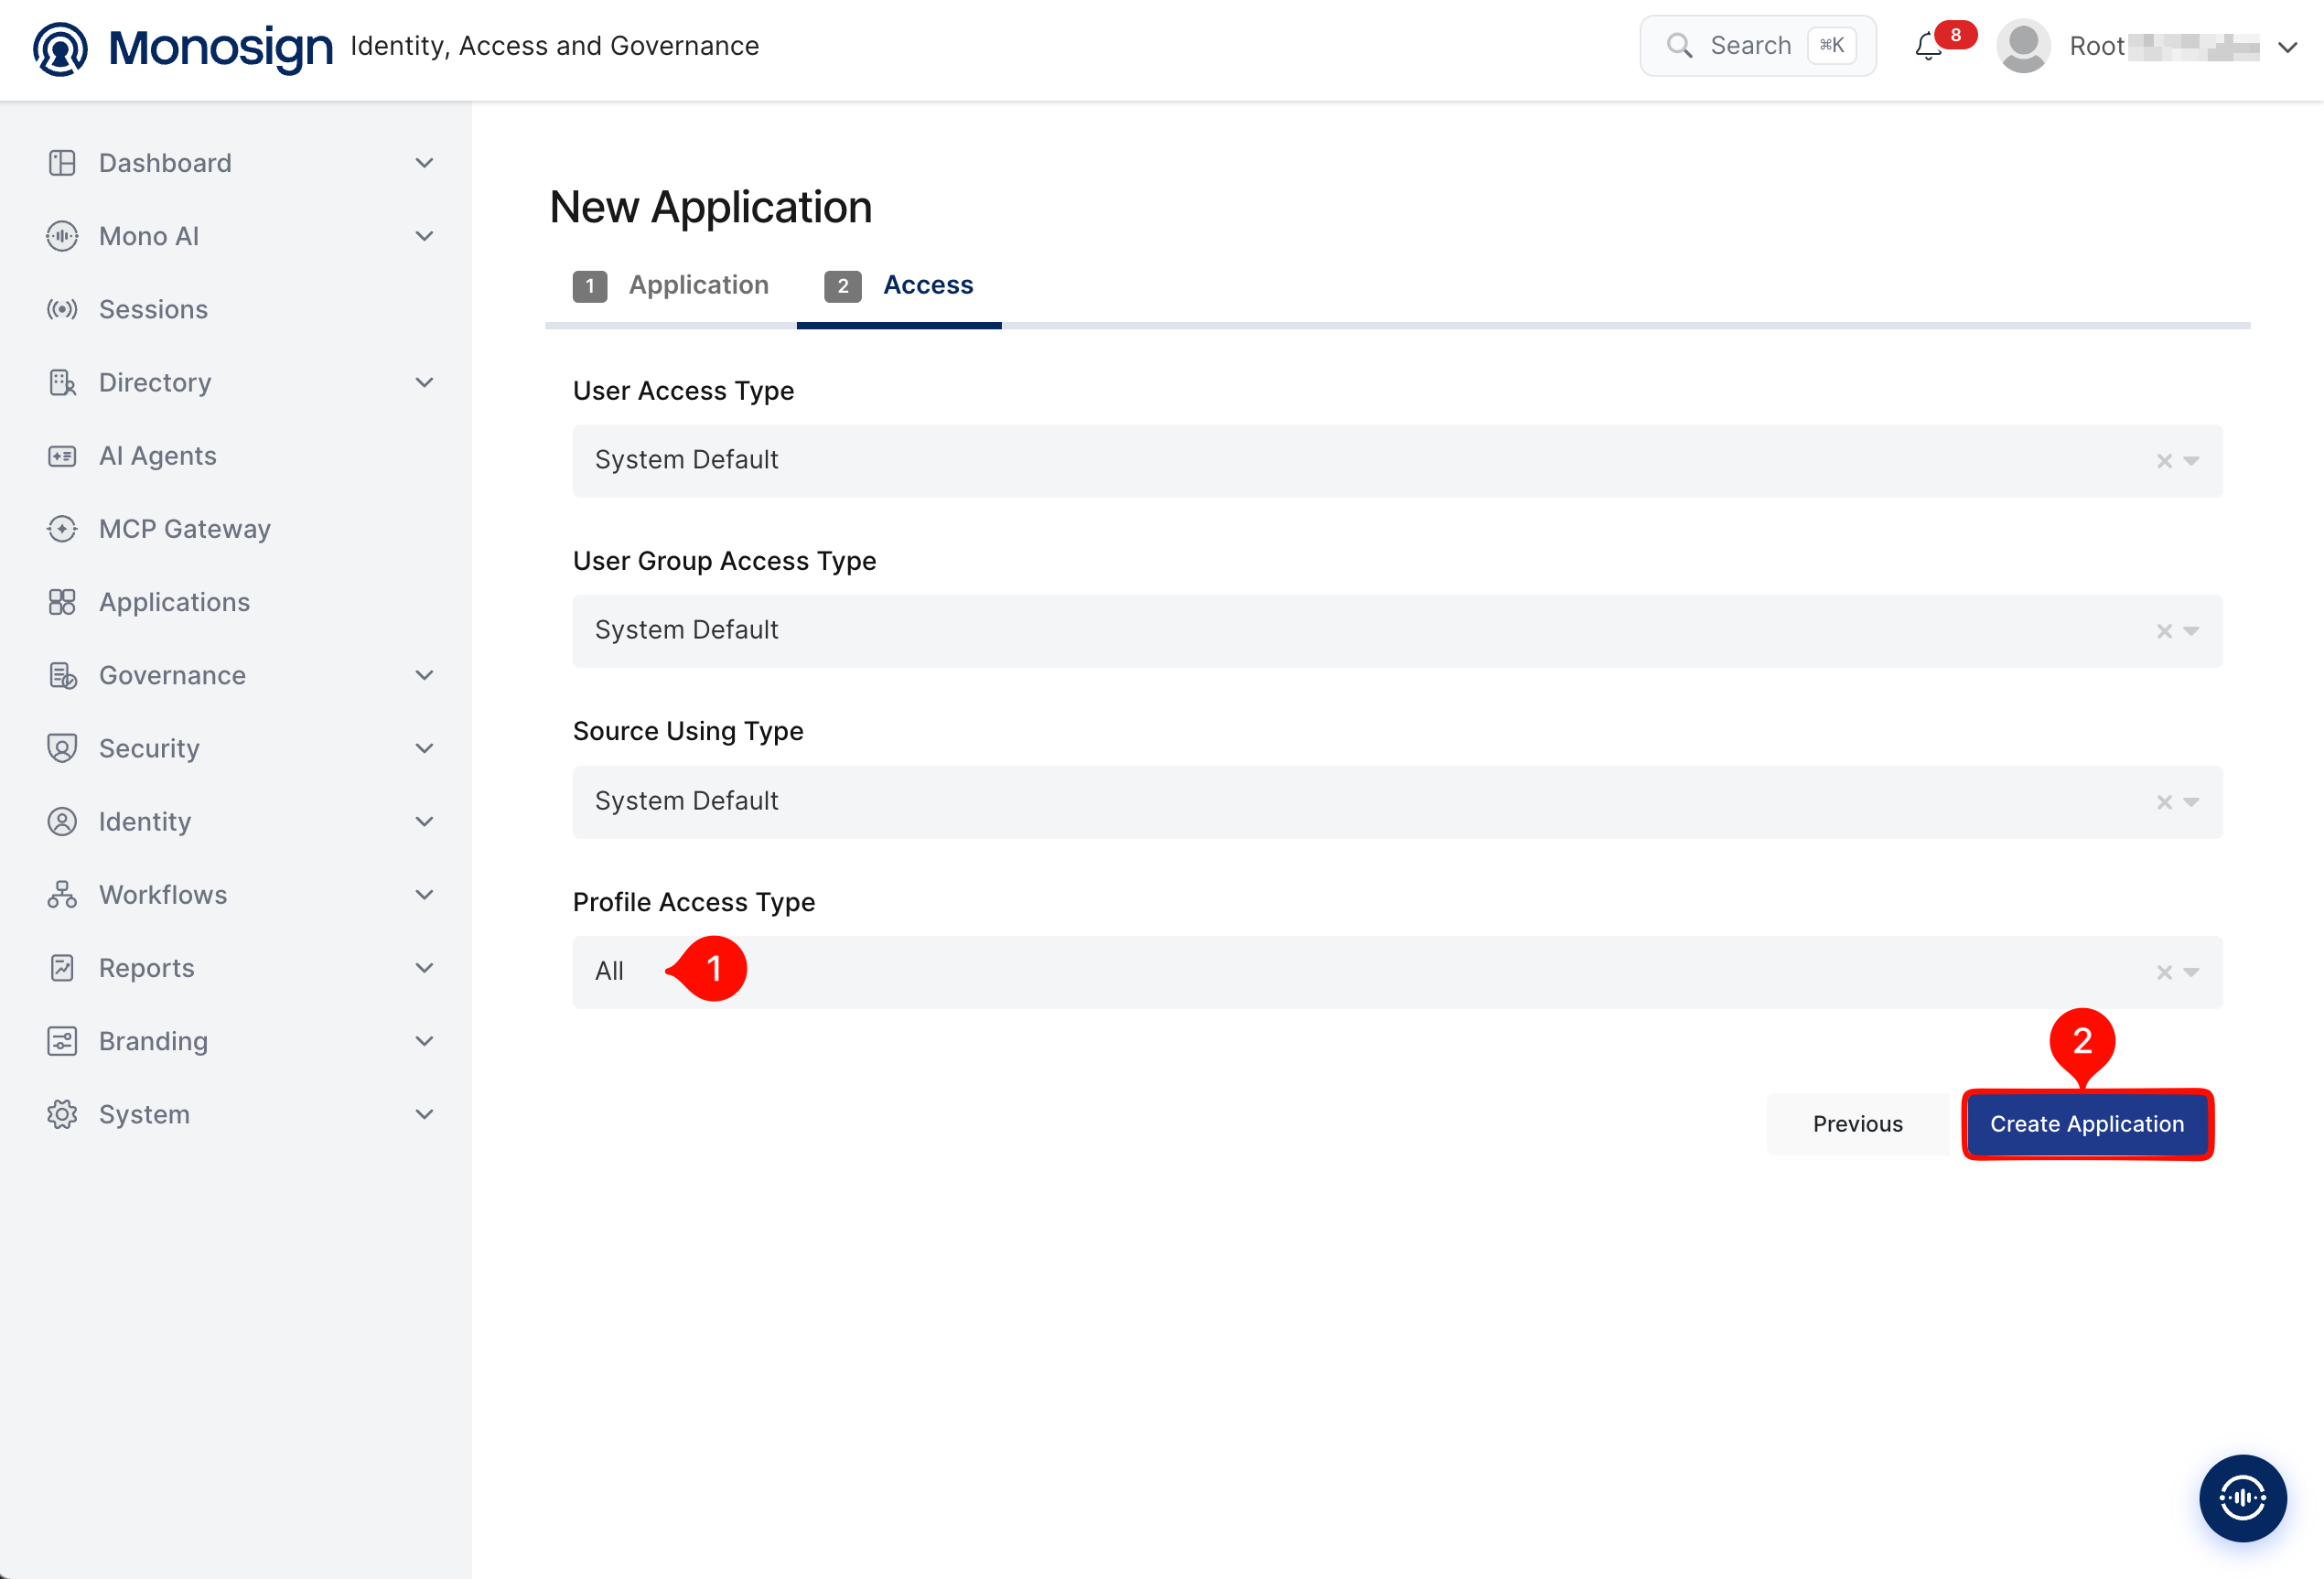
|
Property |
Value |
Description |
|---|---|---|
|
User Access Type |
|
Defines which users can access this application. Options: Only Assigned Users, All Users, System Default. |
|
User Group Access Type |
|
Defines the application’s user group access. |
|
Source Using Type |
|
Defines which user sources the application can use. |
|
Profile Access Type |
|
Defines which user profile attributes are available to the application. Options: Restricted, All. Postiz reads the |
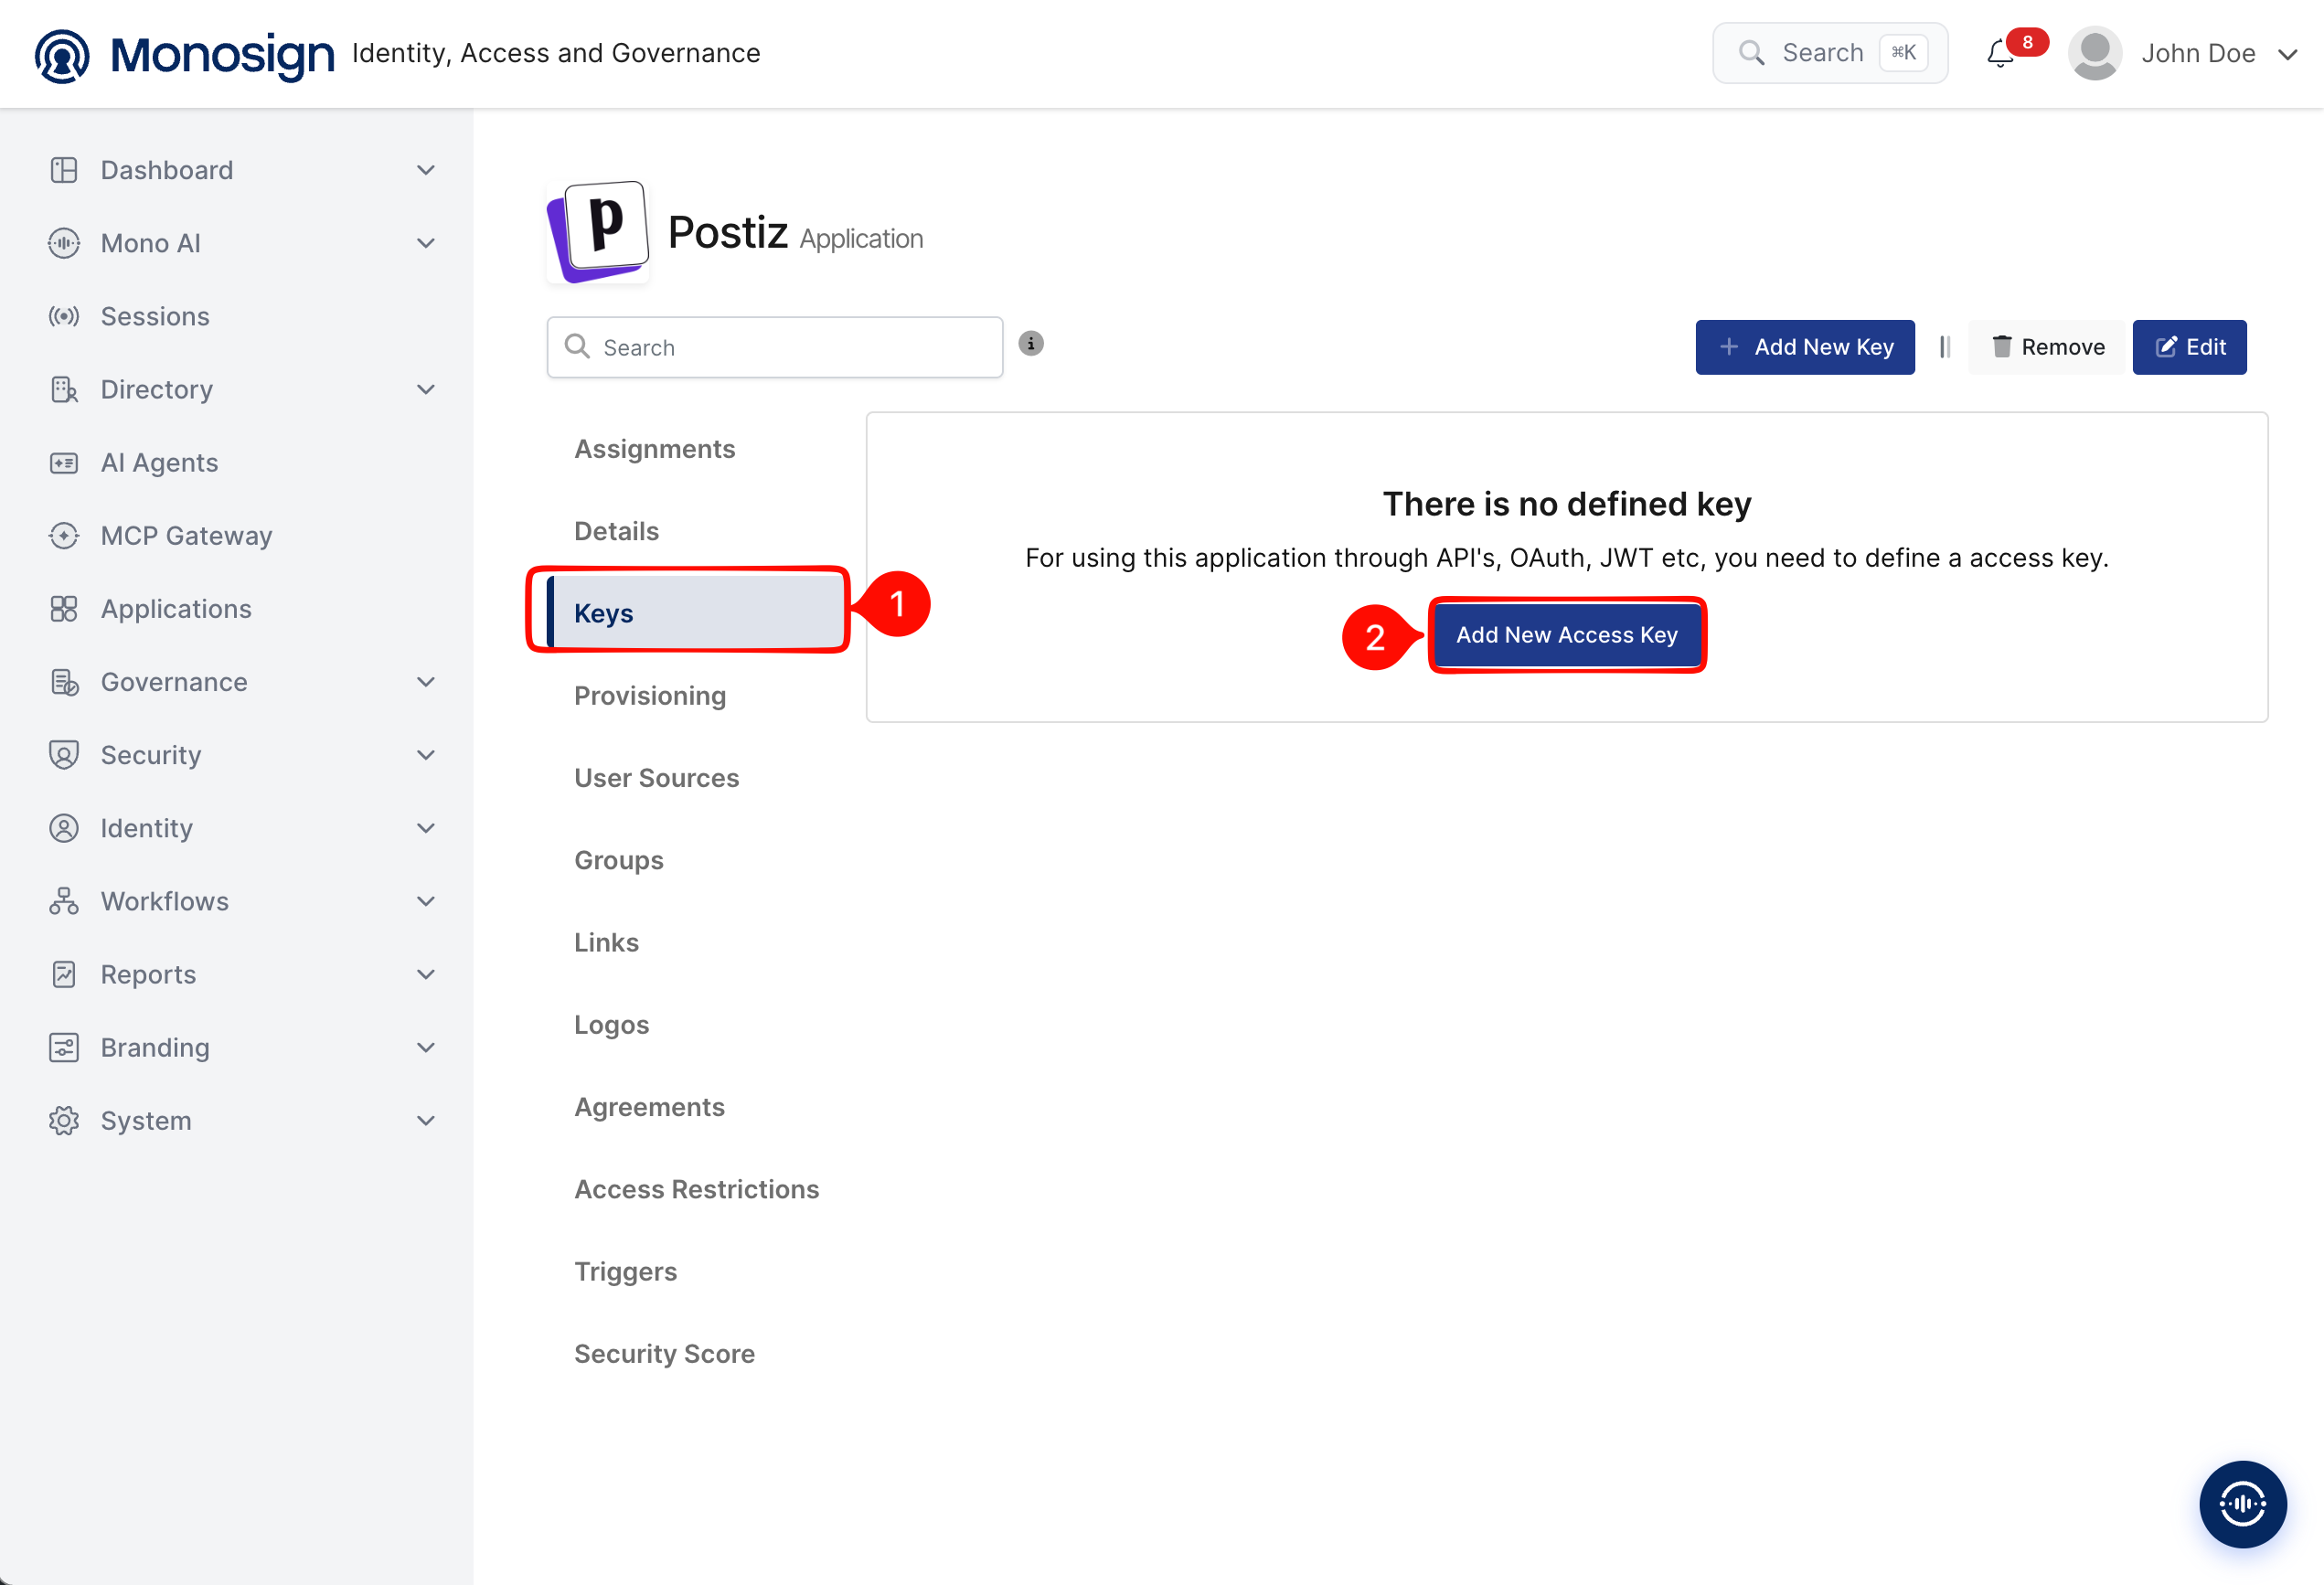
After the application is created, click Keys and add a new Access Key for OIDC/OpenID access.
Select OIDC/OpenID as the key type and click Create. Monosign generates the Client Id and Client Secret automatically.
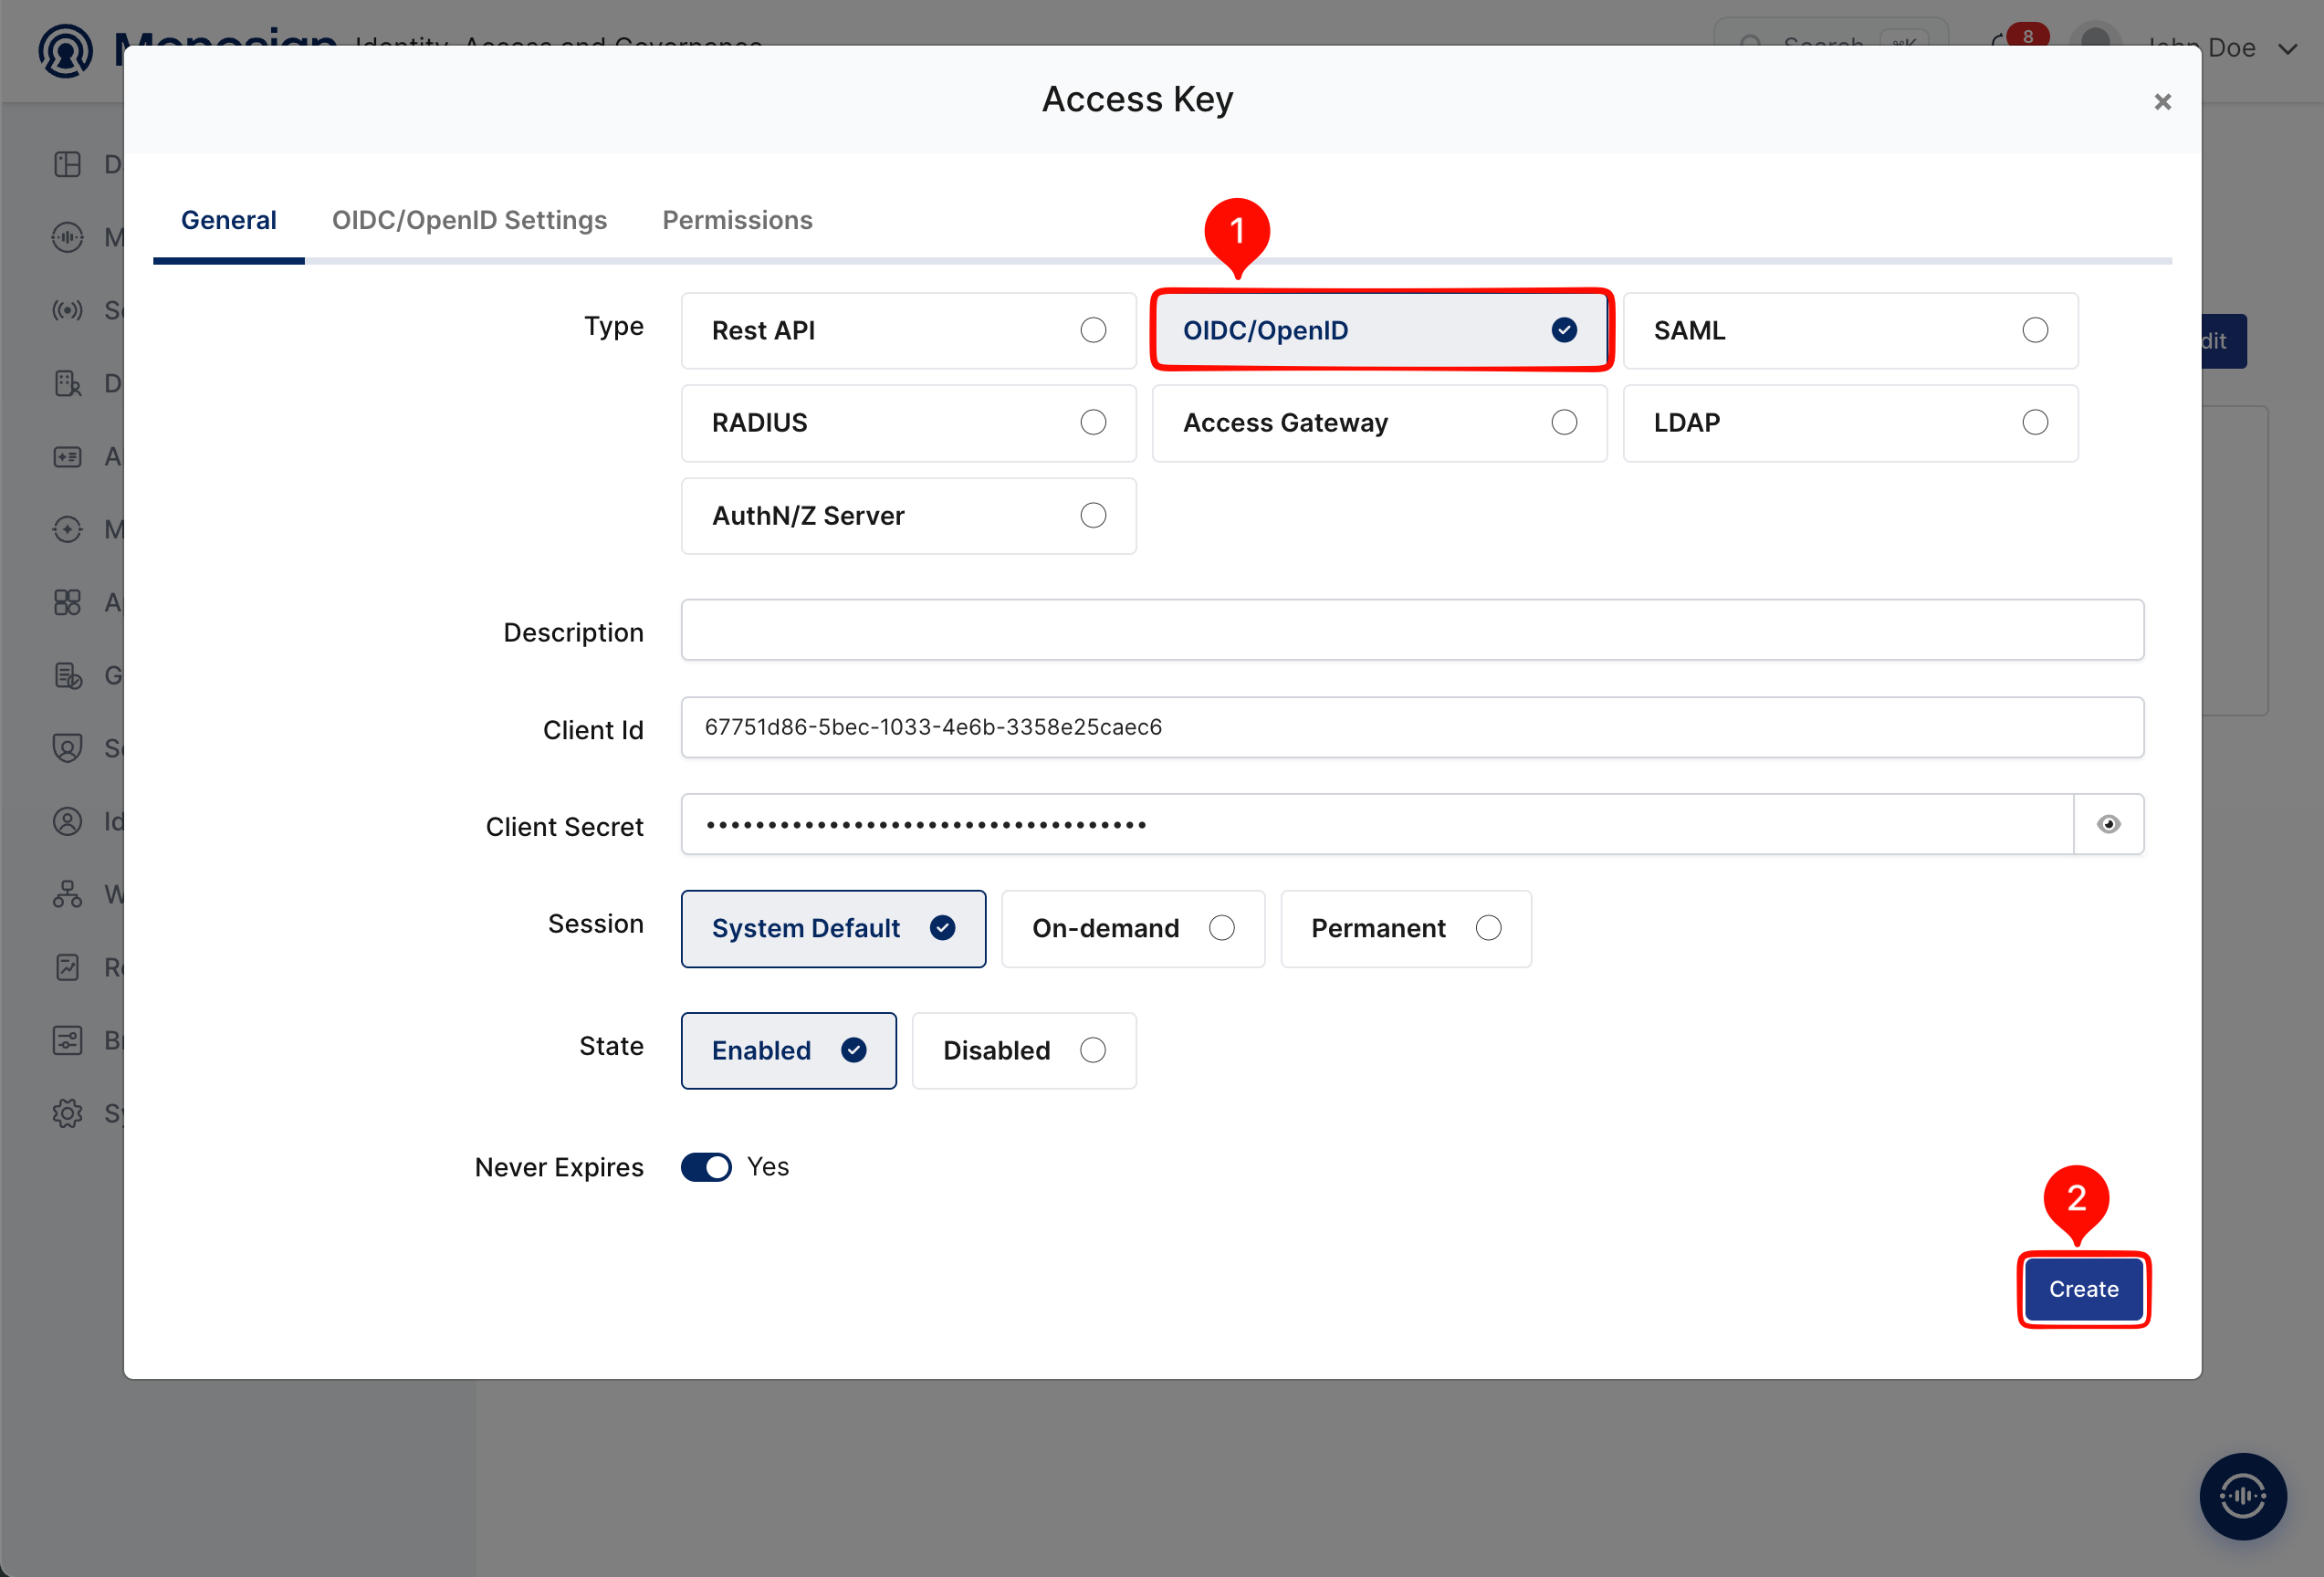
|
Property |
Value |
Options |
|---|---|---|
|
Type |
|
Rest API, OAuth 2.0, JWT, OIDC/OpenID, SAML, RADIUS, Access Gateway, LDAP, AuthN/Z Server |
|
Client Id / Client Secret |
Generated automatically |
Use the eye icon next to the secret to reveal it. The secret is required in step 3. |
|
Session |
|
System Default, On-demand, Permanent |
|
State |
|
Enabled, Disabled |
|
Never Expires |
|
Turn off to define a specific expiration date for the key. |
Configuration details for the Postiz application are provided as follows:
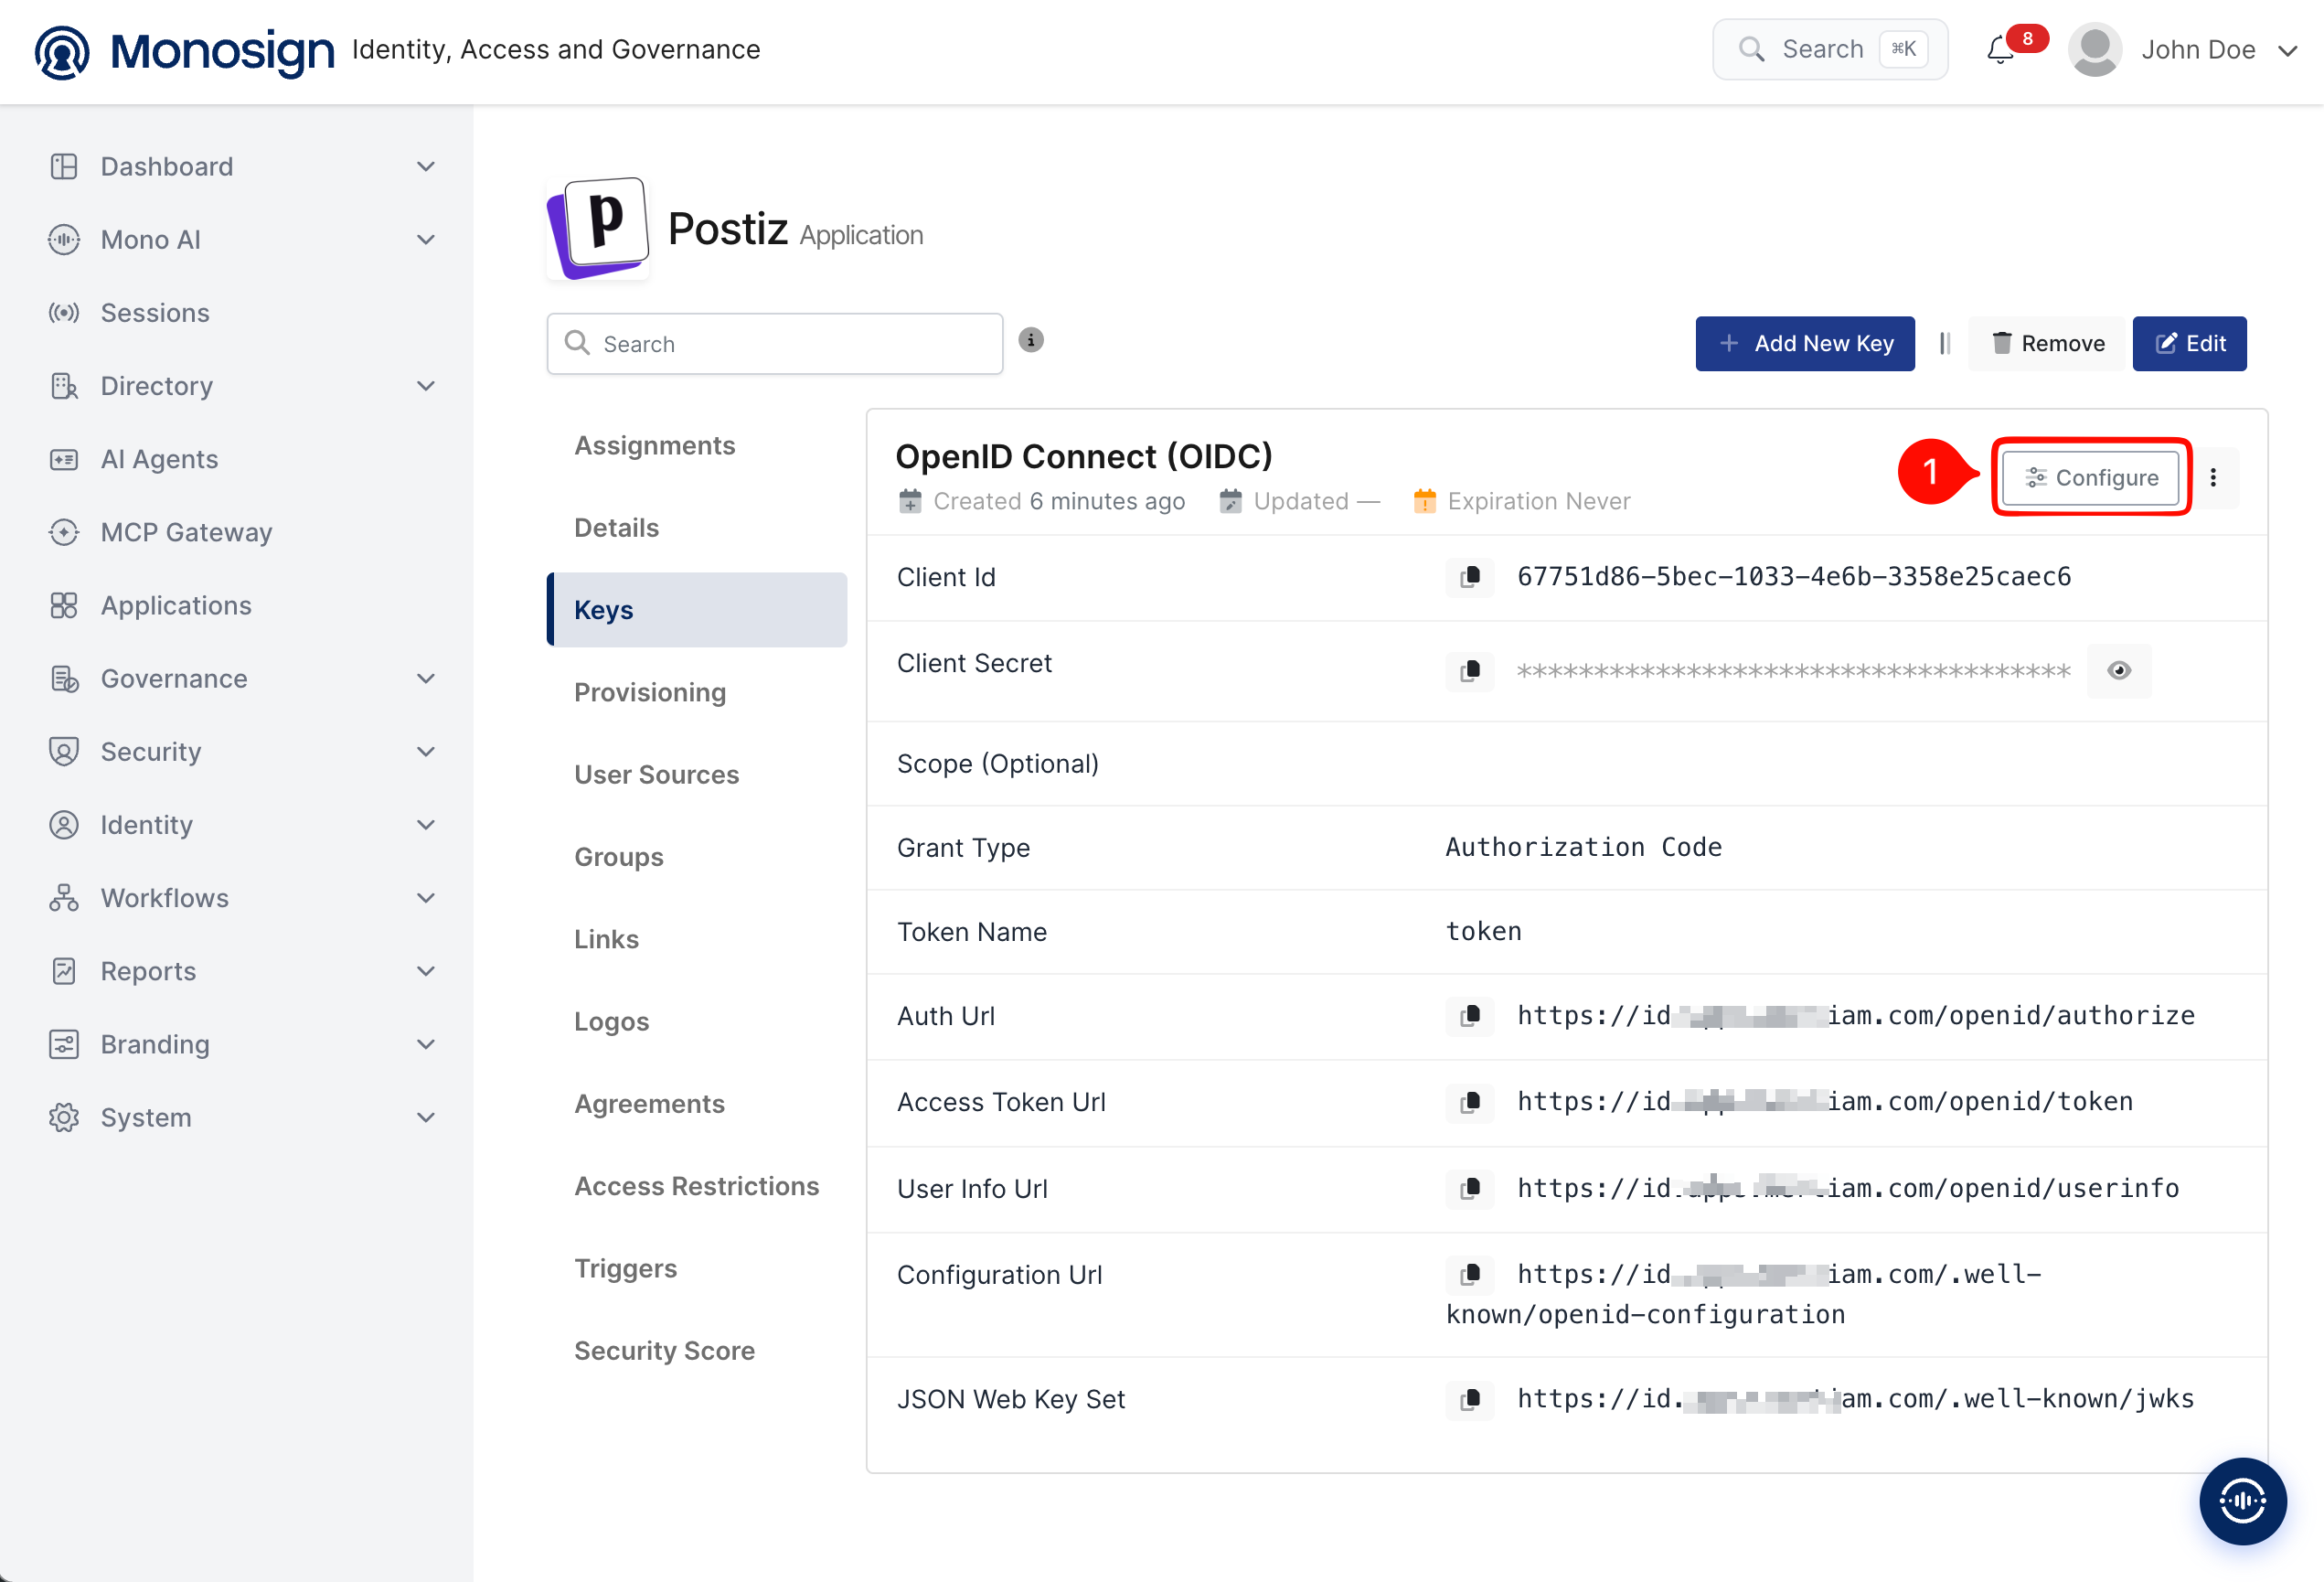
|
Property |
Value |
Used in Postiz as |
|---|---|---|
|
Client Id |
|
|
|
Client Secret |
|
|
|
Grant Type |
|
The flow used by Postiz. |
|
Auth Url |
|
|
|
Access Token Url |
|
|
|
User Info Url |
|
|
|
Configuration Url / JSON Web Key Set |
|
Not used. Postiz does not read the discovery document or validate the token itself. |
The third step uses the Client Id, Client Secret, Auth Url, Access Token Url and User Info Url from the “OIDC/OpenID Access Key Details“ section above to configure Postiz.
2- Configuring the OIDC/OpenID Settings on Monosign
Click the Configure button on the OpenID Connect (OIDC) key and open the OIDC/OpenID Settings → Configuration tab. The default values are used for the Postiz integration.
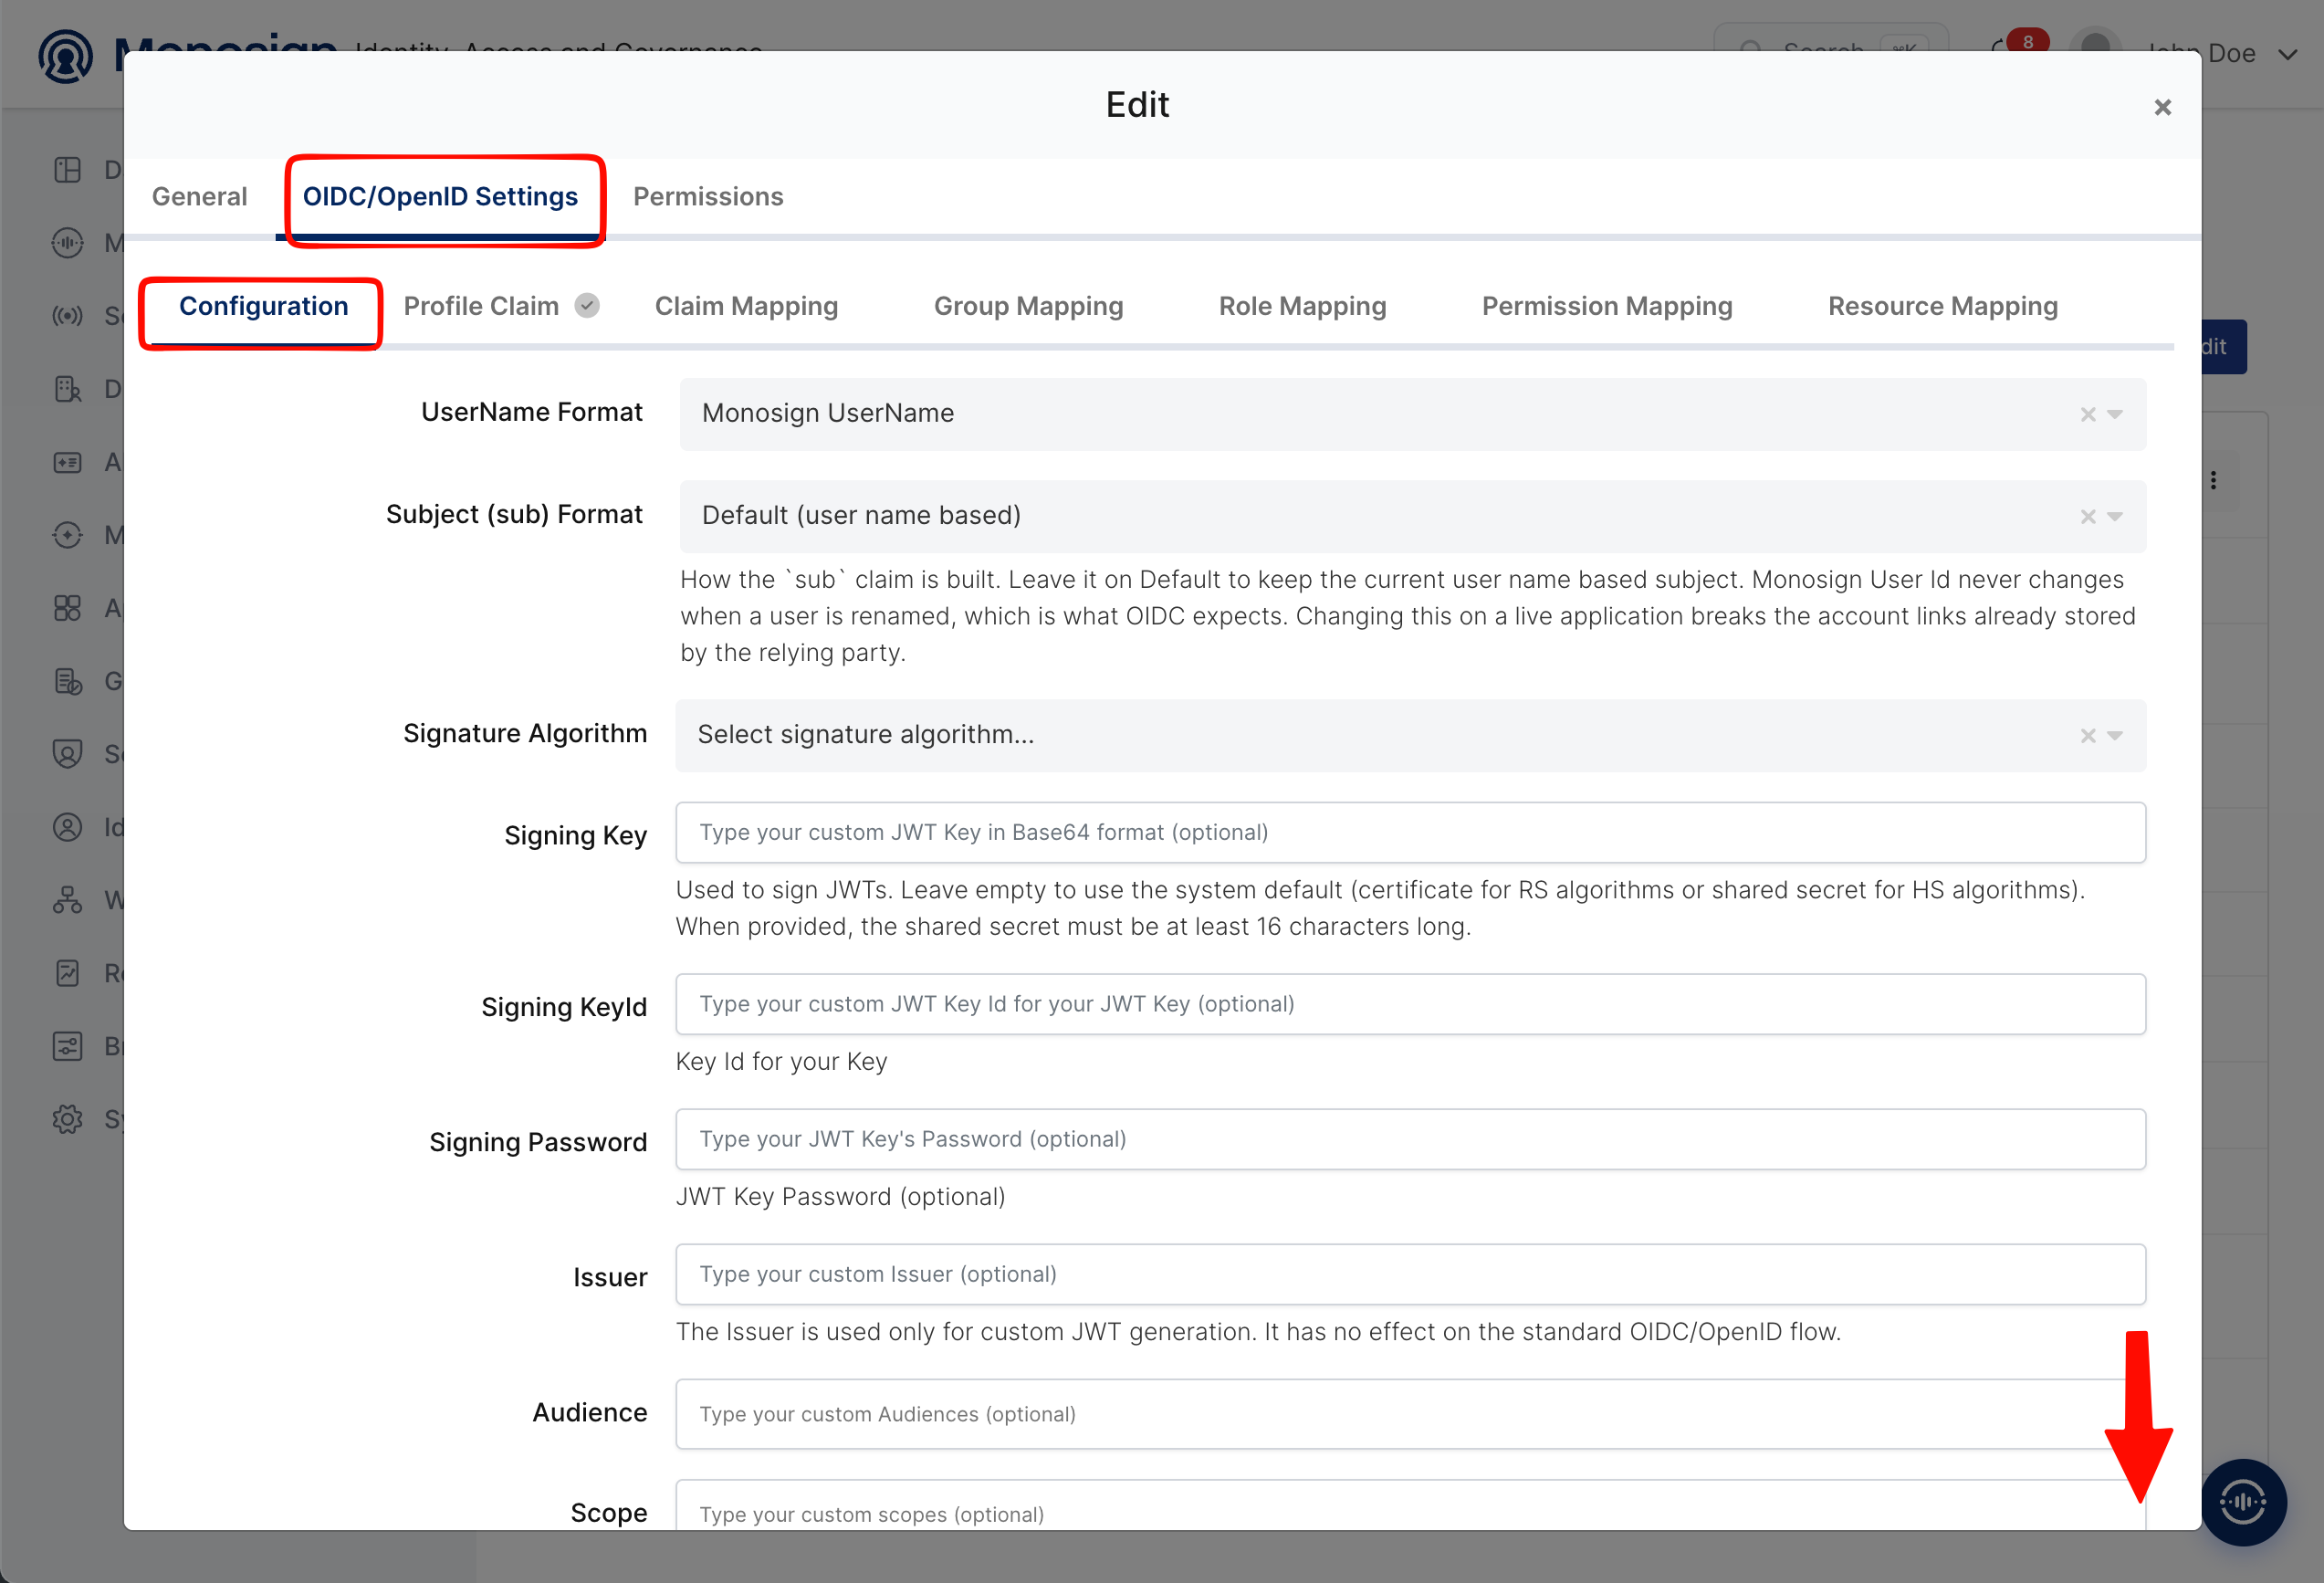
|
Property |
Value |
Description |
|---|---|---|
|
UserName Format |
|
Defines the UserName format such as |
|
Subject (sub) Format |
|
How the |
|
Signature Algorithm |
Not selected |
Postiz does not validate the token signature; it reads the user from the UserInfo endpoint, so no change is required. |
|
Signing Key / Key Id / Password, Issuer, Audience, Scope, Resource |
Empty |
Optional custom JWT settings. They are not needed for Postiz. |
Scroll down to Allowed Redirect URIs and add the callback address of Postiz.
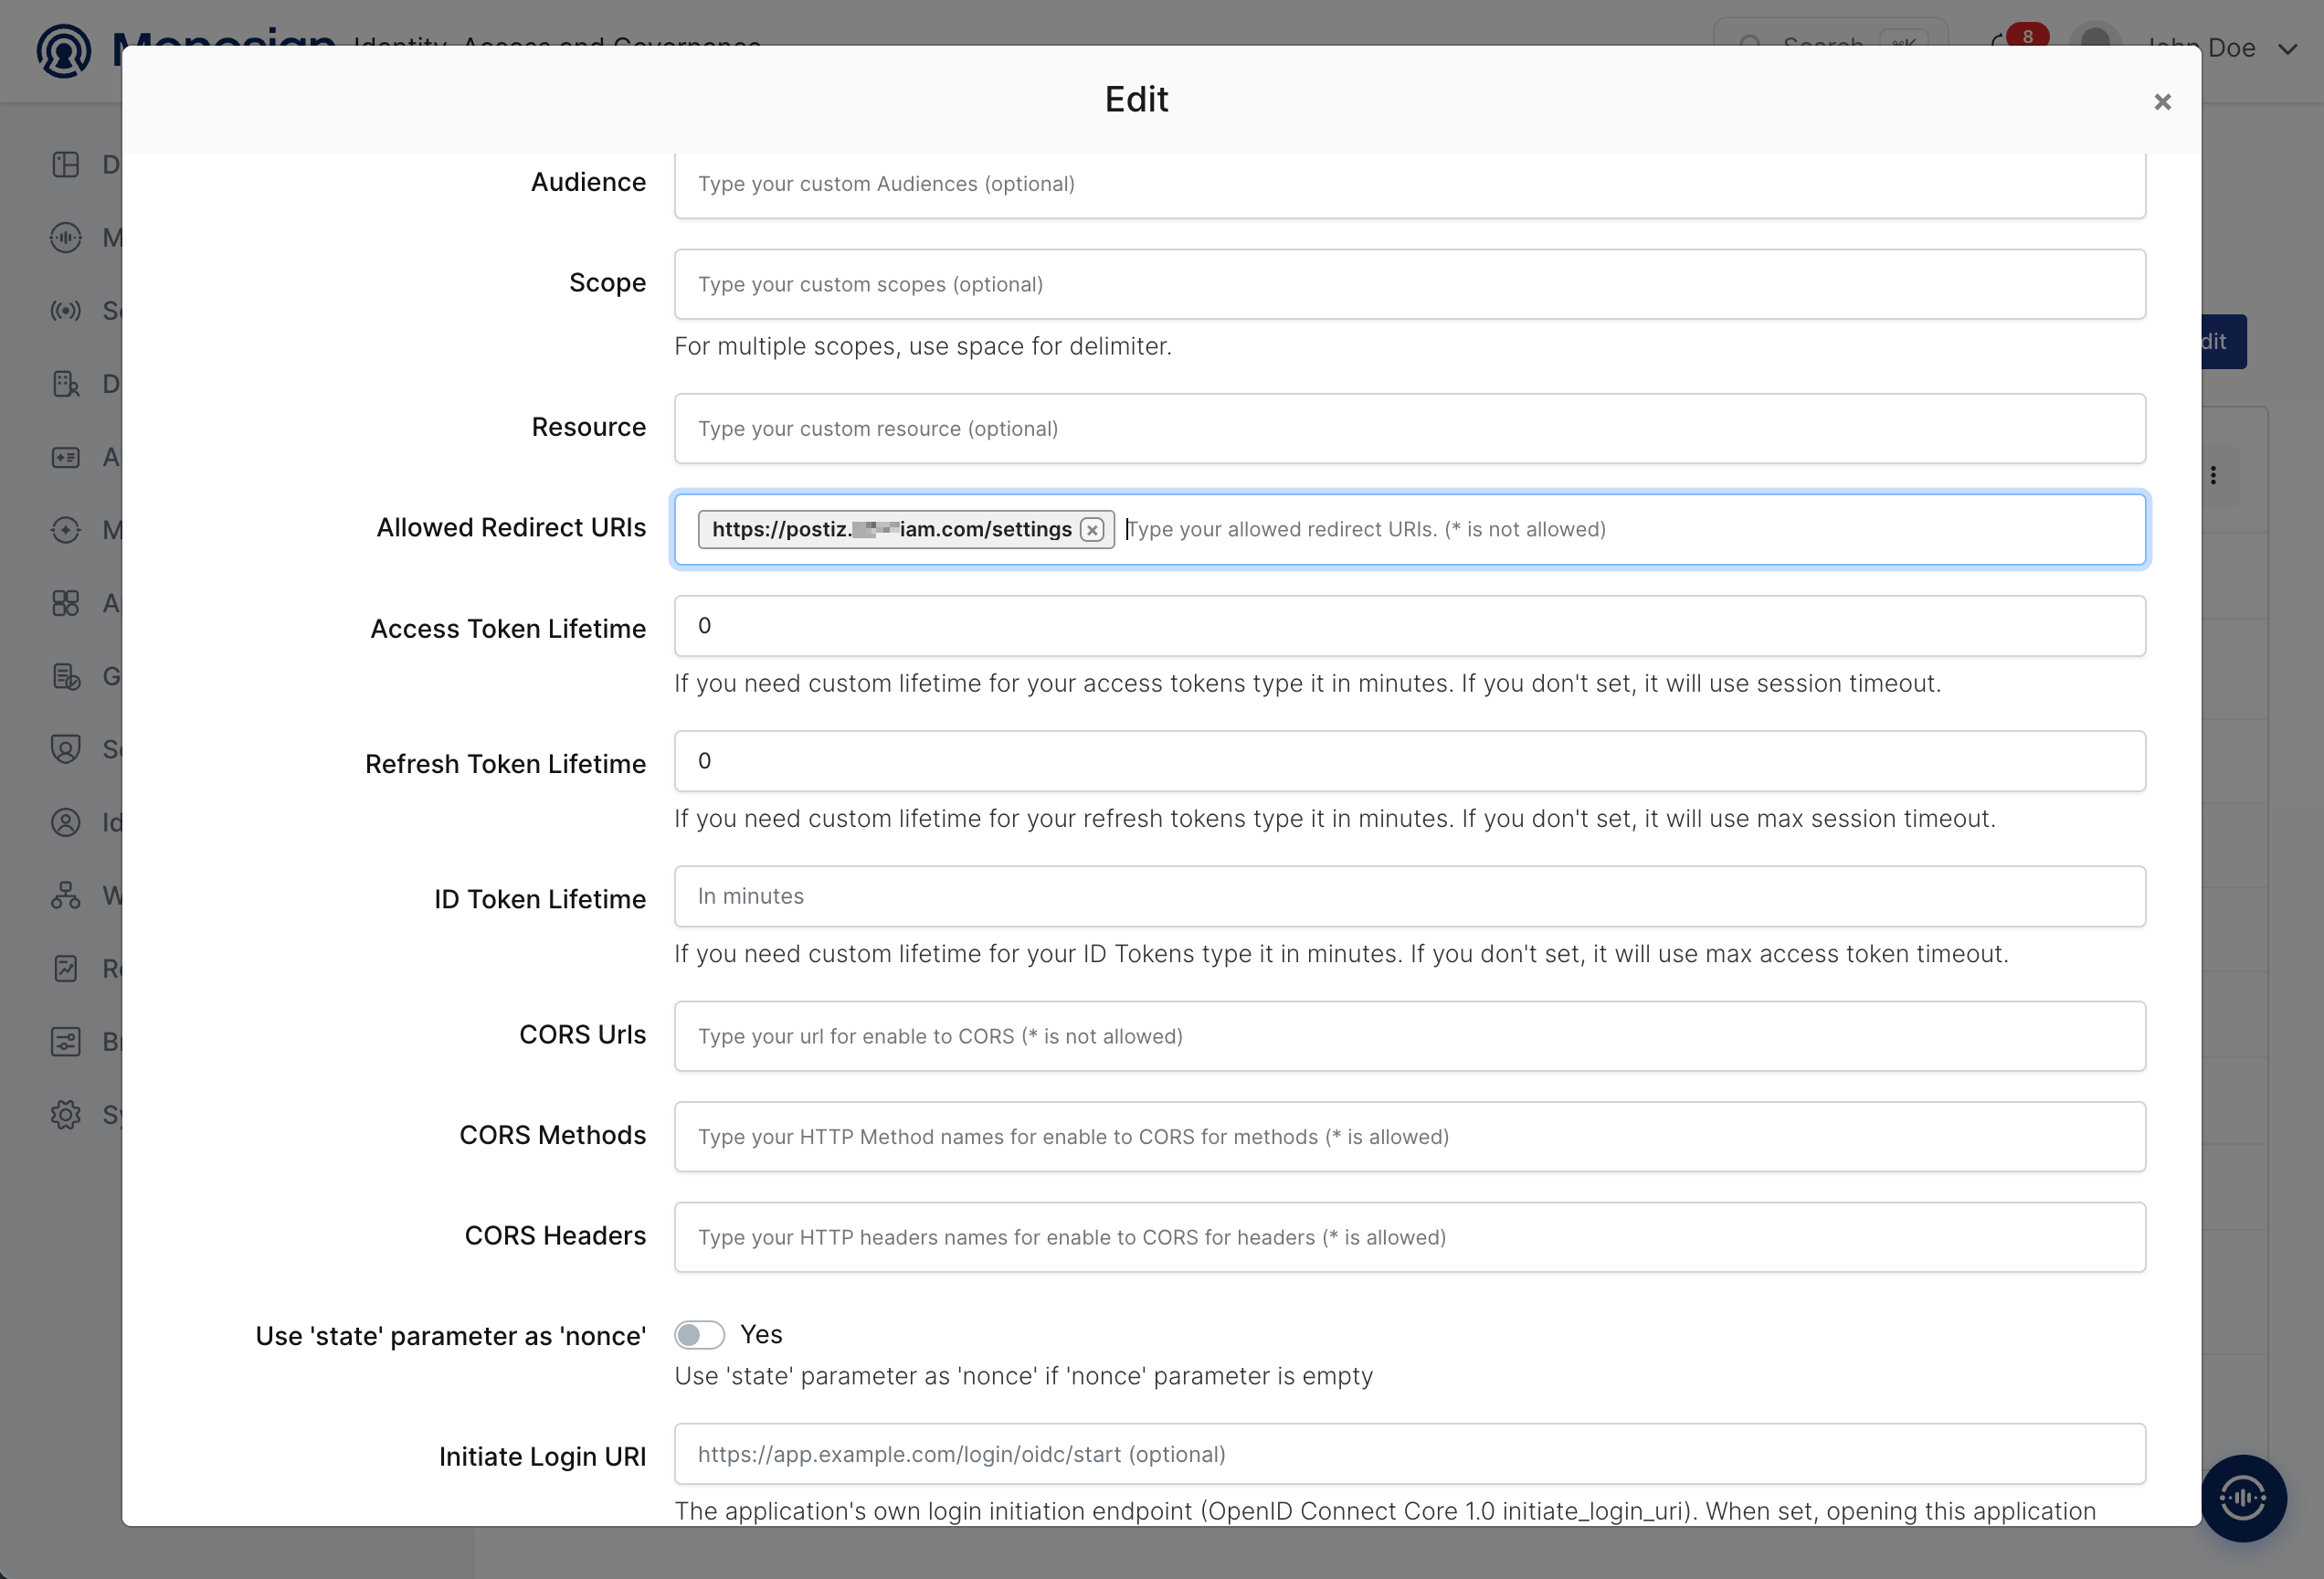
|
Property |
Value |
Description |
|---|---|---|
|
Allowed Redirect URIs |
|
The address where Monosign sends the user back after sign-in. Postiz always uses |
|
Use ‘state’ parameter as ‘nonce’ |
|
No change is required for Postiz. |
|
Access / Refresh / ID Token Lifetime, CORS |
Empty |
Default session based lifetimes are used. CORS is not required. |
The path of the redirect URI is fixed by Postiz and it is /settings. A different path or a trailing slash causes a redirect URI mismatch after the sign-in.
Sign-in URL of the application (optional)
If you also want users to start the sign-in from their Monosign portal, give the application a sign-in URL. Open the application, click Edit, go to the Login tab and enter the OAuth start address of Postiz in Login Url, then click Save.
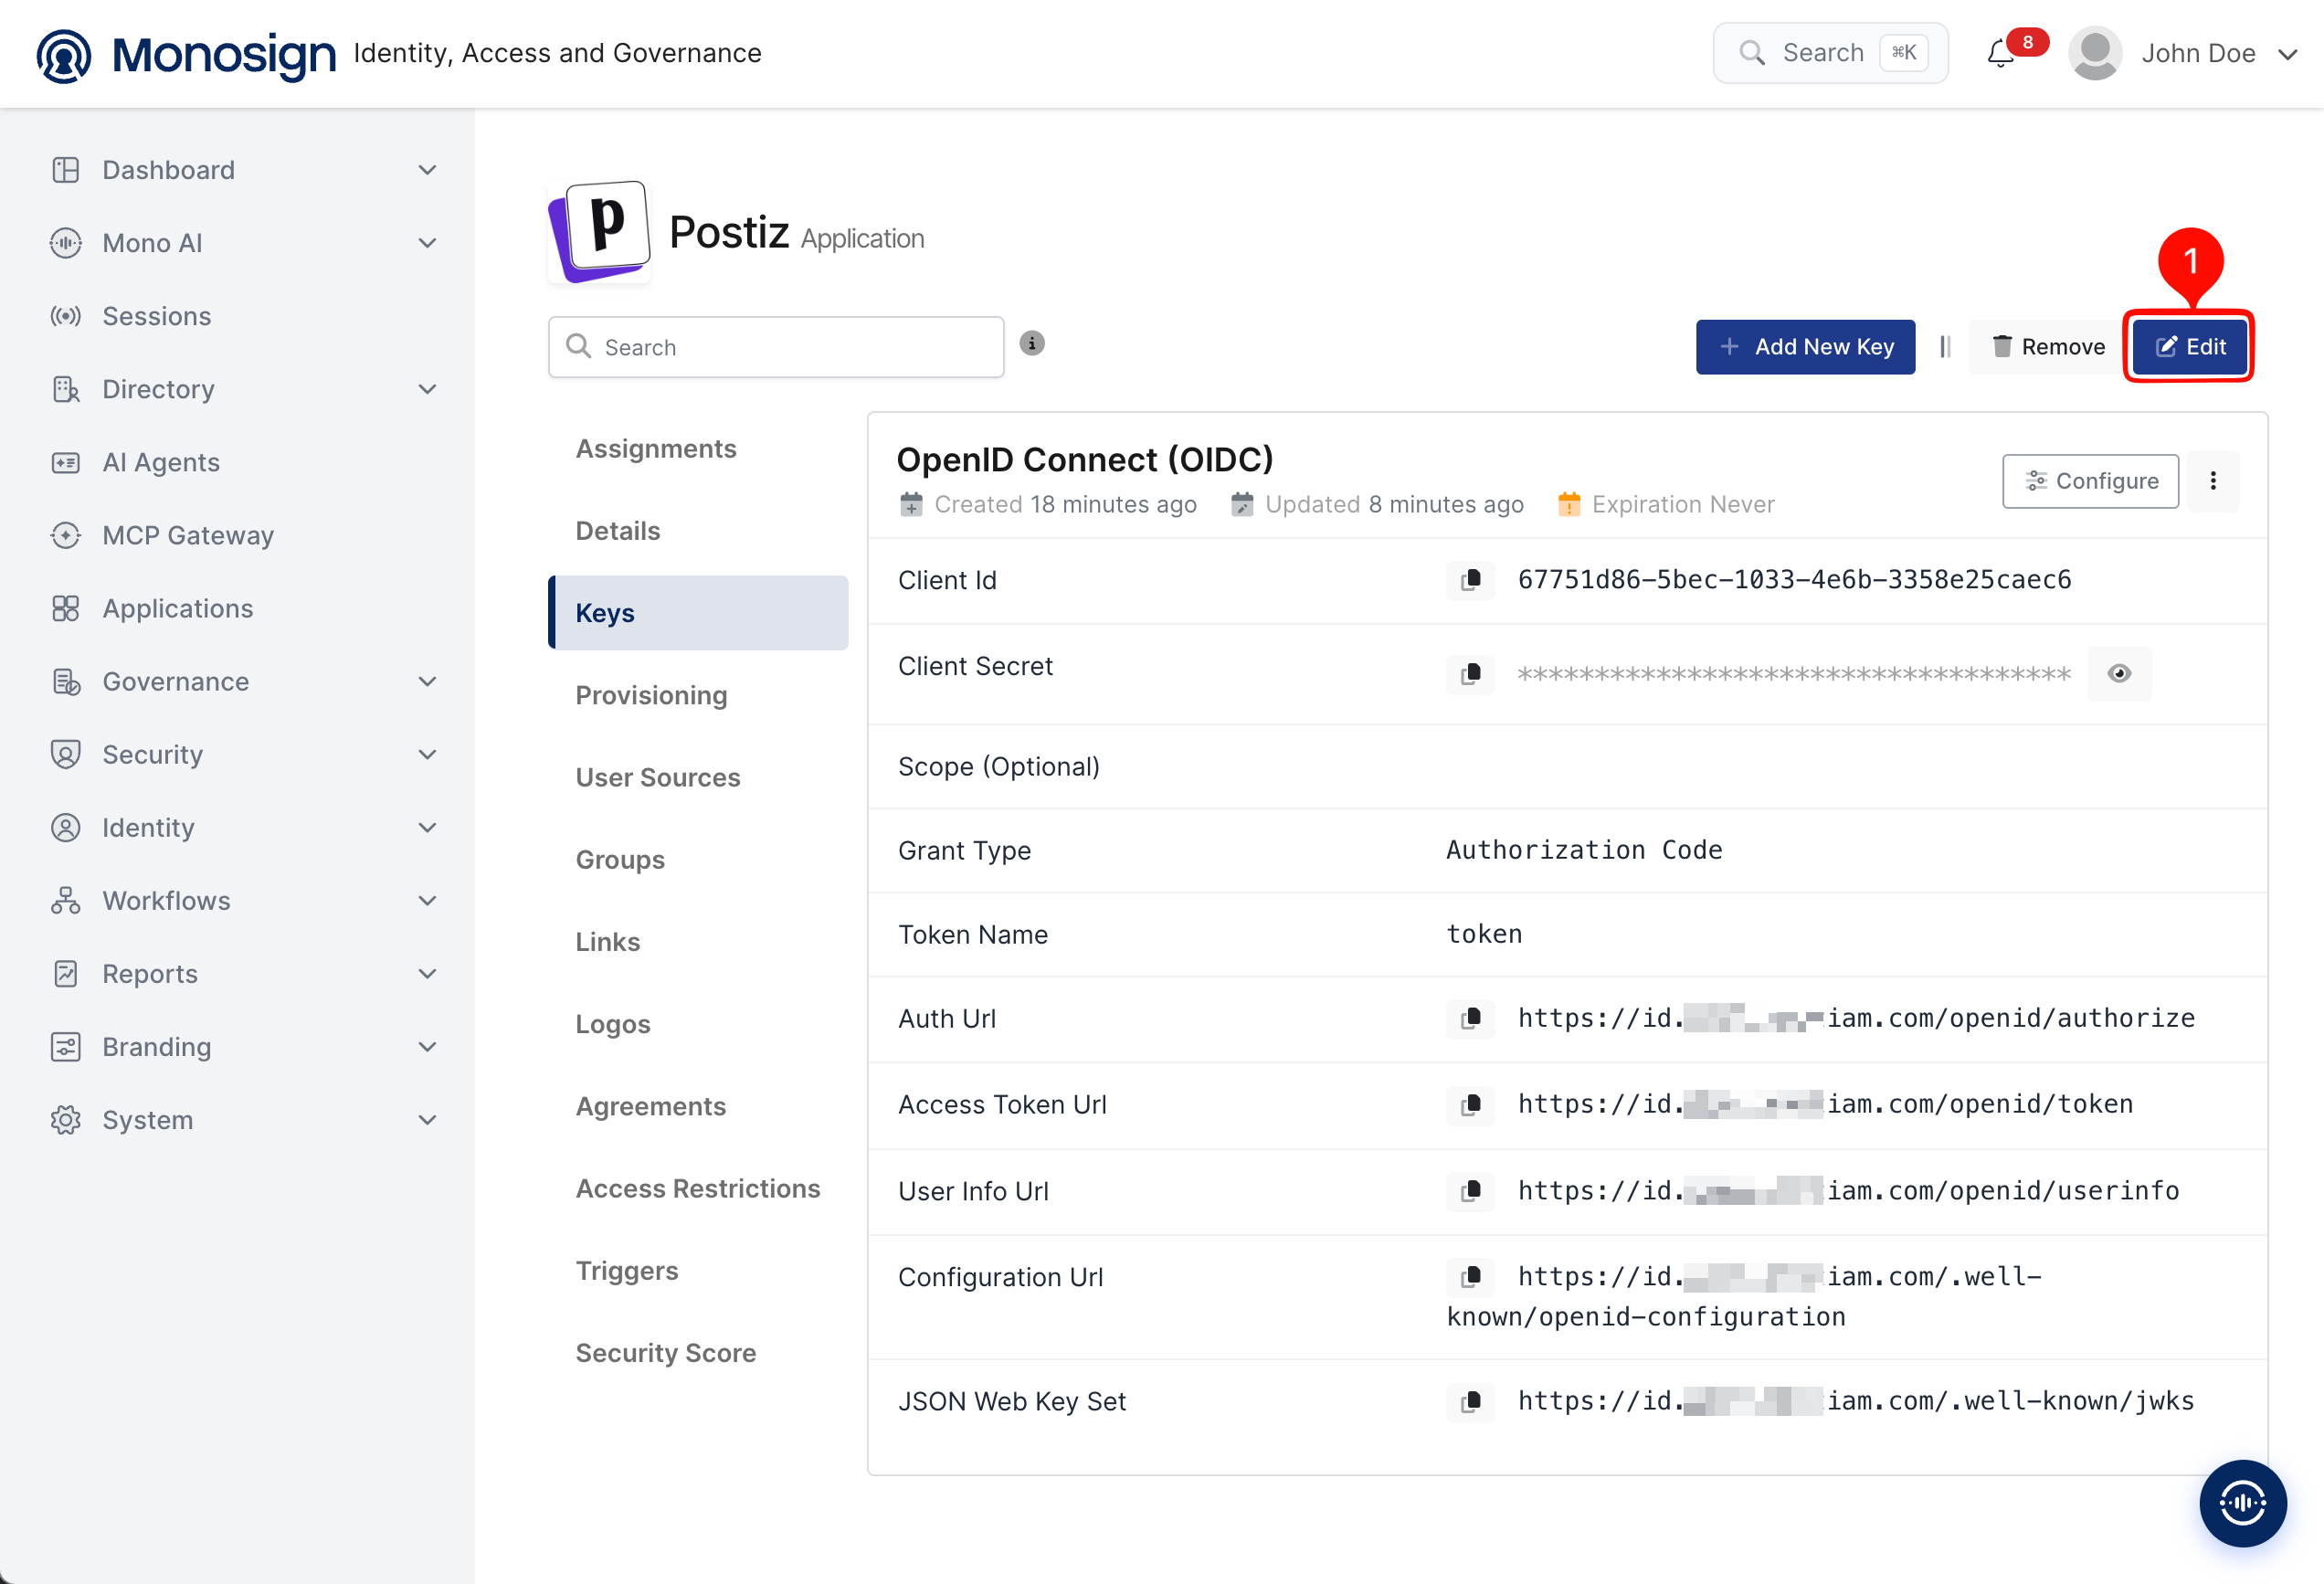
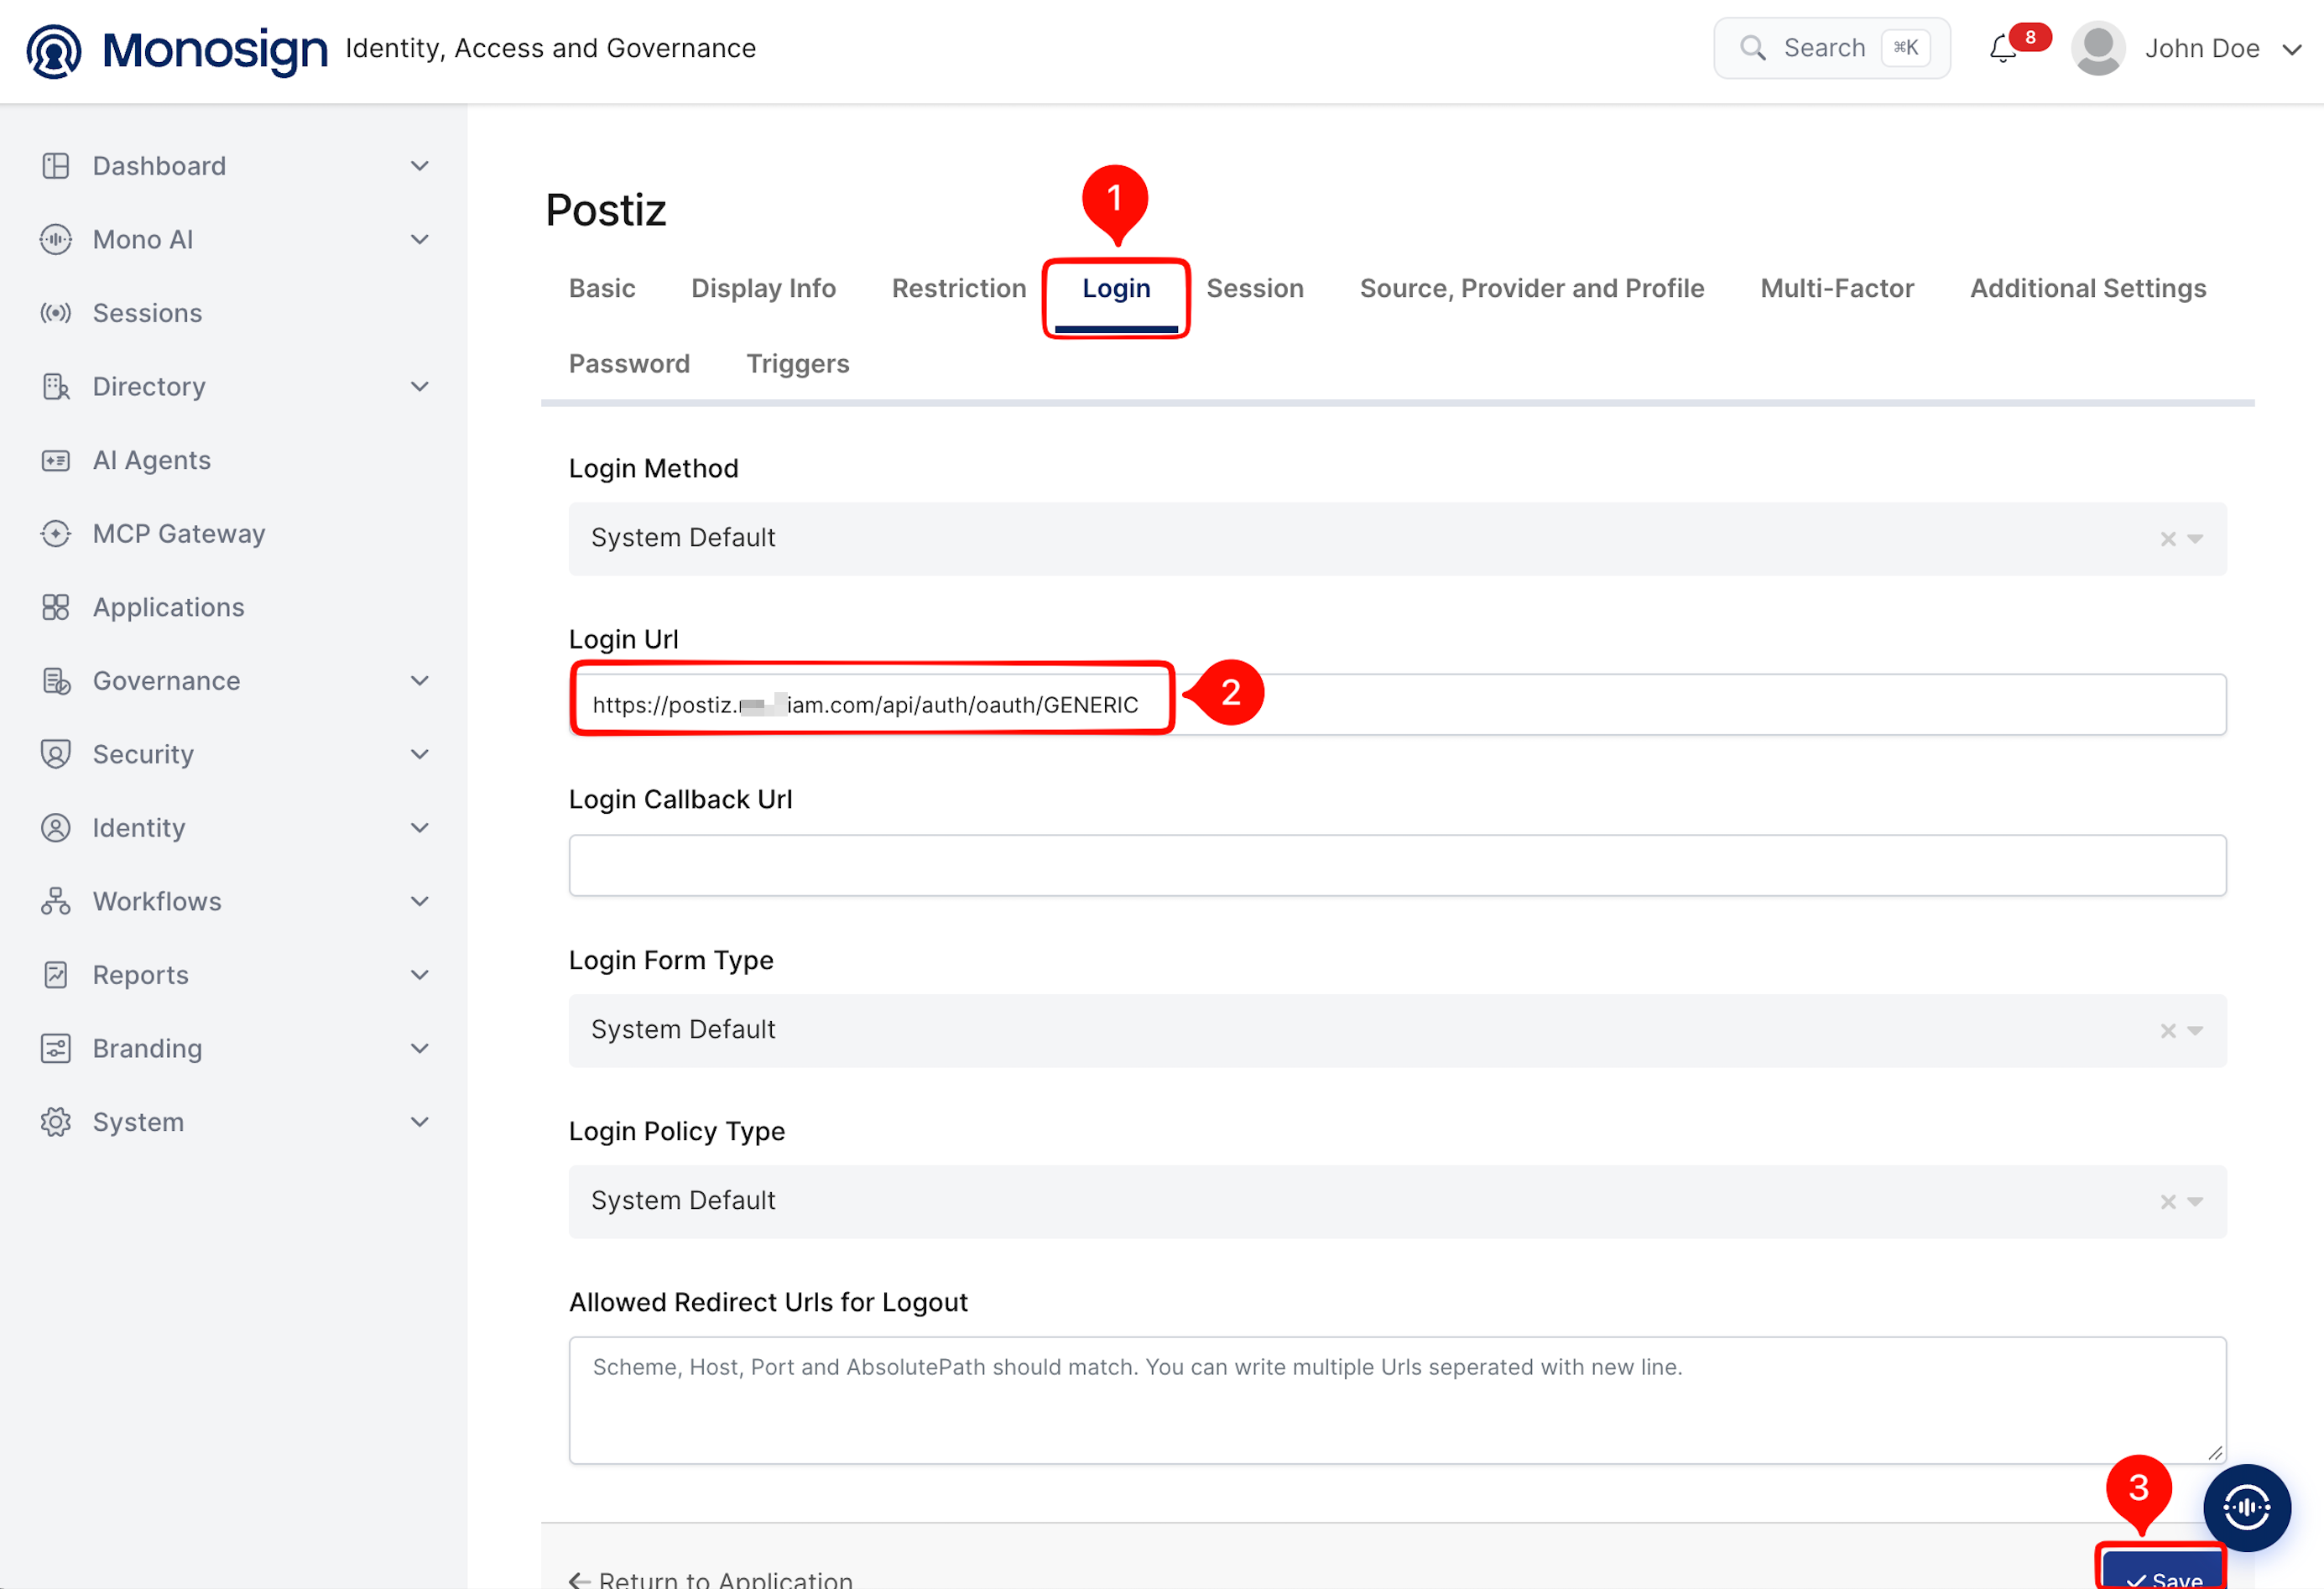
|
Property |
Value |
Description |
|---|---|---|
|
Login Url |
|
Postiz endpoint that starts the OAuth sign-in. When the user opens the Postiz tile in the Monosign portal, the browser goes to this address and Postiz redirects to Monosign. |
3- Configuration Single Sign-On for Postiz
As we mentioned at the start, please check out the Postiz documentation first. Postiz is configured with environment variables only; there is no single sign-on screen in the Postiz interface. In the Docker Compose deployment add the following variables to the environment section of the postiz service and replace the placeholder values.
POSTIZ_GENERIC_OAUTH: 'true'
NEXT_PUBLIC_POSTIZ_OAUTH_DISPLAY_NAME: 'Monosign'
POSTIZ_OAUTH_URL: 'https://<monosign-host>'
POSTIZ_OAUTH_AUTH_URL: 'https://<monosign-host>/openid/authorize'
POSTIZ_OAUTH_TOKEN_URL: 'https://<monosign-host>/openid/token'
POSTIZ_OAUTH_USERINFO_URL: 'https://<monosign-host>/openid/userinfo'
POSTIZ_OAUTH_CLIENT_ID: '<client-id>'
POSTIZ_OAUTH_CLIENT_SECRET: '<client-secret>'
|
Variable |
Value |
Description |
|---|---|---|
|
POSTIZ_GENERIC_OAUTH |
|
Enables the generic OAuth sign-in. Any non-empty value enables it, including |
|
NEXT_PUBLIC_POSTIZ_OAUTH_DISPLAY_NAME |
|
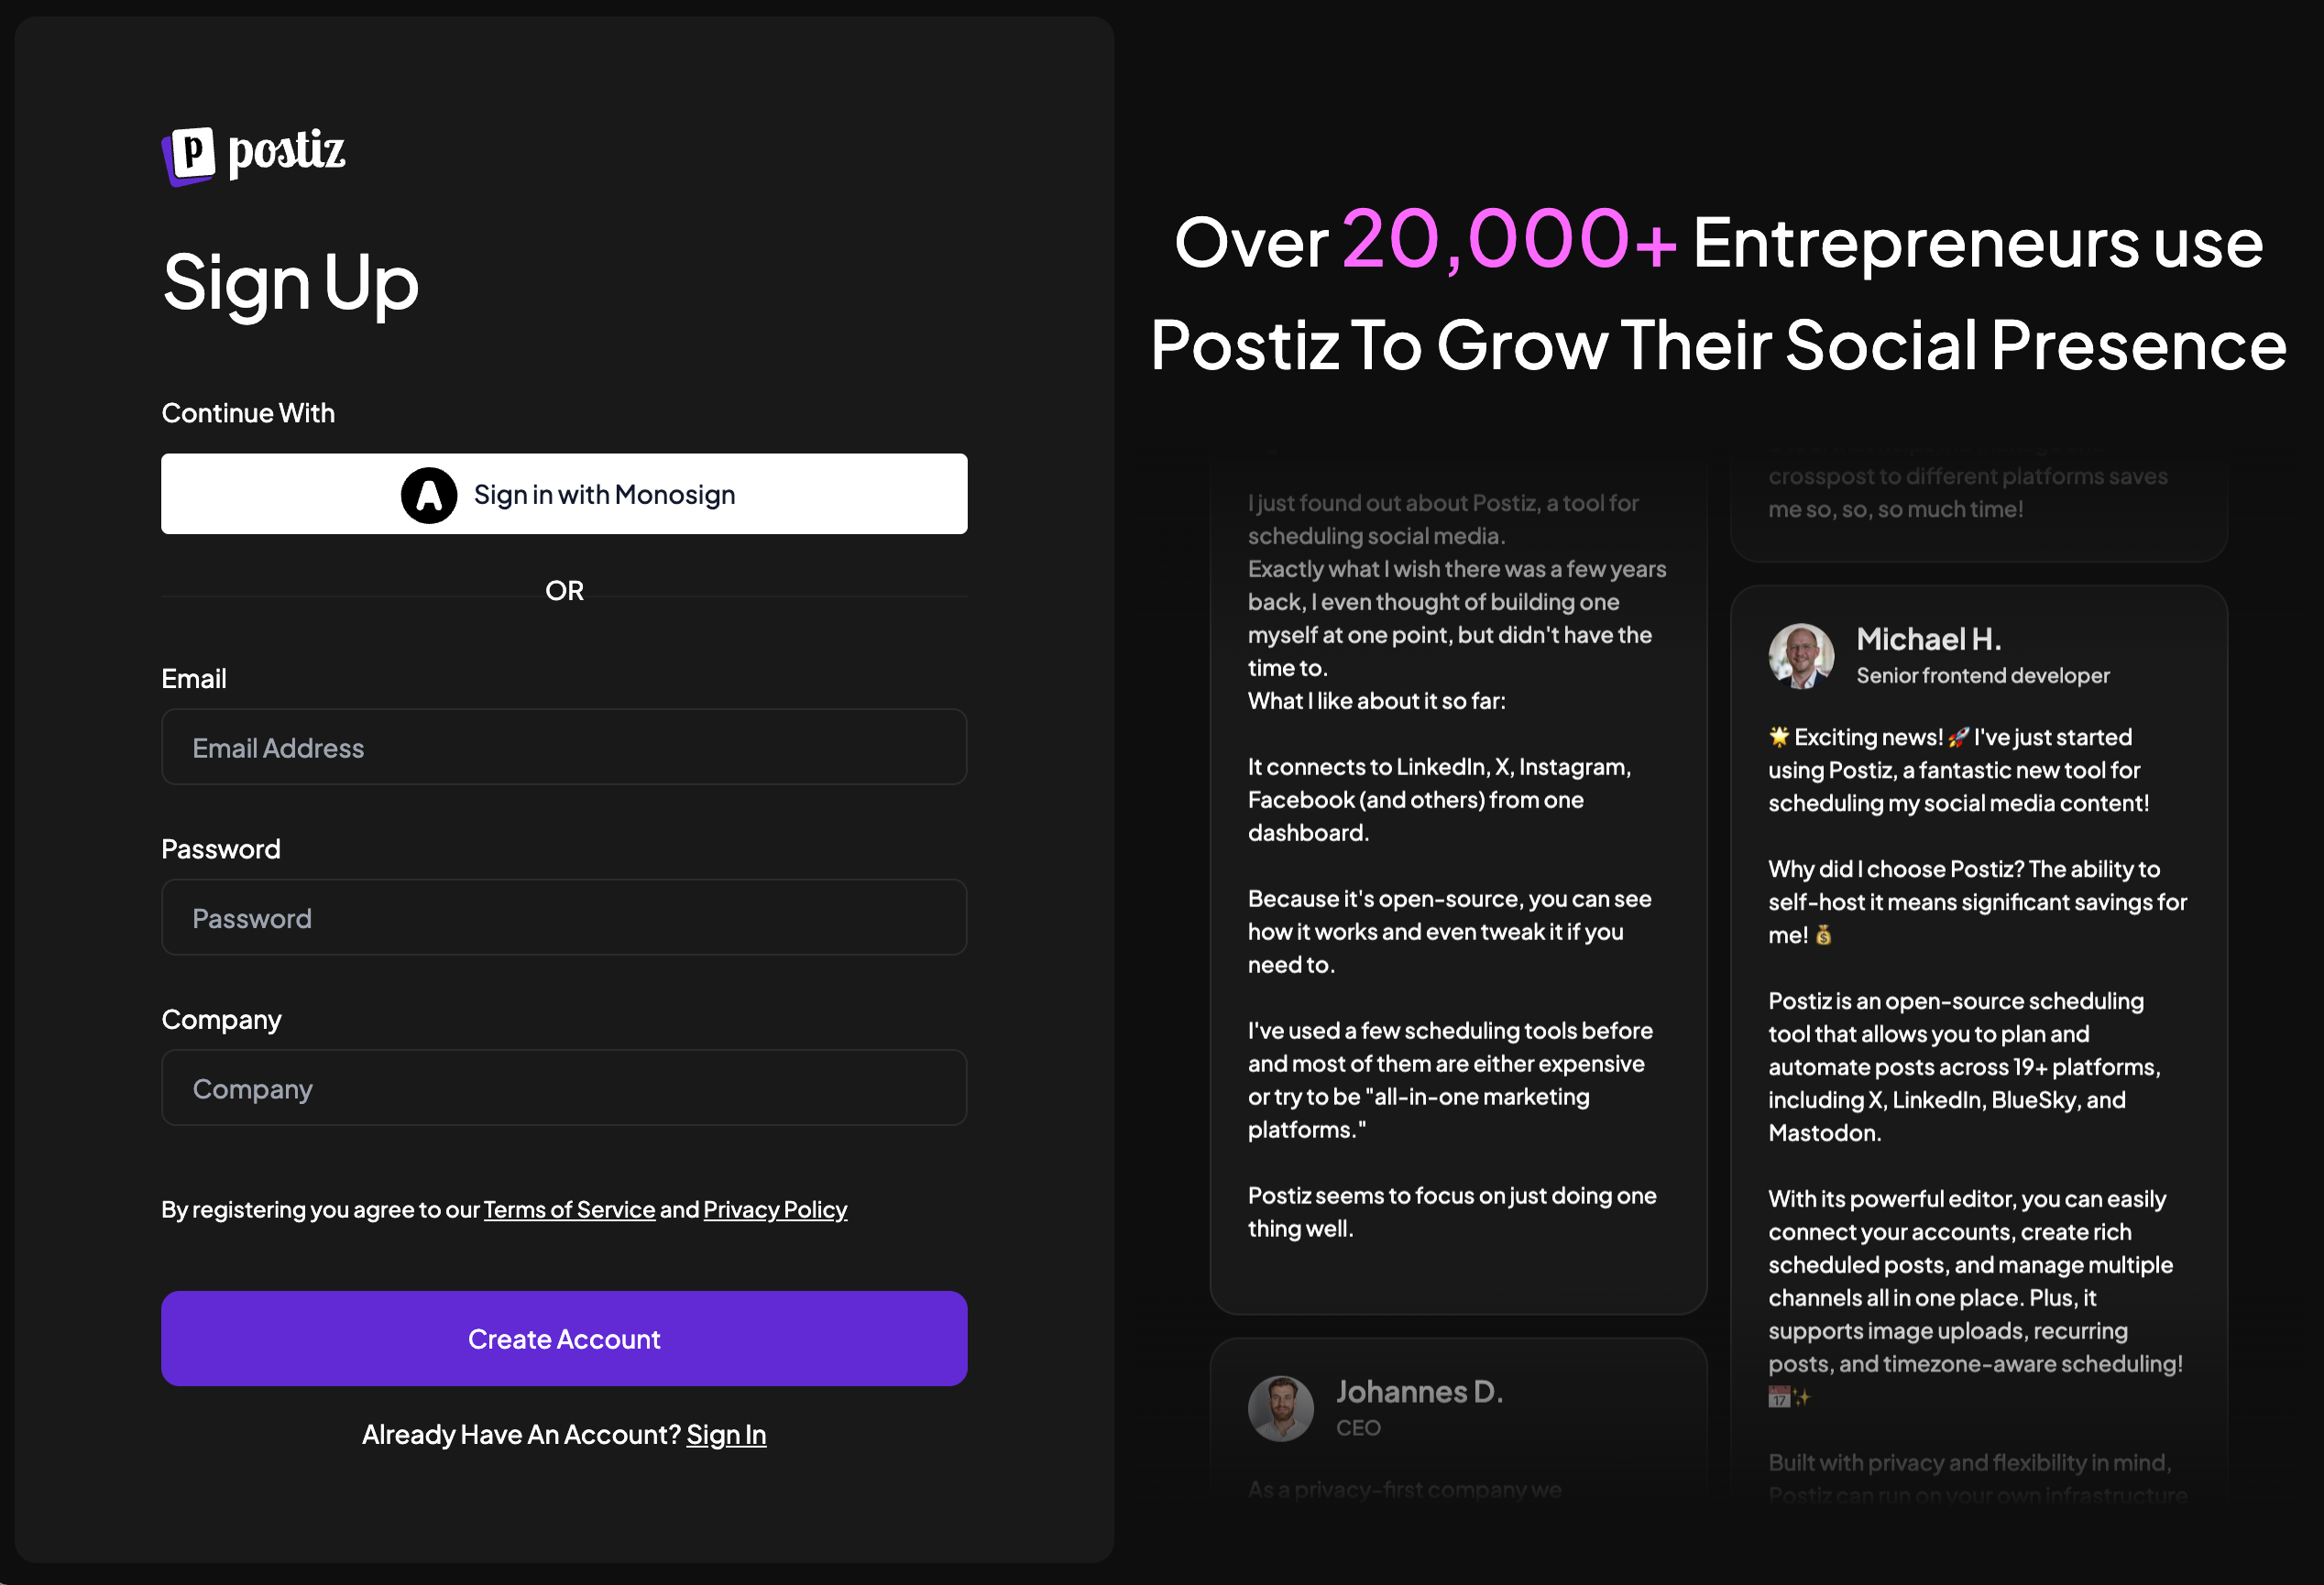
Text of the button on the Postiz sign-in page (“Sign in with Monosign”). |
|
POSTIZ_OAUTH_AUTH_URL |
Auth Url |
Monosign authorization endpoint. |
|
POSTIZ_OAUTH_TOKEN_URL |
Access Token Url |
Monosign token endpoint. |
|
POSTIZ_OAUTH_USERINFO_URL |
User Info Url |
Monosign UserInfo endpoint. Postiz reads the |
|
POSTIZ_OAUTH_CLIENT_ID / POSTIZ_OAUTH_CLIENT_SECRET |
Client Id / Client Secret |
Copied from the Monosign OIDC/OpenID Access Key Details created in the first step. |
|
FRONTEND_URL |
|
Already part of the Postiz configuration. It must be the public address of Postiz; the redirect URI of the sign-in is |
The scope that Postiz sends is fixed in its code as openid profile email. The POSTIZ_OAUTH_SCOPE variable that appears in some examples is not read and cannot be used to change it.
The compose file contains the client secret. Restrict its permissions (for example chmod 600) and do not store it in a shared repository.
Recreate the Postiz container so that the new variables are loaded.
cd /opt/postiz
docker compose up -d postiz
The frontend answers first. The backend of Postiz needs about one to two minutes to start, and the /api address returns 502 until it is ready. After that, the OAuth start address must answer with the Monosign sign-in address:
curl -s http://localhost:4007/api/auth/oauth/GENERIC
# https://<monosign-host>/openid/authorize?client_id=<client-id>&scope=openid+profile+email&response_type=code&state=login-…&redirect_uri=https%3A%2F%2Fpostiz.example.com%2Fsettings
4- Assign a User to the Postiz Application
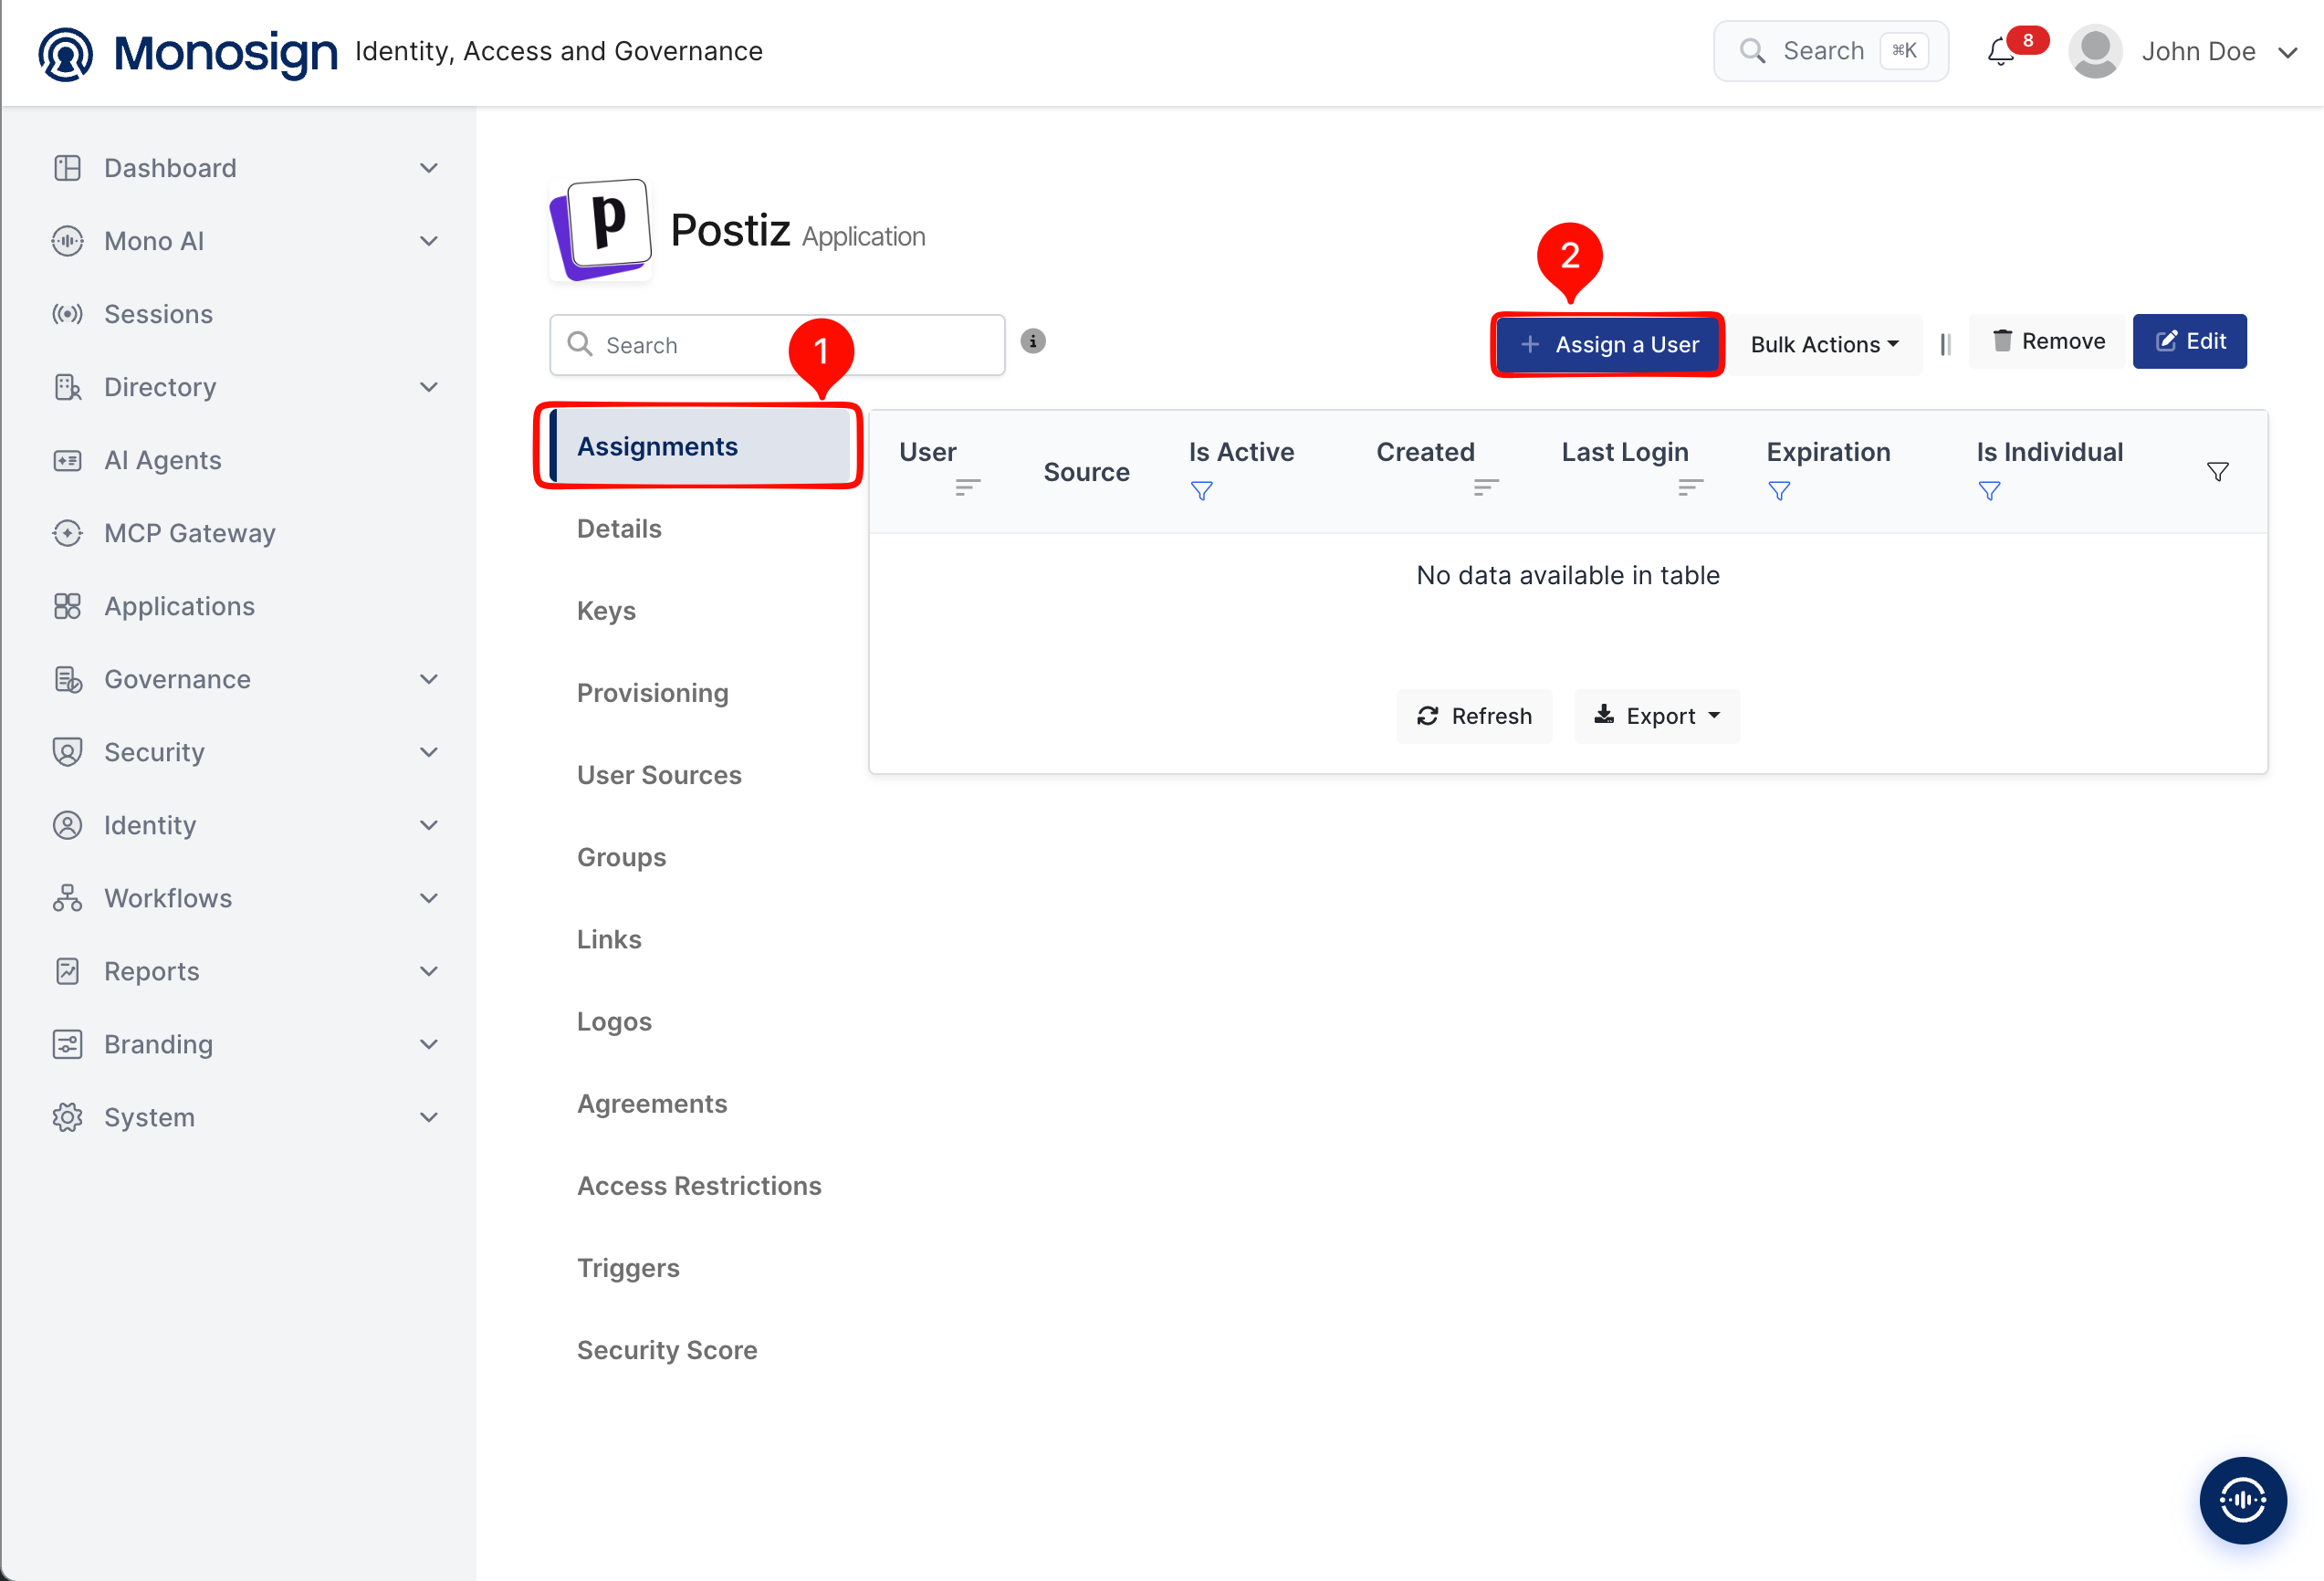
Please follow the below instructions on how to assign a user to the Postiz application. Open the application, click the Assignments tab and click Assign a User.
Search and select the users who can sign in to Postiz, check the Expiration Date and click Save. You can select more than one user.
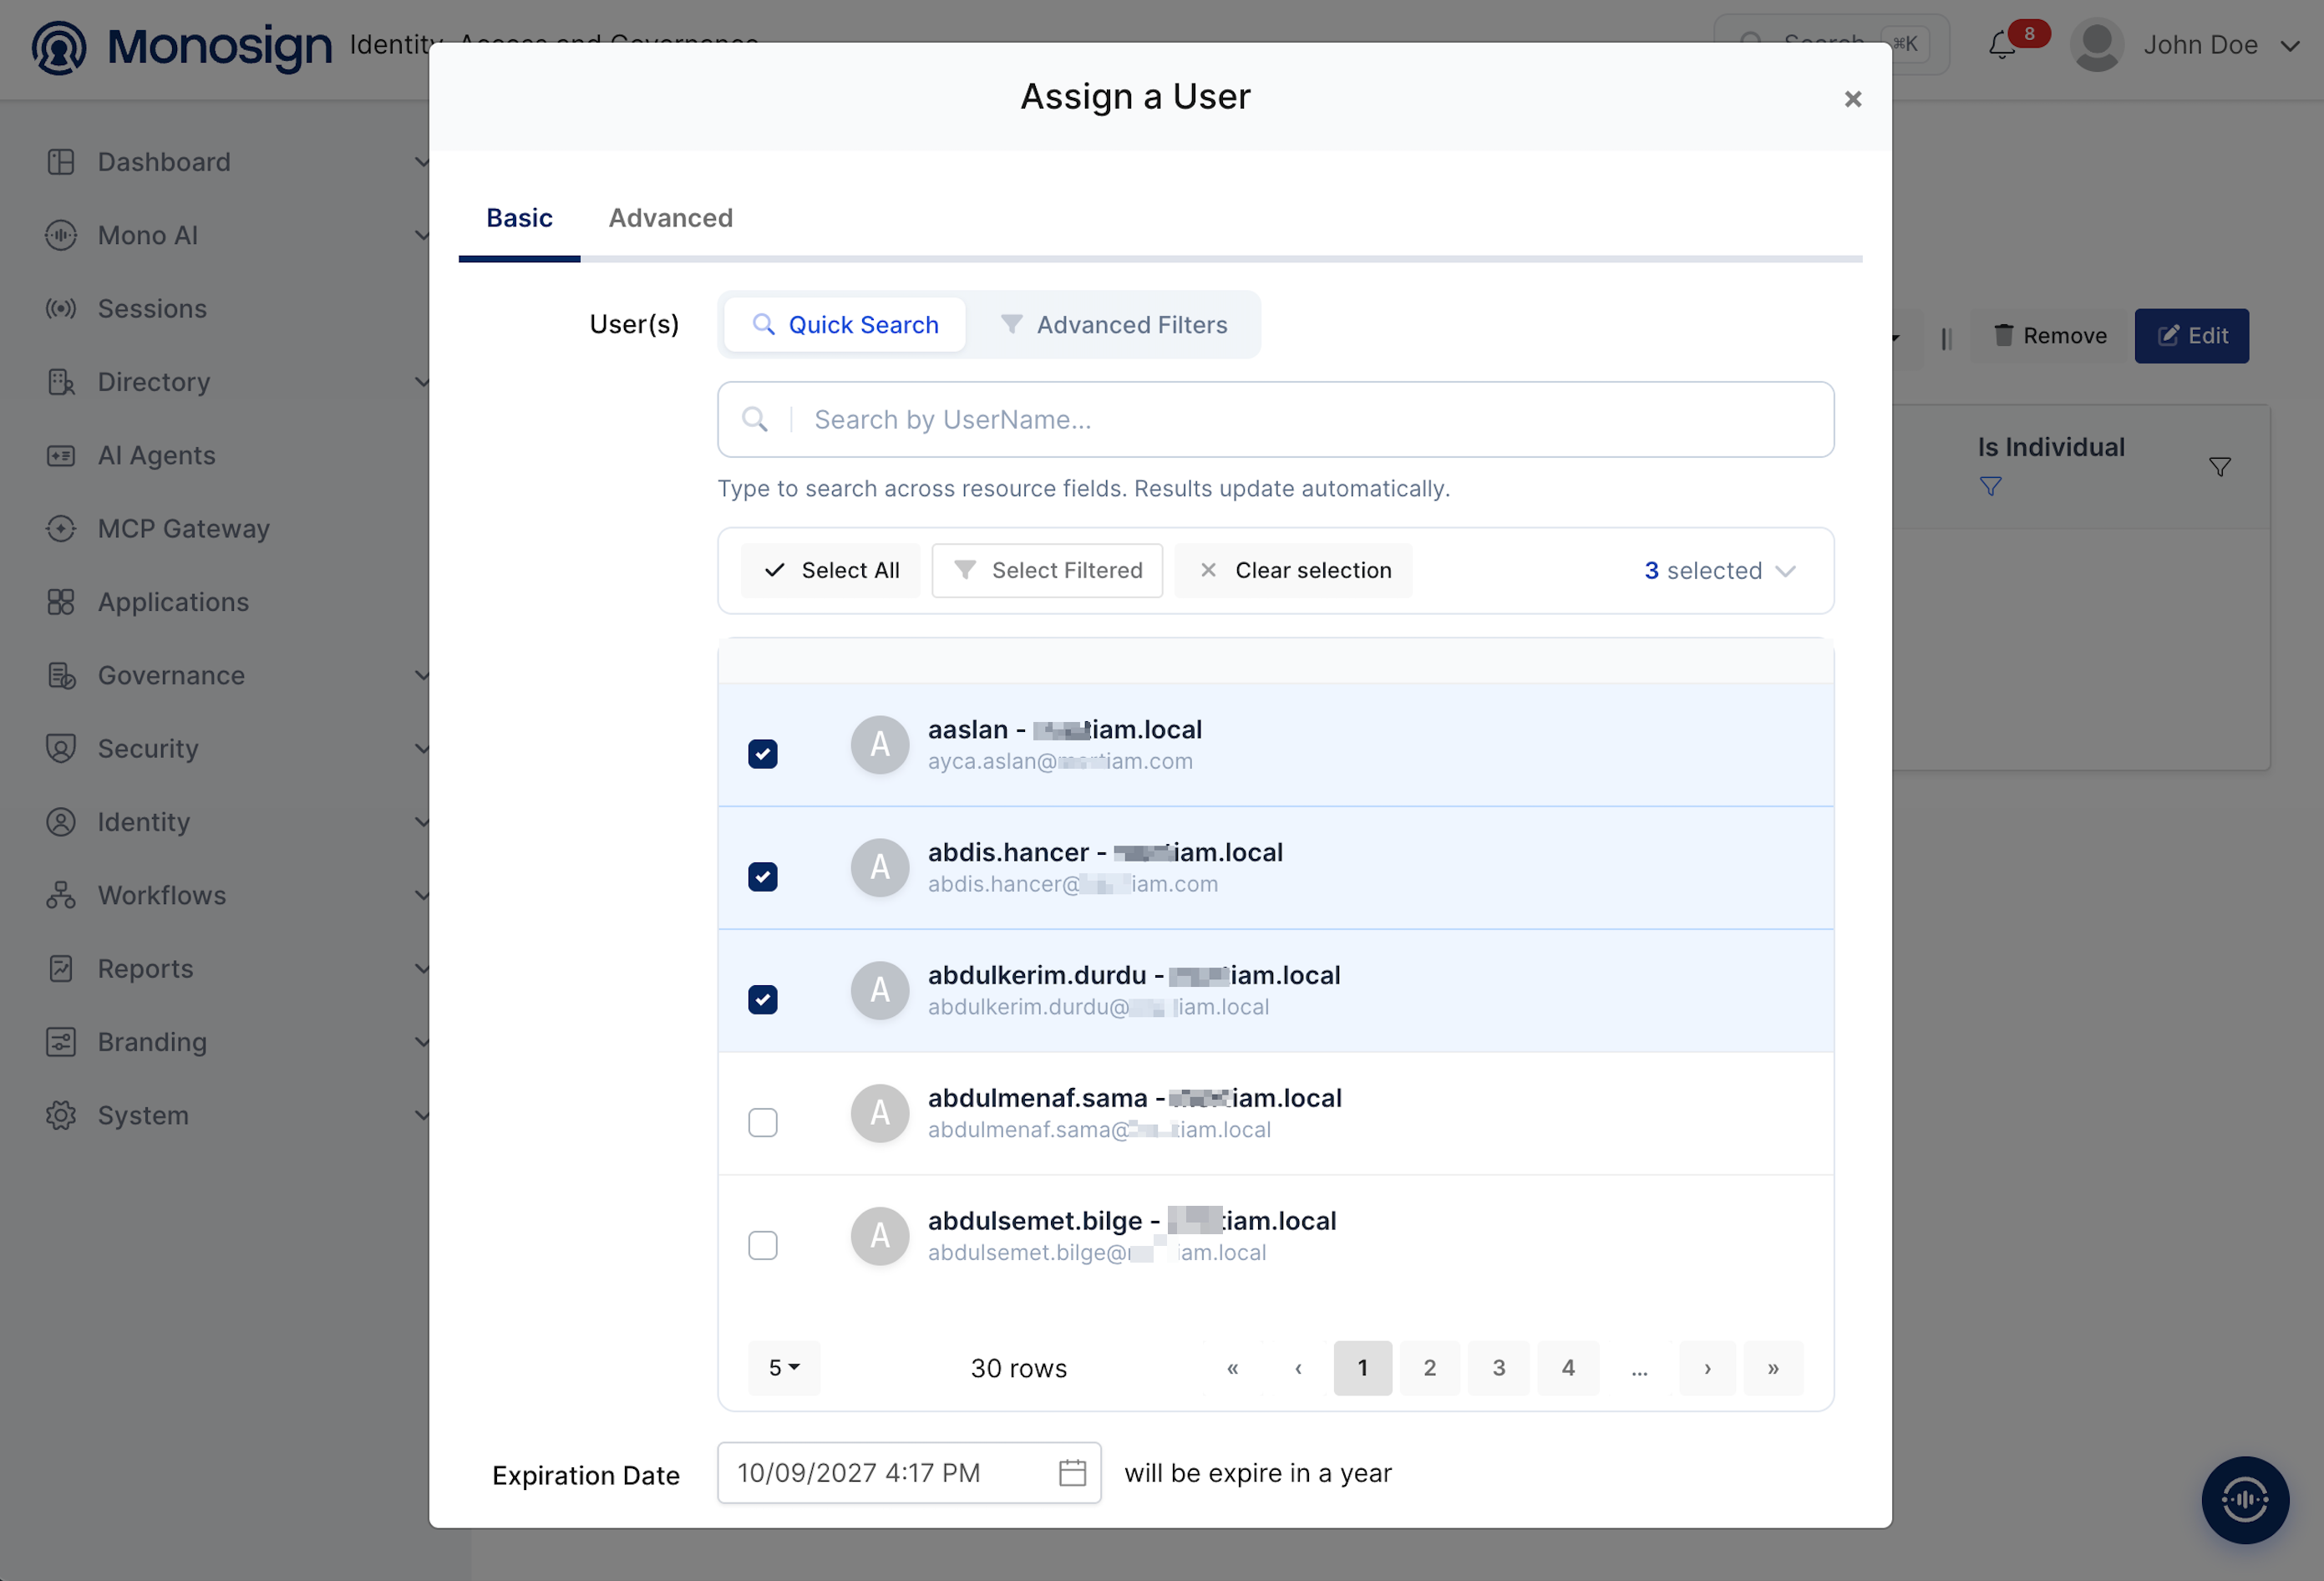
|
Property |
Value |
Description |
|---|---|---|
|
User(s) |
Selected users |
Users who can sign in to Postiz with Monosign. Use the search box to find a user quickly. |
|
Expiration Date |
Default one year |
The assignment expires on this date. |
Monosign decides who can reach Postiz with the application assignments. DISABLE_REGISTRATION of Postiz closes the e-mail and password sign-up after the first organization is created, but it does not block the single sign-on users; a user who signs in with Monosign gets a Postiz account automatically.
5- Sign In Test
Now try to log in to Postiz using Monosign SSO.
-
Open a new browser window (or a private window) and type the Postiz address, for example
https://postiz.example.com. -
Click Sign in with Monosign on the Postiz page.
-
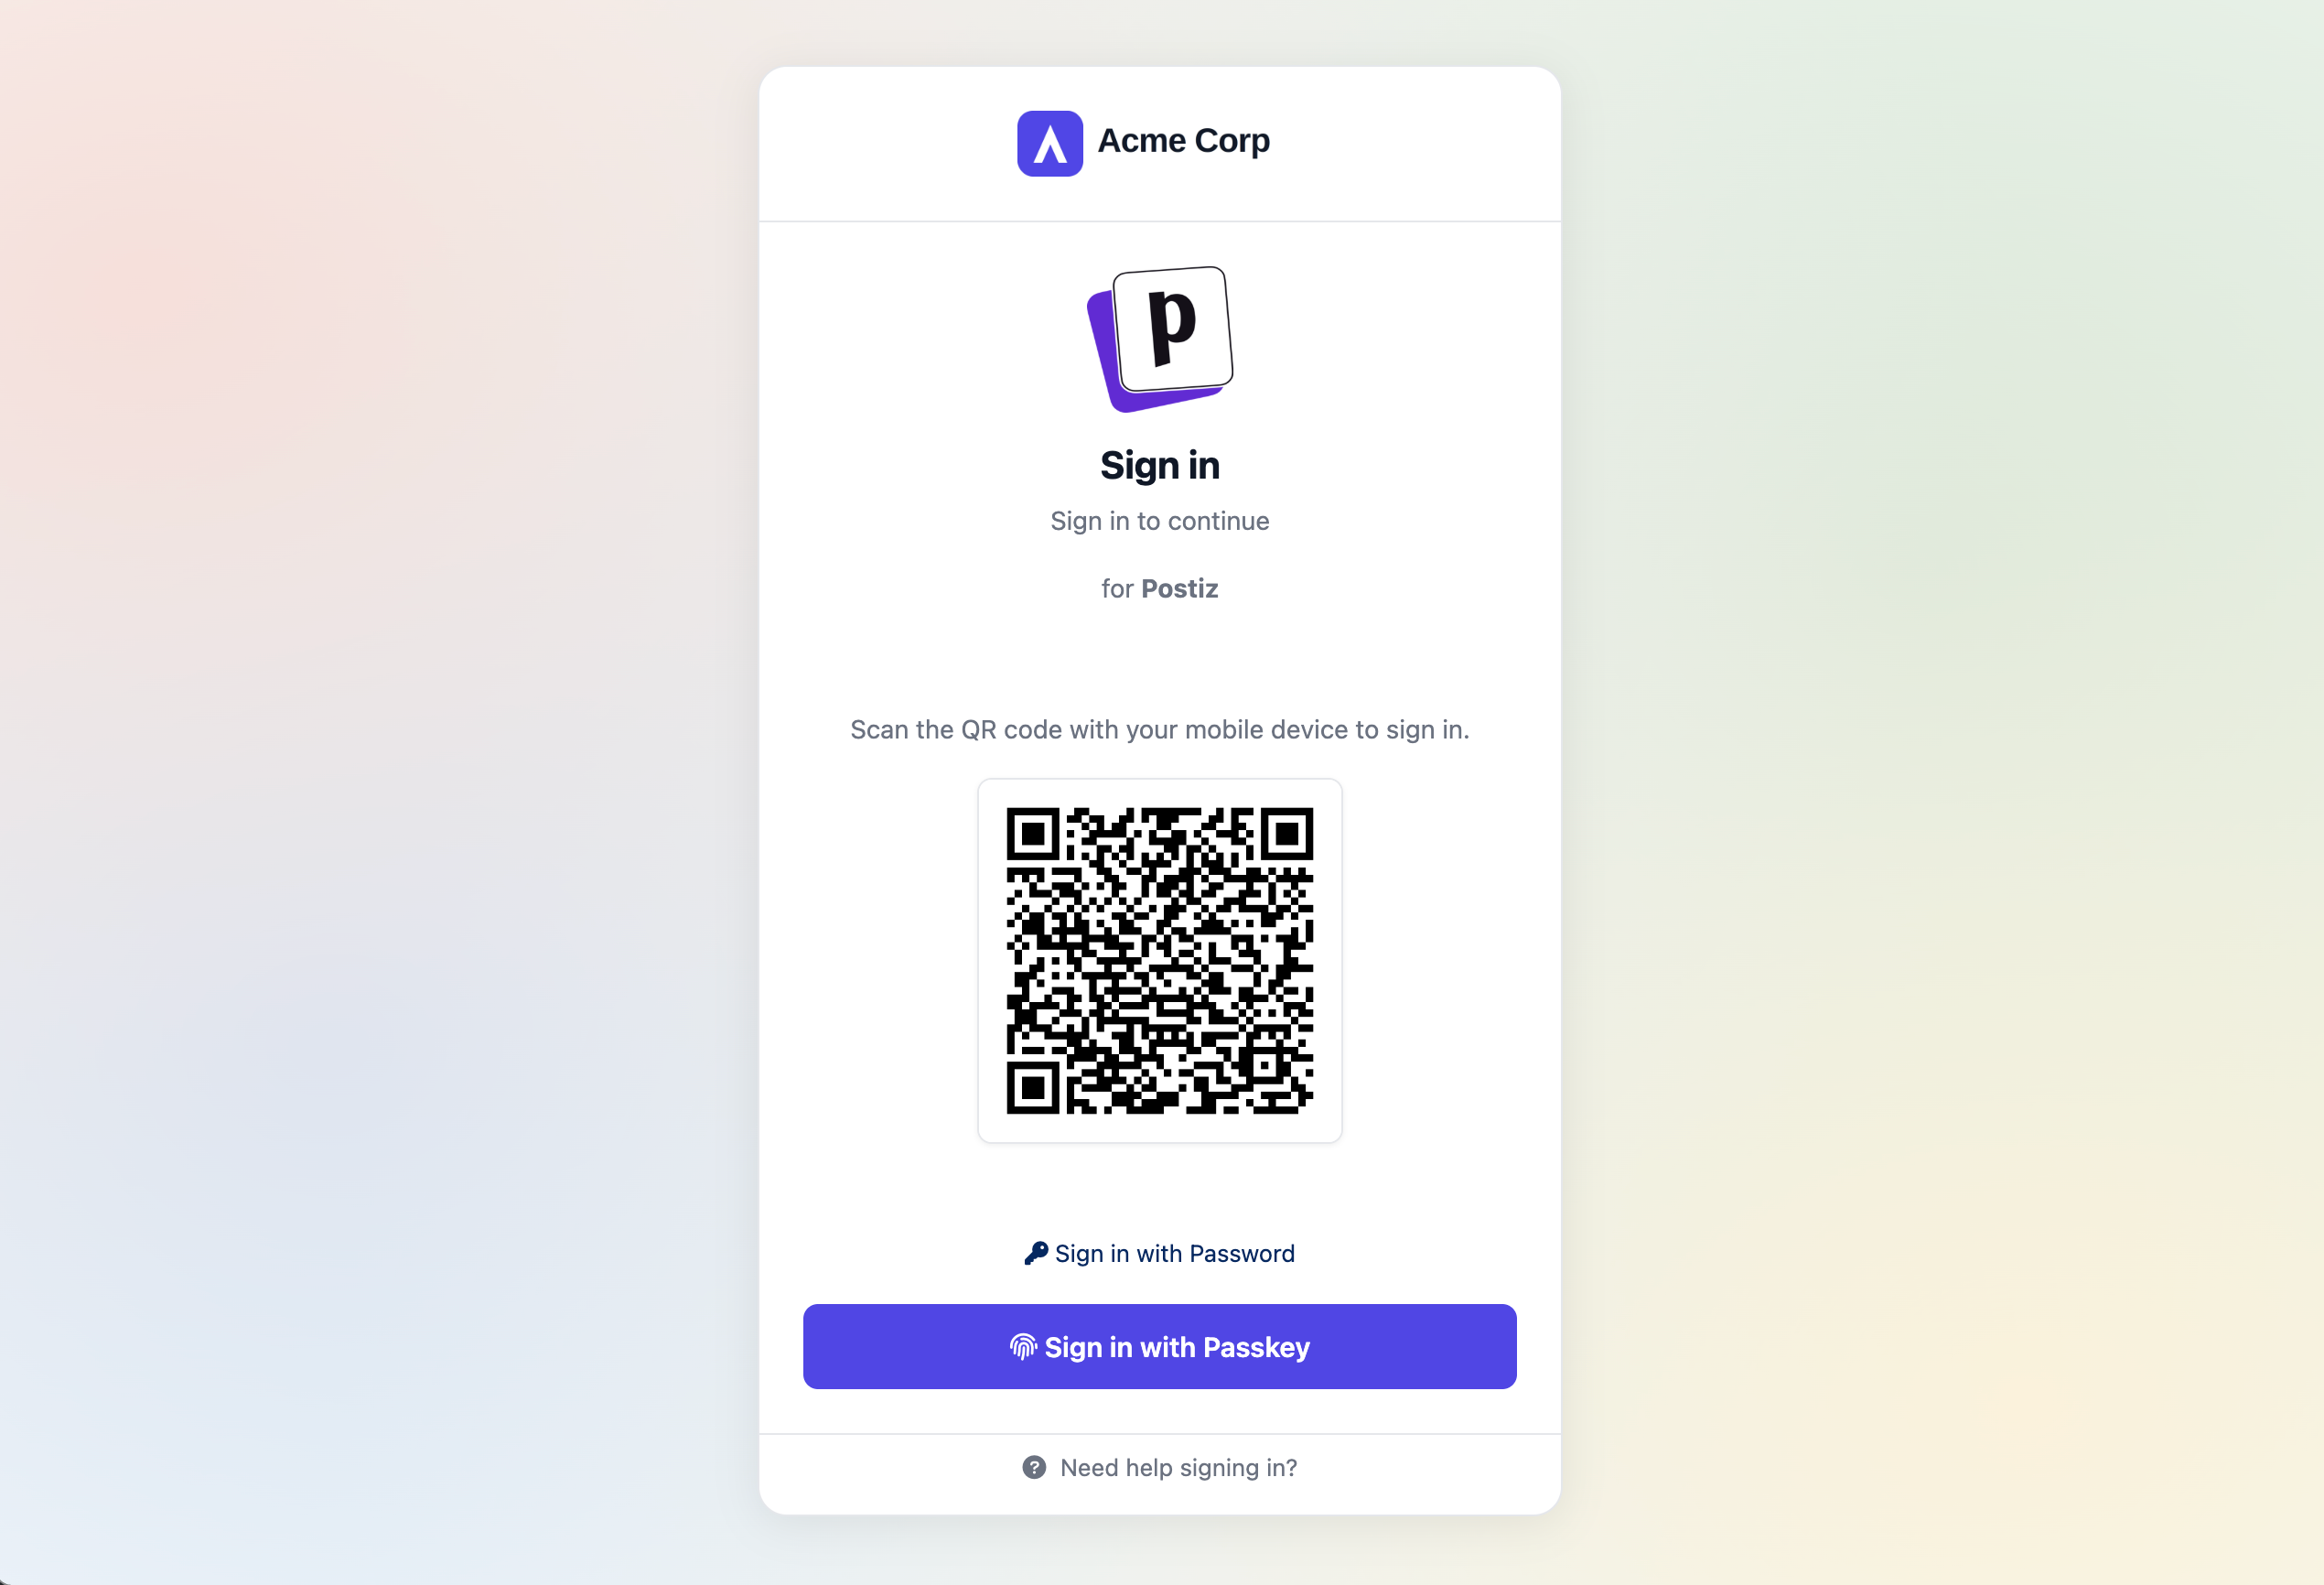
Postiz redirects the browser to the Monosign sign-in page of the Postiz application. You can log in passwordless with your QR code (Monofor Identity), with a Passkey or with your user name and password (Sign in with Password).
-
After the sign-in Monosign redirects the browser back to Postiz (
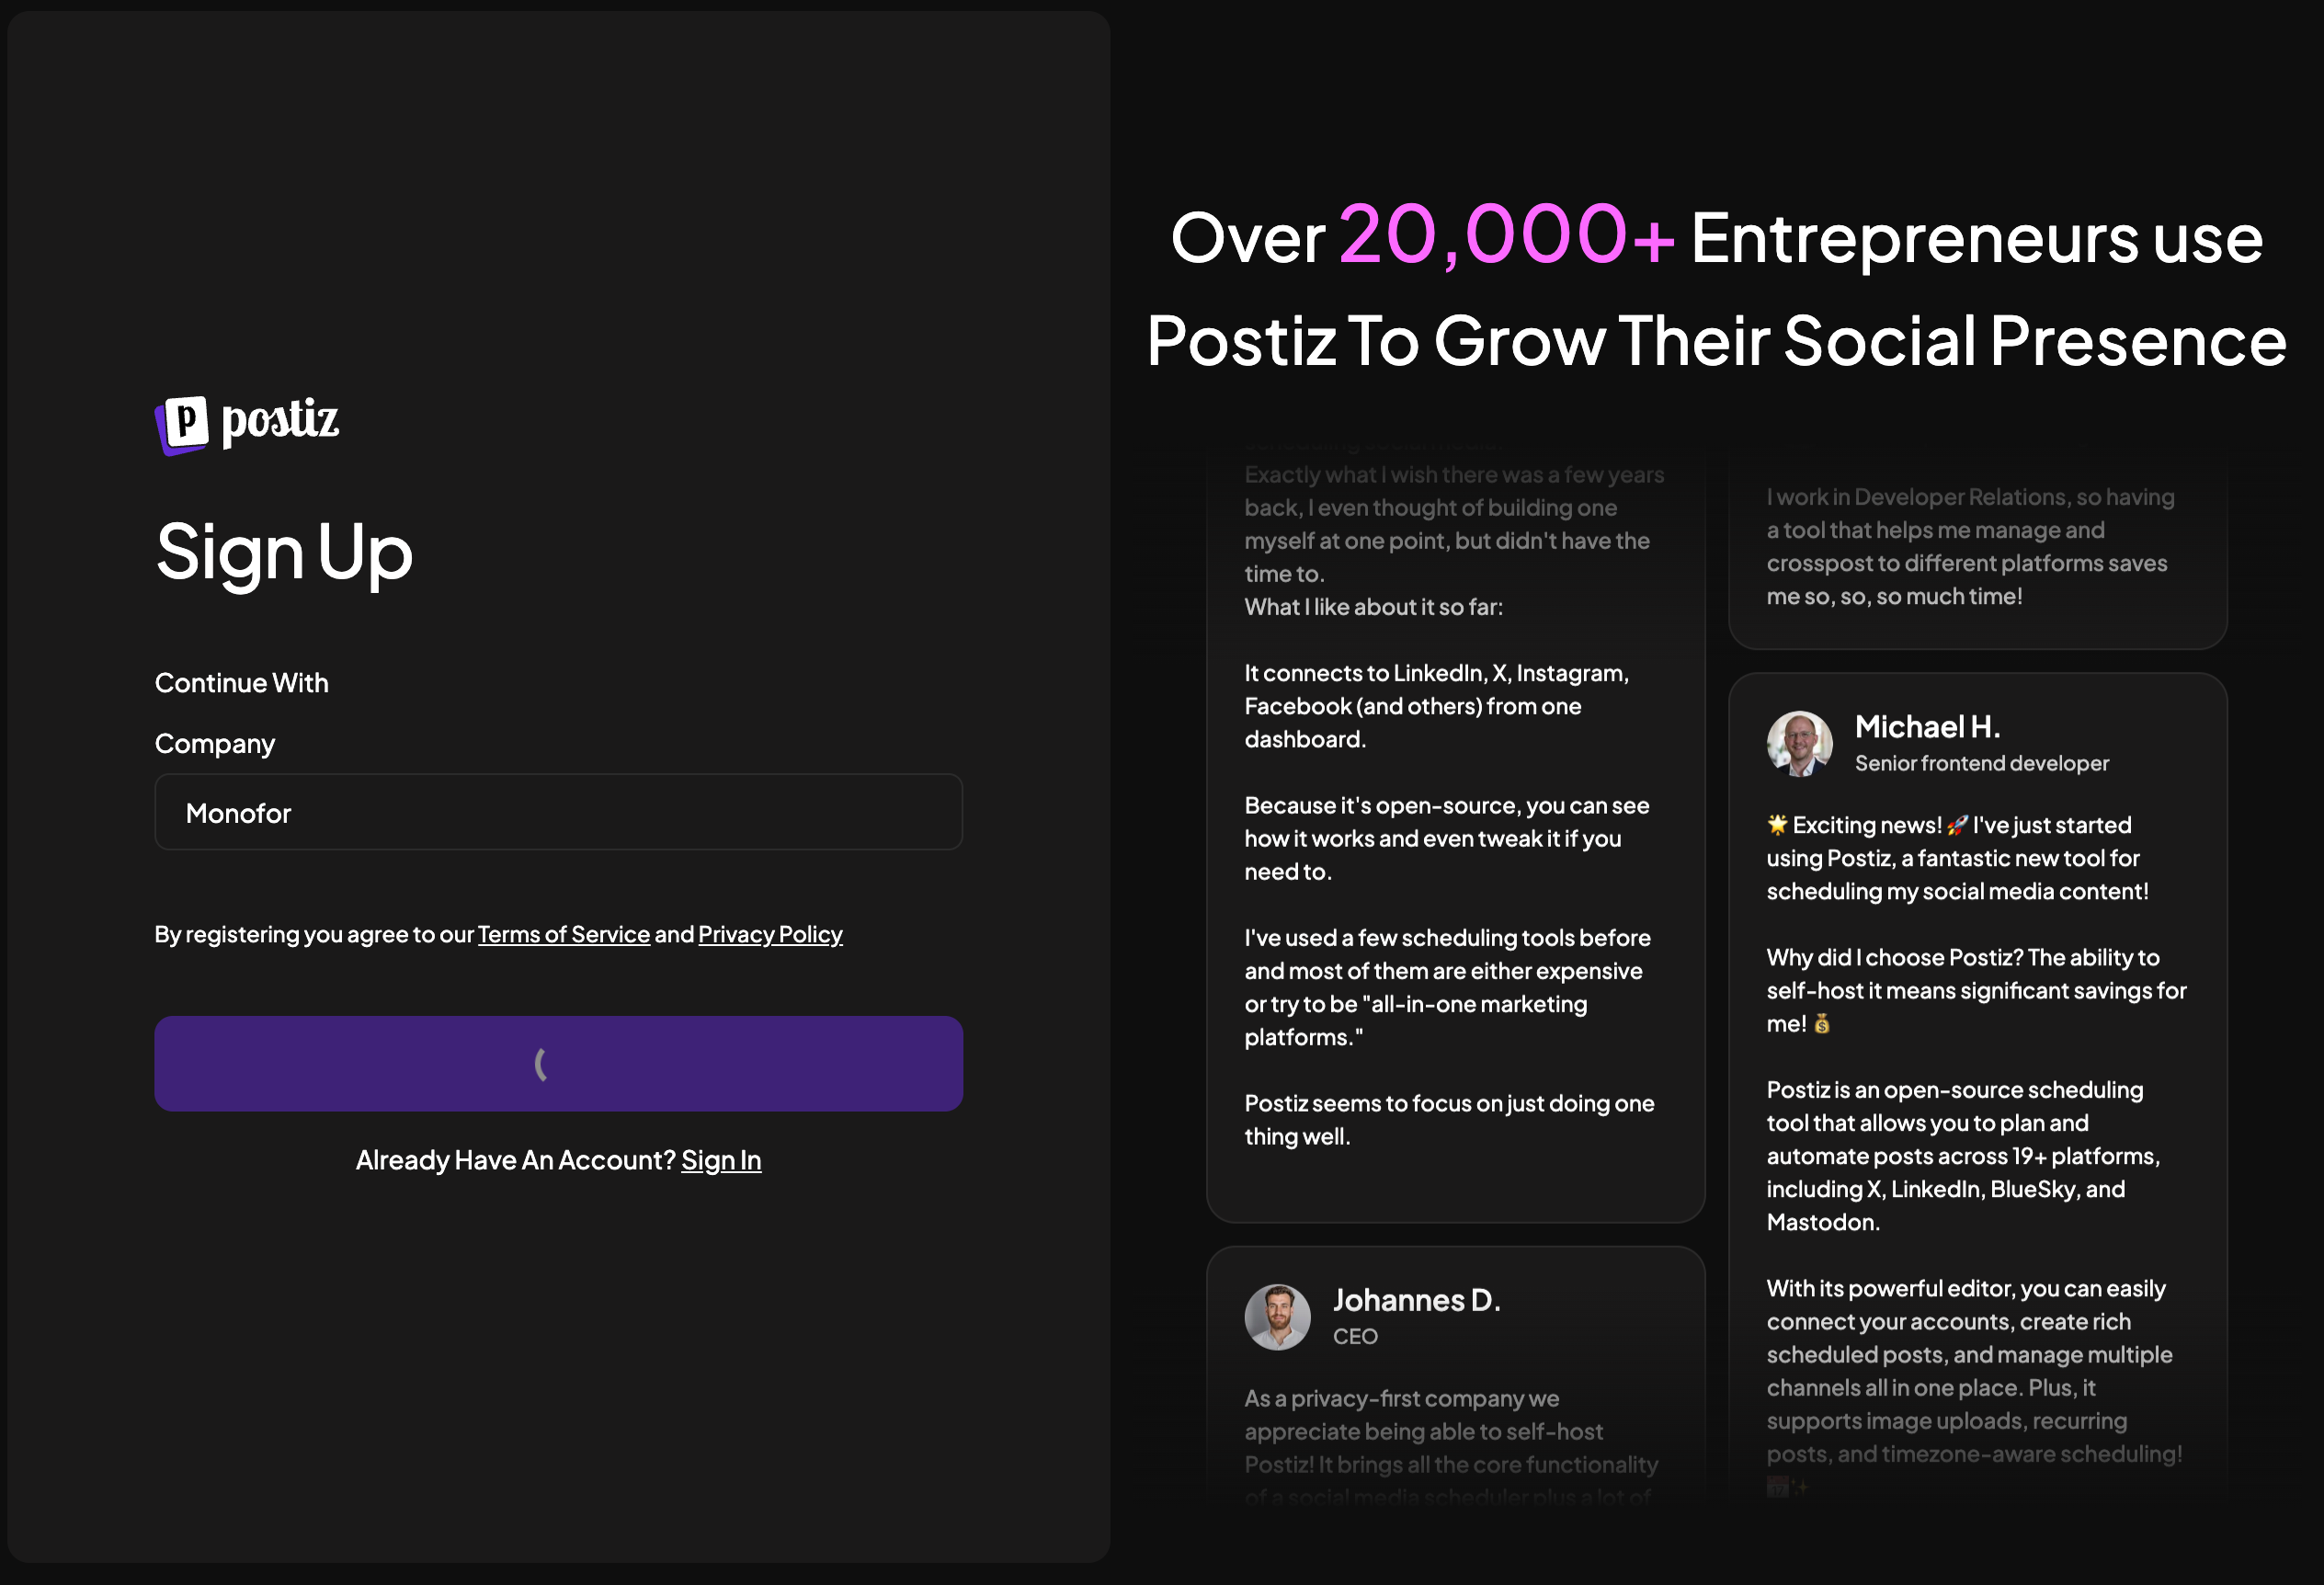
/settings). On the first sign-in Postiz continues with the sign-up form, shows the company name and creates the account of the user.
Troubleshooting
|
Symptom |
Cause |
Solution |
|---|---|---|
|
The “Sign in with Monosign” button is not shown |
|
Add the variables from step 3 and run |
|
|
The Postiz backend starts after the frontend. |
Wait one to two minutes and try again. |
|
Monosign shows a redirect URI error after the sign-in |
The redirect URI that Postiz sends does not exactly match the Allowed Redirect URIs. |
Make sure that |
|
The sign-in succeeds on Monosign but Postiz does not log the user in |
The UserInfo response does not contain the |
Check the Client Id and Secret in the compose file. If the |
|
A user cannot sign in |
The user is not assigned to the application. |
Assign the user in step 4. |
|
Single sign-on stays active after setting |
Postiz only checks whether the variable has a value. |
Delete the variable and recreate the container. |
|
SAML sign-in is required |
Postiz supports OAuth 2.0 / OpenID Connect only. |
Use the OIDC/OpenID key of Monosign as described in this document. |
After completing the configuration on Postiz and Monosign, it is better to test in a new private browser window if the OIDC/OpenID SSO doesn’t work, because old session cookies of the Postiz address may cause errors.