
A dynamic secret creates a credential for each request and removes it when the lease ends: a PostgreSQL, MSSQL or MySQL login, or a Kubernetes service account token.
|
Applies to |
Who can do this |
|---|---|
|
Monopam v2026.10 |
Administrators define dynamic secrets. Machine identities request leases. |
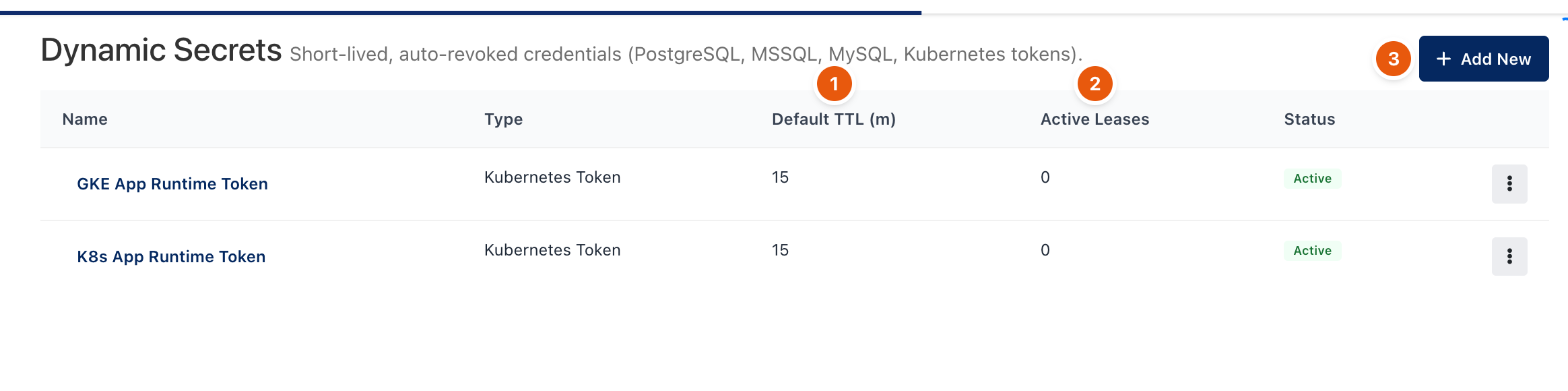
Figure 1. Secrets → Dynamic.
Define a dynamic secret
-
Click Add New (3), choose the type and the project it belongs to.
-
Enter the connection to the database or cluster. For databases, optionally write your own creation and revocation statements with
{{username}},{{password}}and{{expiration}}. -
Set the Default TTL (1) and the Max TTL in minutes.
Leases
A machine identity with a grant on the project requests a lease through the API (POST /api/v1/dynamic/<name>/lease) and receives a new login or token. Active Leases (2) counts the live ones. Monopam revokes expired leases every minute; an administrator can revoke one early from the Leases view.
Kubernetes token leases cannot be renewed; request a new lease. A revoked Kubernetes token may still work for about 10 seconds because the cluster caches token checks.
Related
-
Identities and the CLI
-
Projects and environments