This document explains how to implement Monosign with ChiefOnboarding, the open-source employee onboarding platform. It covers Single Sign-On with OpenID Connect (OIDC), which ChiefOnboarding provides through the django-allauth library. ChiefOnboarding discovers the Monosign addresses from the OIDC discovery document, so the OIDC/OpenID access key of Monosign is used. Before you continue, it is better to start with the ChiefOnboarding OIDC documentation.
This configuration is done with the ChiefOnboarding Docker image (chiefonboarding/chiefonboarding:latest, October 2026) and postgres:16 running on Docker Compose. If your ChiefOnboarding version or deployment type is different, please check the ChiefOnboarding documentation.
ChiefOnboarding supports OpenID Connect only. SAML is not available in ChiefOnboarding. There is no single sign-on screen in the ChiefOnboarding interface; the provider is configured with environment variables.
Monofor has no responsibility to do ChiefOnboarding configurations. If you need support please contact the ChiefOnboarding community or your ChiefOnboarding support provider.
📑 Instructions
This documentation contains 5 main steps for integration.
-
Creating an application on Monosign
-
Configuring the OIDC/OpenID settings on Monosign
-
Assign a user to the ChiefOnboarding application
-
Configuration Single Sign-On for ChiefOnboarding
-
Sign In Test
1- Creating an Application on Monosign
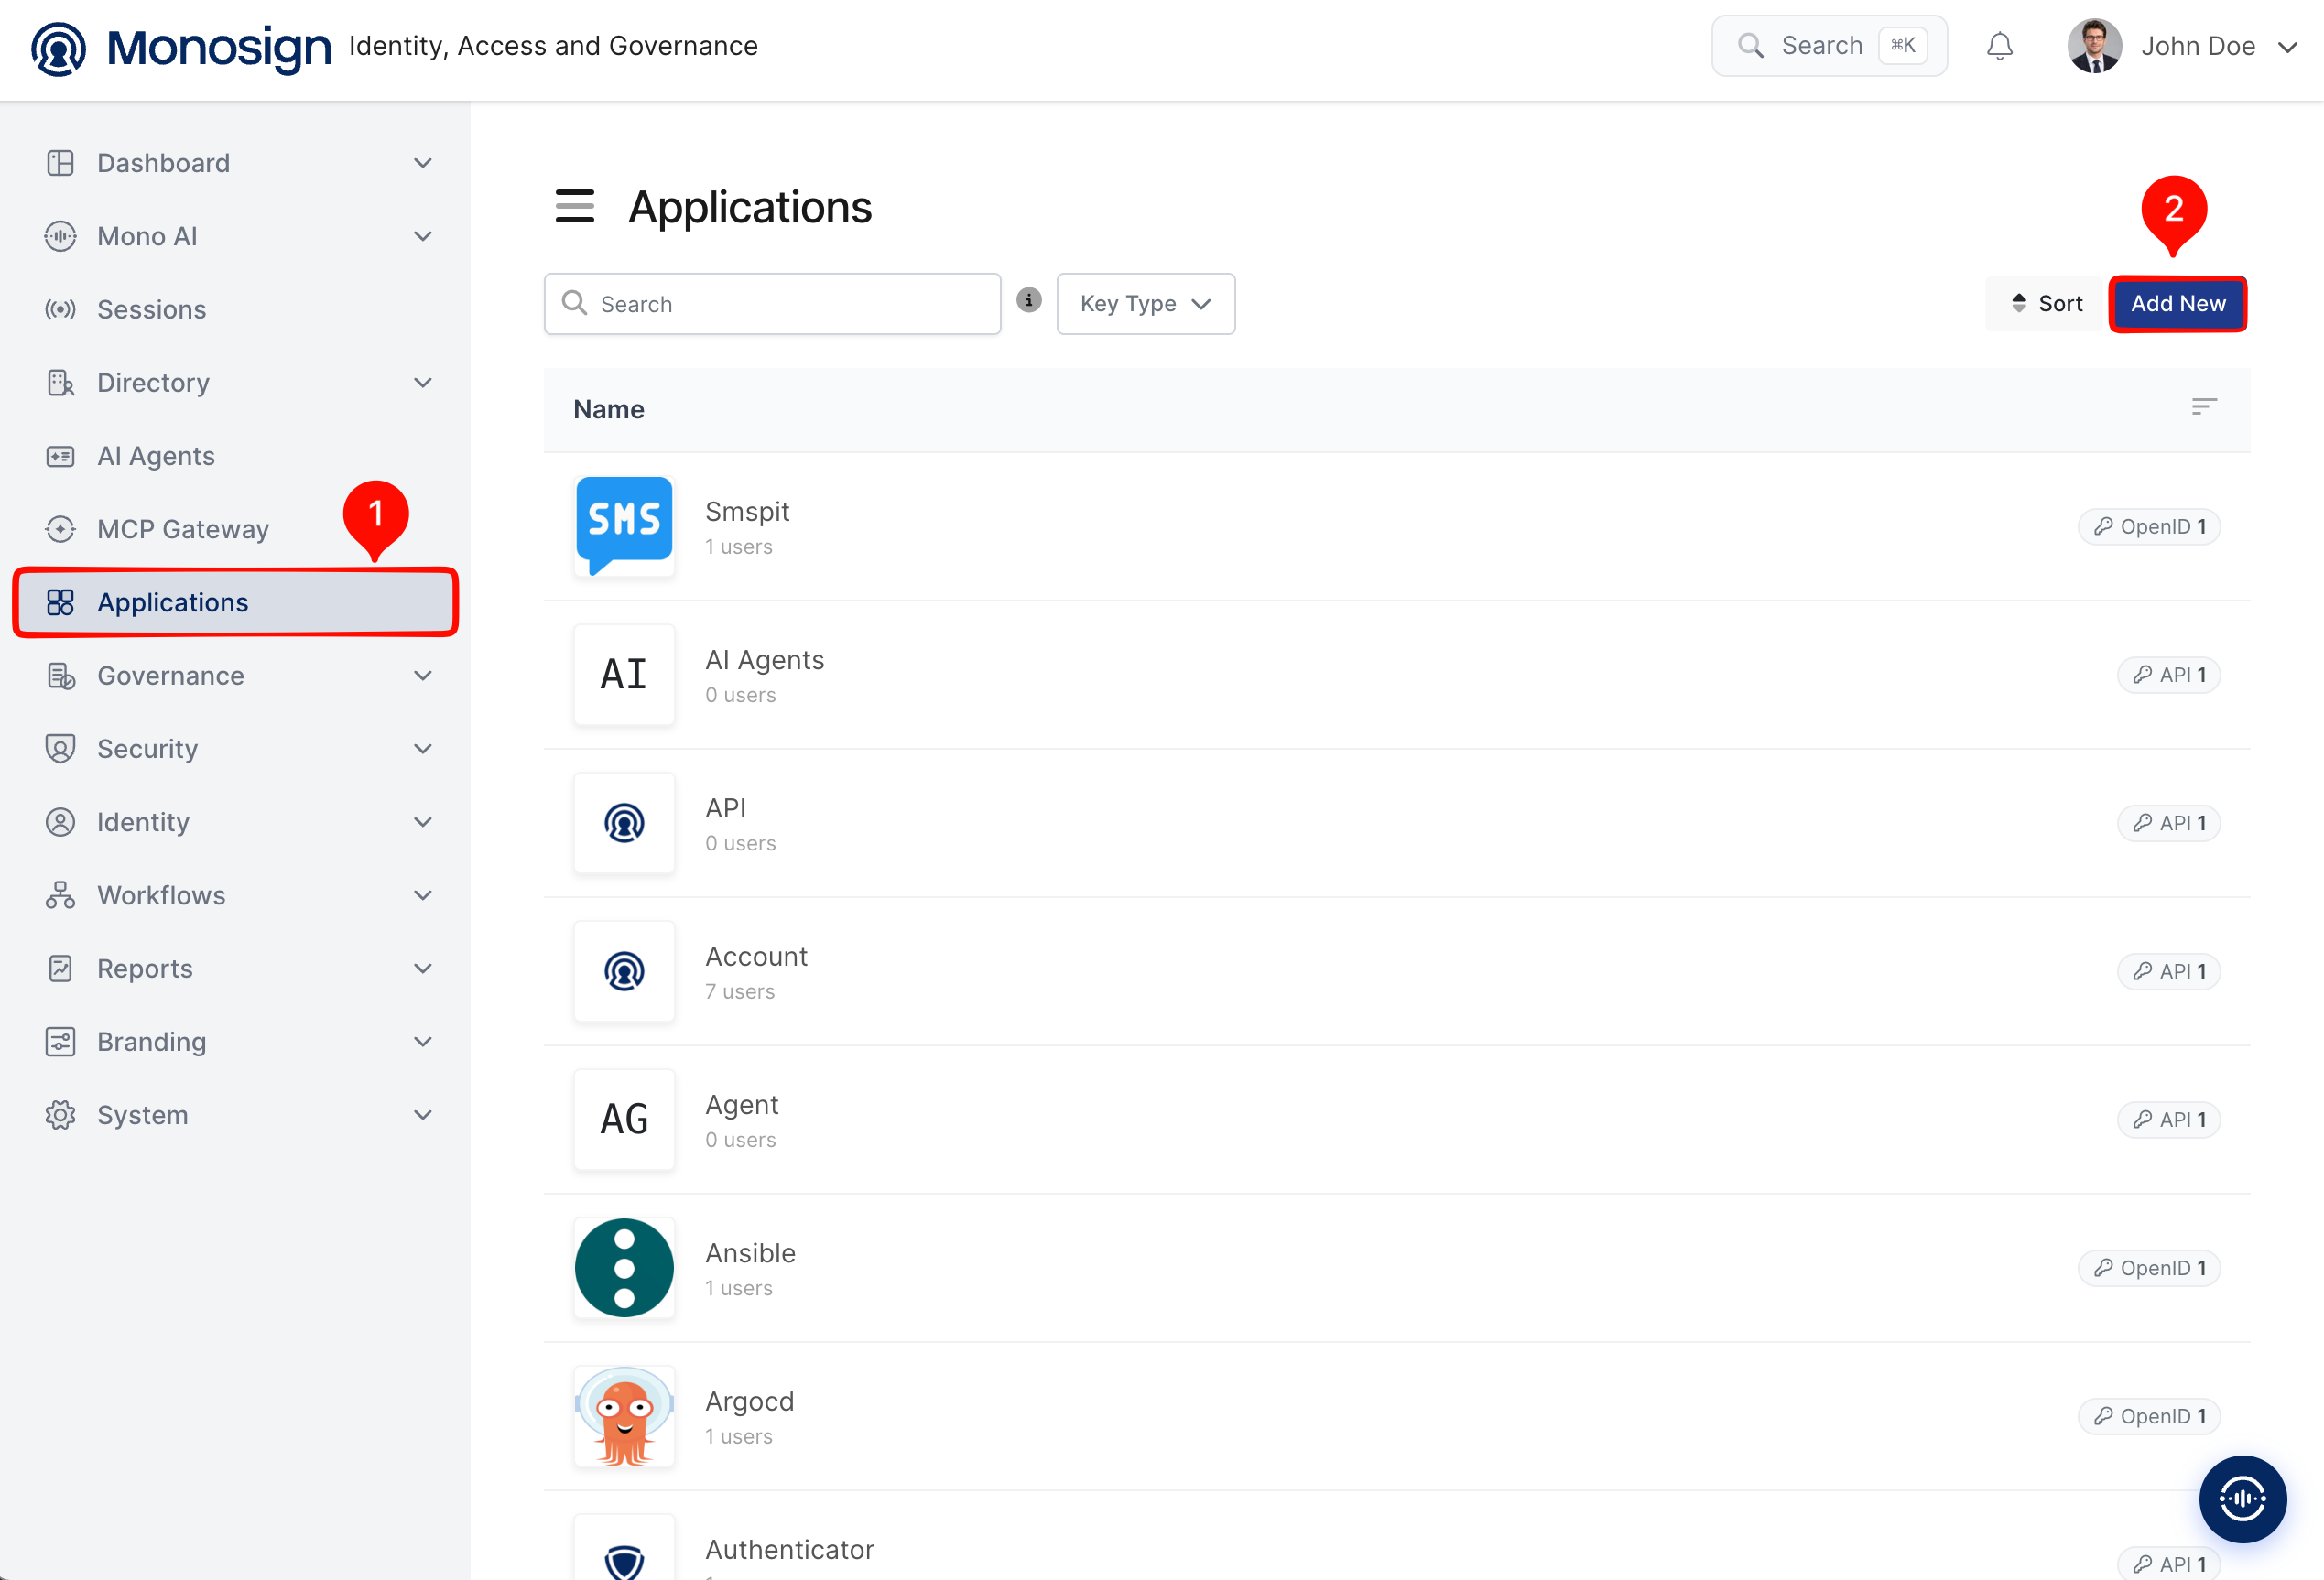
Create your application on Monosign first. Open the Applications page from the left menu and click Add New.
ChiefOnboarding is not in the application catalog, so click Create from scratch, fill in the application details on the Application tab and click Next.
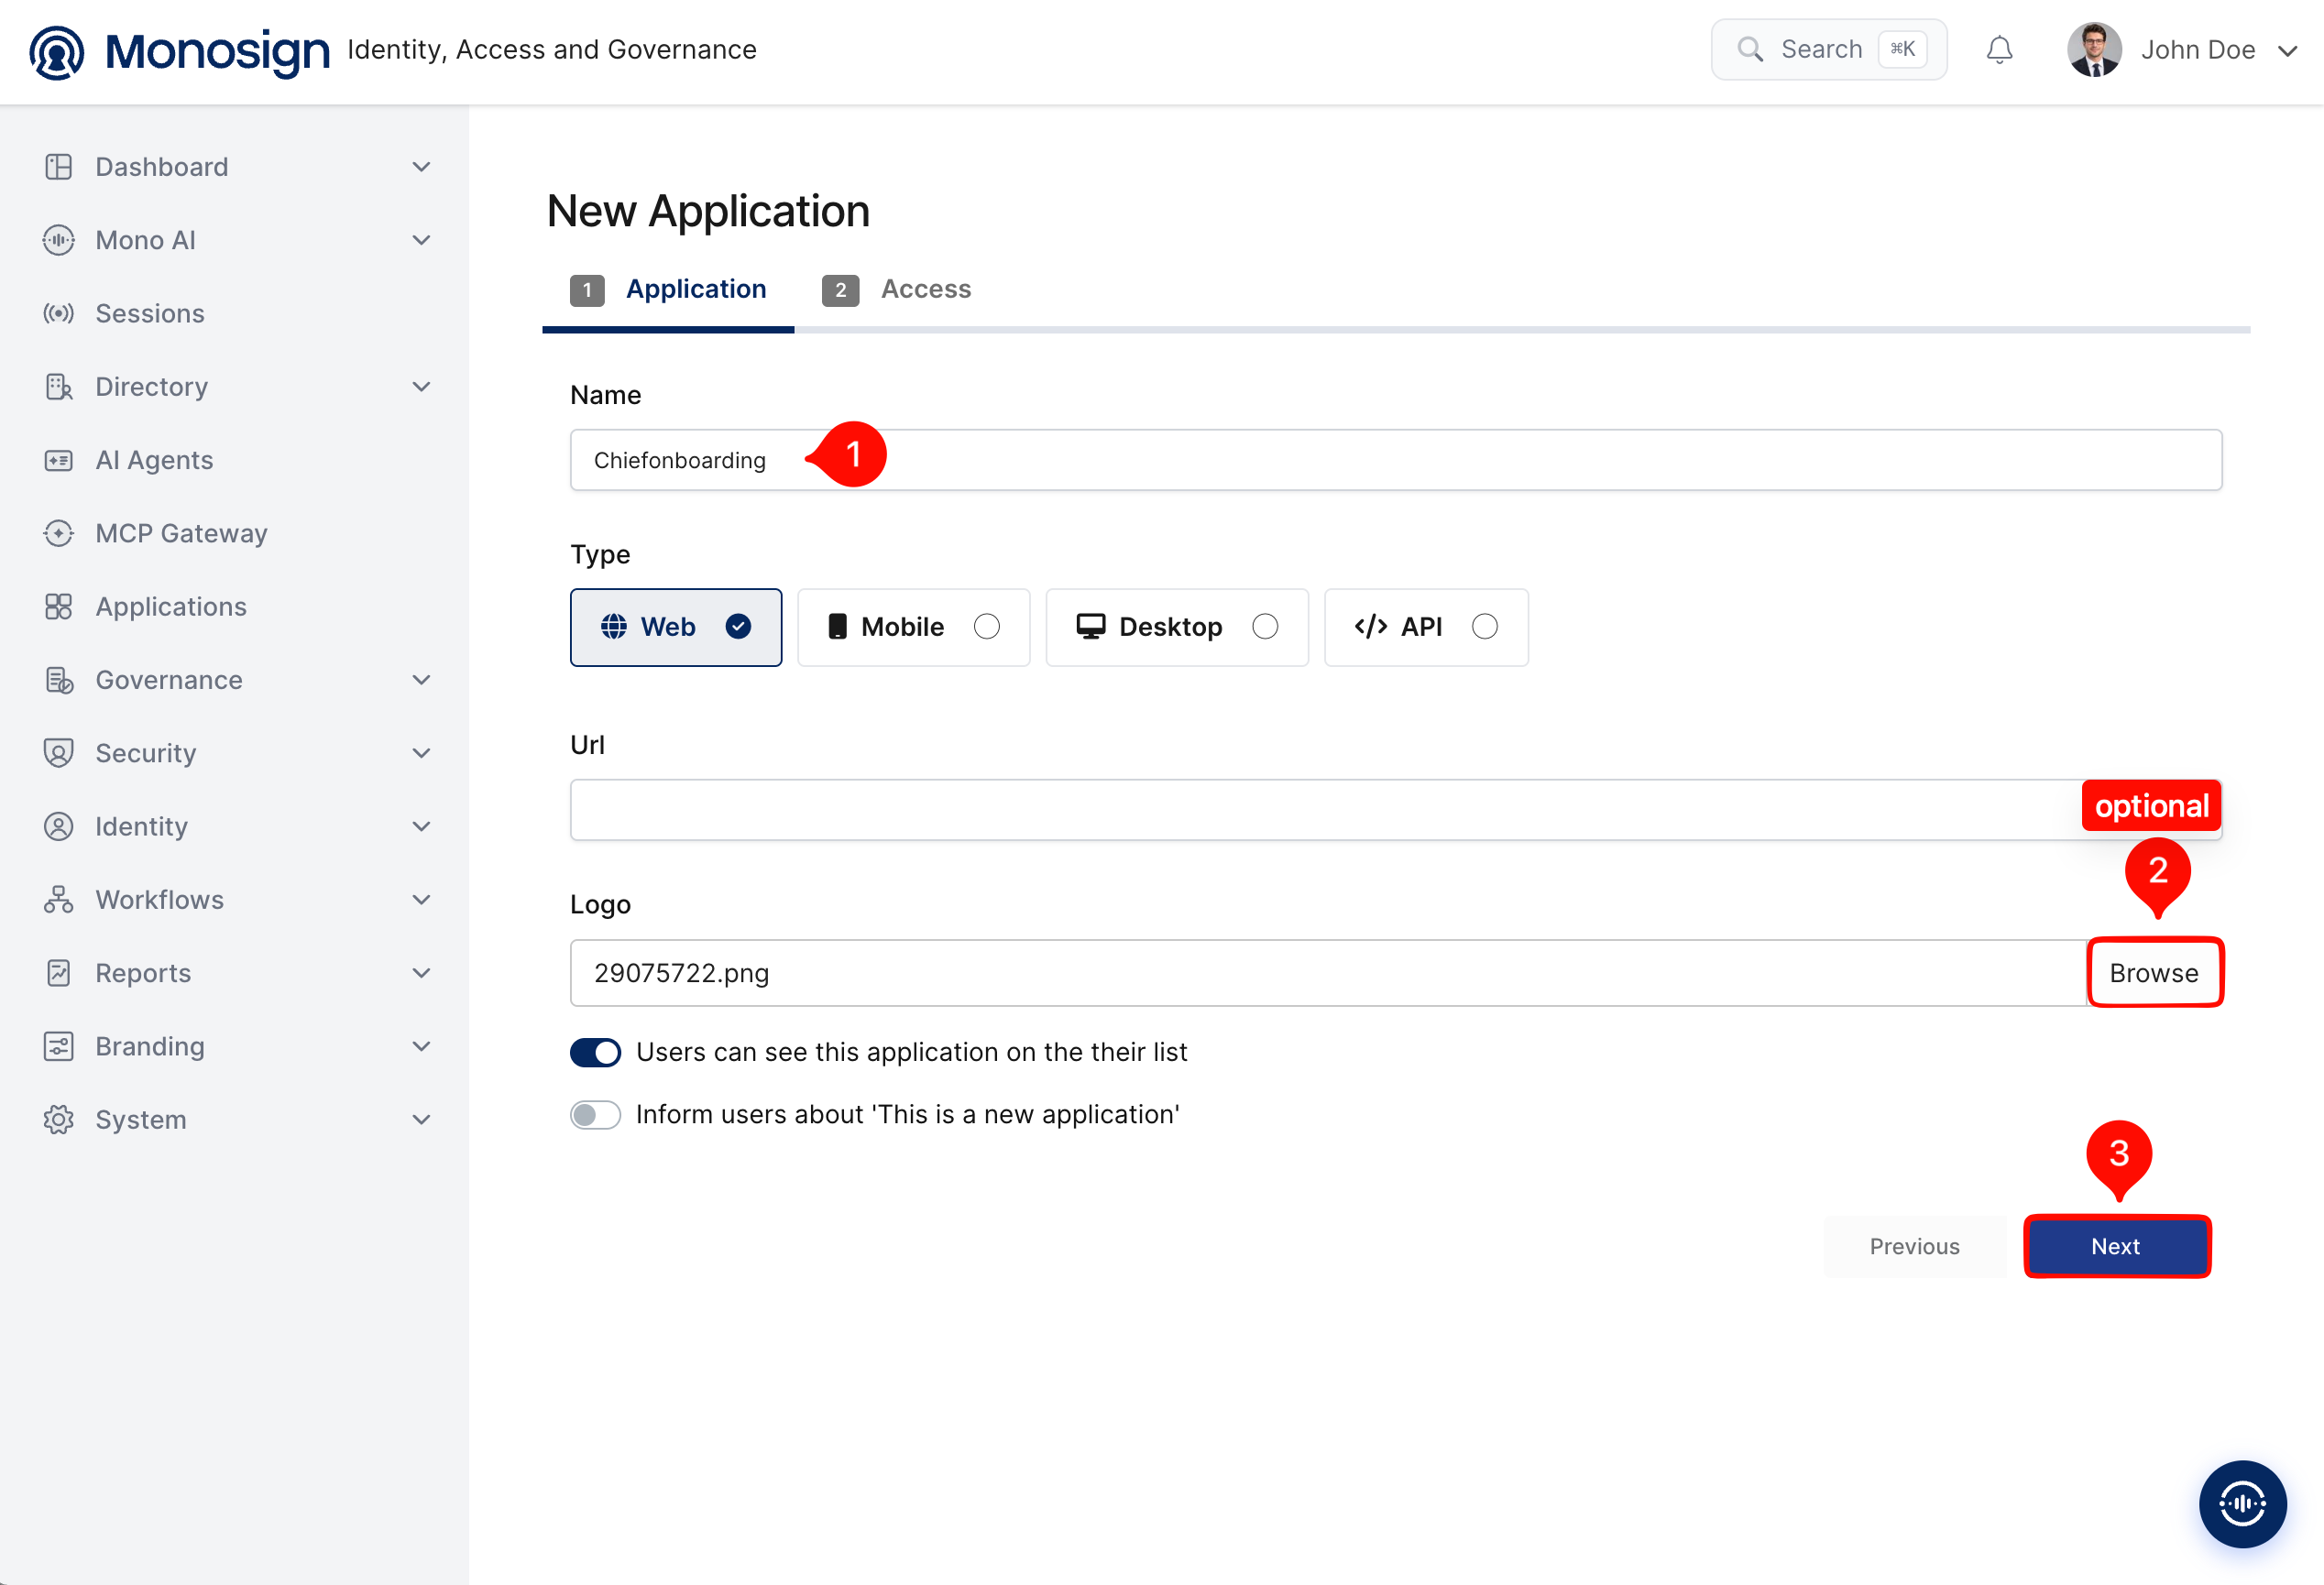
|
Property |
Value |
Description |
|---|---|---|
|
Name |
|
Name of the application shown to users on the Monosign portal and on the Monosign sign-in page. |
|
Type |
|
ChiefOnboarding is accessed through a web browser. Options: Web, Mobile, Desktop, API. |
|
Url |
Optional |
Leave empty or enter the ChiefOnboarding address so users can open the application from their Monosign portal (see the note in step 5). |
|
Logo |
Optional |
Browse and upload a logo; it is also shown on the Monosign sign-in page. |
|
Users can see this application on their list |
|
Displays the application on the user portal. |
On the Access tab define who can reach the application and click Create Application.
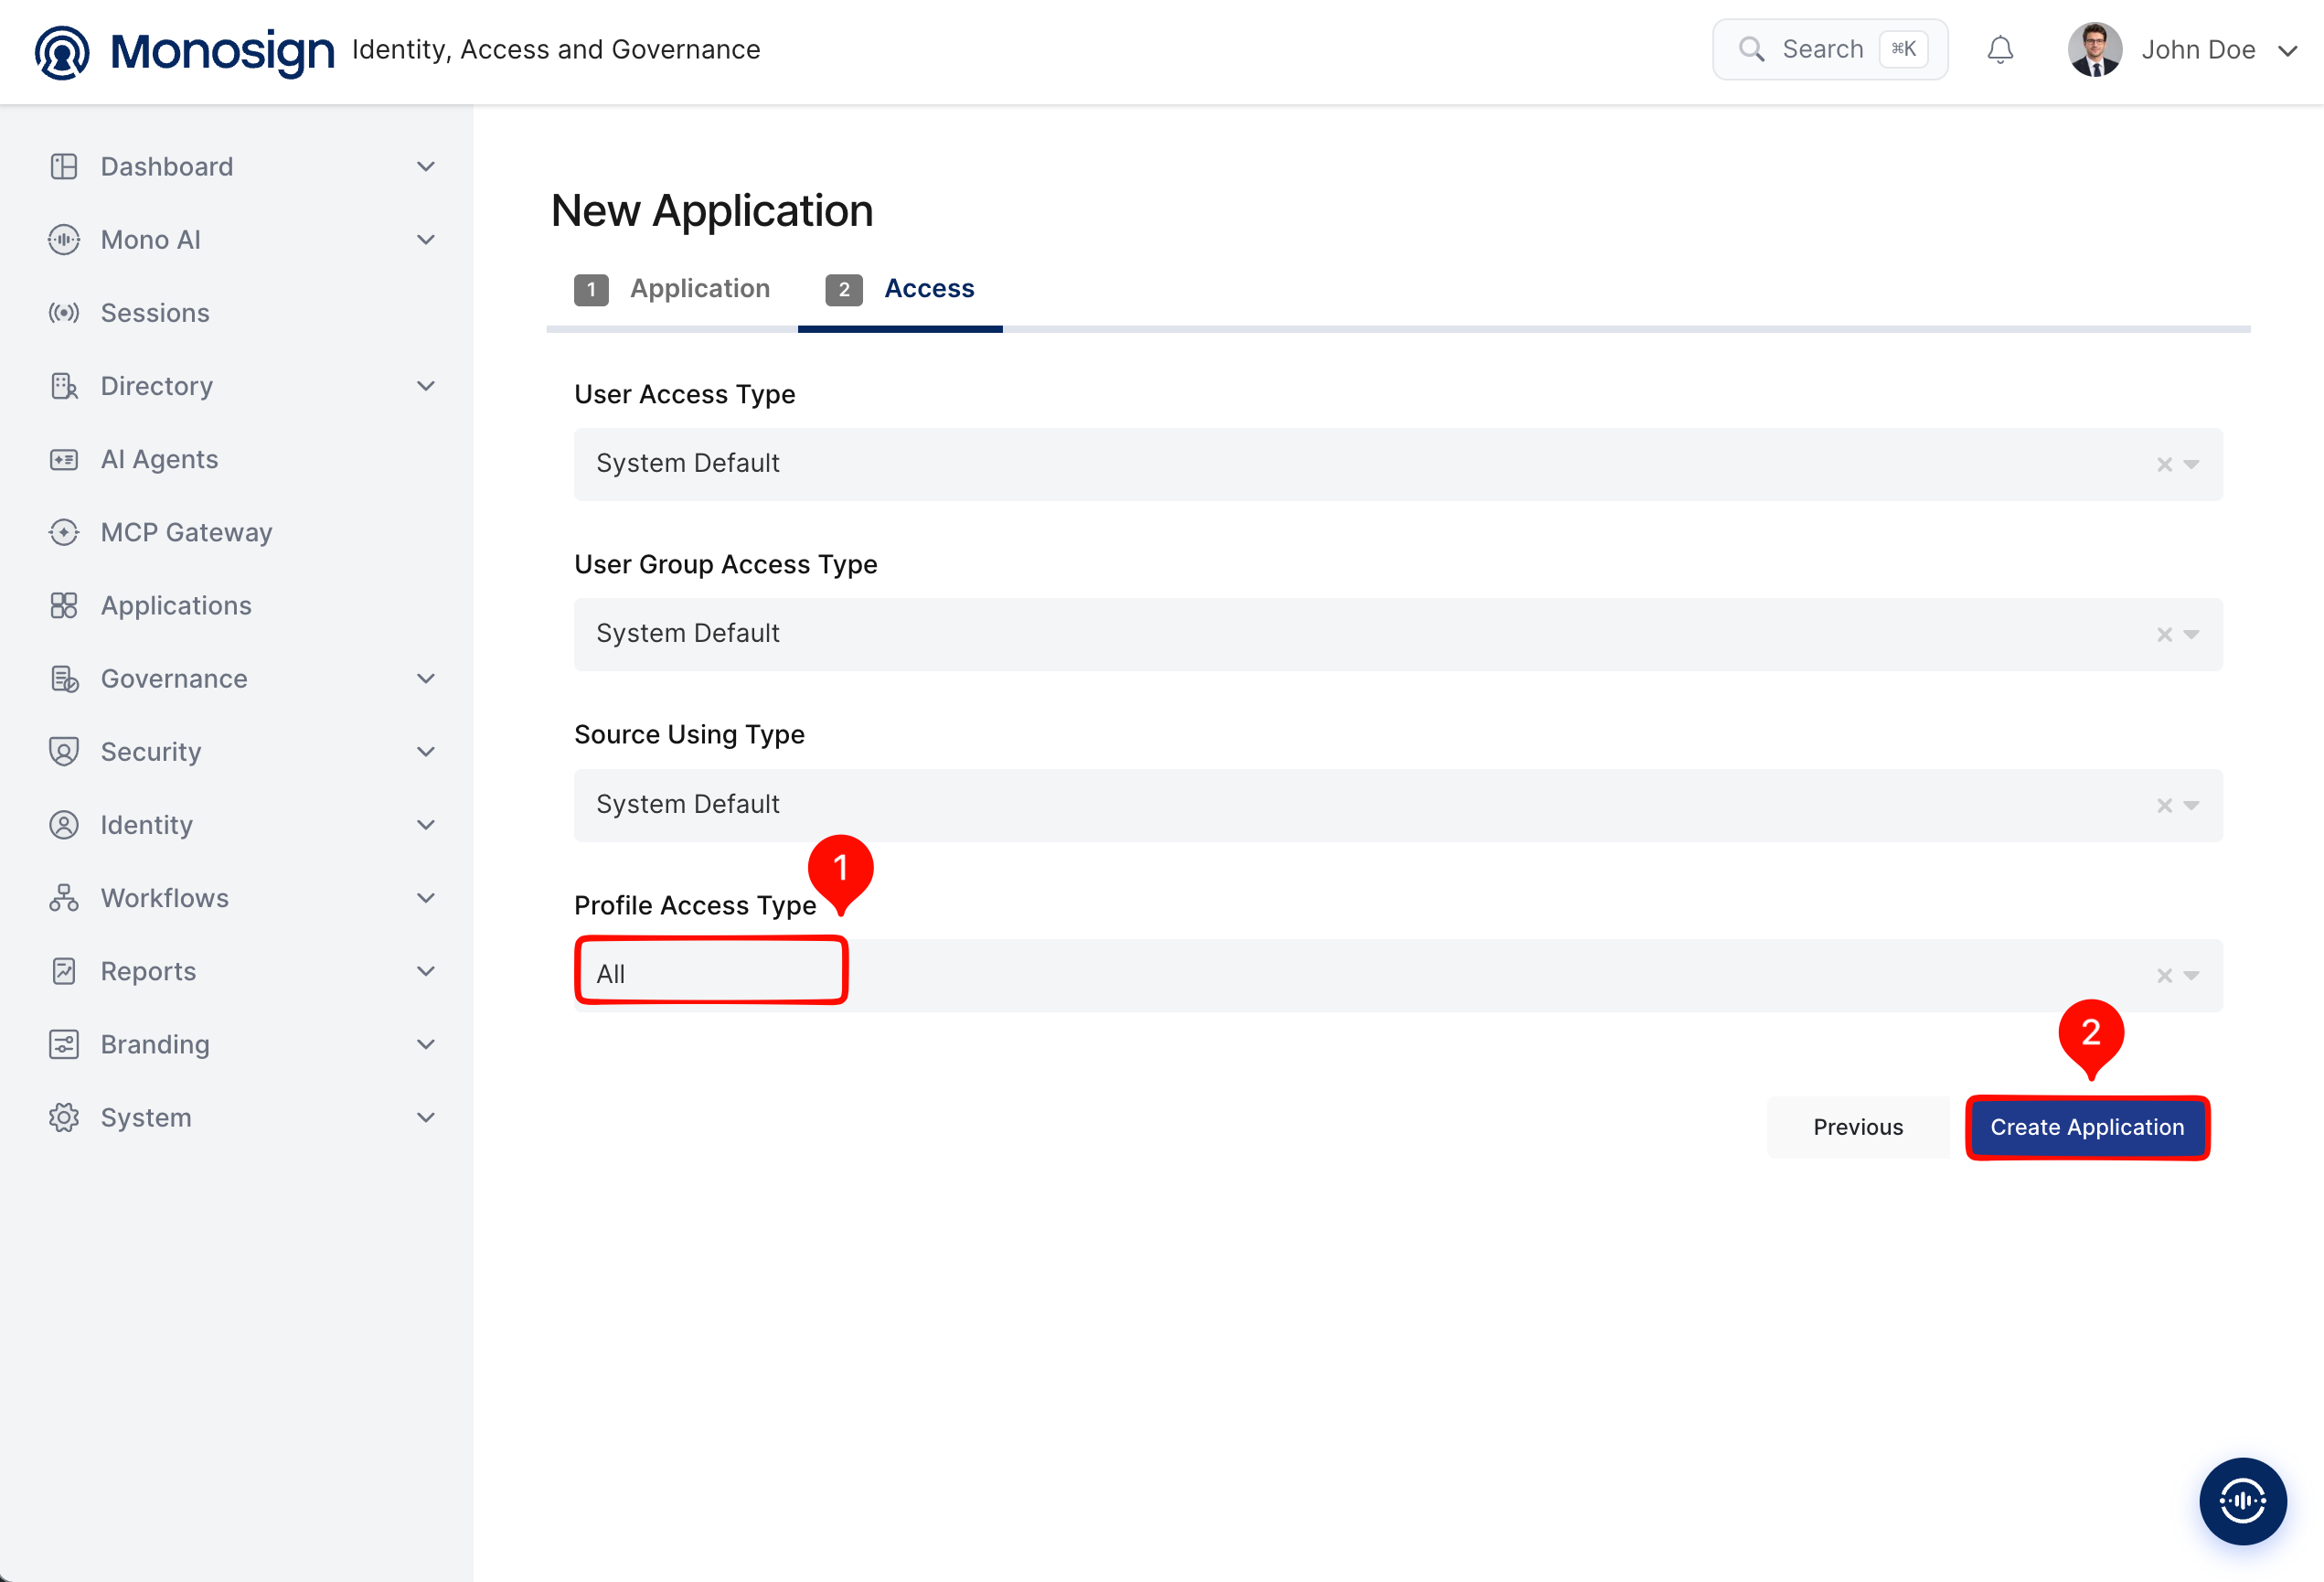
|
Property |
Value |
Description |
|---|---|---|
|
User Access Type |
|
Defines which users can access this application. Options: Only Assigned Users, All Users, System Default. |
|
User Group Access Type |
|
Defines the application’s user group access. |
|
Source Using Type |
|
Defines which user sources the application can use. |
|
Profile Access Type |
|
Defines which user profile attributes are available to the application (Options: Restricted, All). ChiefOnboarding needs the e-mail address and the name of the user. |
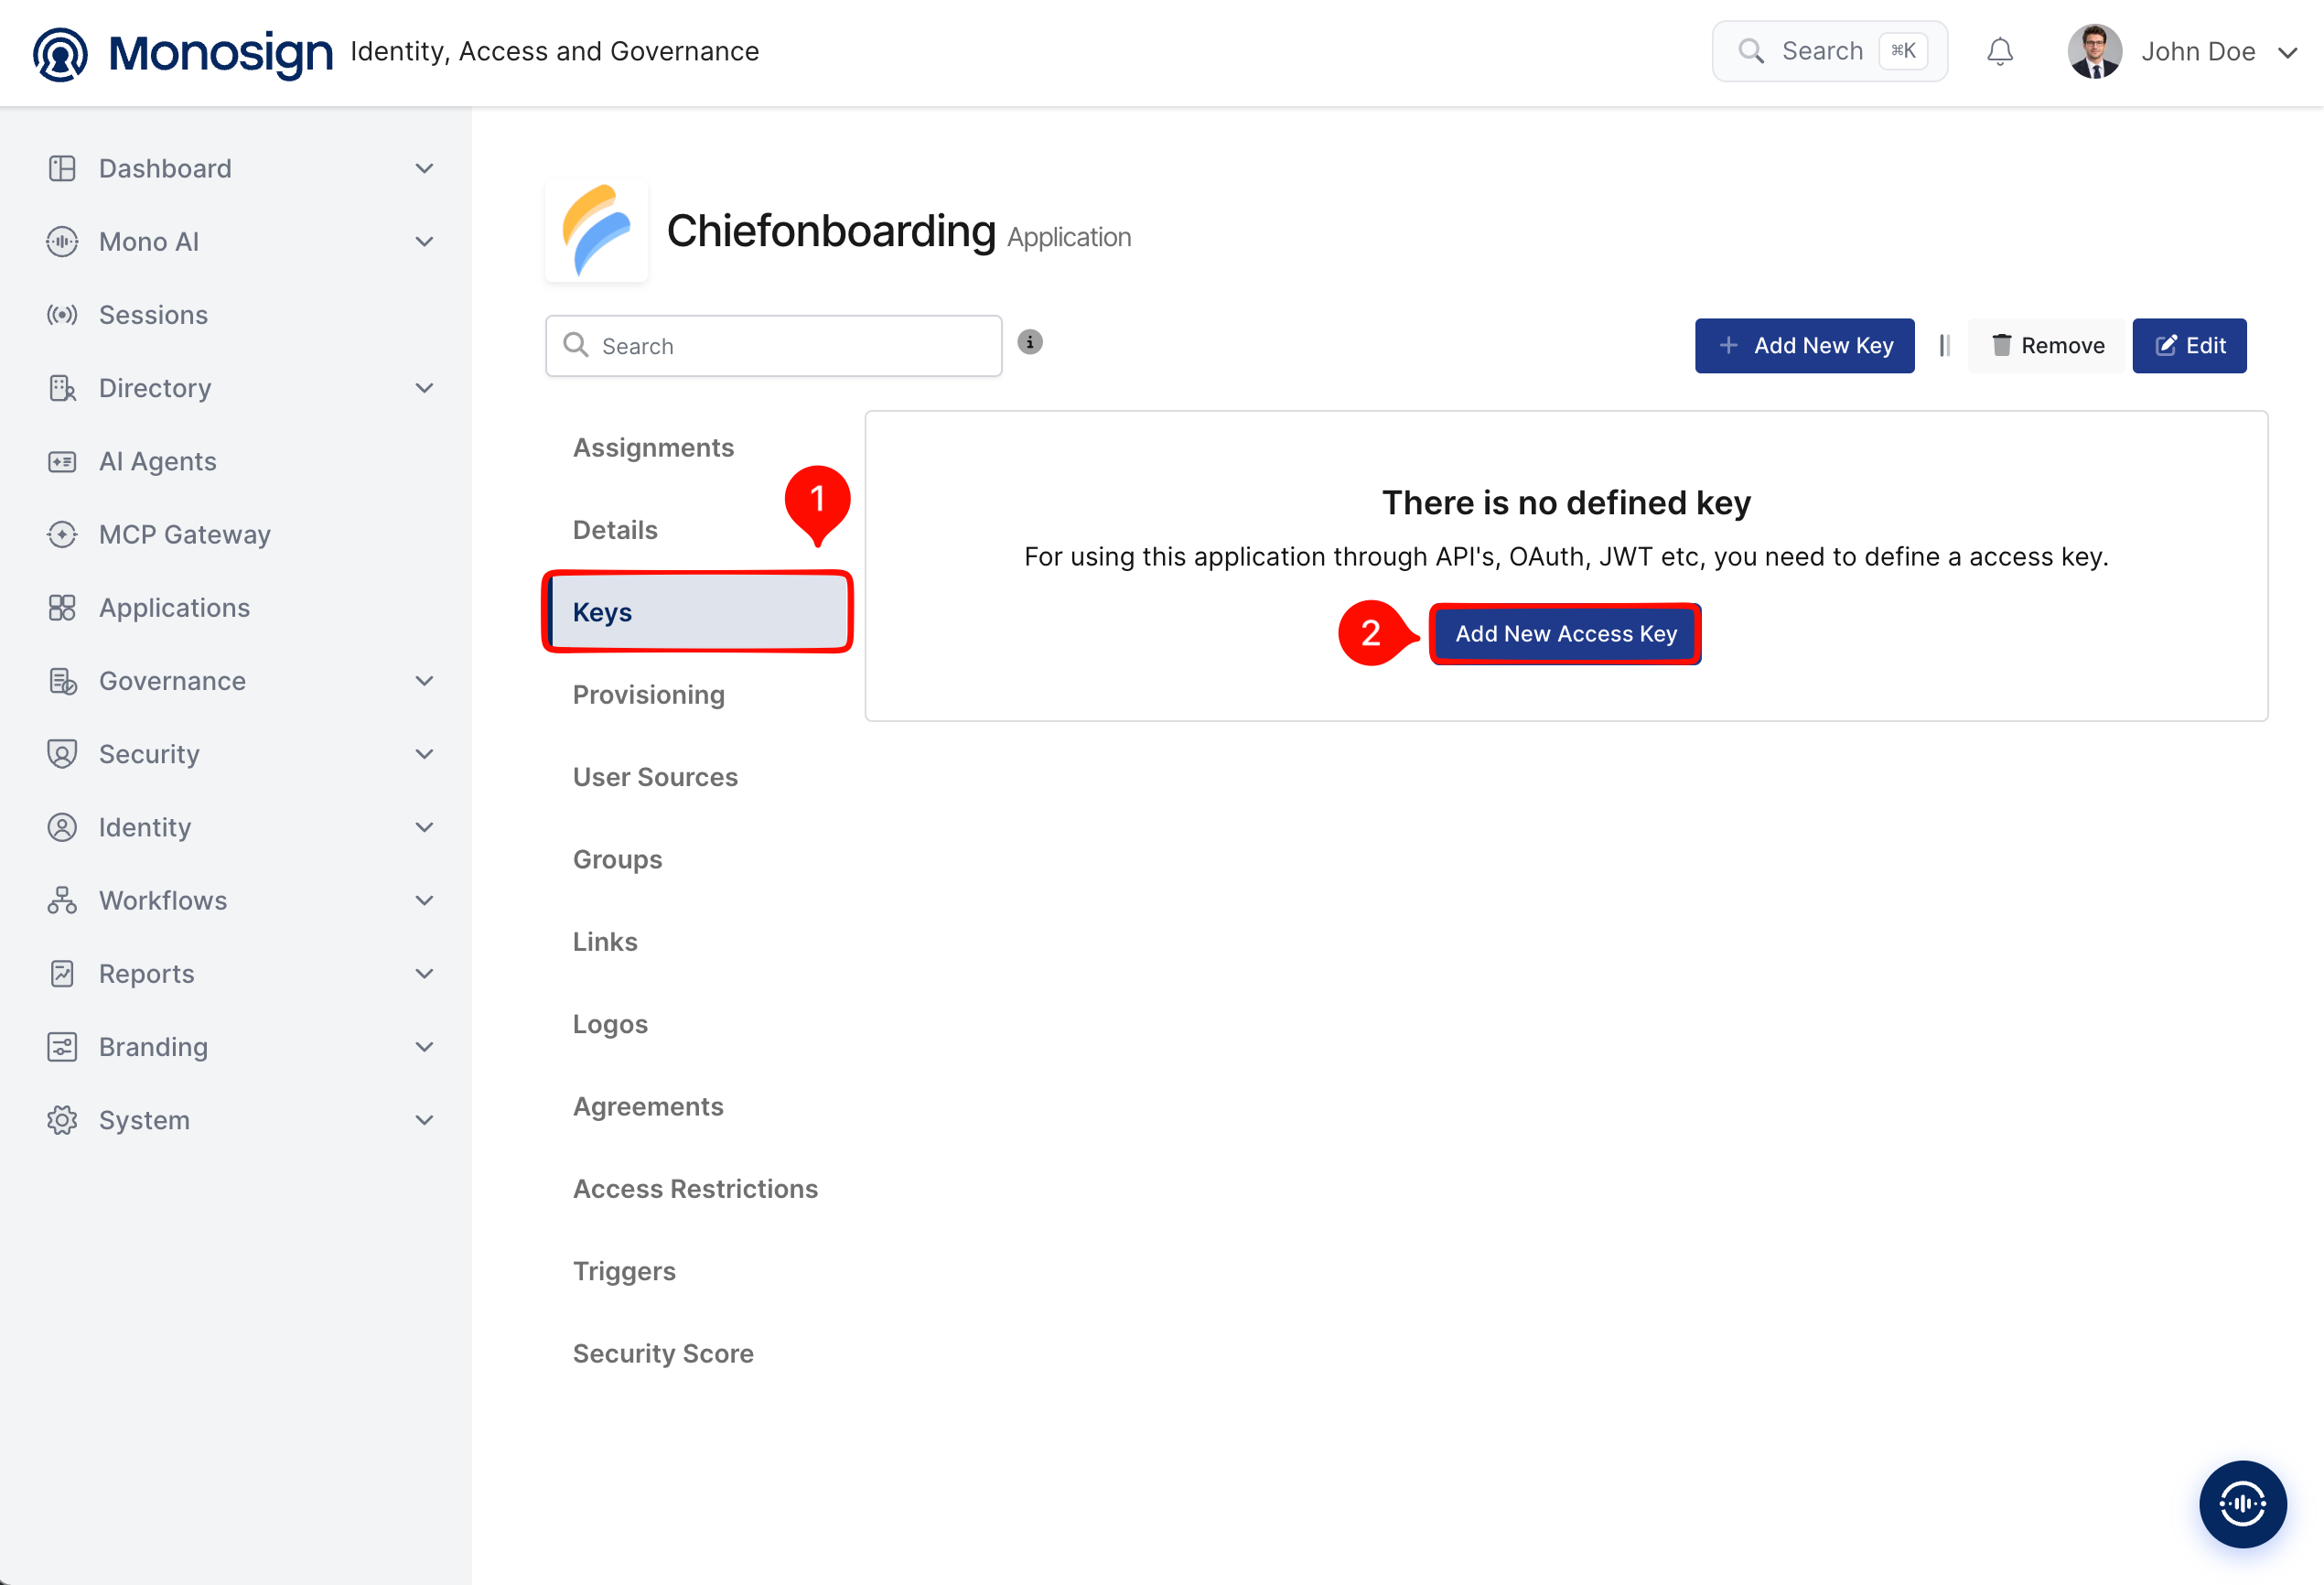
After the application is created, click Keys and add a new Access Key for OIDC/OpenID access.
Select OIDC/OpenID as the key type and click Create. Monosign generates the Client Id and Client Secret automatically.
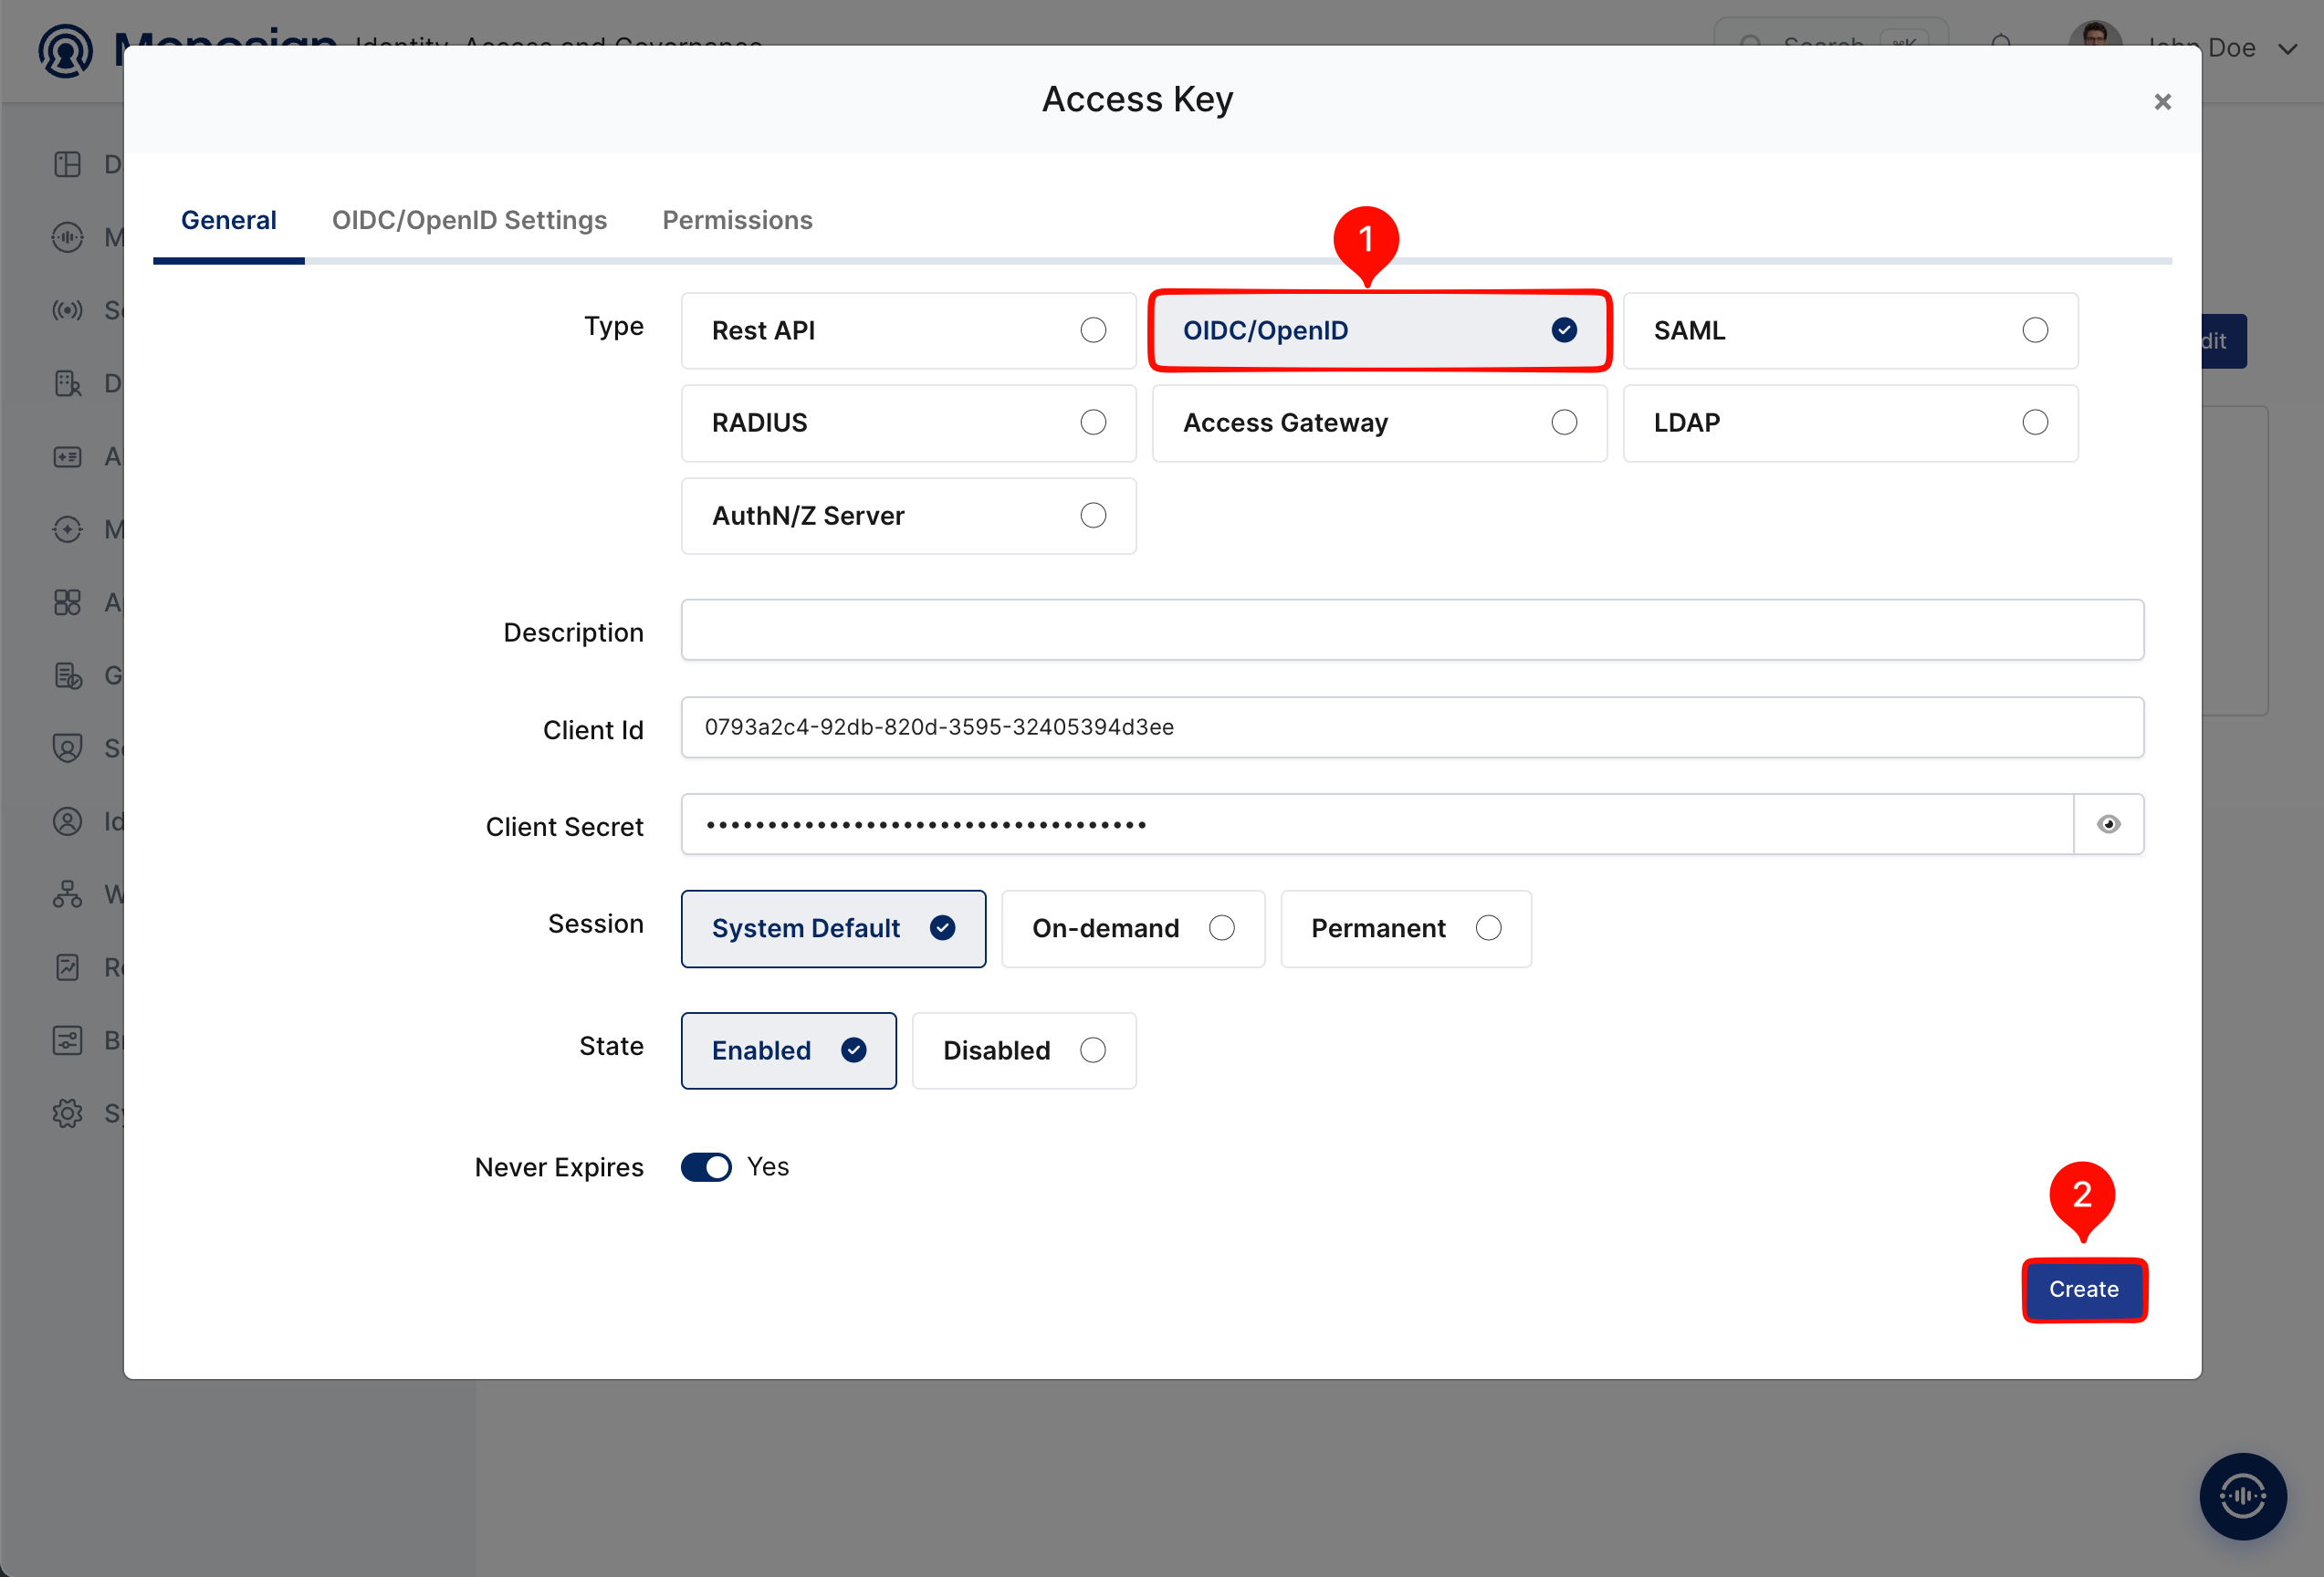
|
Property |
Value |
Options |
|---|---|---|
|
Type |
|
Rest API, OAuth 2.0, JWT, OIDC/OpenID, SAML, RADIUS, Access Gateway, LDAP, AuthN/Z Server |
|
Client Id / Client Secret |
Generated automatically |
Use the eye icon next to the secret to reveal it. Both values are required in step 4. |
|
Session |
|
System Default, On-demand, Permanent |
|
State |
|
Enabled, Disabled |
|
Never Expires |
|
Turn off to define a specific expiration date for the key. |
Configuration details for the Chiefonboarding application are provided as follows:
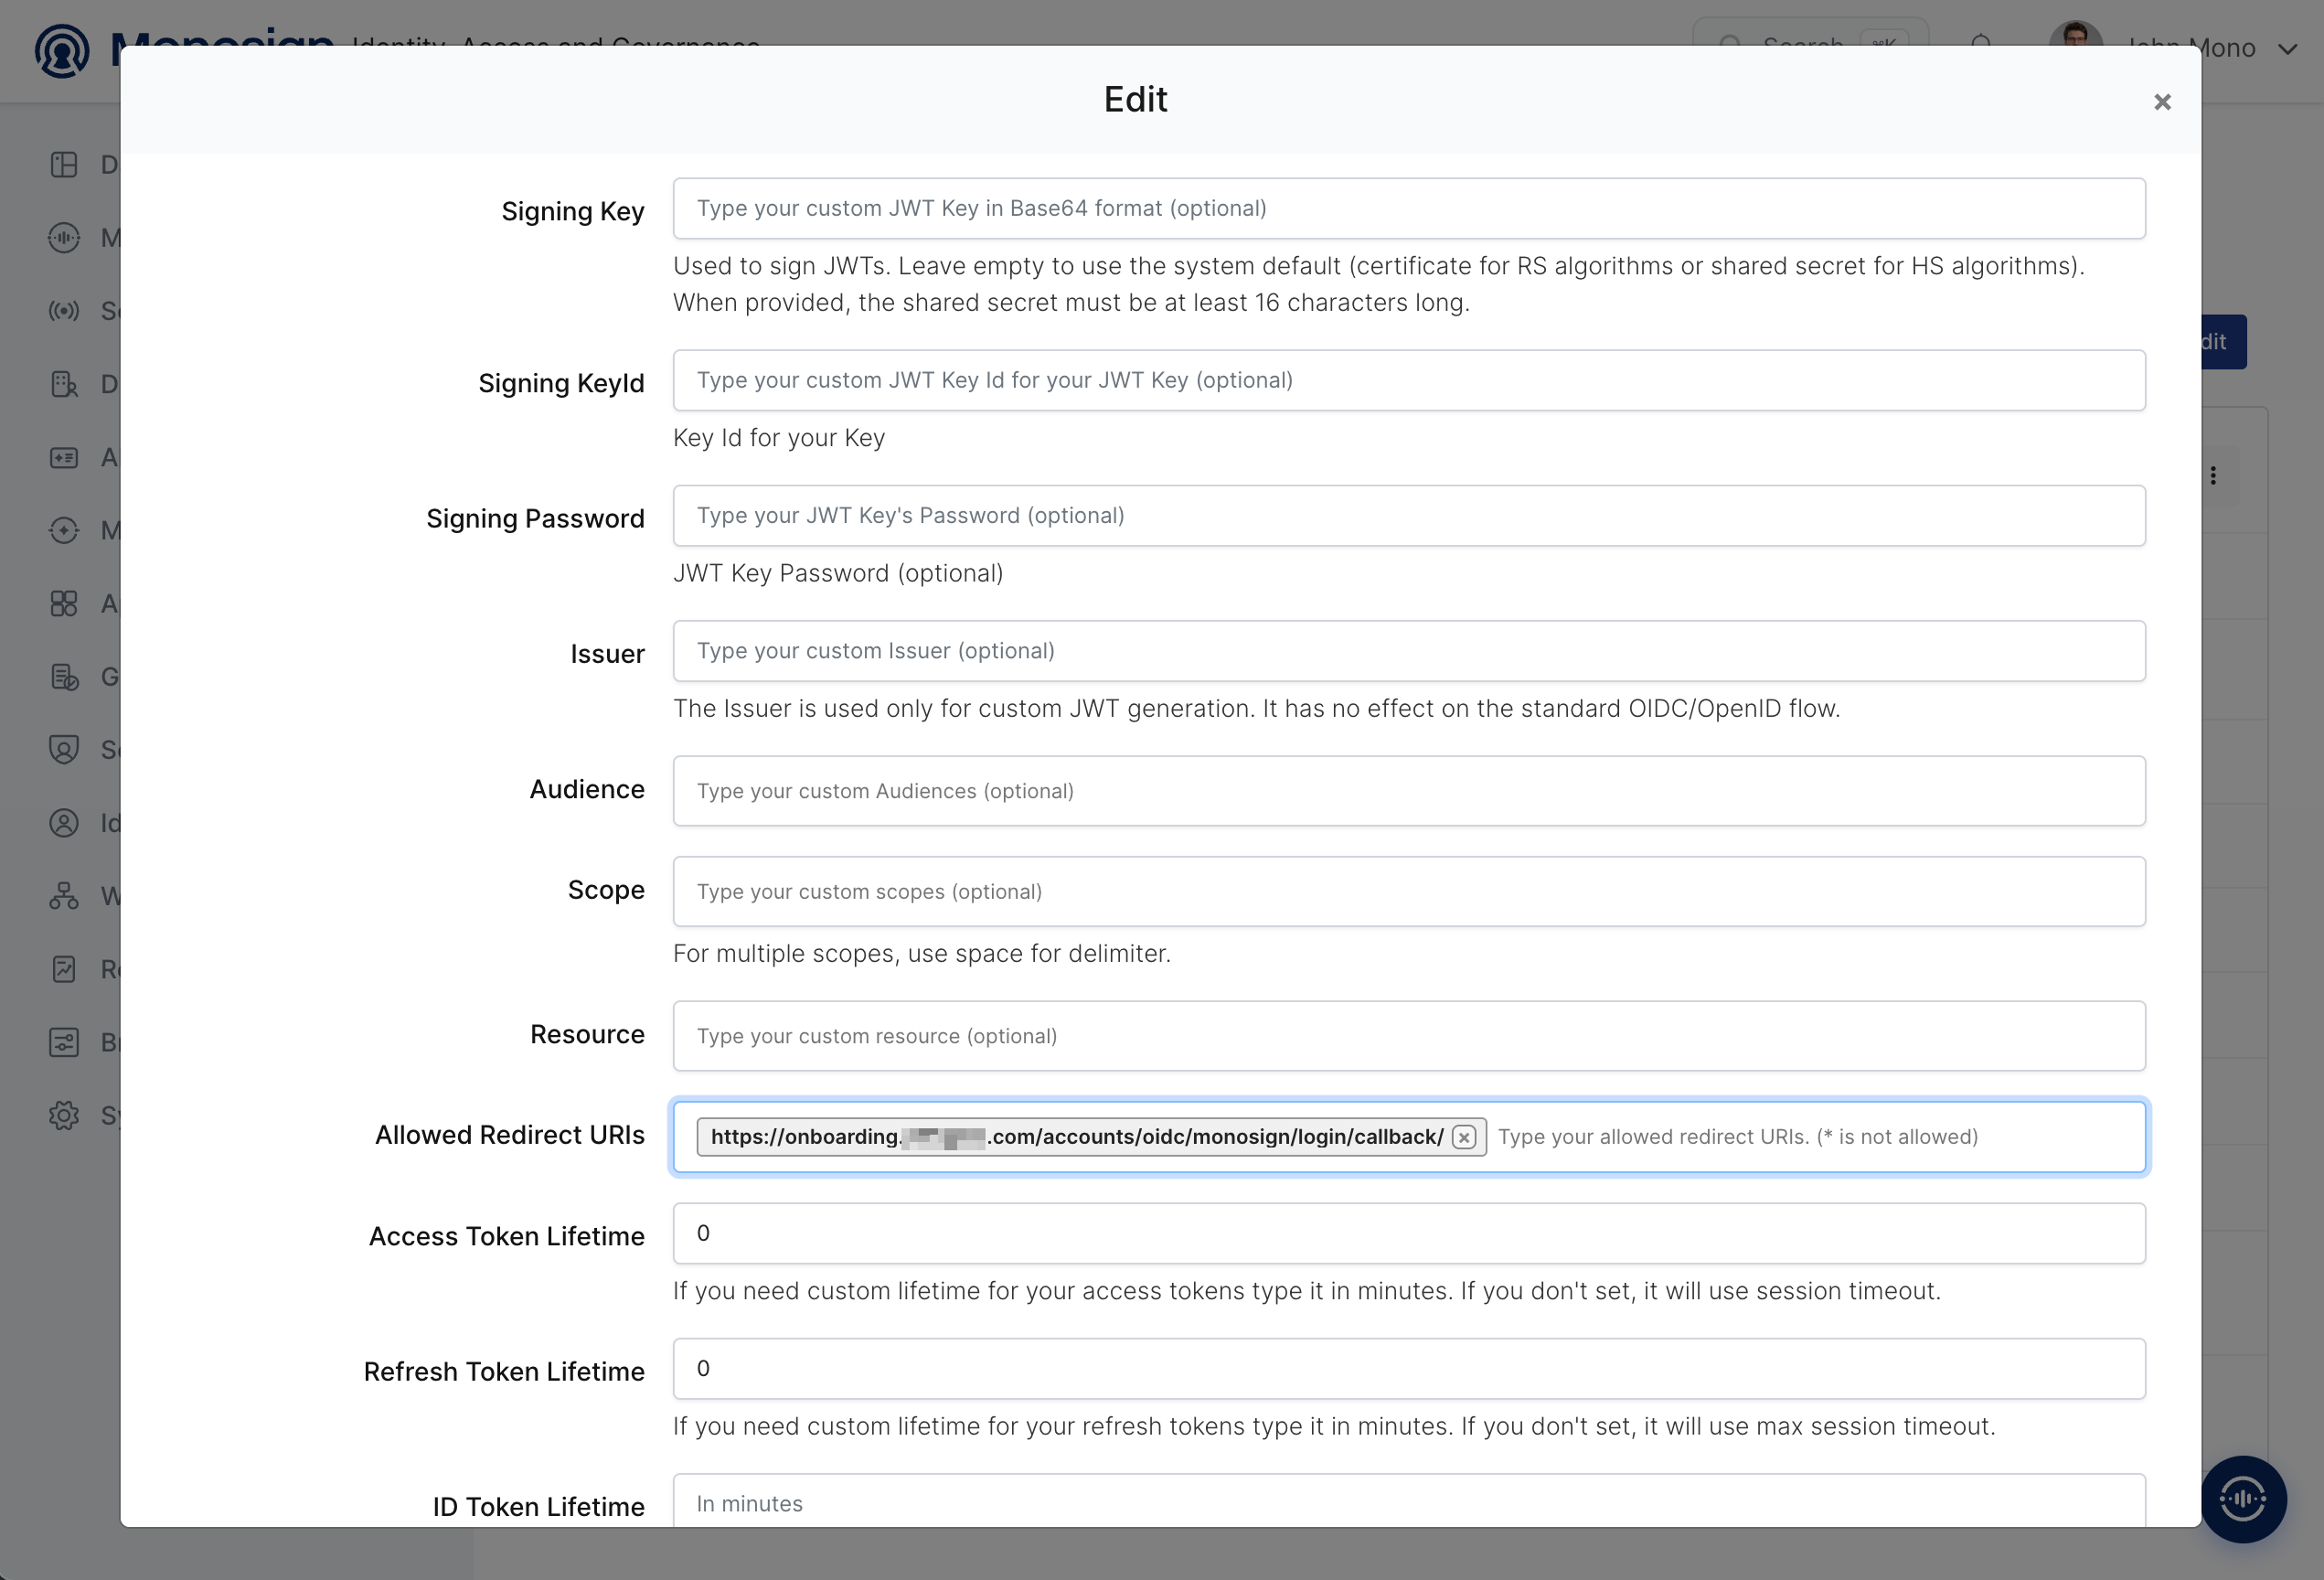
|
Monosign value |
Example |
Used in ChiefOnboarding as |
|---|---|---|
|
Client Id |
|
|
|
Client Secret |
|
|
|
Configuration Url (without the |
|
|
2- Configuring the OIDC/OpenID Settings on Monosign
Open the key with the Configure button, go to OIDC/OpenID Settings and add the callback address of ChiefOnboarding to Allowed Redirect URIs.
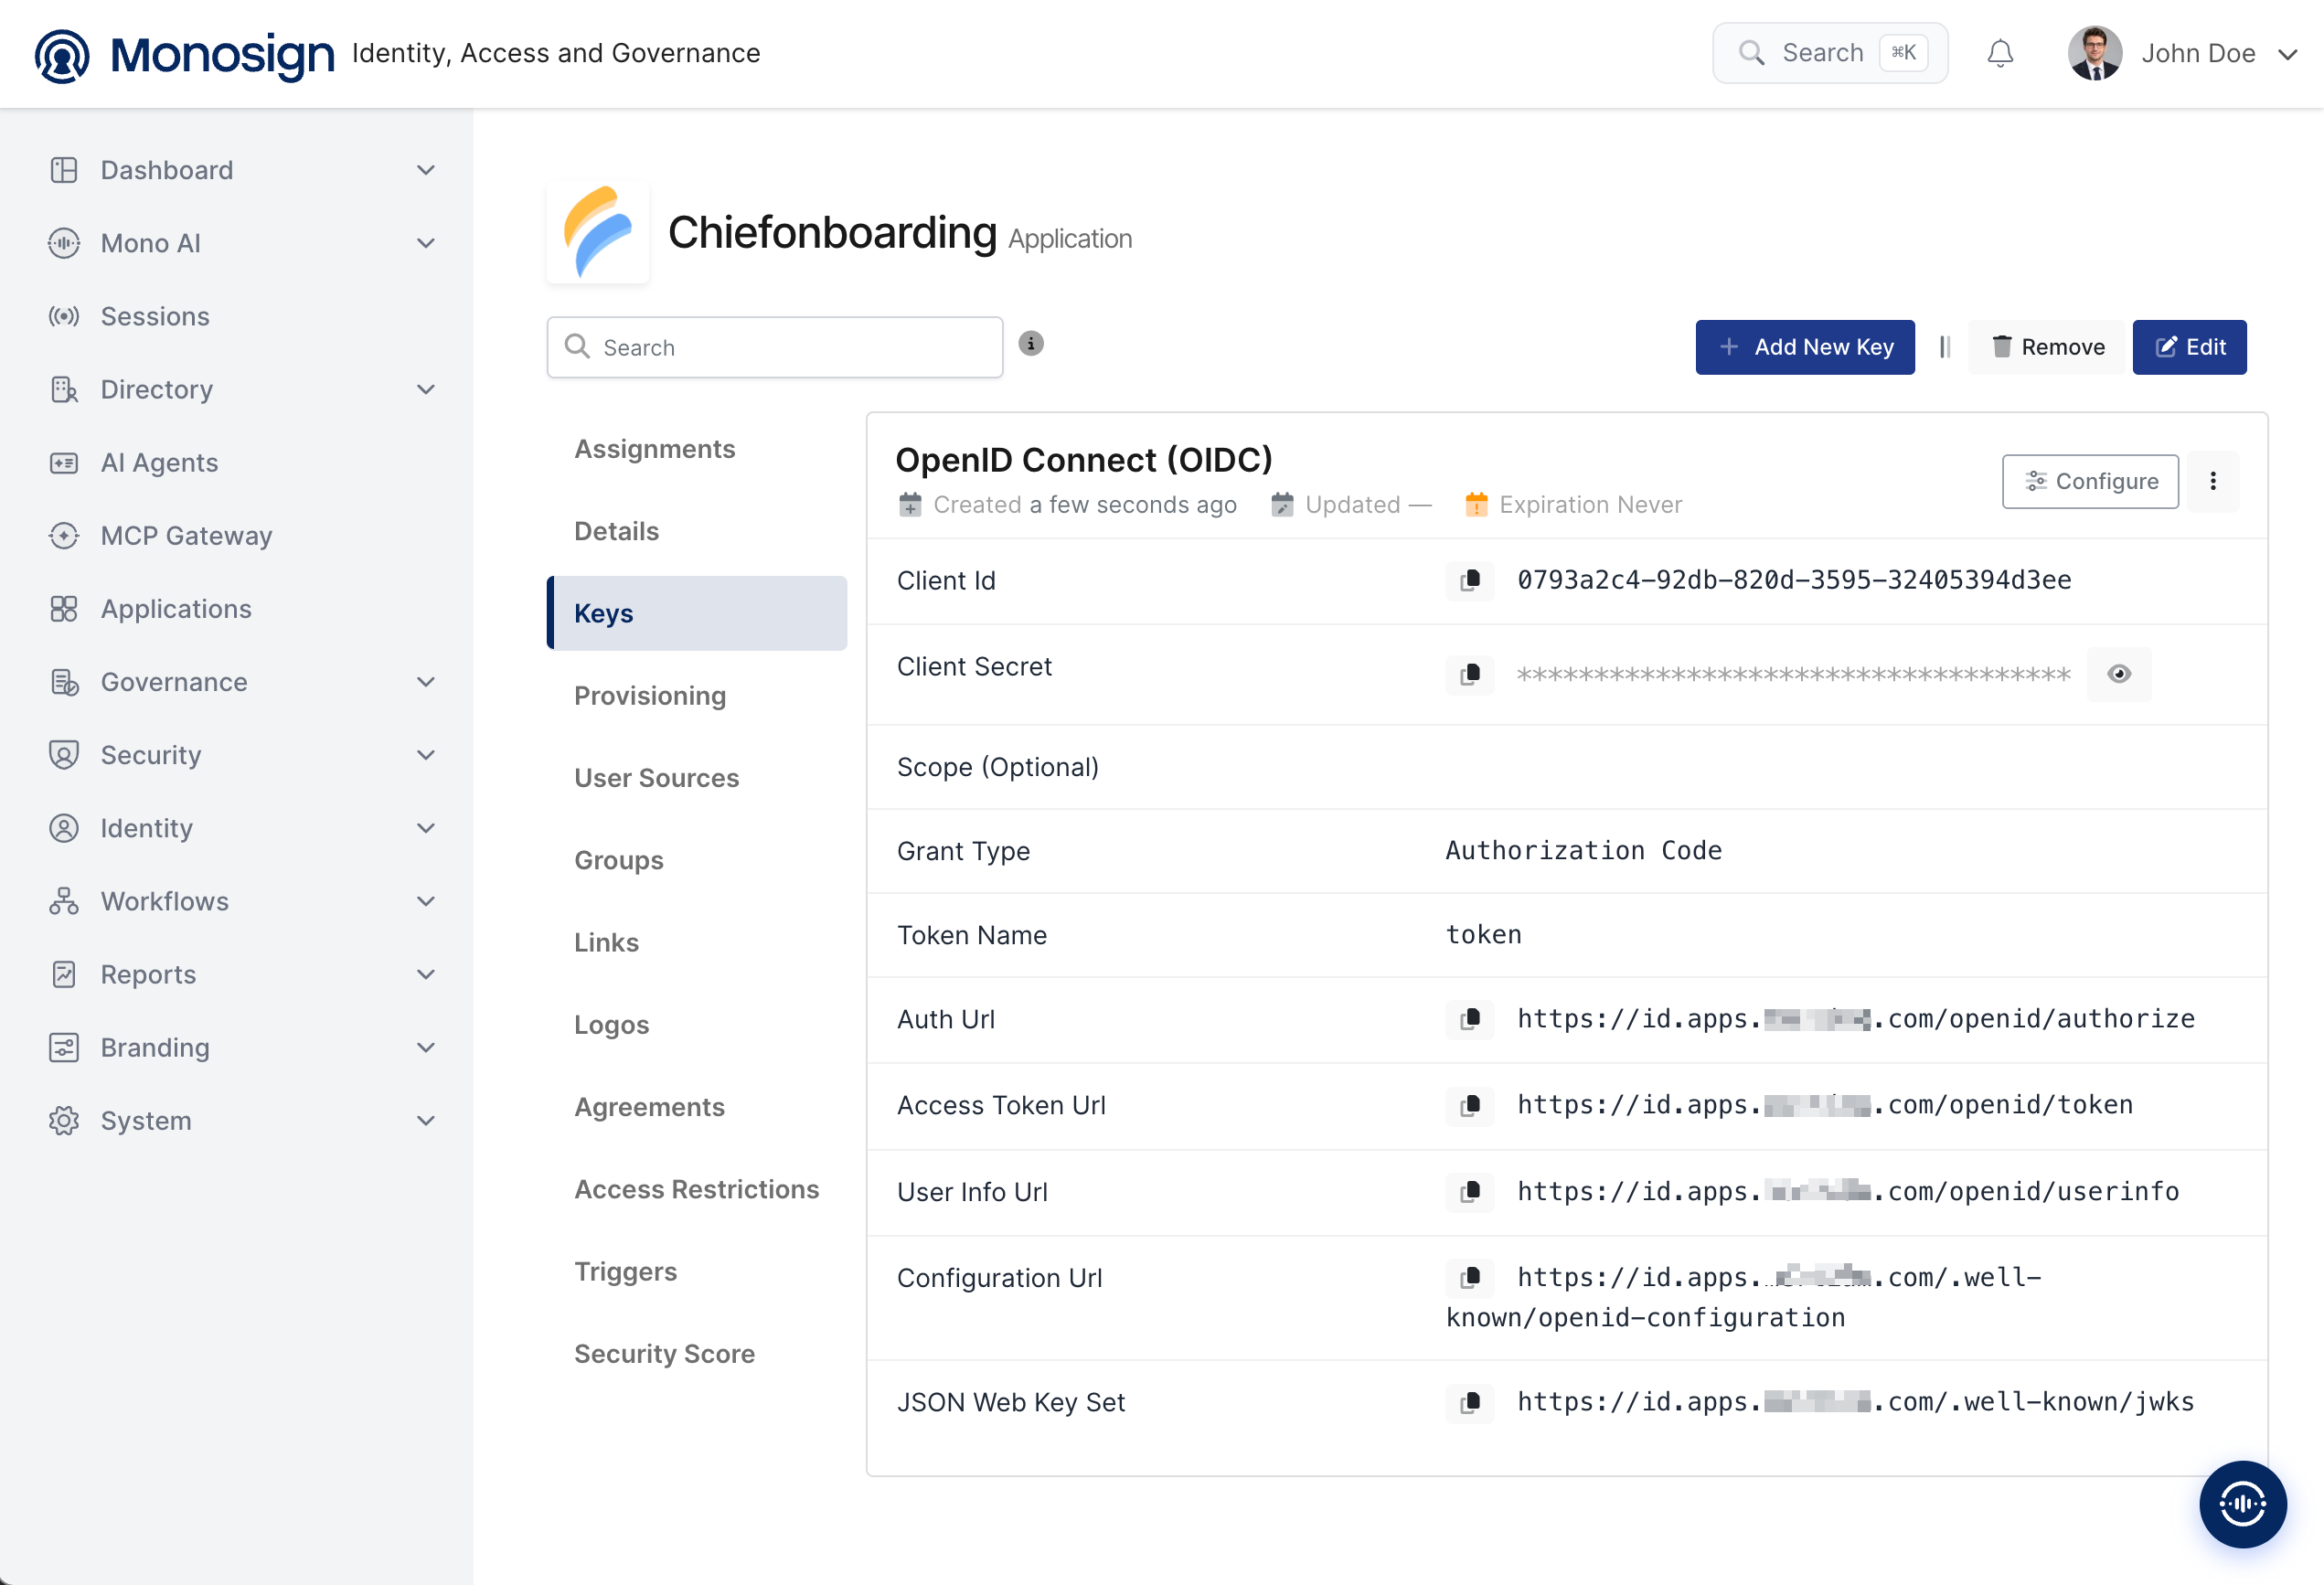
|
Property |
Value |
Description |
|---|---|---|
|
Allowed Redirect URIs |
|
The address where Monosign sends the user back after sign-in. The path is |
|
Signing Key / Key Id / Password, Issuer, Audience, Scope, Resource |
Empty |
Optional custom JWT settings. They are not needed for ChiefOnboarding. |
|
Token lifetimes, CORS |
Empty |
Default values are used. |
ChiefOnboarding reads the user information from the Monosign ID token and UserInfo endpoint: sub, the email address and the name. Monosign returns these claims by default, so a claim mapping is not required. The e-mail address is required. If you want the first and last name to be filled in as well, add the claims given_name ({{Profile.FirstName}}) and family_name ({{Profile.LastName}}) on the Claim Mapping tab and click Update.
3- Assign a User to the ChiefOnboarding Application
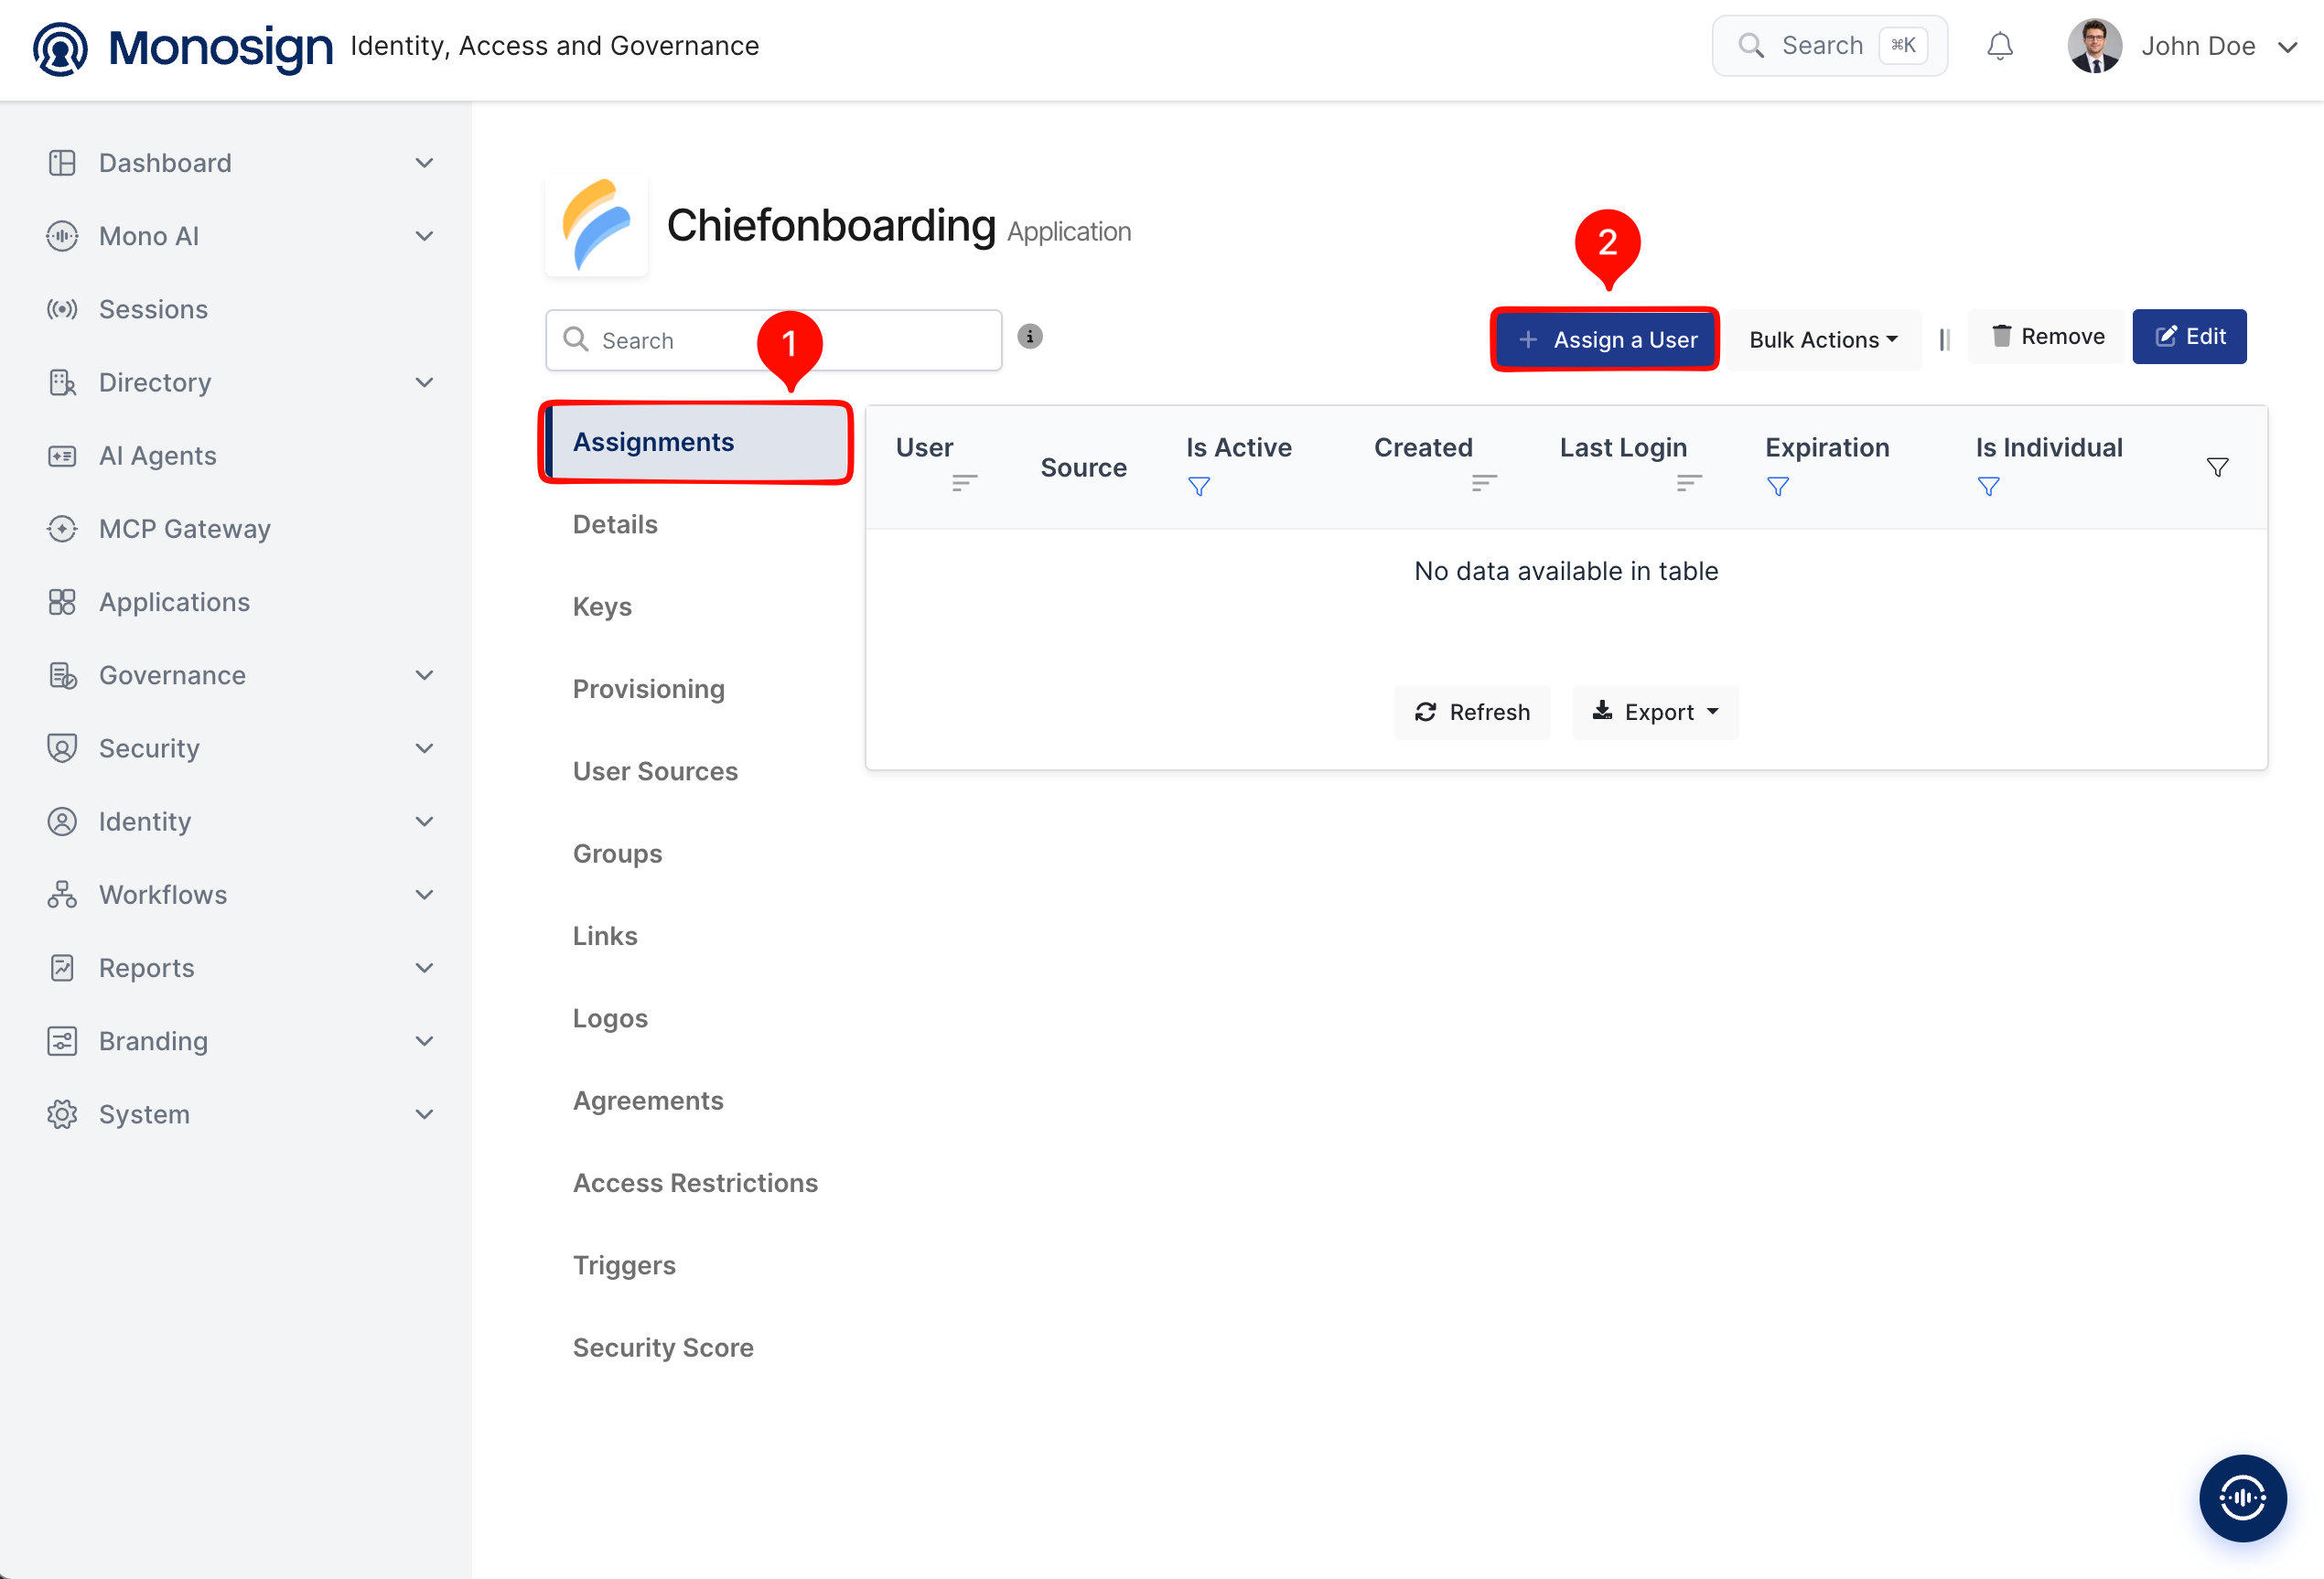
Please follow the below instructions on how to assign a user to the ChiefOnboarding application. Open the application, click the Assignments tab and click Assign a User.
Search and select the users who can sign in to ChiefOnboarding, check the Expiration Date and save. You can select more than one user.
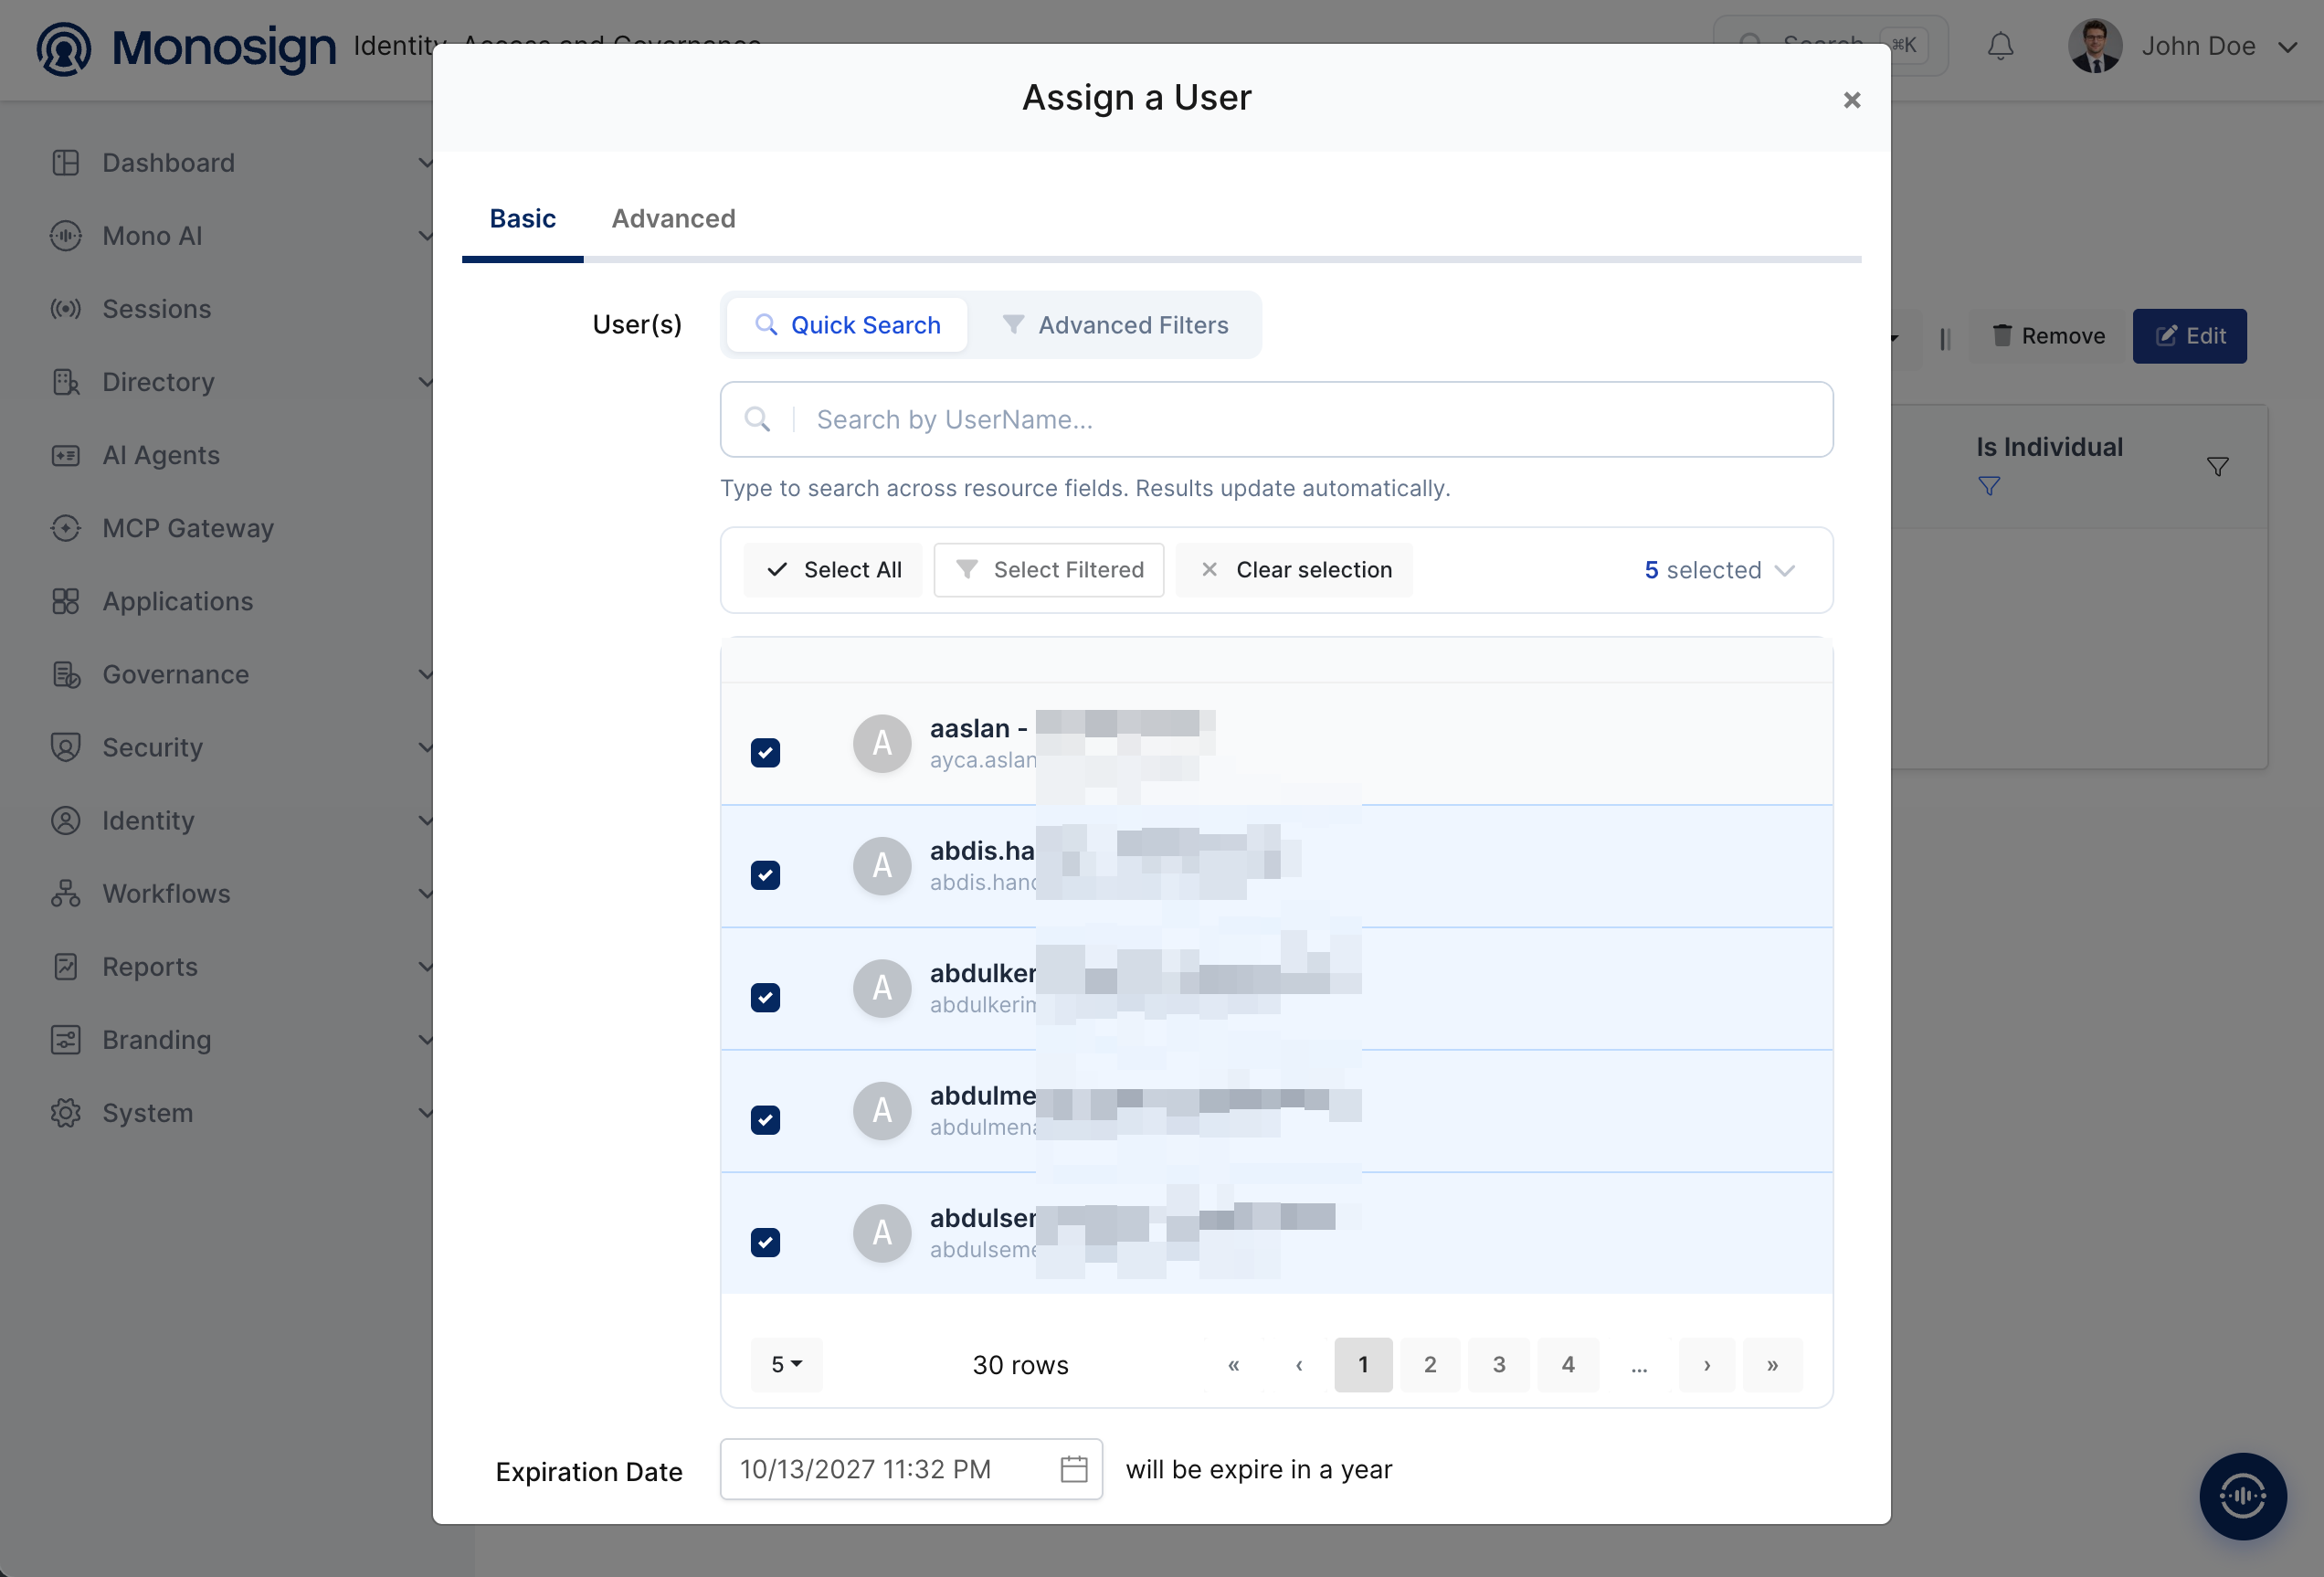
|
Property |
Value |
Description |
|---|---|---|
|
User(s) |
Selected users |
Users who can sign in to ChiefOnboarding with Monosign. |
|
Expiration Date |
Default one year |
The assignment expires on this date. |
4- Configuration Single Sign-On for ChiefOnboarding
As we mentioned at the start, please check out the ChiefOnboarding documentation first. ChiefOnboarding is configured with environment variables. In the Docker Compose deployment add the following variables to the environment file of the app service (for example the .env file that is used with env_file) and replace the placeholder values.
ALLOWED_HOSTS=<chiefonboarding-host-name>
BASE_URL=https://<chiefonboarding-host-name>
ALLAUTH_PROVIDERS=openid_connect
SSO_AUTO_CREATE_USER=True
SSO_PROVIDERS='{"openid_connect": {"APPS": [{"provider_id": "monosign", "name": "Monosign", "client_id": "<client-id>", "secret": "<client-secret>", "settings": {"server_url": "https://<monosign-host>", "VERIFIED_EMAIL": True}}]}}'
|
Variable |
Value |
Description |
|---|---|---|
|
ALLOWED_HOSTS / BASE_URL |
Host name / public HTTPS address |
The host name that users type in the browser. ChiefOnboarding answers only these host names and uses |
|
ALLAUTH_PROVIDERS |
|
Enables the generic OpenID Connect provider of |
|
SSO_AUTO_CREATE_USER |
|
Creates the user automatically at the first sign-in. When it is not |
|
SSO_PROVIDERS |
Provider definition |
The value is read as a Python dictionary, so write |
|
provider_id |
|
Becomes part of the callback address ( |
|
name |
|
Text of the button on the sign-in page (“Log in with Monosign”). |
|
client_id / secret |
Client Id / Client Secret |
Copied from the Monosign OIDC/OpenID Access Key Details created in the first step. |
|
server_url |
|
Address of Monosign. ChiefOnboarding reads |
|
VERIFIED_EMAIL |
|
ChiefOnboarding accepts the e-mail address only when the OIDC server returns |
The role of a new user comes from the optional variables OIDC_ROLE_PATH_IN_RETURN, OIDC_ROLE_ADMIN_PATTERN, OIDC_ROLE_MANAGER_PATTERN and OIDC_ROLE_NEW_HIRE_PATTERN, which read a group claim from the token. When they are not set, every new user created by single sign-on gets the role Other and sees only the Colleagues and Resources pages. To keep the administrator role, create the administrator first (the first account can be created with the ACCOUNT_EMAIL and ACCOUNT_PASSWORD variables) and use the same e-mail address in Monosign; ChiefOnboarding links the single sign-on account to the existing user with the same e-mail address.
The environment file contains the client secret, the secret key of the application and the database password. Restrict its permissions (for example chmod 600) and do not store it in a shared repository. Because the e-mail address links an identity provider account to an existing user, use single sign-on only with an identity provider that you trust (Monosign) and do not leave VERIFIED_EMAIL on for a provider that does not check the e-mail address.
Recreate the ChiefOnboarding container so that the new variables are loaded:
cd <chiefonboarding-compose-directory>
docker compose up -d
The sign-in page must now show the local e-mail and password form and the “Log in with Monosign” button.
5- Sign In Test
Now try to log in to ChiefOnboarding using Monosign SSO.
-
Open a new browser window (or a private window) and type the ChiefOnboarding address. The sign-in page shows the local form and the Log in with Monosign button.
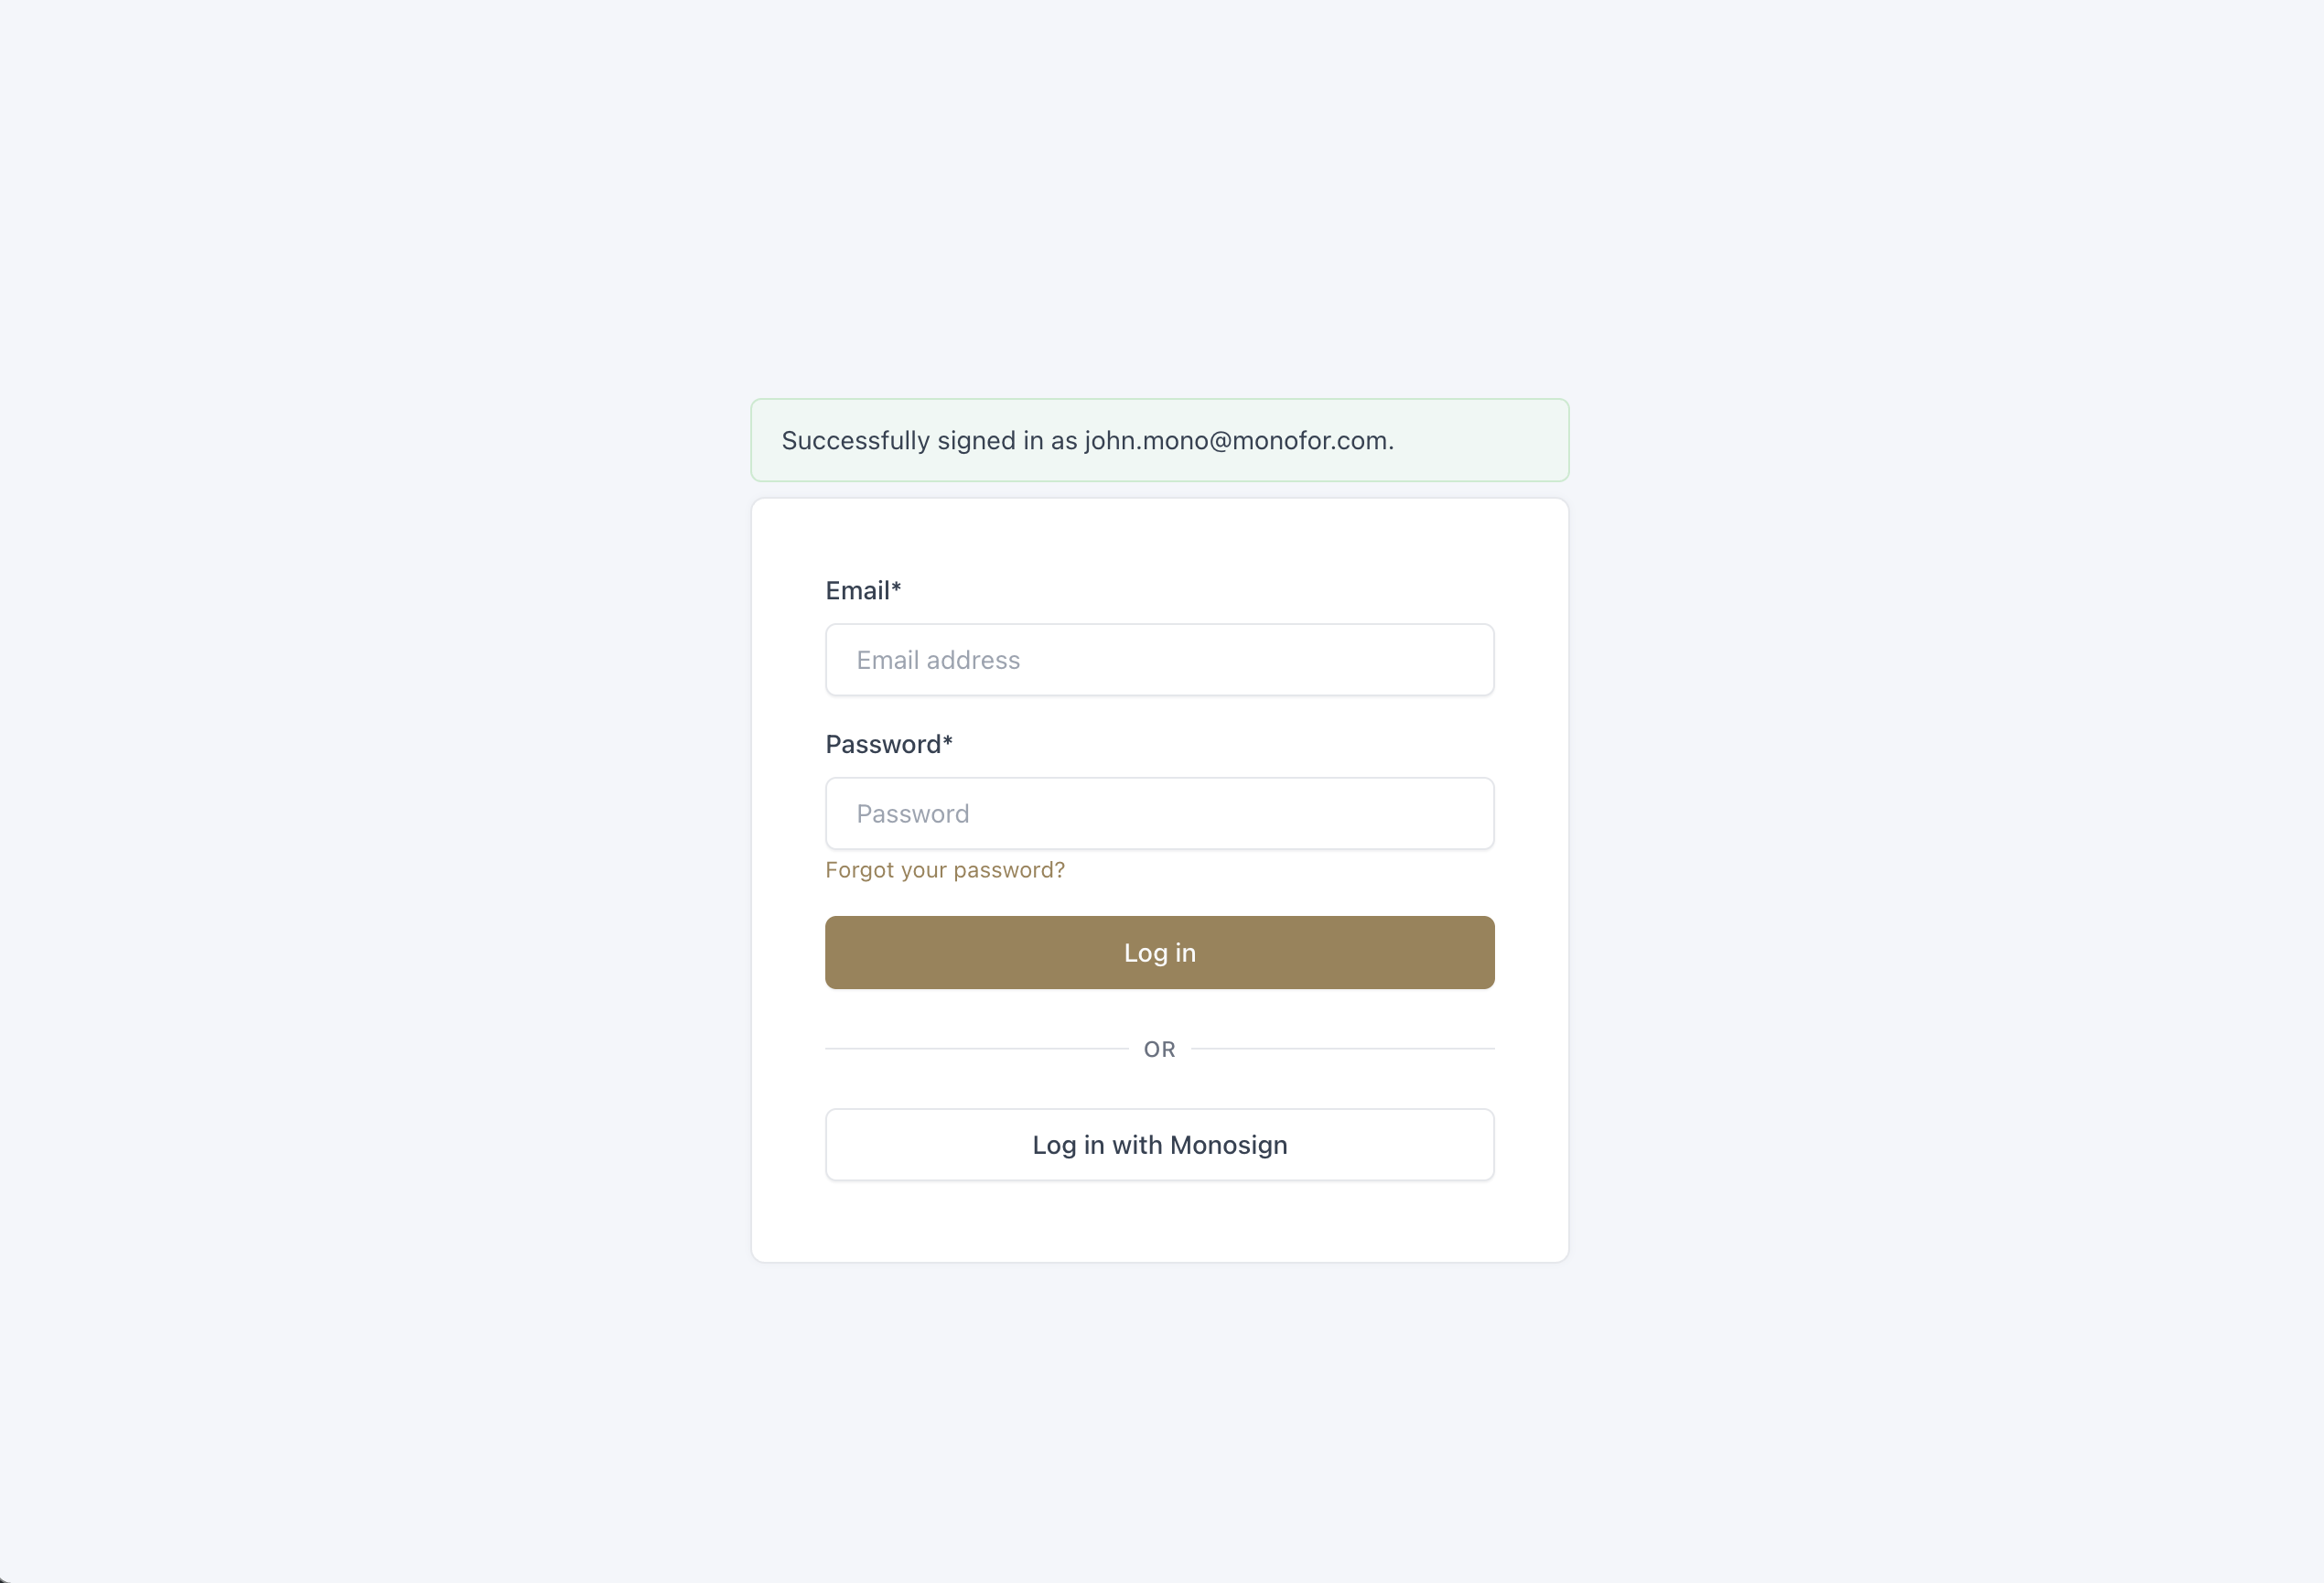
-
Click Log in with Monosign. ChiefOnboarding redirects the browser to the Monosign sign-in page of the Chiefonboarding application. You can log in passwordless with your QR code (Monofor Identity), with a Passkey or with your user name and password (Sign in with Password). If you are already signed in to Monosign, the page is skipped.
-
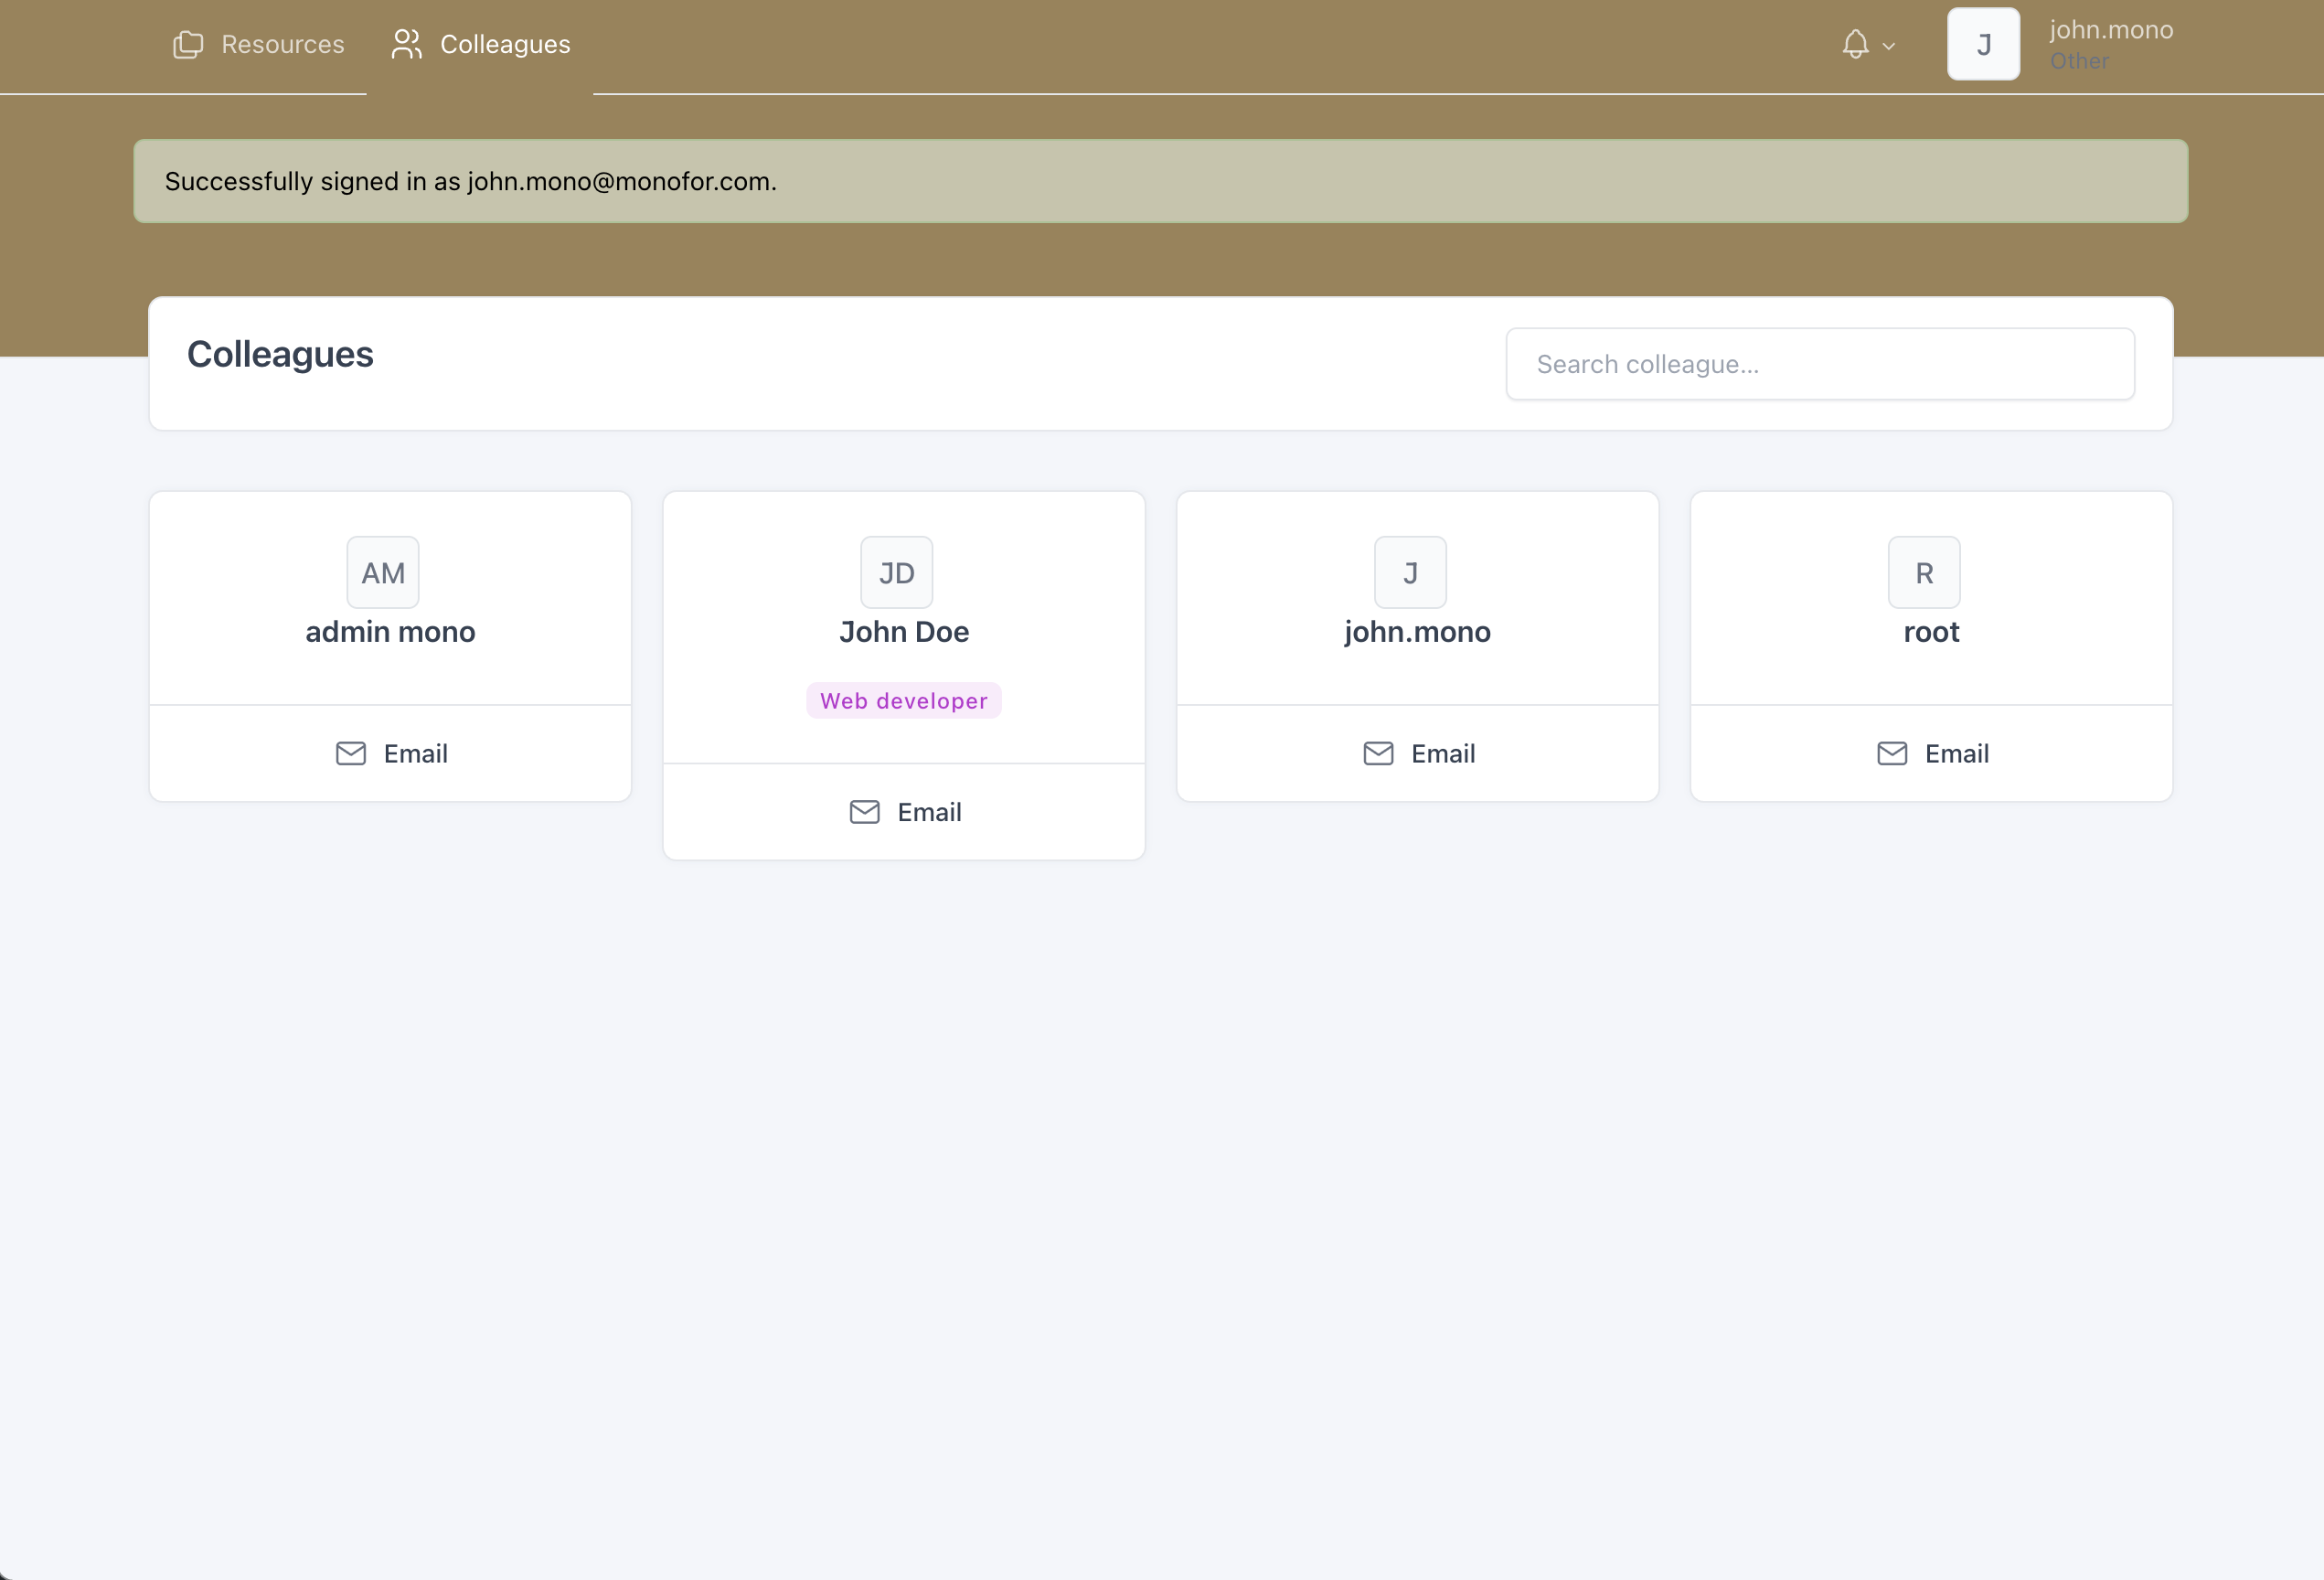
After the sign-in Monosign redirects the browser back to ChiefOnboarding. ChiefOnboarding creates the account on the first sign-in and shows the message that you are signed in. A new user with the role Other opens the Colleagues page, and the signed-in user is shown at the top right.
When you open ChiefOnboarding from the Monosign portal, a link to the single sign-on address (https://<chiefonboarding-address>/accounts/oidc/monosign/login/?process=login) opens a confirmation page of ChiefOnboarding and you click Continue once. The sign-in is started with a form (POST request), so Monosign cannot start it directly with a link. If you enter only the ChiefOnboarding address as the Url of the application, the user opens the sign-in page and clicks Log in with Monosign.
Troubleshooting
|
Symptom |
Cause |
Solution |
|---|---|---|
|
The “Log in with Monosign” button is not shown |
|
Set the variables and run |
|
The container stops at the start with the message “You need to configure OIDC differently” |
The old variable |
Remove |
|
Monosign shows a redirect URI error |
The redirect URI that ChiefOnboarding sends does not exactly match the Allowed Redirect URIs. |
Add |
|
The sign-in at Monosign succeeded, but ChiefOnboarding does not complete the login |
Monosign did not return |
Add |
|
The sign-in is refused for a user who does not exist in ChiefOnboarding |
|
Set |
|
The user signs in but sees only the Colleagues page |
No role mapping is set, so the new user gets the role Other. |
Create the administrator in ChiefOnboarding first and use the same e-mail address, or configure the |
|
ChiefOnboarding answers 400 Bad Request for the address |
The host name is not in |
Add the host name that is used in the browser to |
|
The sign-in form returns a CSRF error behind a reverse proxy |
The proxy does not send |
Send the |
|
A user cannot sign in |
The user is not assigned to the application. |
Assign the user in step 3. |
|
SAML sign-in is required |
ChiefOnboarding supports OpenID Connect only. |
Use the OIDC integration in this document. |
After completing the configuration on ChiefOnboarding and Monosign, it is better to test in a new private browser window if the OIDC SSO doesn’t work, because old session cookies of the ChiefOnboarding address may cause errors.