This document explains how to implement Monosign with GoToSocial, the lightweight ActivityPub (fediverse) social network server. It covers Single Sign-On with OpenID Connect (OIDC), which is built into GoToSocial. GoToSocial uses the Authorization Code flow and reads the user from the ID token, so the OIDC/OpenID access key of Monosign is used. Before you continue, it is better to read the GoToSocial documentation (opens in a new tab).
This configuration was tested with GoToSocial 0.22.3 running in Docker. If your version is different, please check the GoToSocial documentation.
OIDC is configured with the oidc-* settings of the GoToSocial configuration file or with the matching GTS_OIDC_* environment variables (step 4). There is no administration screen for it. SAML is not available.
Monofor has no responsibility to do GoToSocial configurations. If you need support please contact the GoToSocial community or your GoToSocial support provider.
Instructions
This documentation contains 5 main steps for integration.
Creating an application on Monosign
Configuring the OIDC/OpenID settings on Monosign
Assign a user to the GoToSocial application
Configuration Single Sign-On for GoToSocial
Sign In Test
1- Creating an Application on Monosign
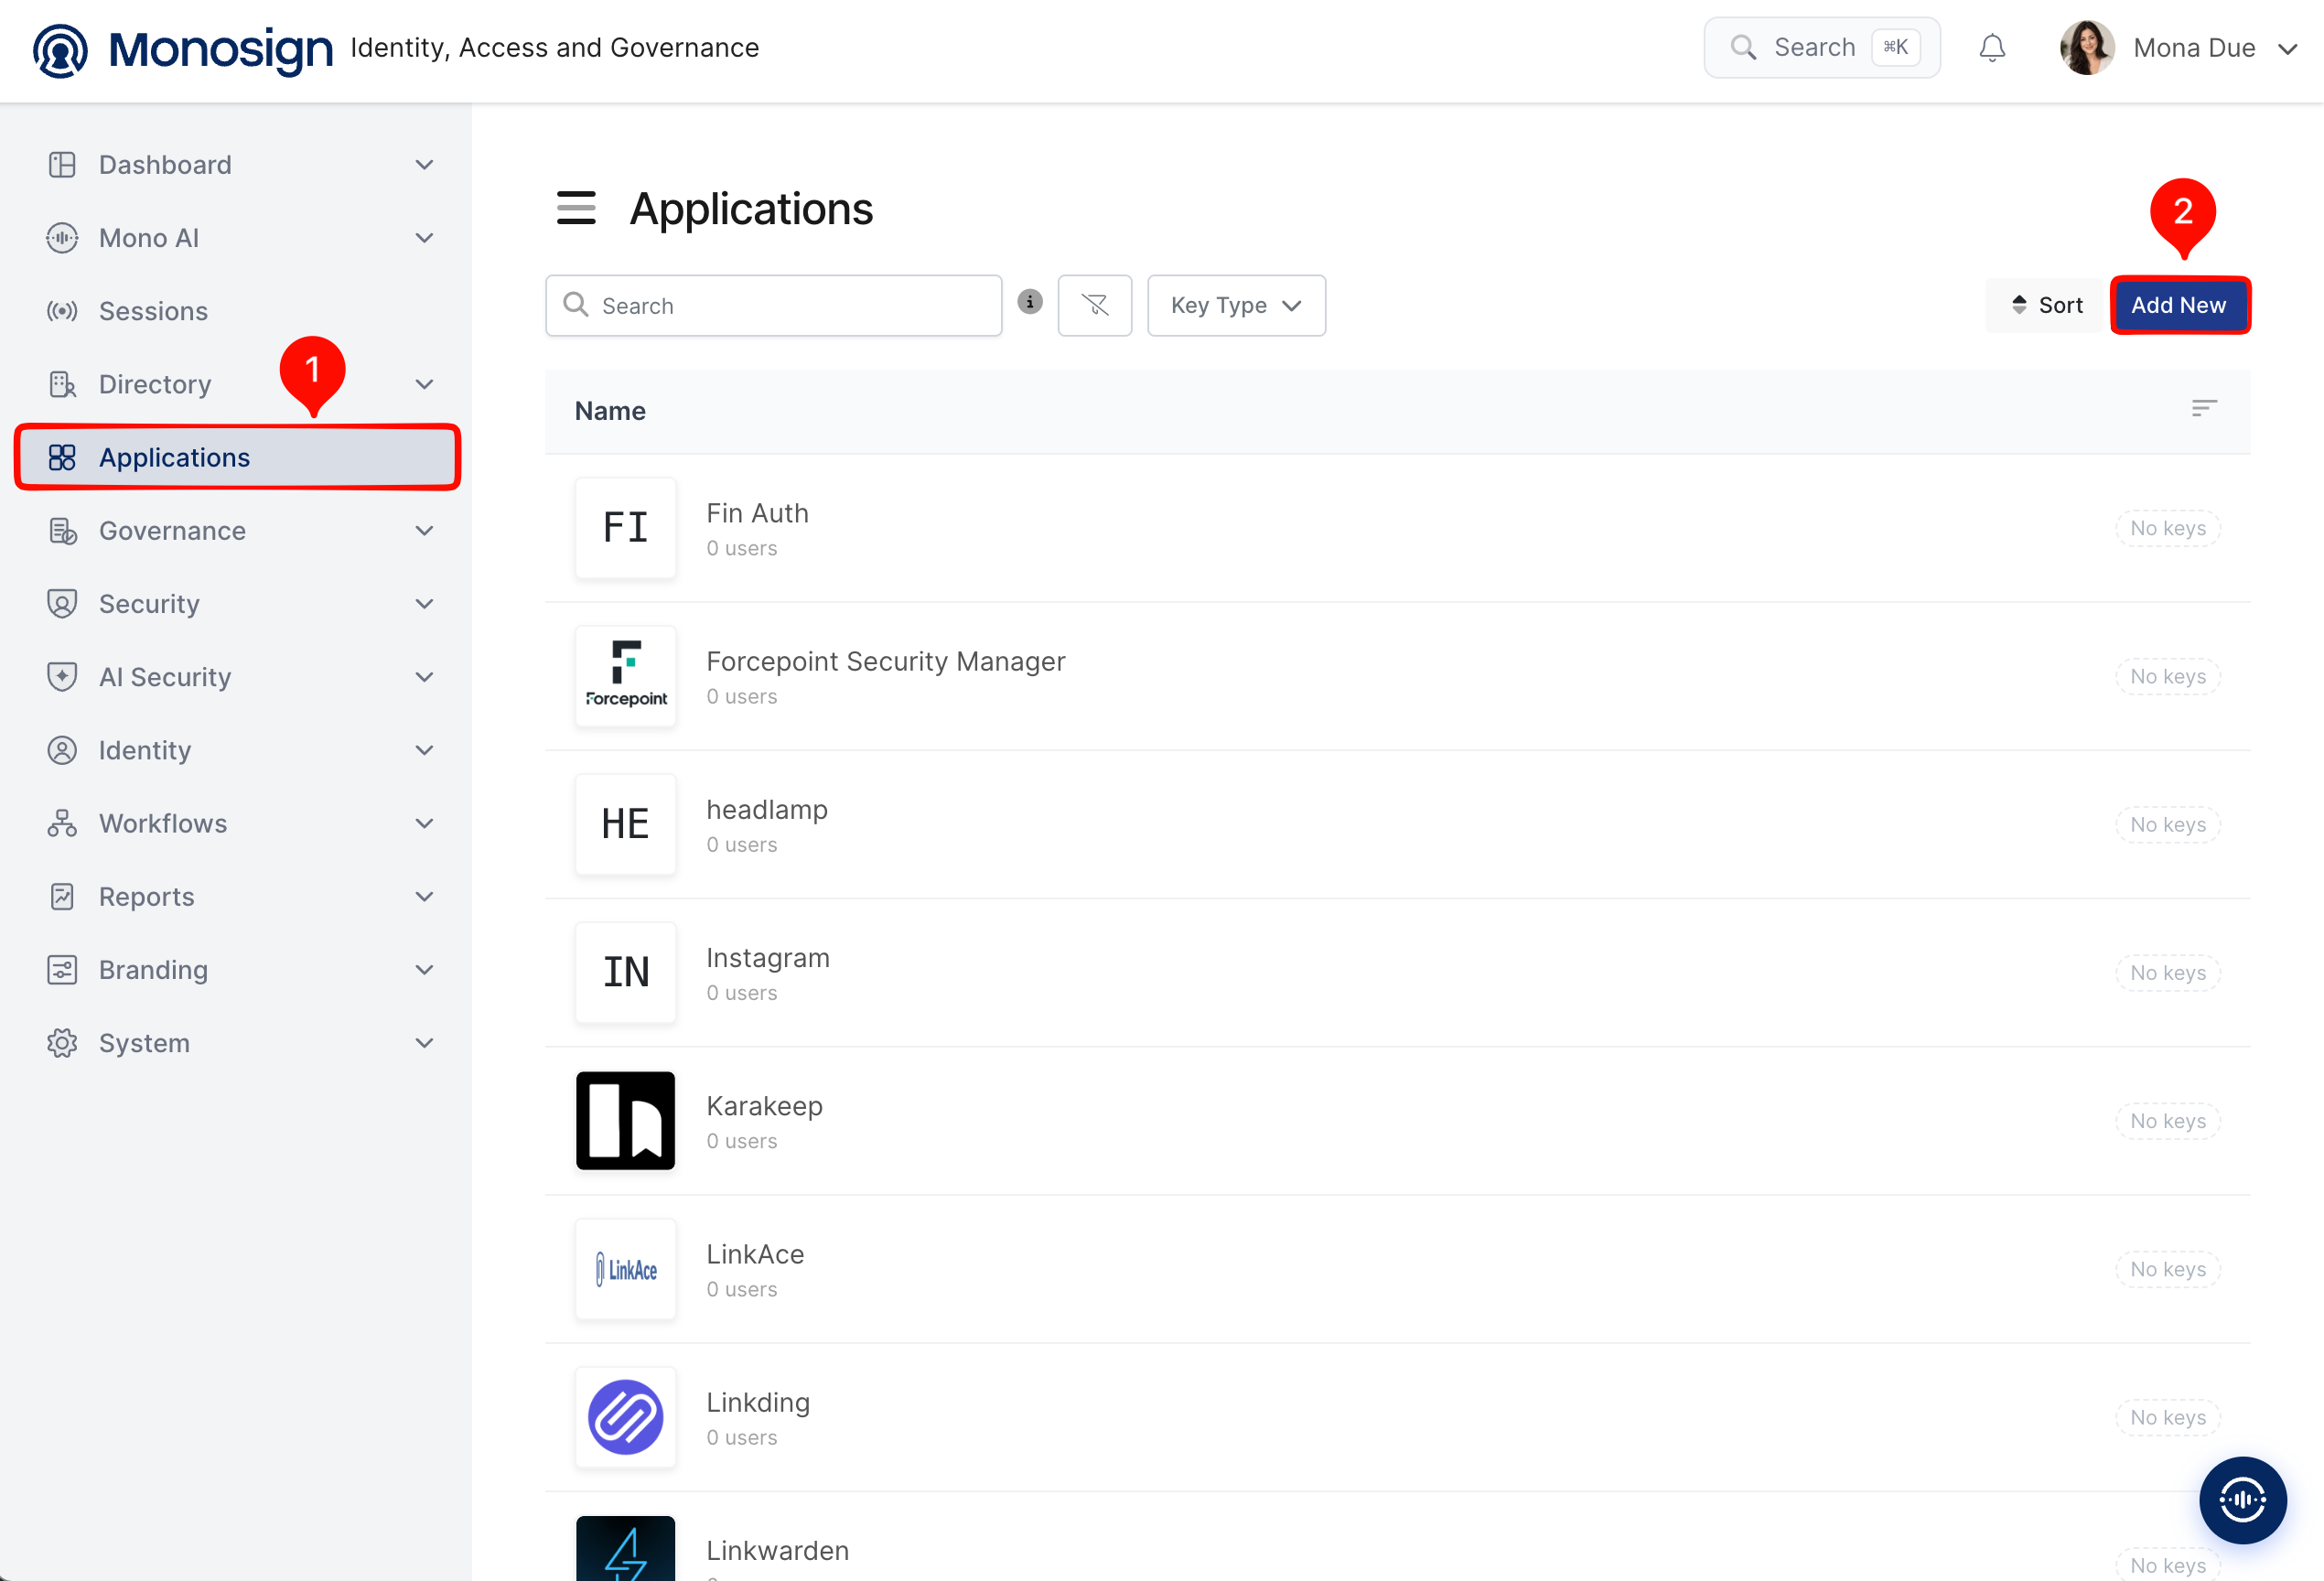
Create your application on Monosign first. Open the Applications page from the left menu and click Add New.
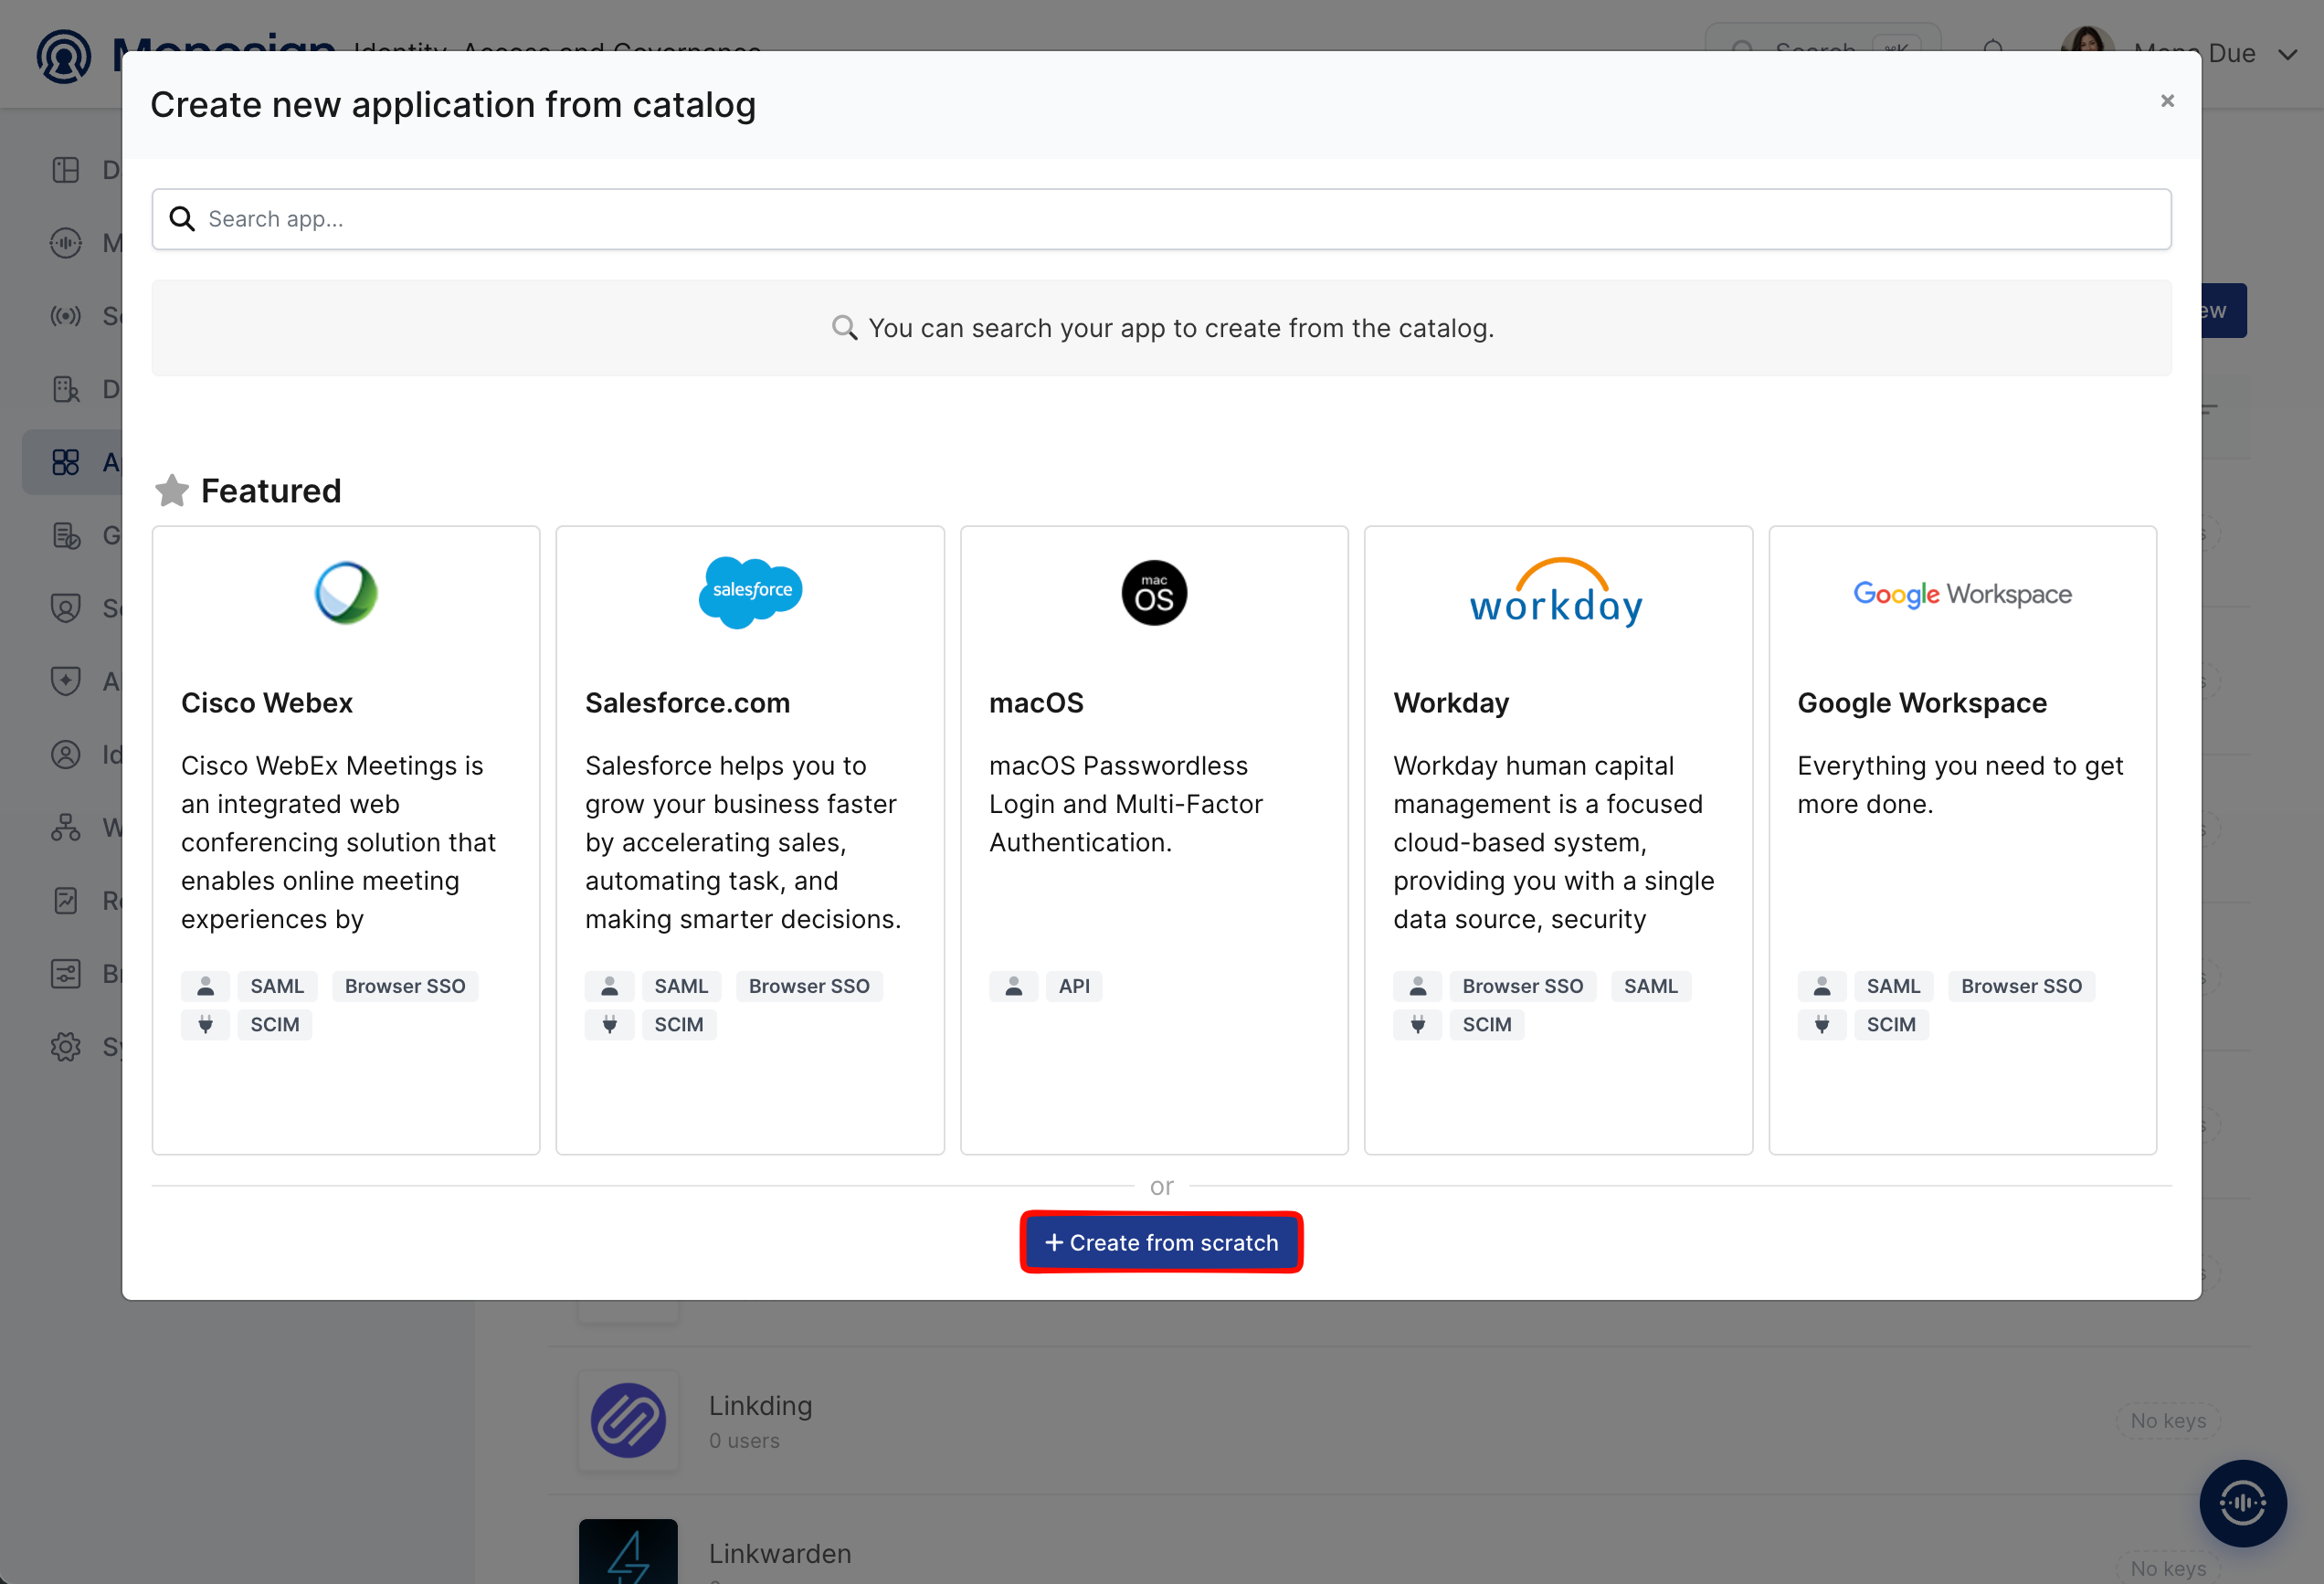
GoToSocial is not in the application catalog, so click Create from scratch.
Fill in the application details on the Application tab and click Next.
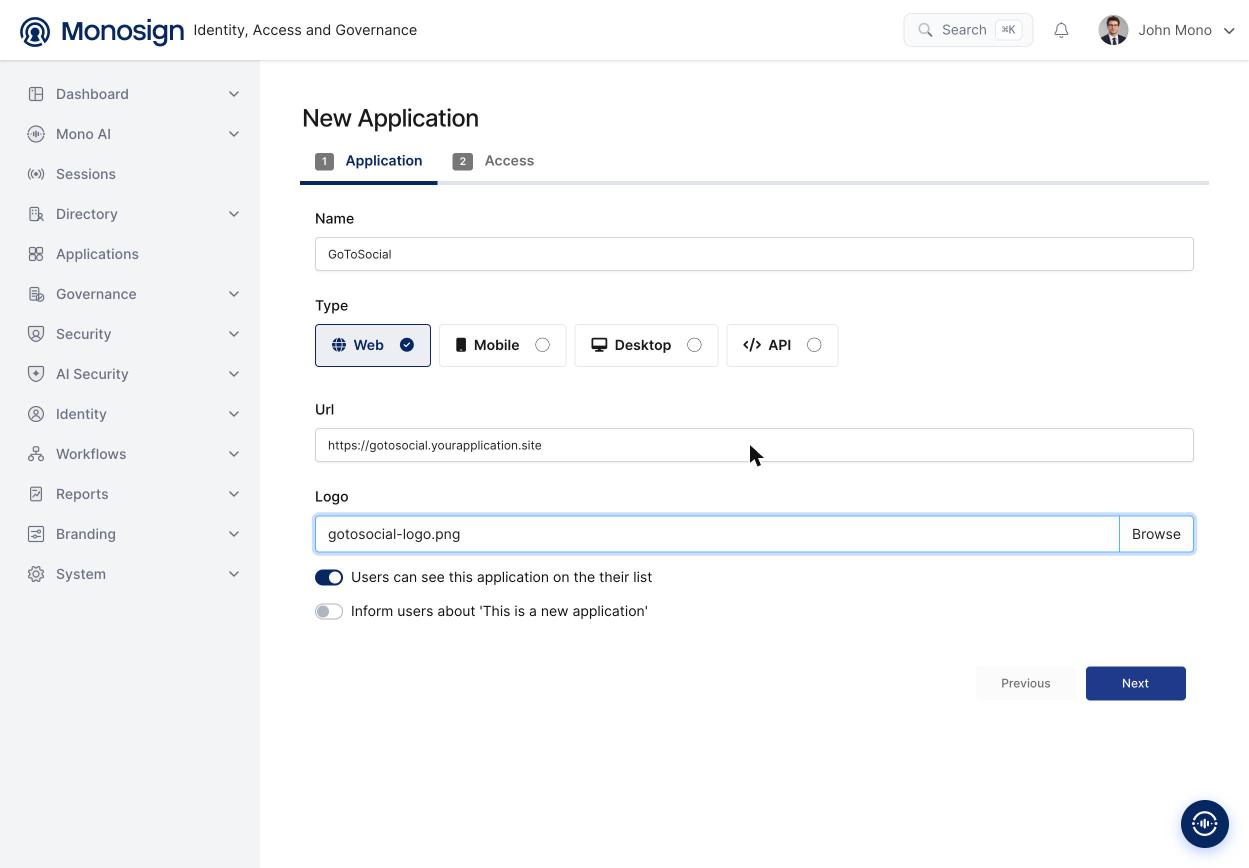
Property | Value | Description |
|---|---|---|
Name |
| Name of the application shown to users on the Monosign portal and on the Monosign sign-in page. |
Type |
| GoToSocial is accessed through a web browser. Options: Web, Mobile, Desktop, API. |
Url | Optional | Leave empty or enter the address of GoToSocial (for example |
Logo | Optional | Browse and upload a logo (PNG or JPG, max 1 MB); it is also shown on the Monosign sign-in page. |
Users can see this application on their list |
| Displays the application on the user portal. |
On the Access tab define who can reach the application and click Create Application.
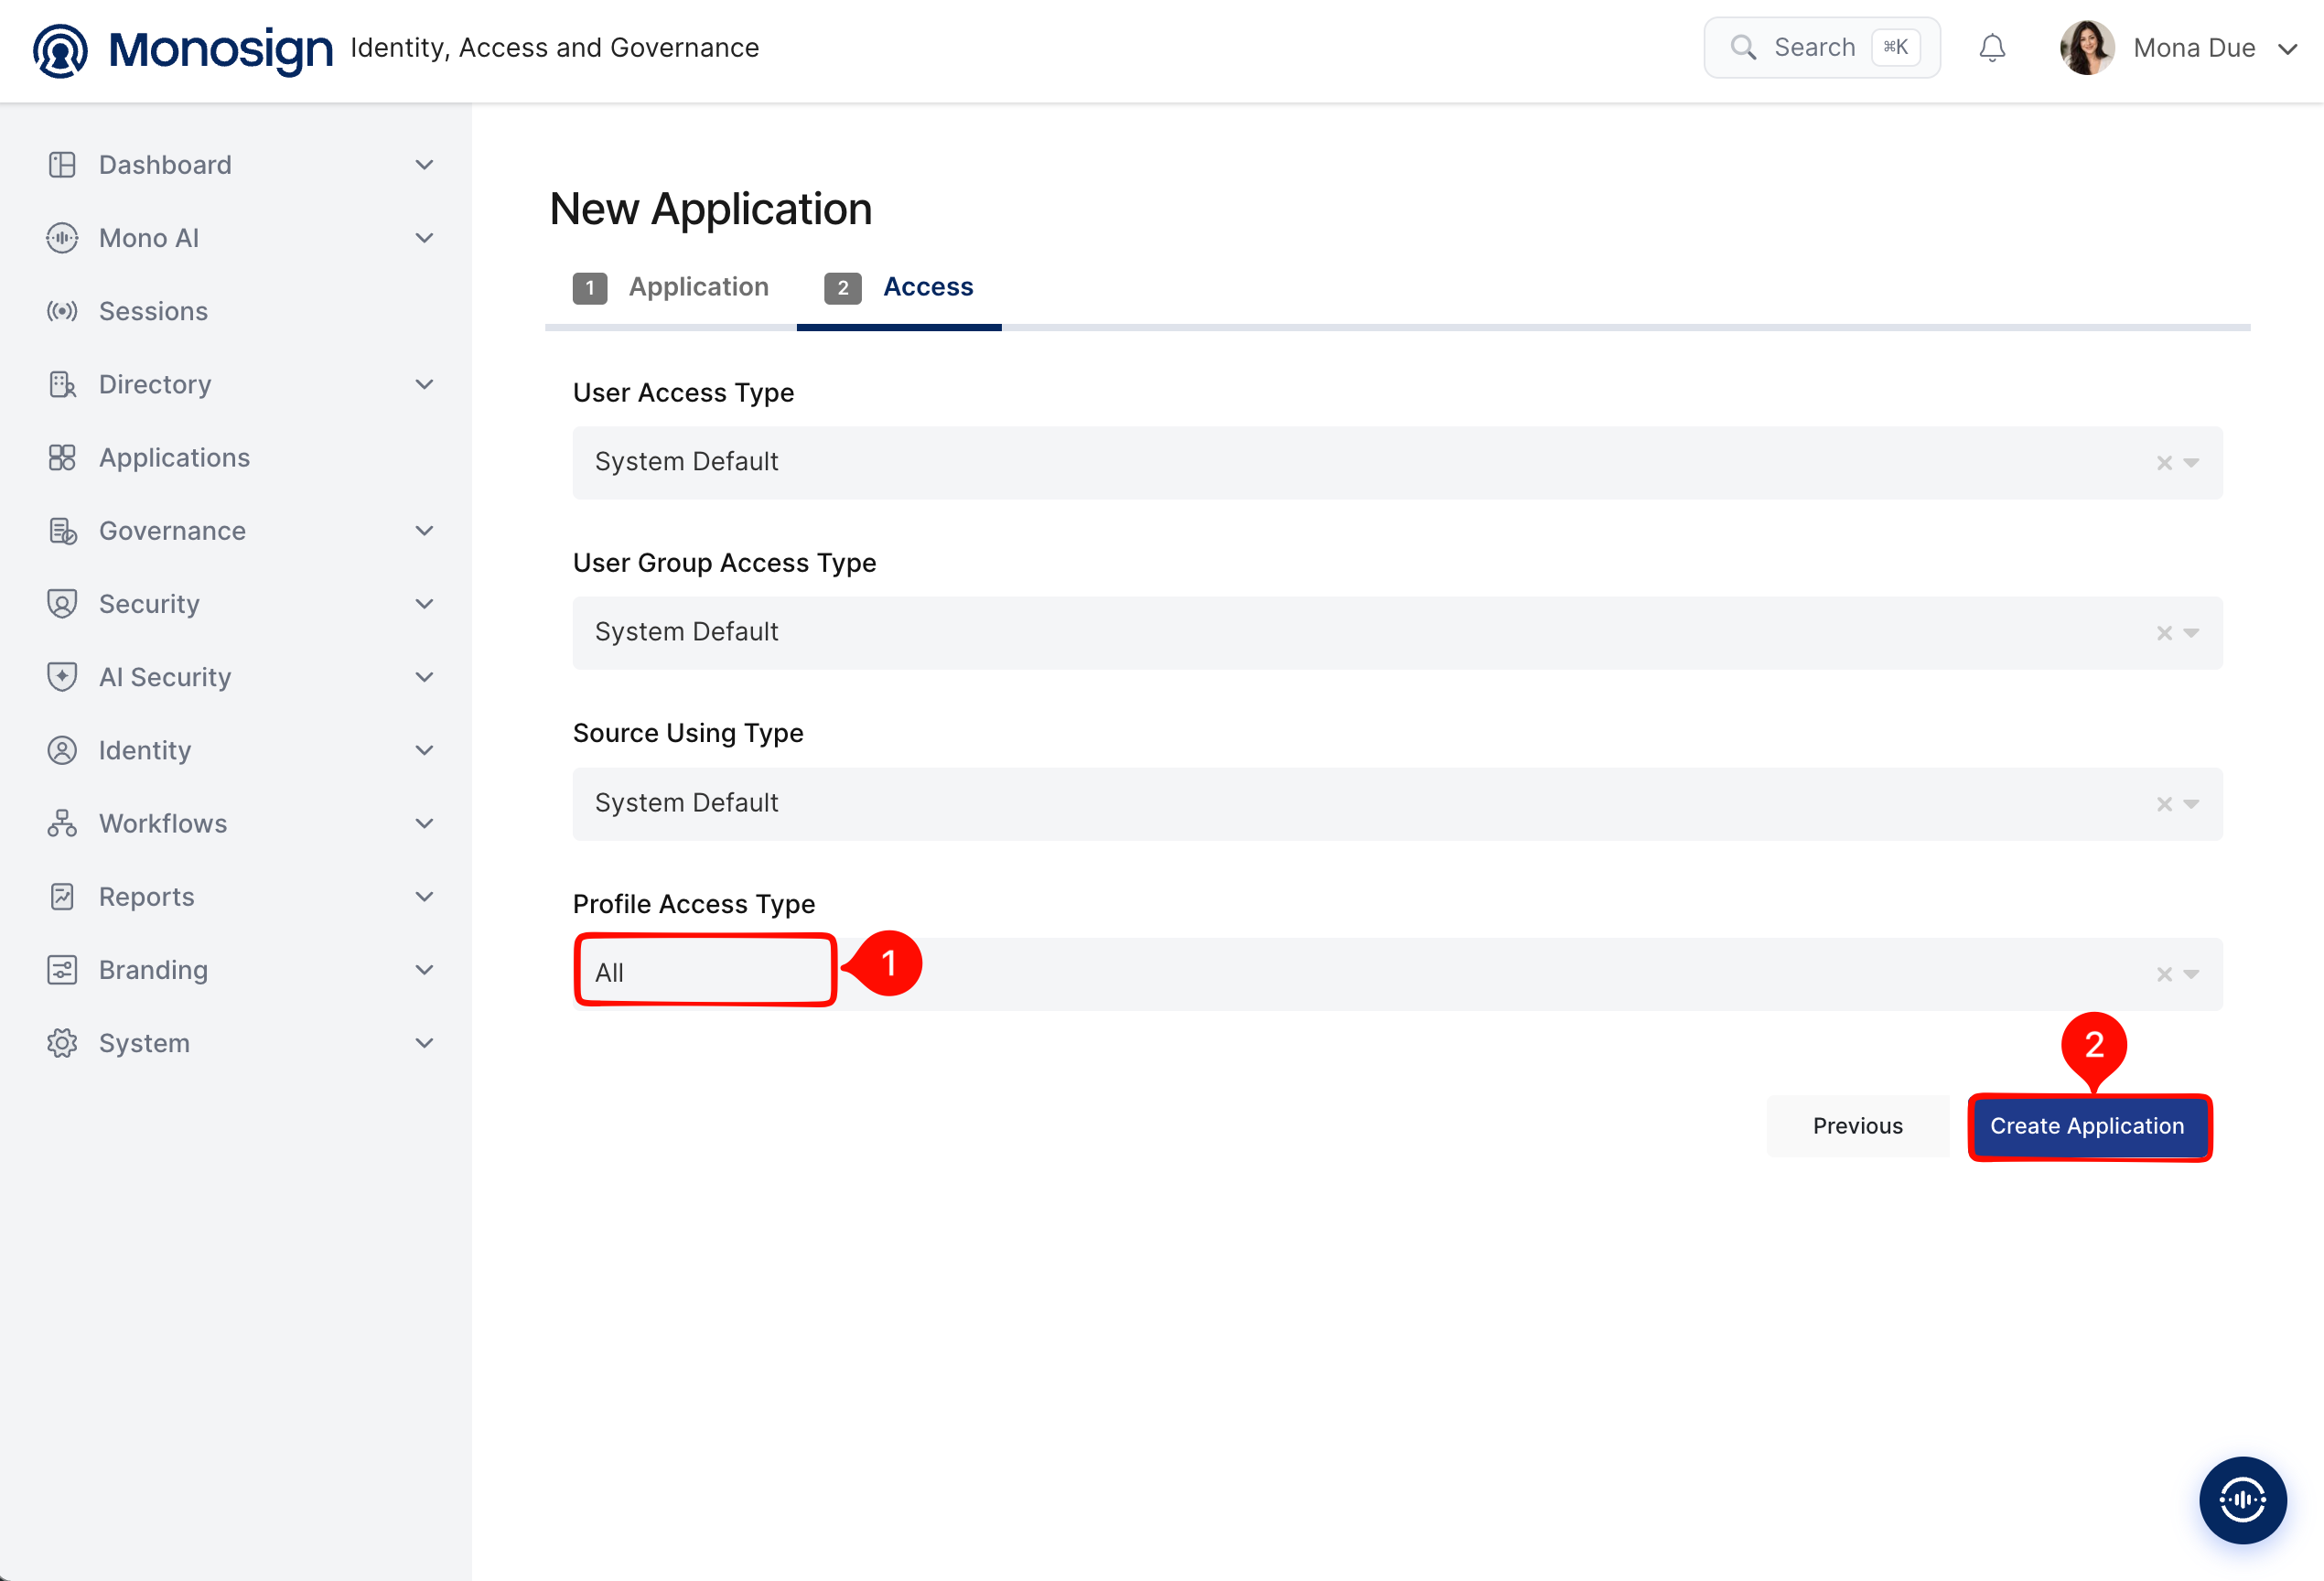
Property | Value | Description |
|---|---|---|
User Access Type |
| Defines which users can access this application. Options: Only Assigned Users, All Users, System Default. |
User Group Access Type |
| Defines the application’s user group access. |
Source Using Type |
| Defines which user sources the application can use. |
Profile Access Type |
| Defines which user profile attributes are available to the application (Options: Restricted, All). GoToSocial needs the e-mail address and the user name of the user. |
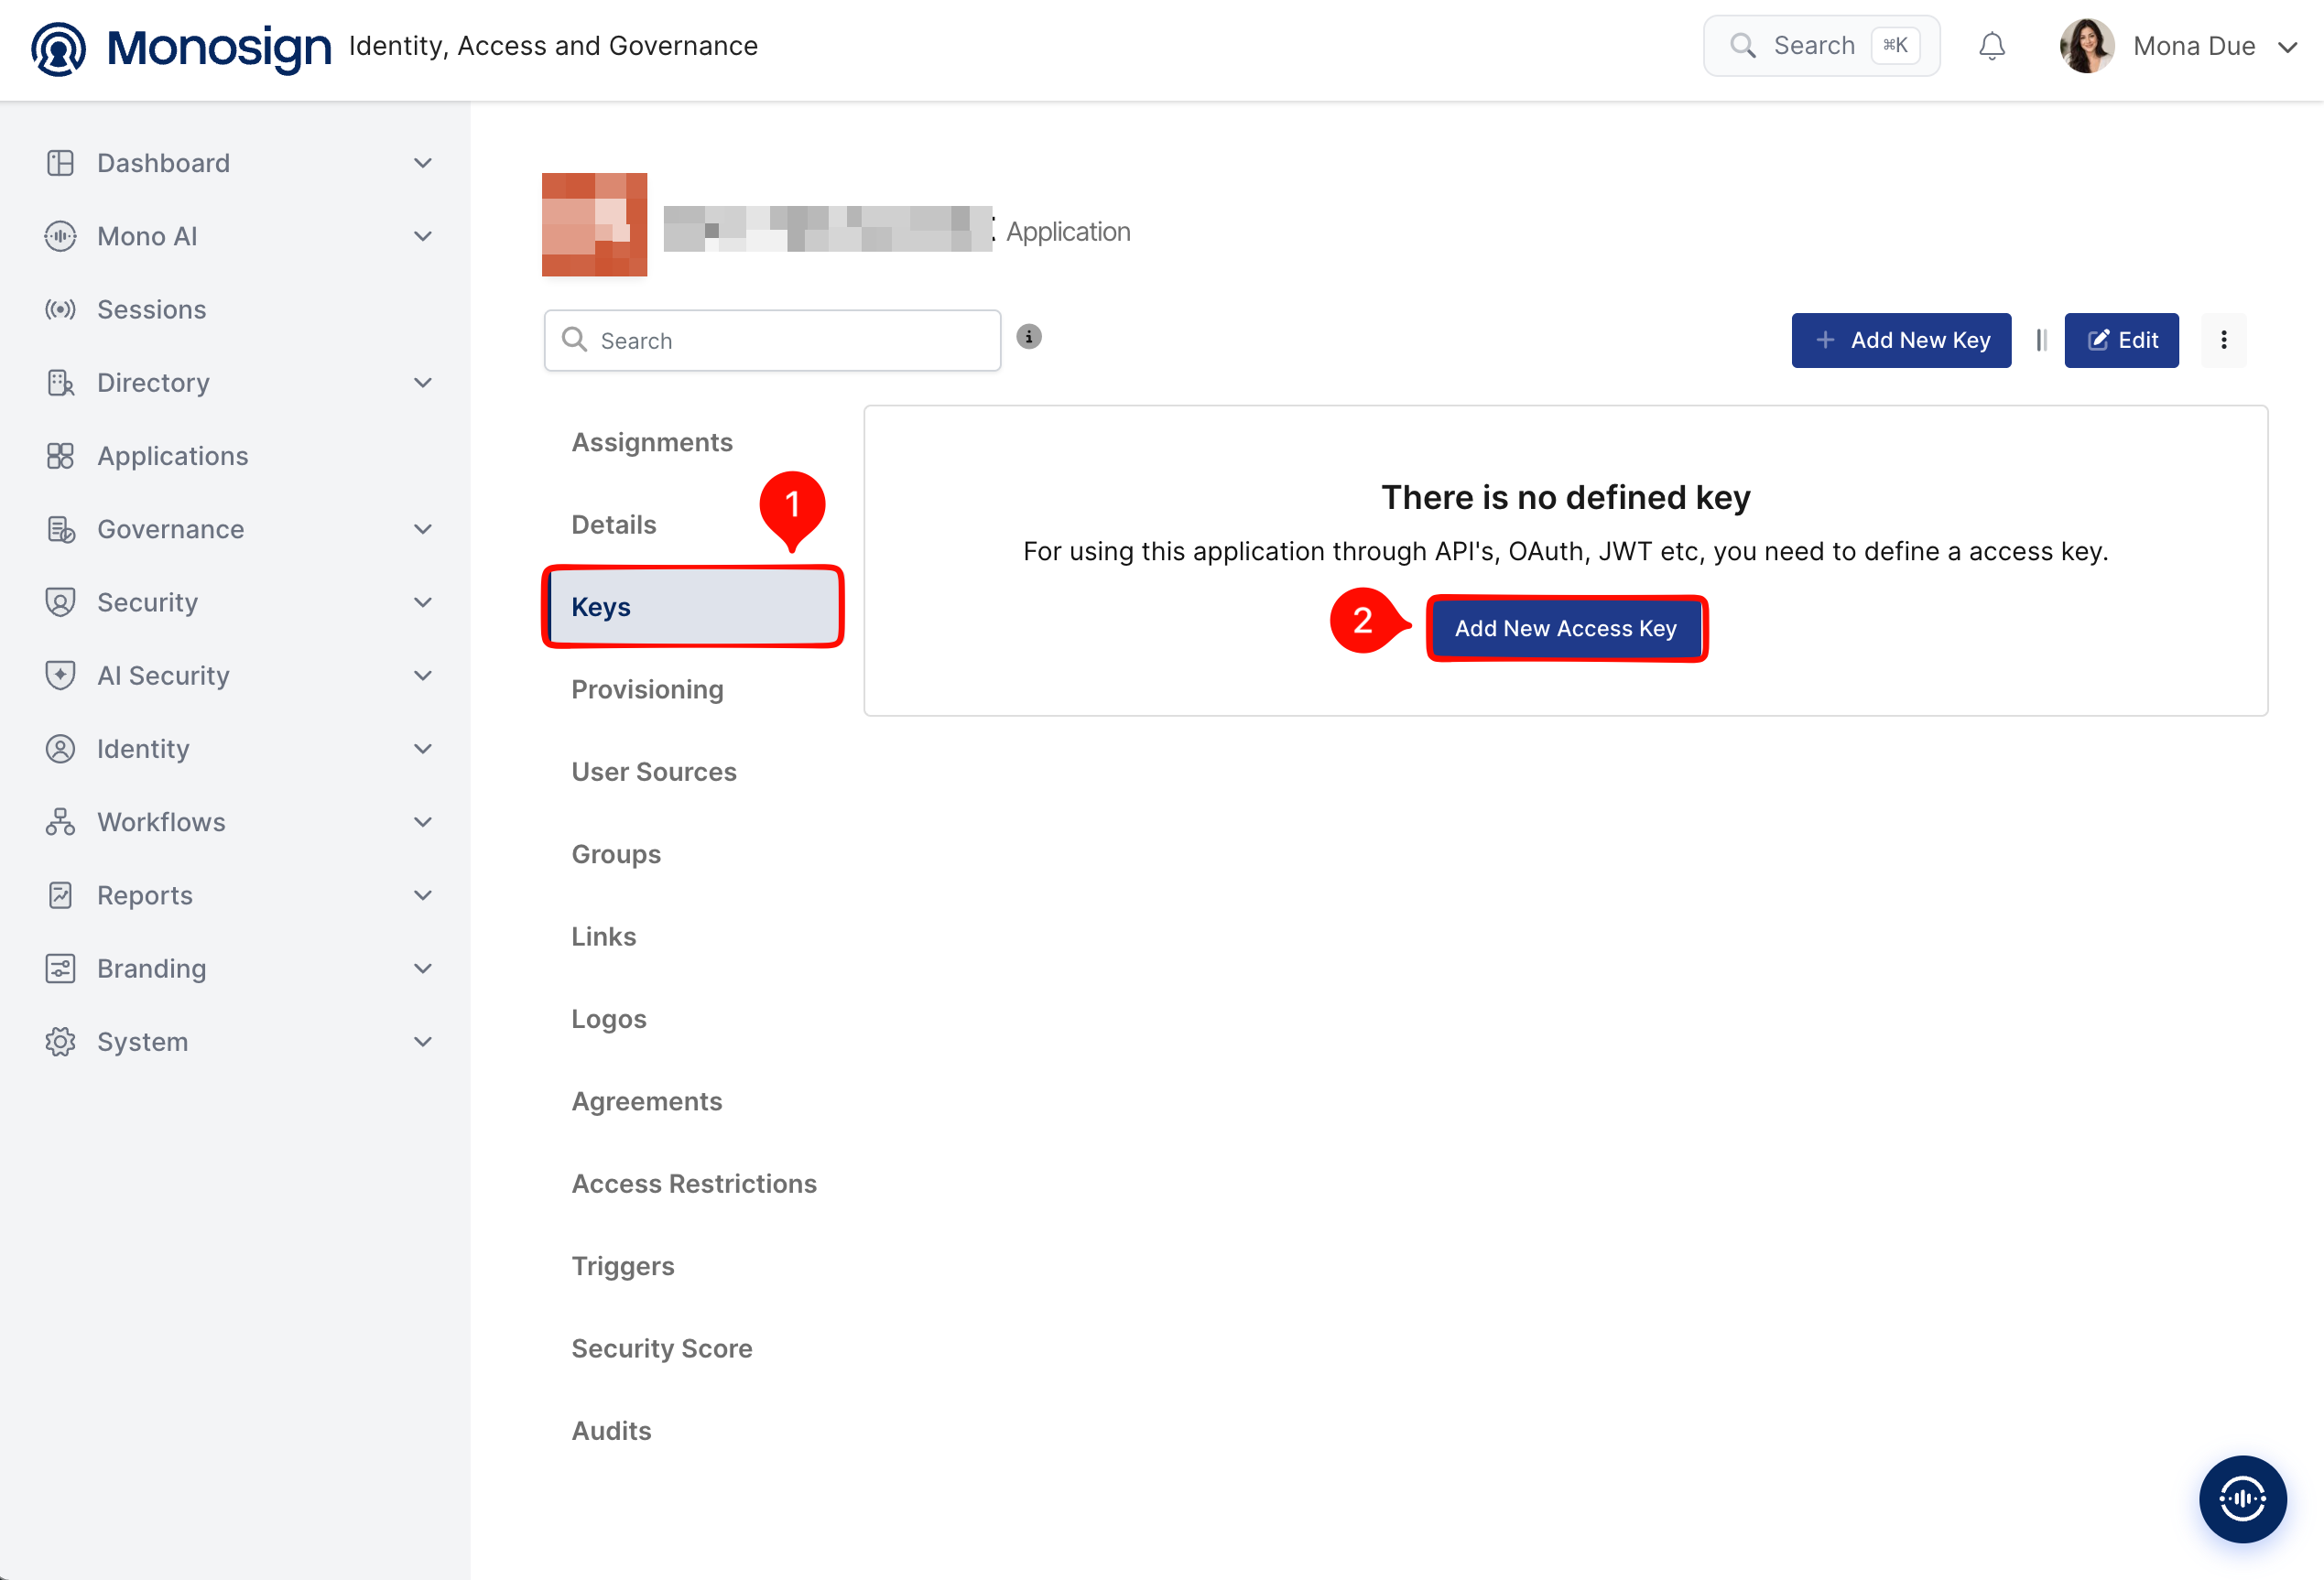
After the application is created, click Keys and add a new Access Key for OIDC/OpenID access.
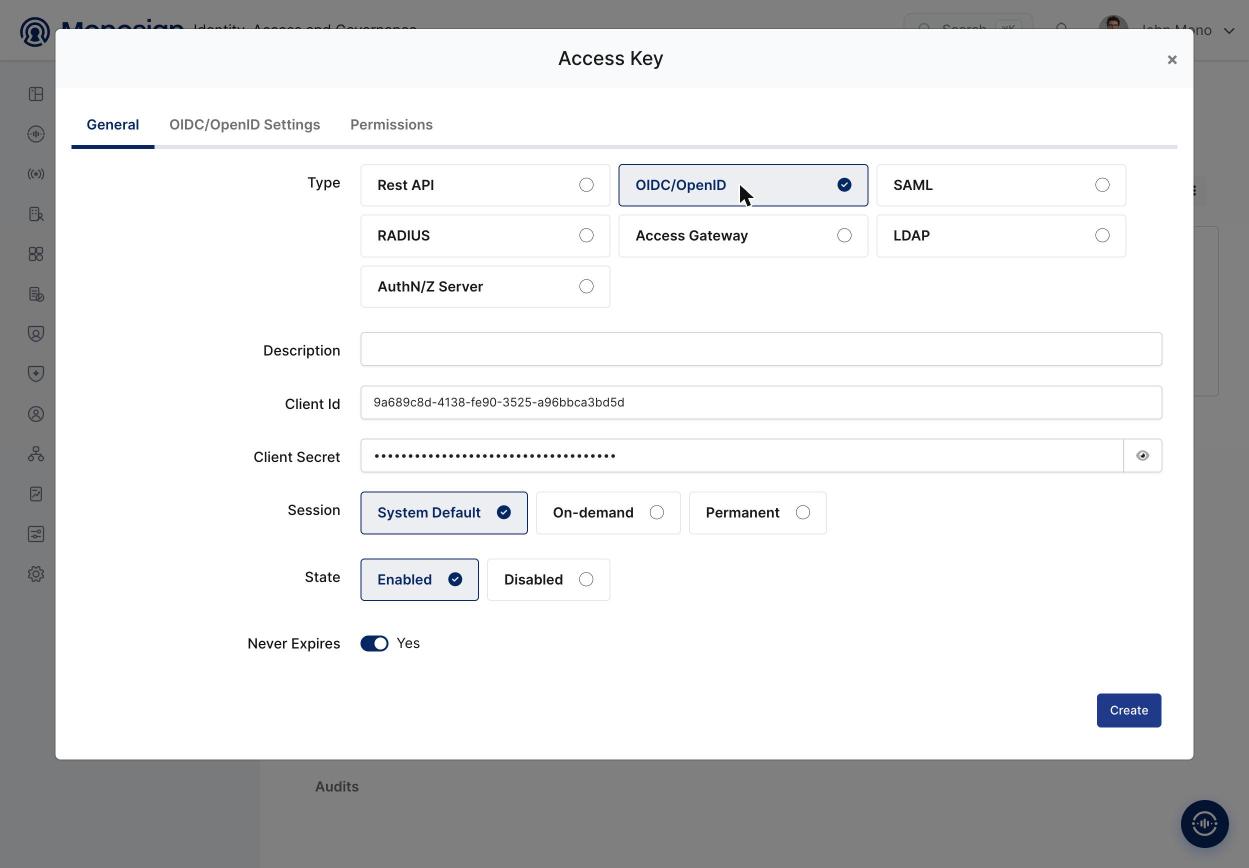
Select OIDC/OpenID as the key type and click Create. Monosign generates the Client Id and Client Secret automatically.
Configuration details for the GoToSocial application are provided as follows:
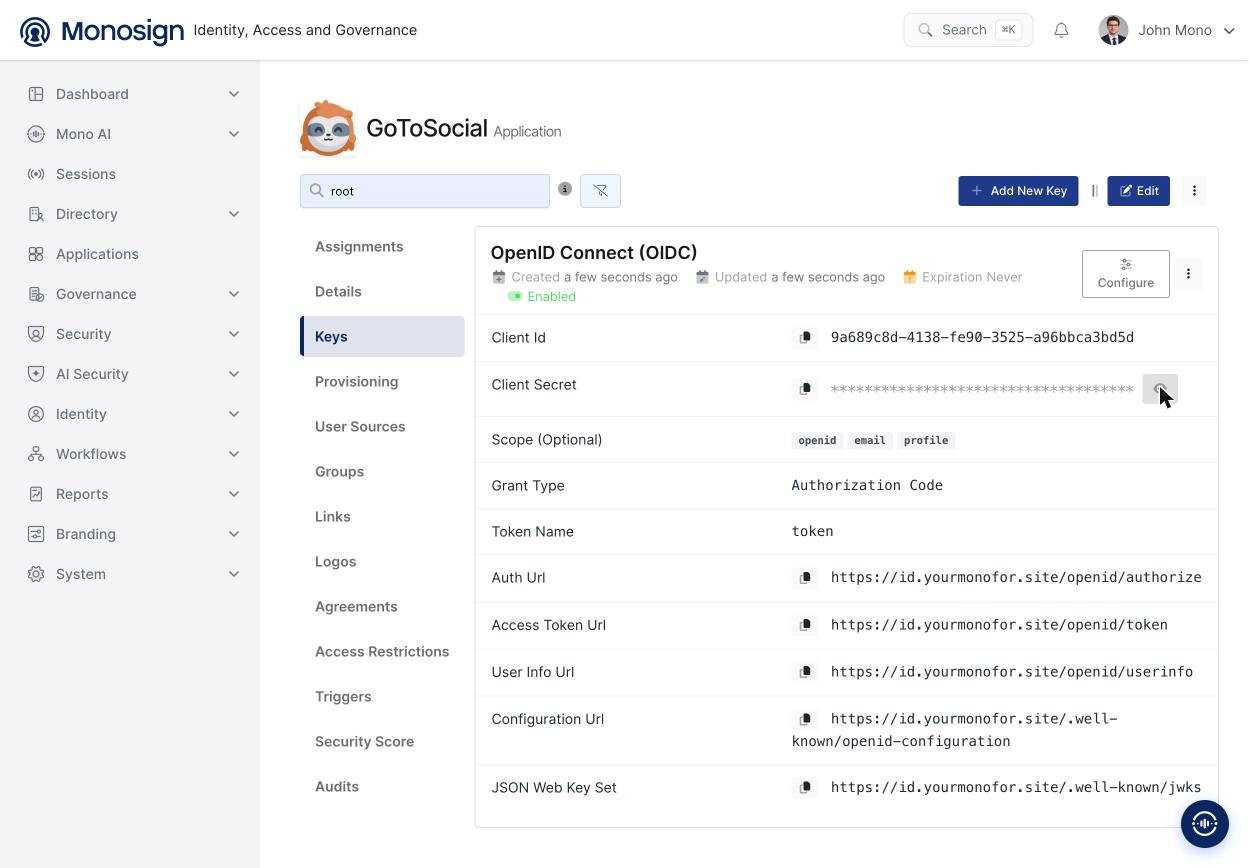
Monosign value | Example | Used in GoToSocial as |
|---|---|---|
Client Id |
|
|
Client Secret |
|
|
Issuer |
|
|
2- Configuring the OIDC/OpenID Settings on Monosign
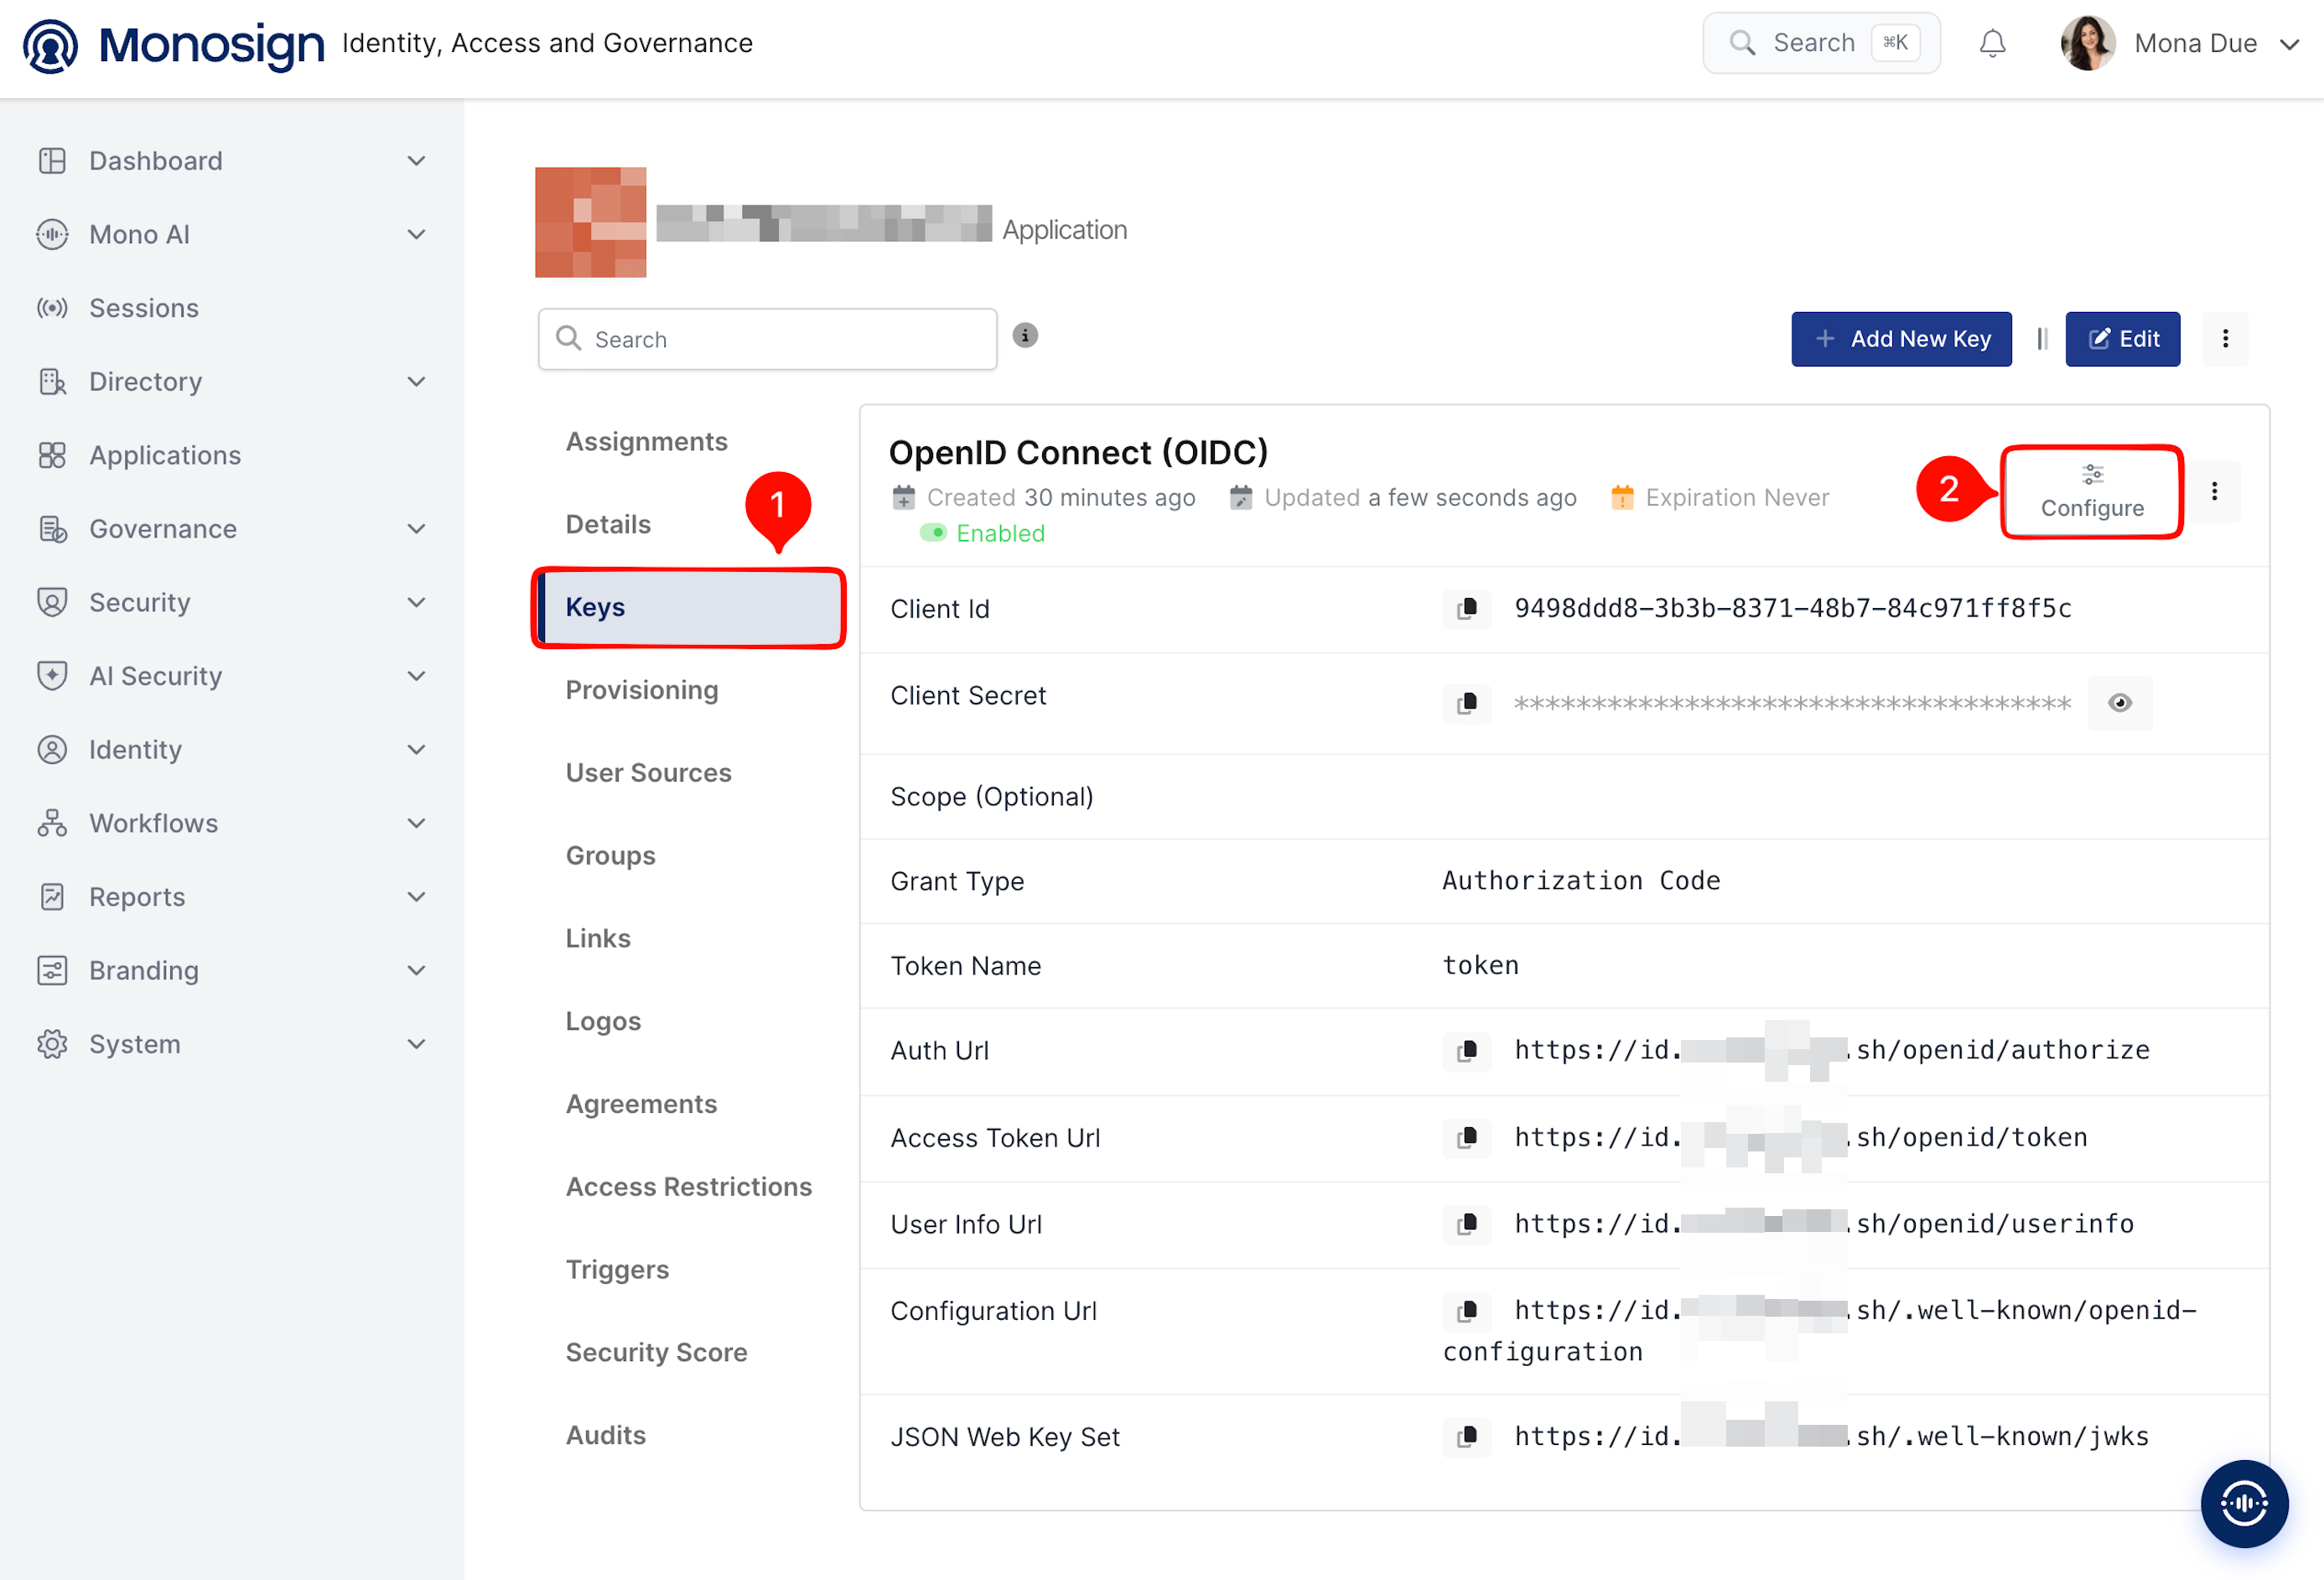
Open the Keys tab of the application and click the Configure button of the OpenID Connect (OIDC) key to open the OIDC/OpenID settings.
Add the callback address of GoToSocial to Allowed Redirect URIs, enter the scopes in the Scope field, then press Update.
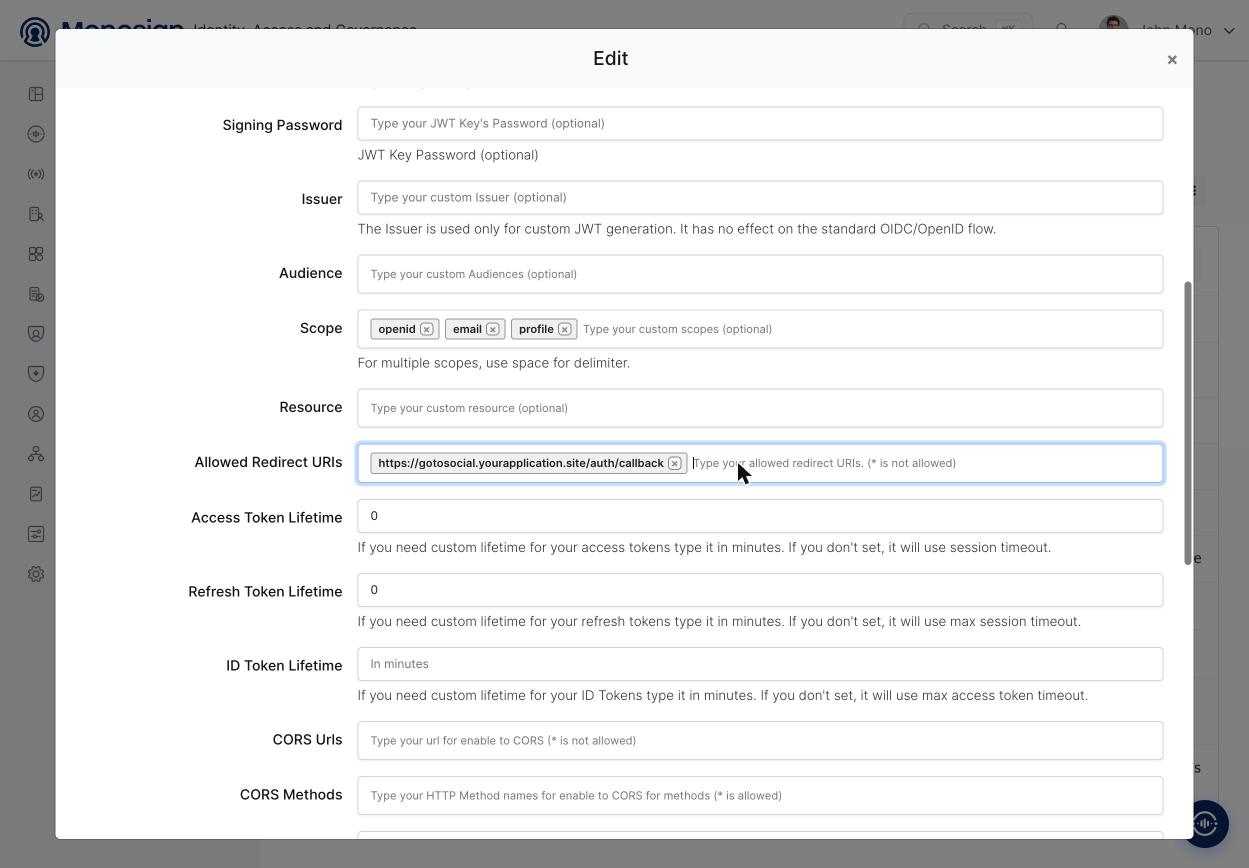
Property | Value | Description |
|---|---|---|
Allowed Redirect URIs |
| The address where Monosign sends the user back after sign-in. Use the public (HTTPS) address of GoToSocial, exactly as it is written here. |
Scope |
| Enter the three scopes one by one. They must be the same as |
Other fields | Empty / default | The other fields (Issuer, Audience, Resource, token lifetimes, CORS) are not needed. |
3- Assign a User to the GoToSocial Application
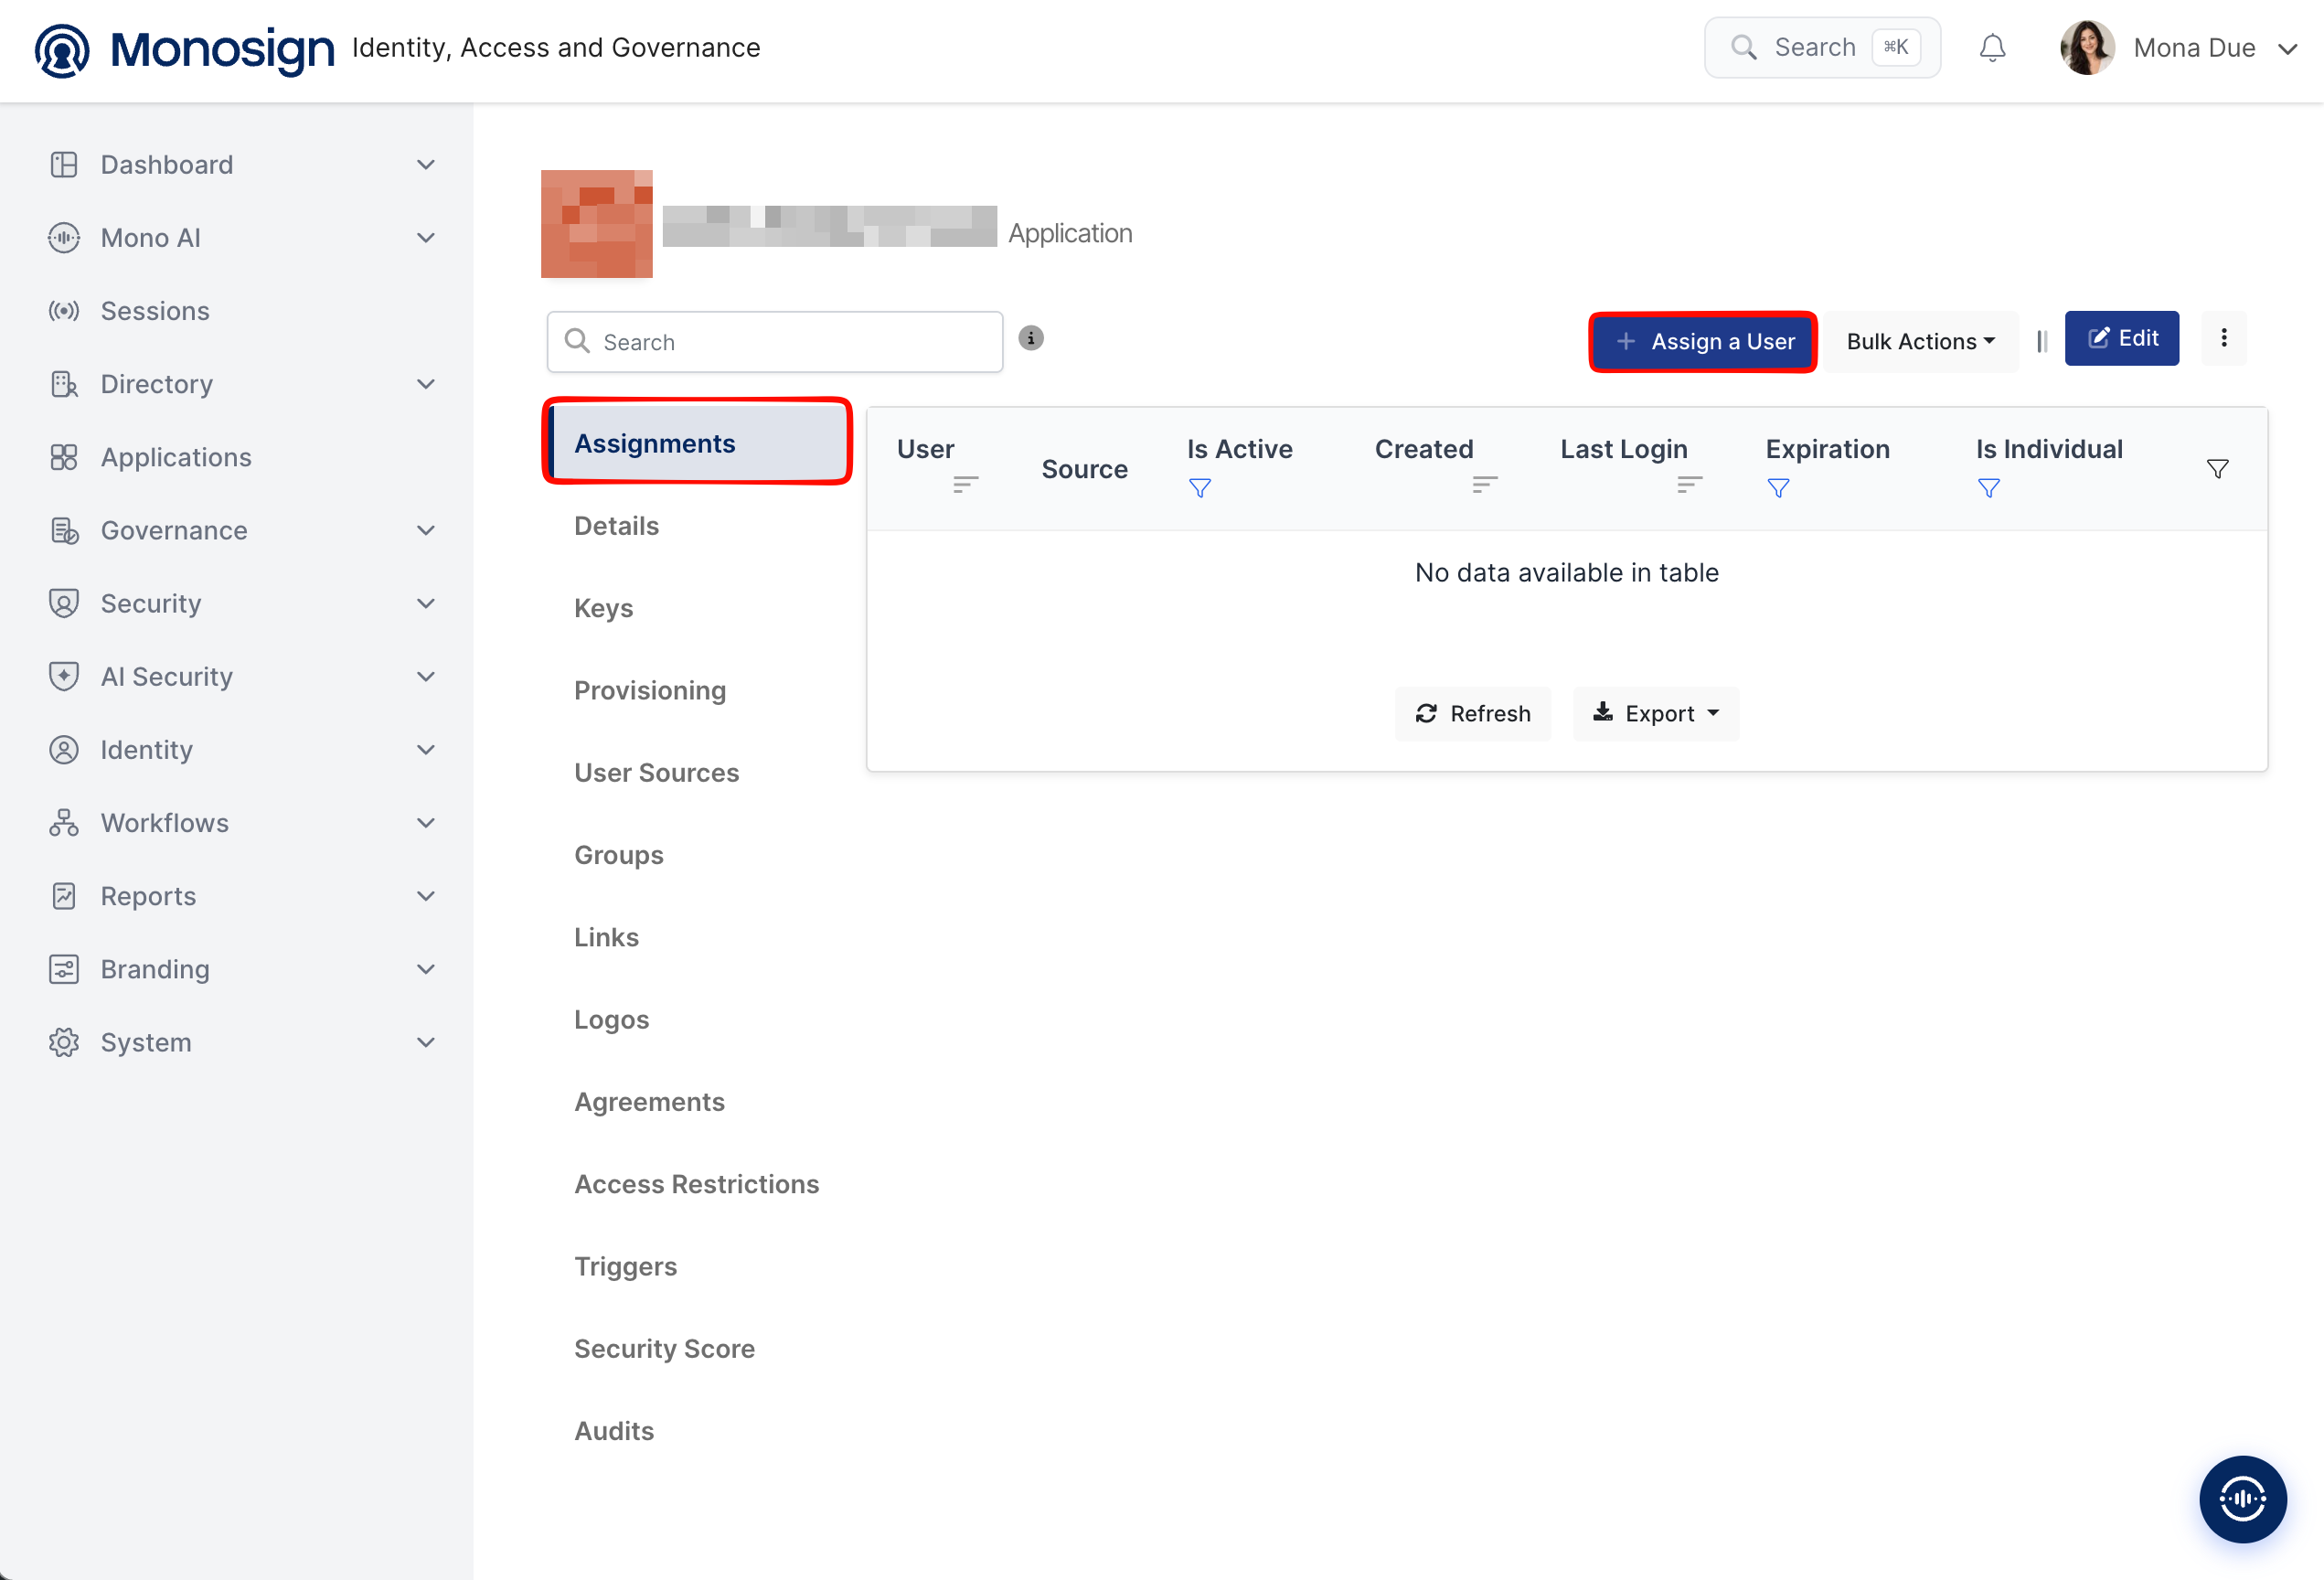
Open the application in Monosign, click the Assignments tab and click Assign a User.
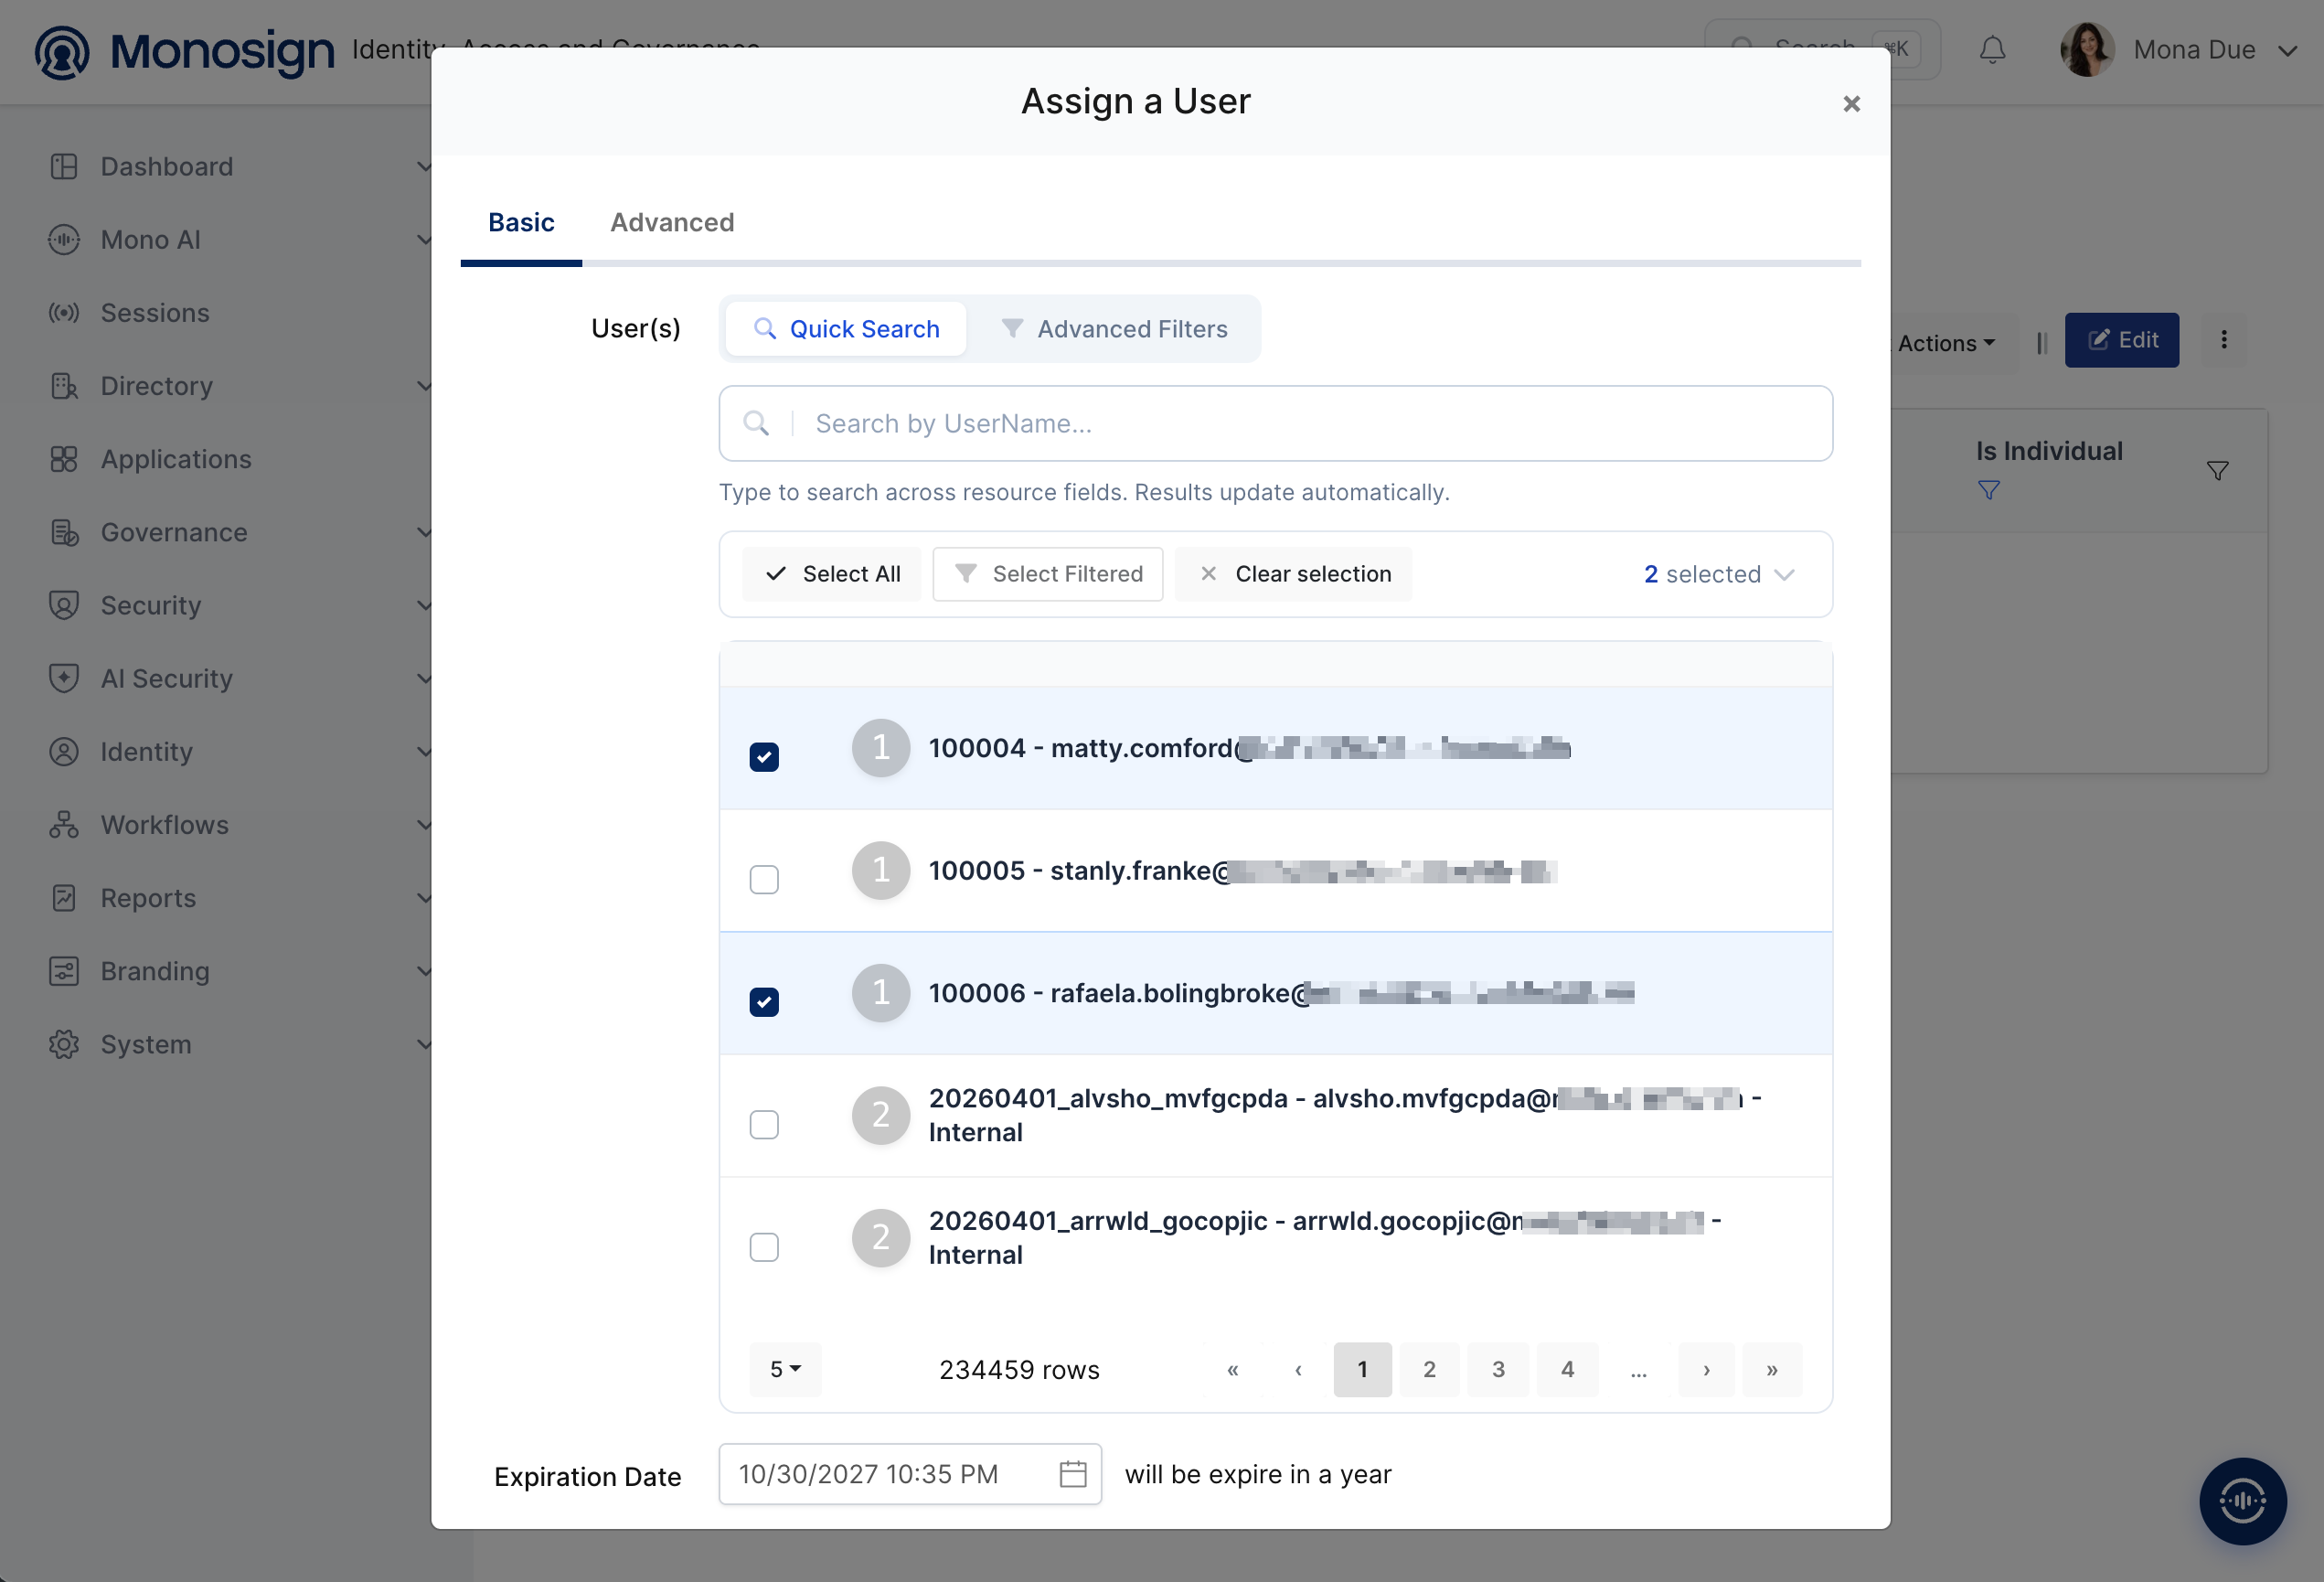
Search and select the users who can sign in to GoToSocial, check the Expiration Date and save. You can select more than one user. Every user needs an e-mail address and a user name in Monosign.
4- Configuration Single Sign-On for GoToSocial
As we mentioned at the start, please check out the GoToSocial documentation first. GoToSocial has no administration screen for OIDC: add the settings below to the GoToSocial configuration file (config.yaml) or, as in this document, to the environment variables of the container, and restart GoToSocial.
environment:
  GTS_OIDC_ENABLED: "true"
  GTS_OIDC_IDP_NAME: Monosign
  GTS_OIDC_ISSUER: https://<monosign-host>/
  GTS_OIDC_CLIENT_ID: <client-id>
  GTS_OIDC_CLIENT_SECRET: <client-secret>
  GTS_OIDC_SCOPES: openid,email,profile
  GTS_OIDC_LINK_EXISTING: "true"
Setting | Value | Description |
|---|---|---|
|
| Turns on OIDC. GoToSocial then replaces the e-mail and password login completely. |
|
| Name of the identity provider shown to users. |
|
| Address of Monosign with the slash at the end. GoToSocial reads the discovery document from it. |
| Client Id | Copied from the Monosign OIDC/OpenID Access Key Details created in the first step. |
| Client Secret | Copied from the same page. Keep it in a protected file (for example an |
|
|
|
|
| Links the Monosign user to an existing GoToSocial account with the same e-mail address (see the administrator note below). |
GoToSocial identifies the user with the claim sub and needs a non-empty email claim; the e-mail address must be unique on the instance. The configured host (GTS_HOST) cannot be changed after the first start. When GoToSocial is behind a reverse proxy, add the address of the proxy to GTS_TRUSTED_PROXIES and make sure the proxy sends X-Forwarded-Proto: https.
Administrator: GoToSocial gives administrator rights from the groups claim (oidc-admin-groups), which Monosign does not send. Create the administrator account first with the command line, using the same e-mail address as the Monosign user, and promote it. With oidc-link-existing on, the Monosign user then signs in to this account as an administrator:
gotosocial admin account create --username <name> --email <e-mail> --password <password>
gotosocial admin account confirm --username <name>
gotosocial admin account promote --username <name>
5- Sign In Test
Now try to log in to GoToSocial using Monosign SSO. Open a new browser window (or a private window) and type https://<gotosocial-address>/settings. The page asks for the instance; click Login.
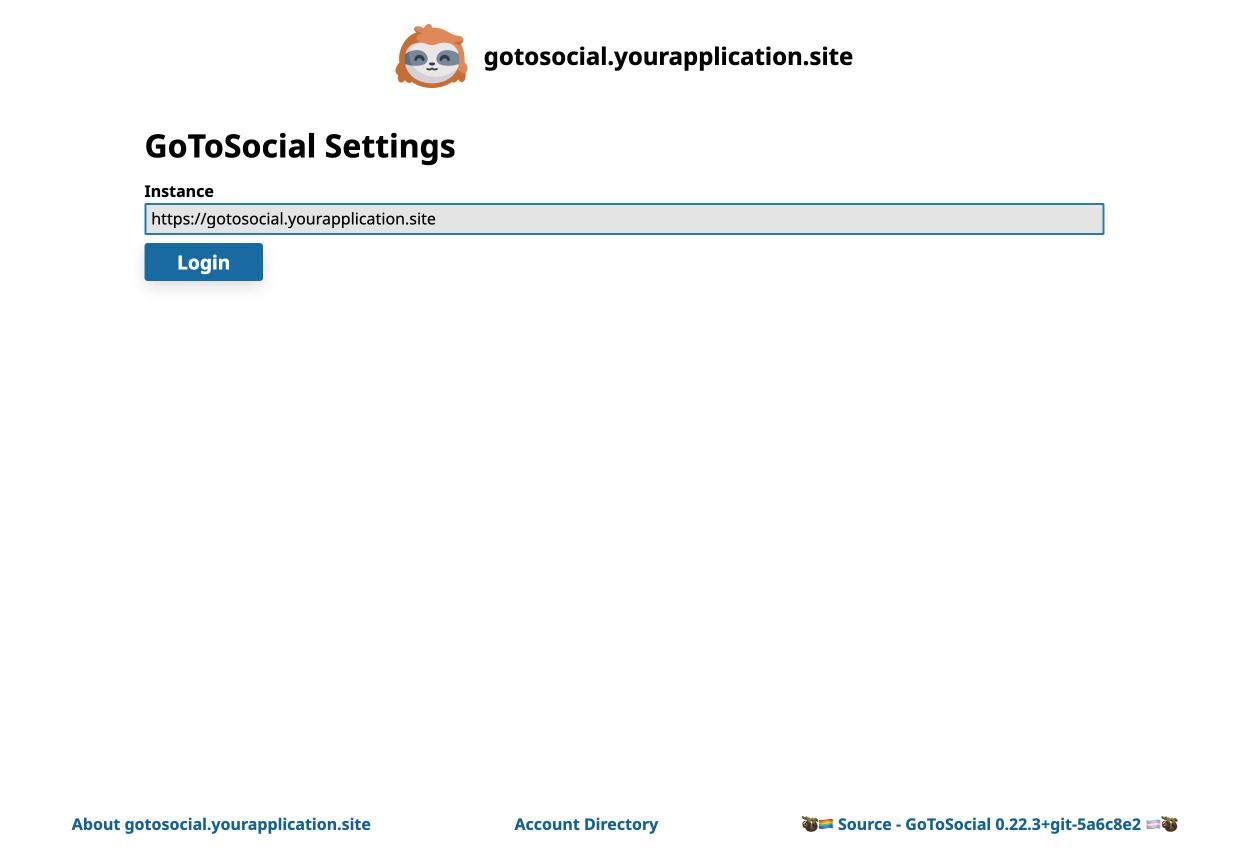
Click Login once. GoToSocial redirects the browser to Monosign.
On the Monosign sign-in page log in passwordless with your QR code (Monofor Identity), with a Passkey or with your user name and password (Sign in with Password). If you are already signed in to Monosign, the page is skipped.
After the sign-in Monosign redirects the browser back to GoToSocial (
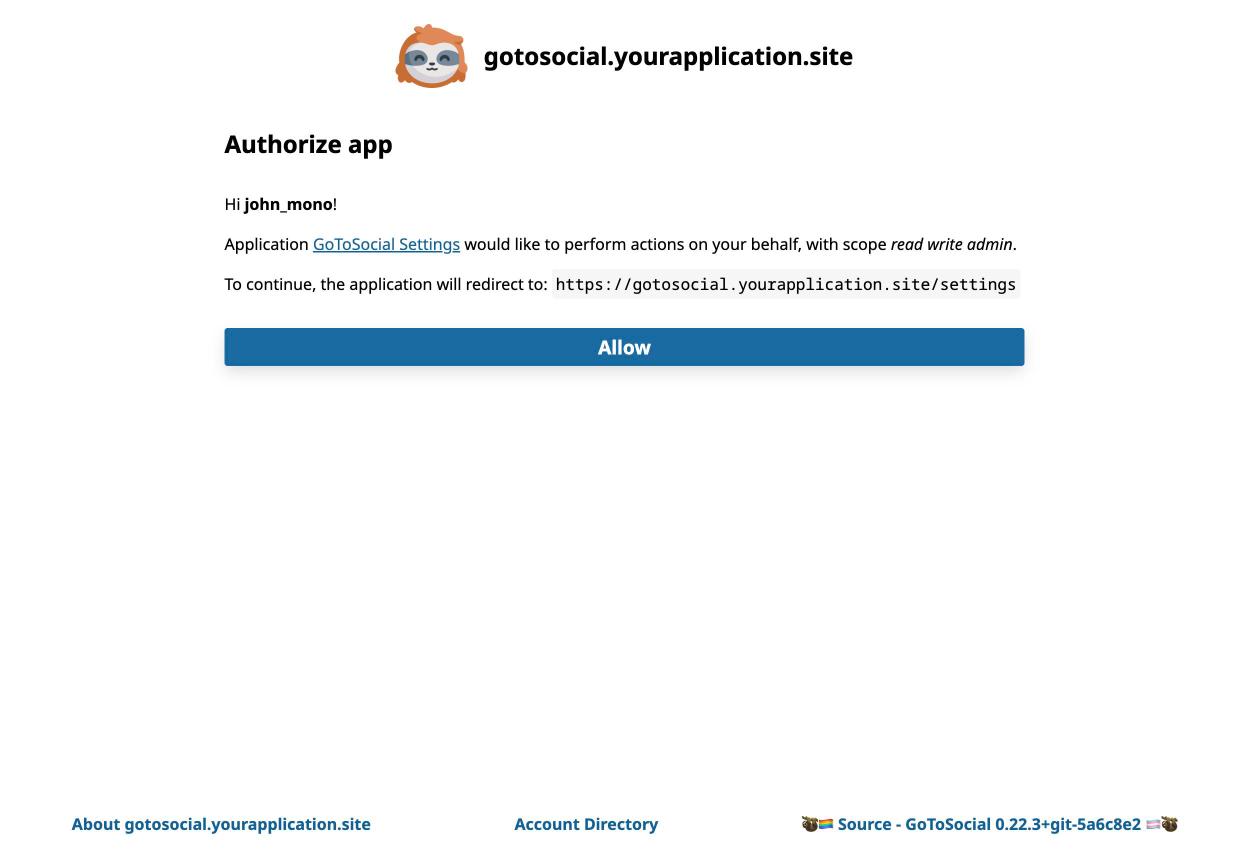
/auth/callback). GoToSocial shows the Authorize app page with the name of the signed-in user. Click Allow.
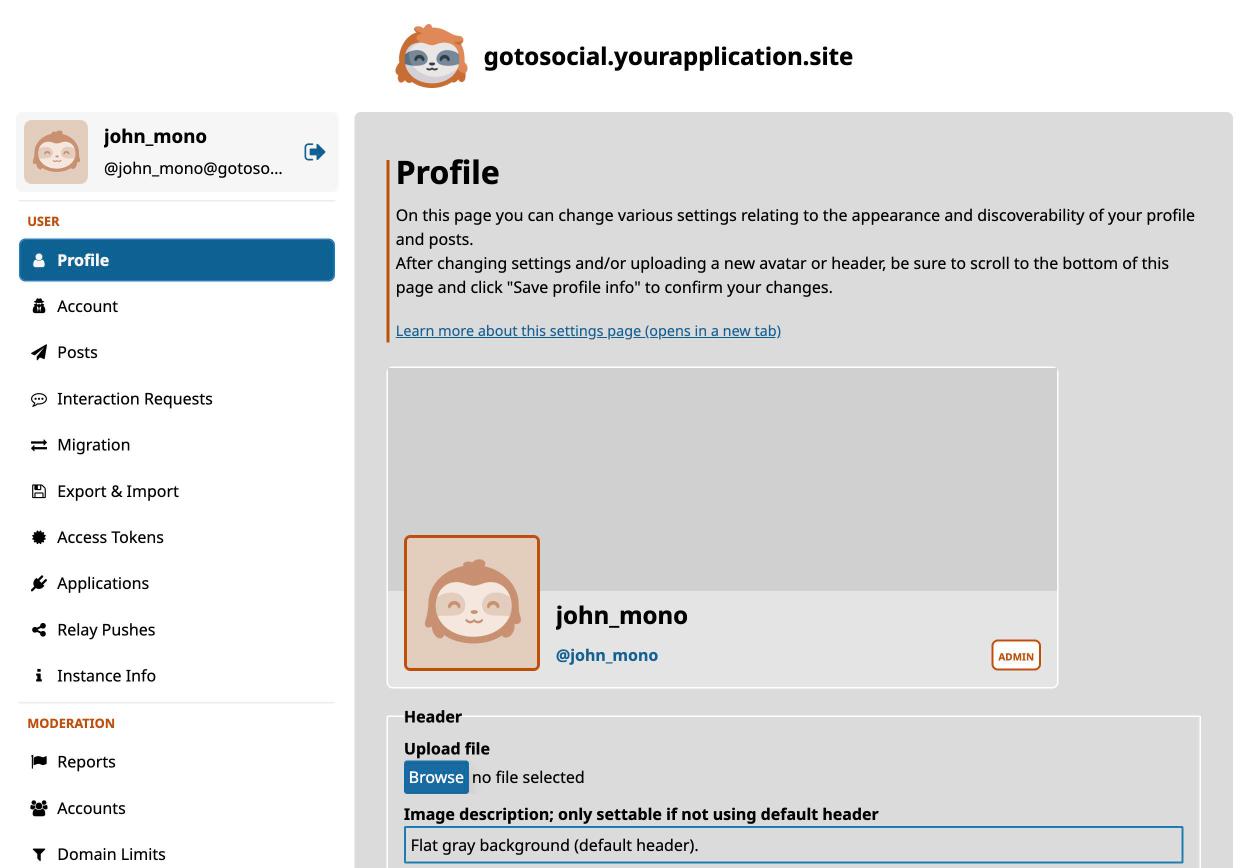
The user is signed in to the GoToSocial settings. The administrator account created in step 4 is marked as ADMIN.
A user who has no GoToSocial account yet is asked for a user name at the first sign-in; the field is pre-filled with preferred_username from Monosign. GoToSocial user names can only contain letters, numbers and underscores and cannot be changed later, so a Monosign name with a dot (for example john.mono) has to be adjusted (for example john_mono).
Troubleshooting
Symptom | Cause | Solution |
|---|---|---|
GoToSocial does not start or shows an OIDC error in the log | The issuer is wrong or GoToSocial cannot read the discovery document of Monosign. | Enter the issuer with the slash at the end and check that |
Monosign shows a redirect URI error | The callback address does not exactly match the Allowed Redirect URIs, for example because it starts with | Use |
An error appears after returning from Monosign | The Client Id or Client Secret is wrong, or the user has no e-mail address. | Copy the values again from the Monosign access key (step 1) and check that the user has an e-mail address in Monosign. |
The user is asked for a new account instead of using the existing one |
| Turn on |
The e-mail and password login disappeared | GoToSocial replaces the password login completely when OIDC is enabled. | This is expected. Keep the command line administrator commands available for recovery. |
A user cannot sign in | The user is not assigned to the application. | Assign the user in step 3. |
After completing the configuration on GoToSocial and Monosign, it is better to test in a new private browser window if the OIDC SSO doesn’t work, because old session cookies may cause errors.