This document explains how to implement Monosign with Metabase, the open-source business intelligence and analytics application. It covers Single Sign-On using OpenID Connect (OIDC), where Monosign acts as the Identity Provider (OpenID Provider) and Metabase as the Relying Party. Metabase reads the Monosign addresses from the OIDC discovery document and uses the Authorization Code flow, so the OIDC/OpenID access key of Monosign is used. Before you continue, it is better to read the Metabase OIDC documentation (opens in a new tab).
This configuration is done with Metabase Enterprise v1.64.3.2 (image metabase/metabase-enterprise:v1.64.3.2). The same OIDC settings apply to Metabase Cloud. If your Metabase version or deployment type is different, please check the Metabase documentation.
OIDC is configured in the Metabase admin interface (Admin → Settings → Authentication → OIDC) or with the MB_OIDC_PROVIDERS environment variable. Metabase matches and creates users by their e-mail address.
License. OIDC single sign-on in Metabase is an Enterprise / Pro feature (self-hosted and Metabase Cloud). The open-source edition has only Google and LDAP authentication. The enterprise Docker image runs with open-source features until a license token is activated, so a token is required for OIDC. A self-service trial token is available at store.metabase.com/checkout (opens in a new tab); activate it under Admin → Settings → License. On a self-hosted instance, MB_ENCRYPTION_SECRET_KEY must be set before enabling OIDC (Metabase Cloud handles this for you).
Monofor has no responsibility to do Metabase configurations. If you need support please contact Metabase or your Metabase support provider.
Instructions
This documentation contains 5 main steps for integration.
Creating an application on Monosign
Configuring the OIDC/OpenID settings on Monosign
Assign a user to the Metabase application
Configuration Single Sign-On for Metabase
Sign In Test
1- Creating an Application on Monosign
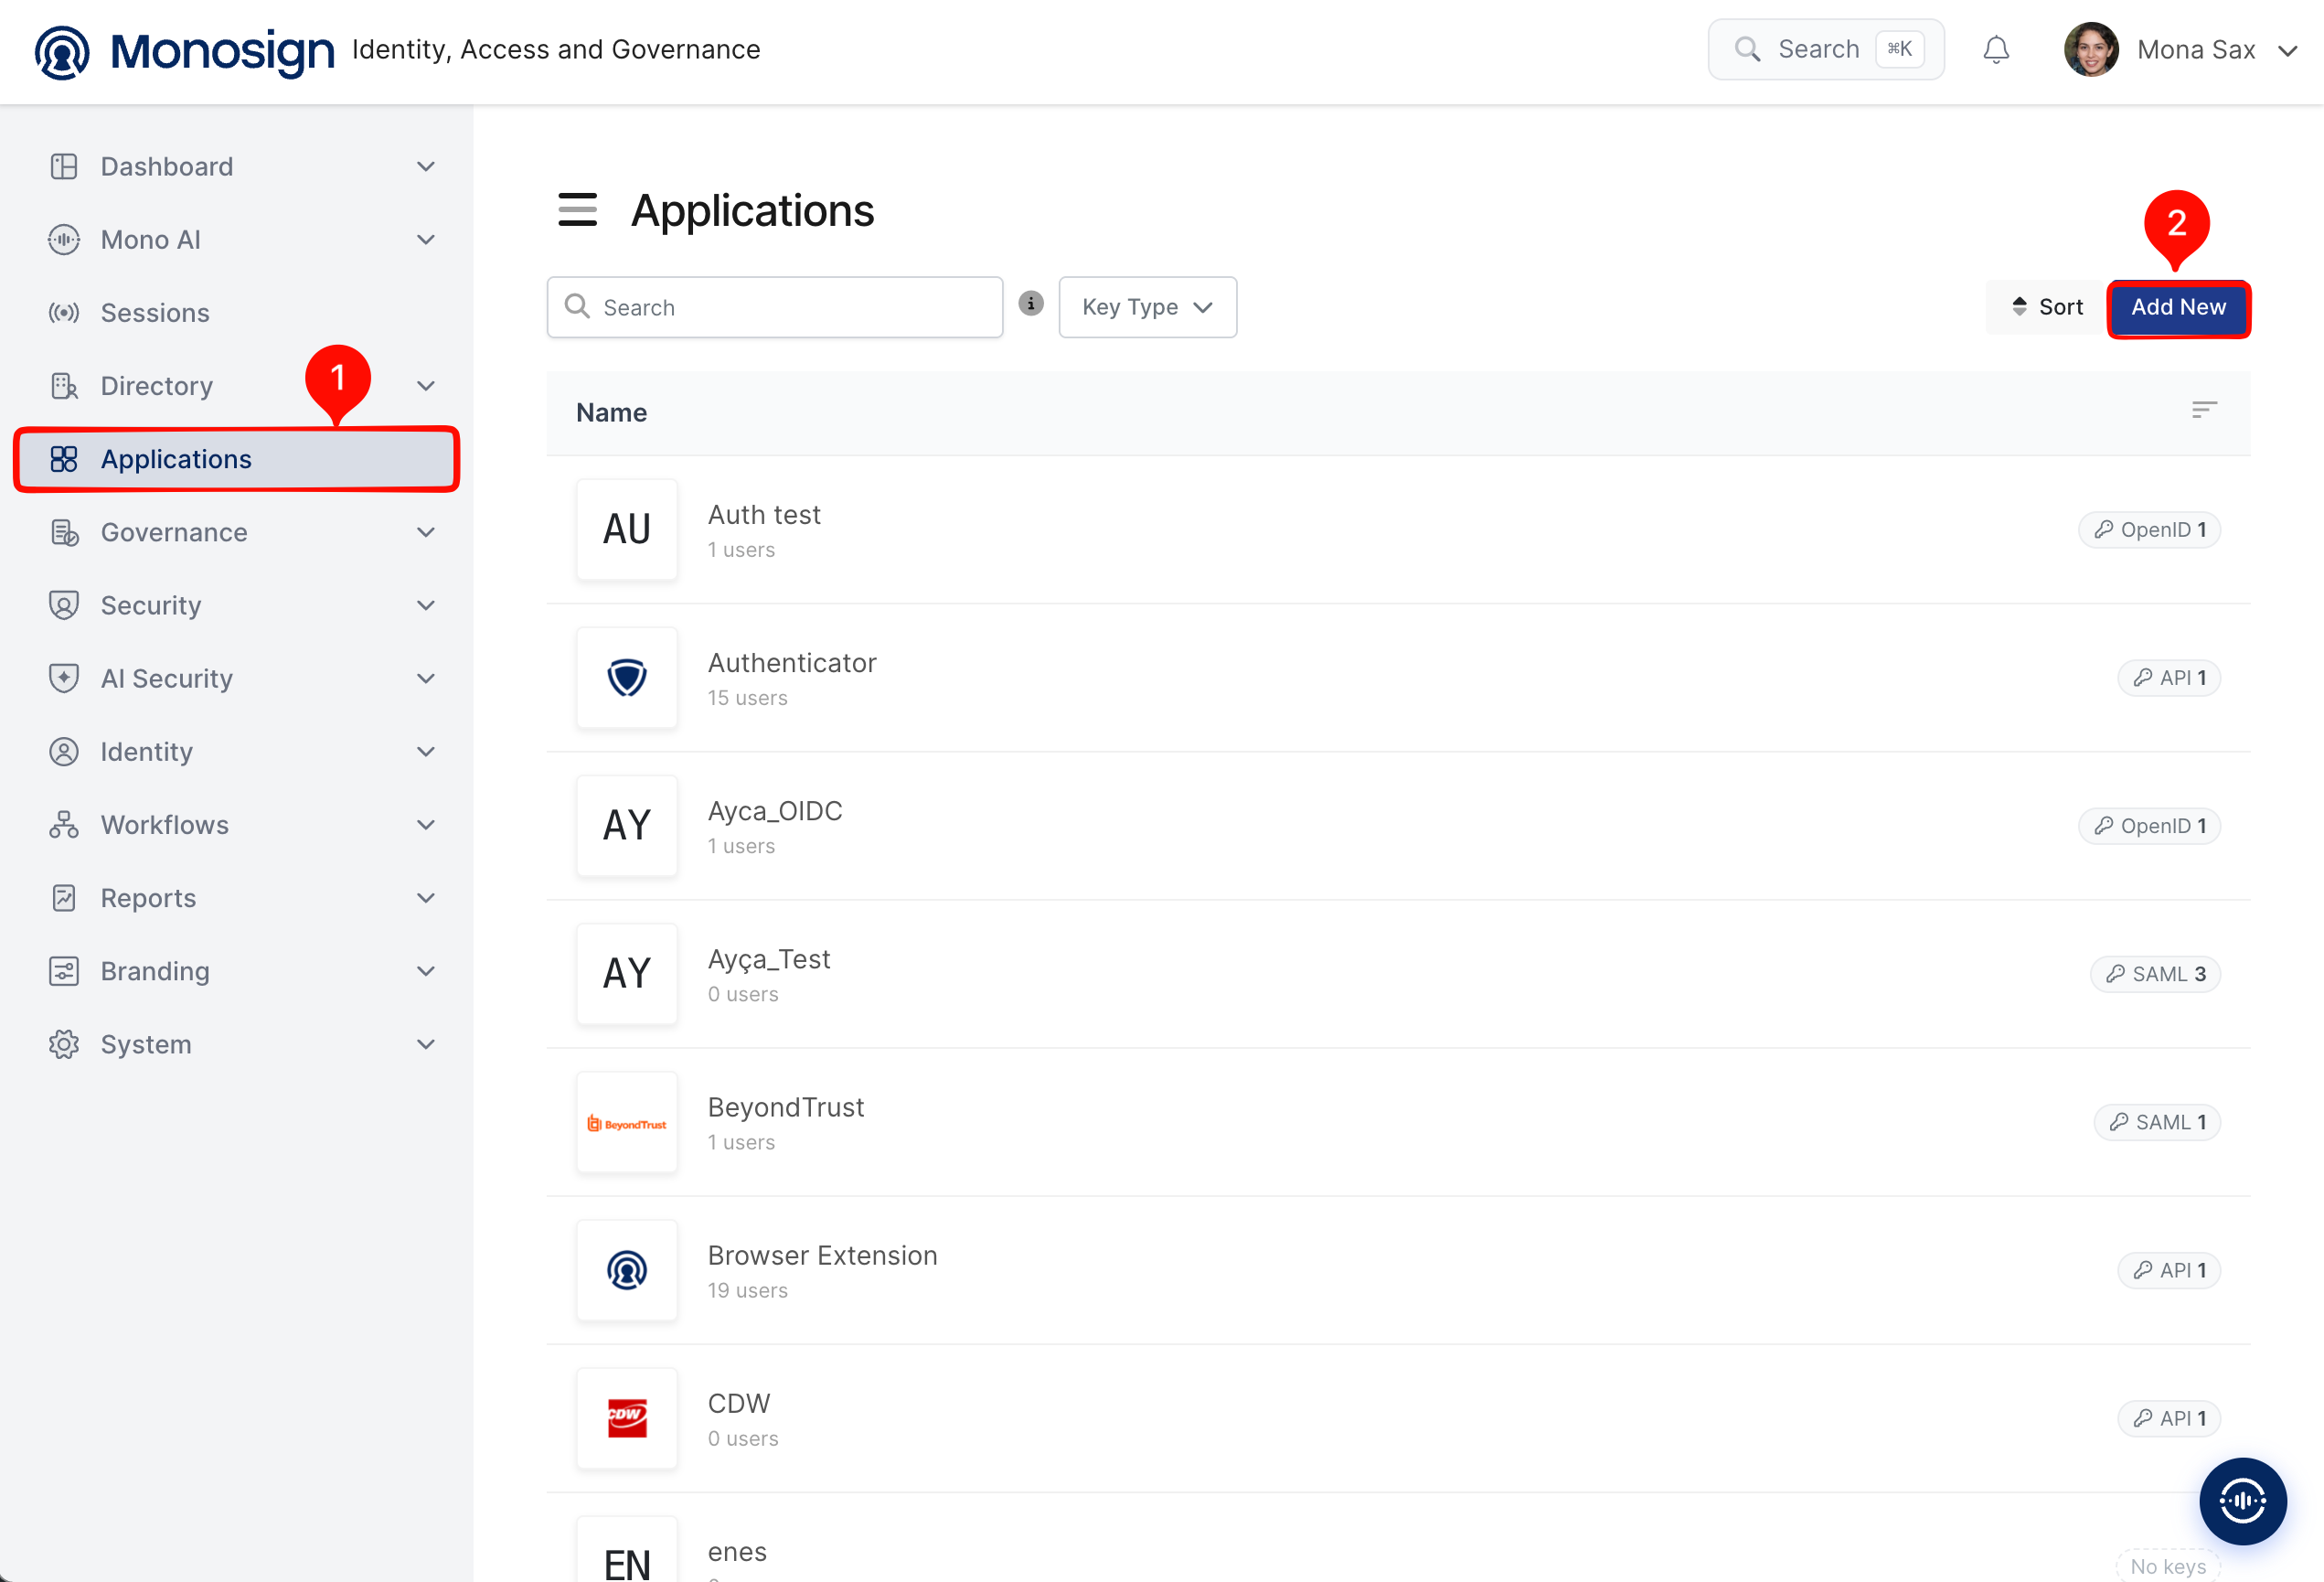
Create your application on Monosign first. Open the Applications page from the left menu and click Add New.
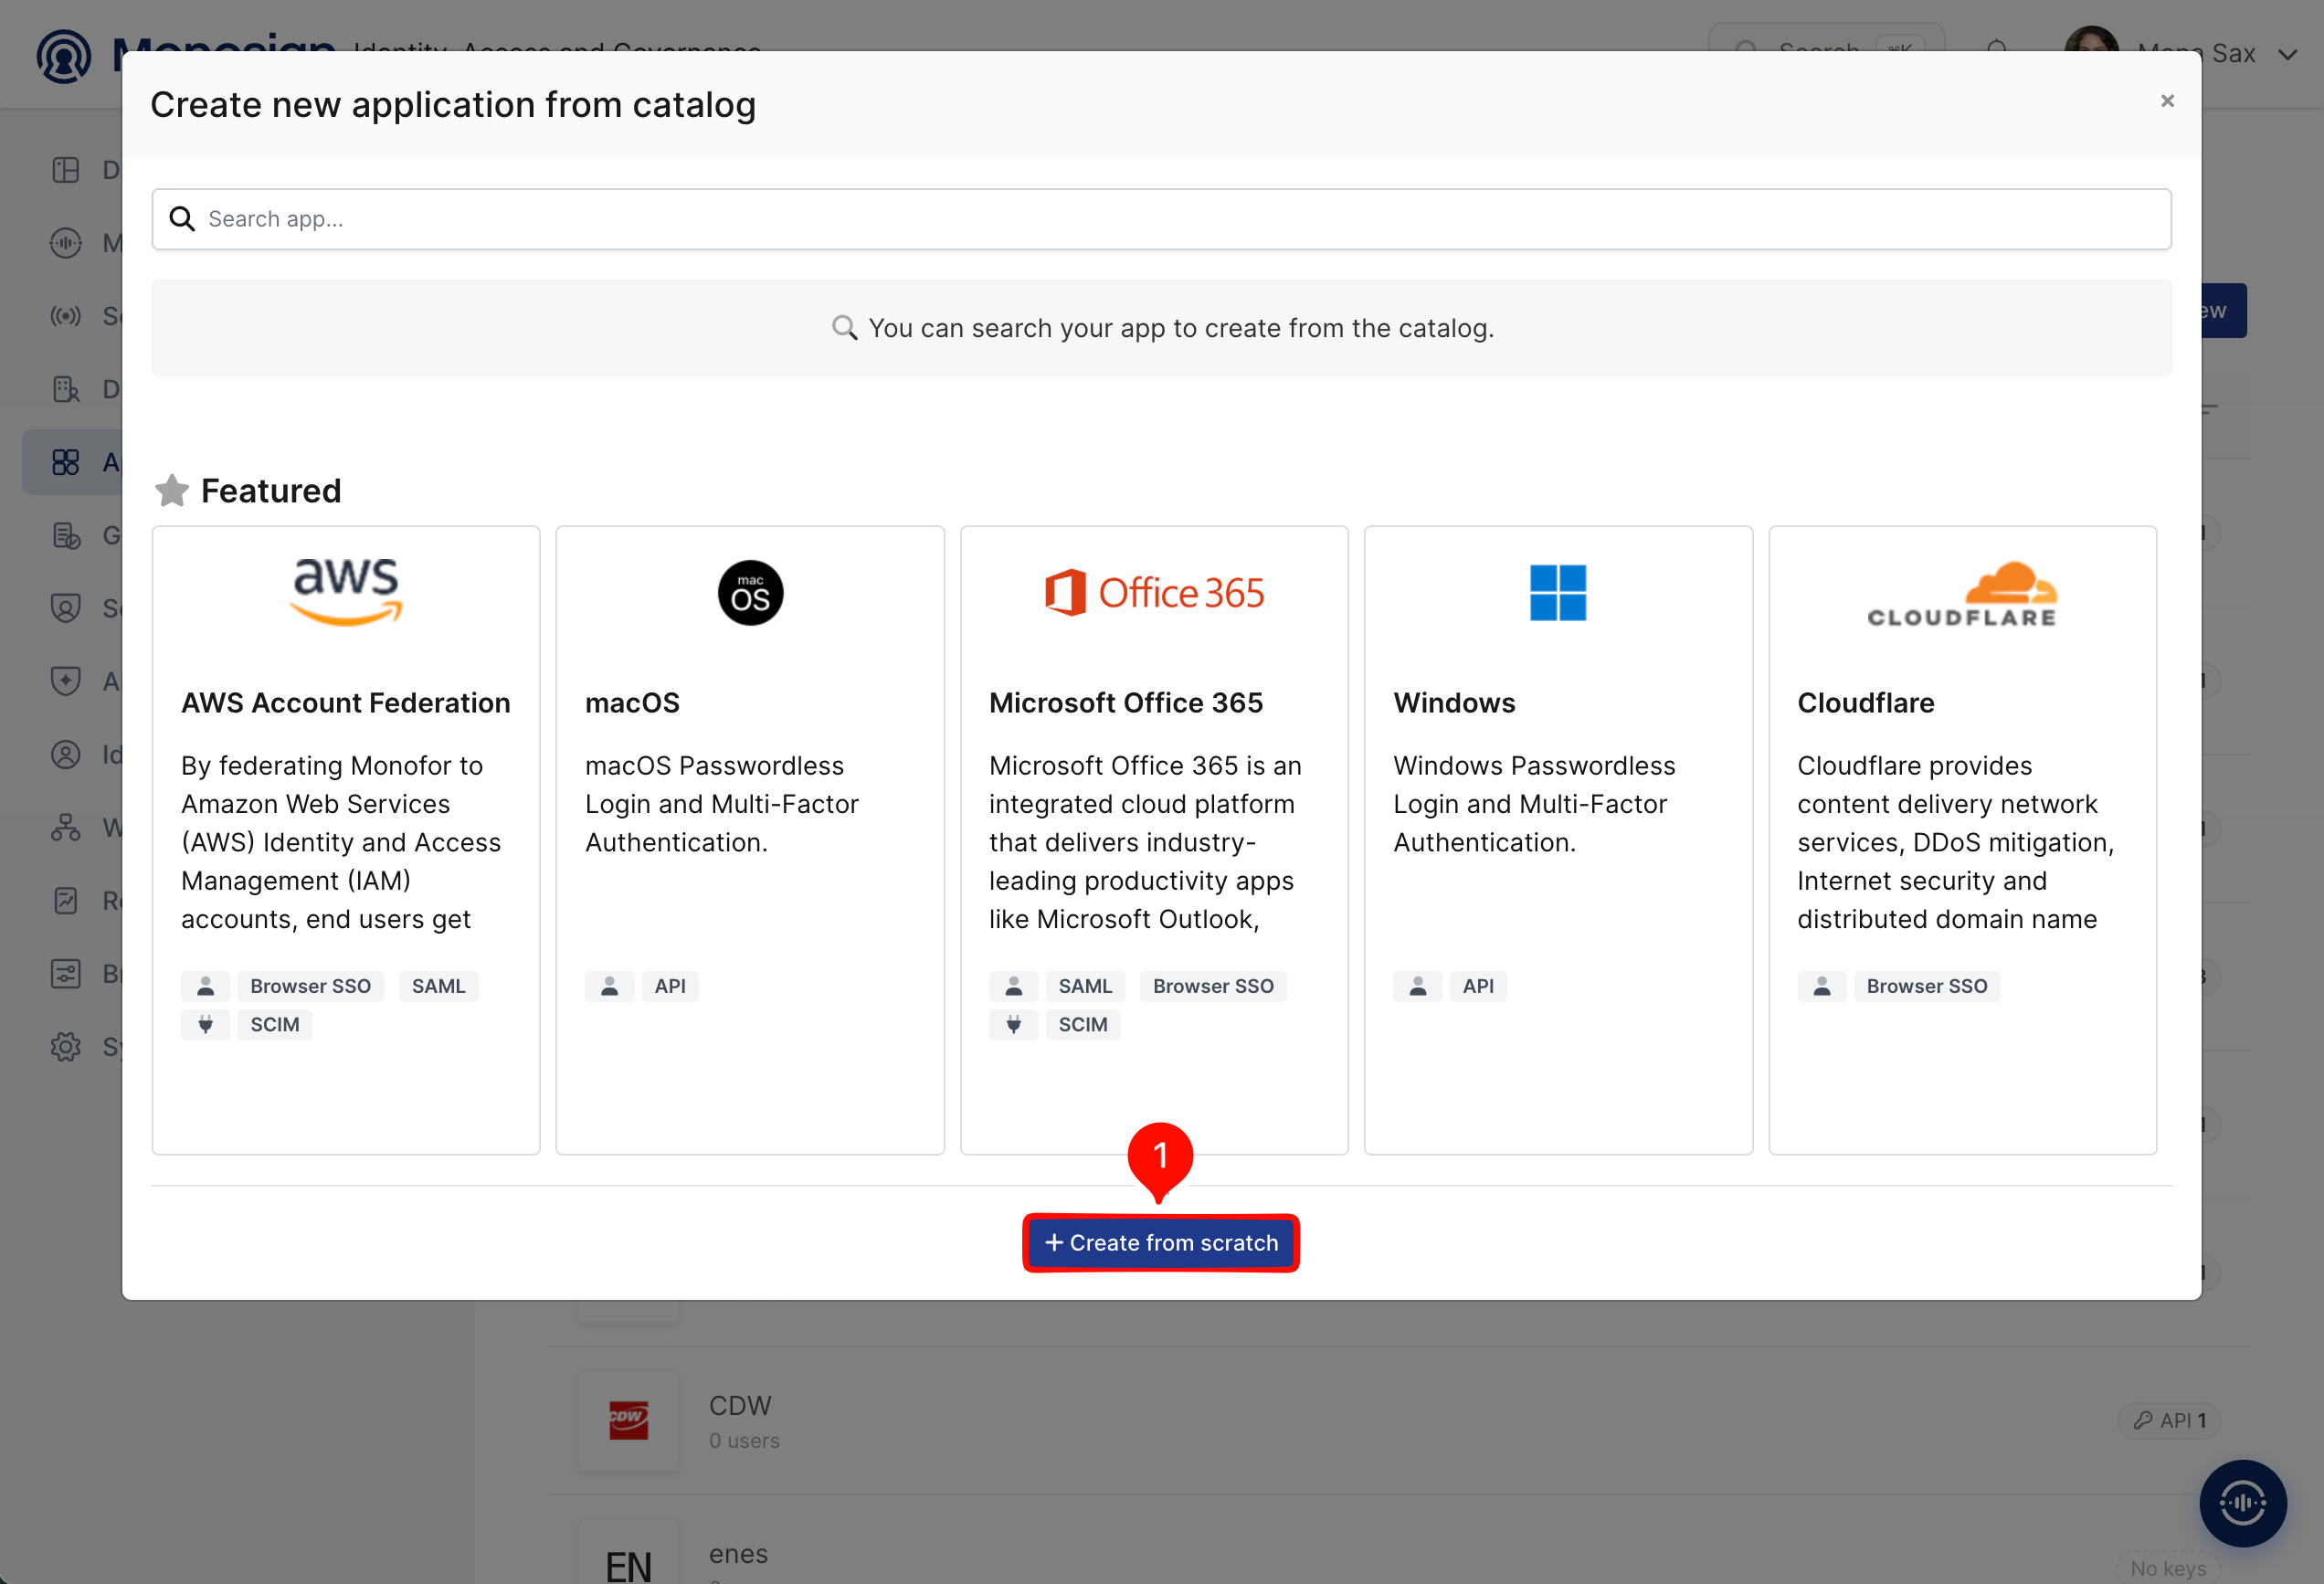
Metabase is not in the application catalog, so click Create from scratch.
Fill in the application details on the Application tab and click Next.
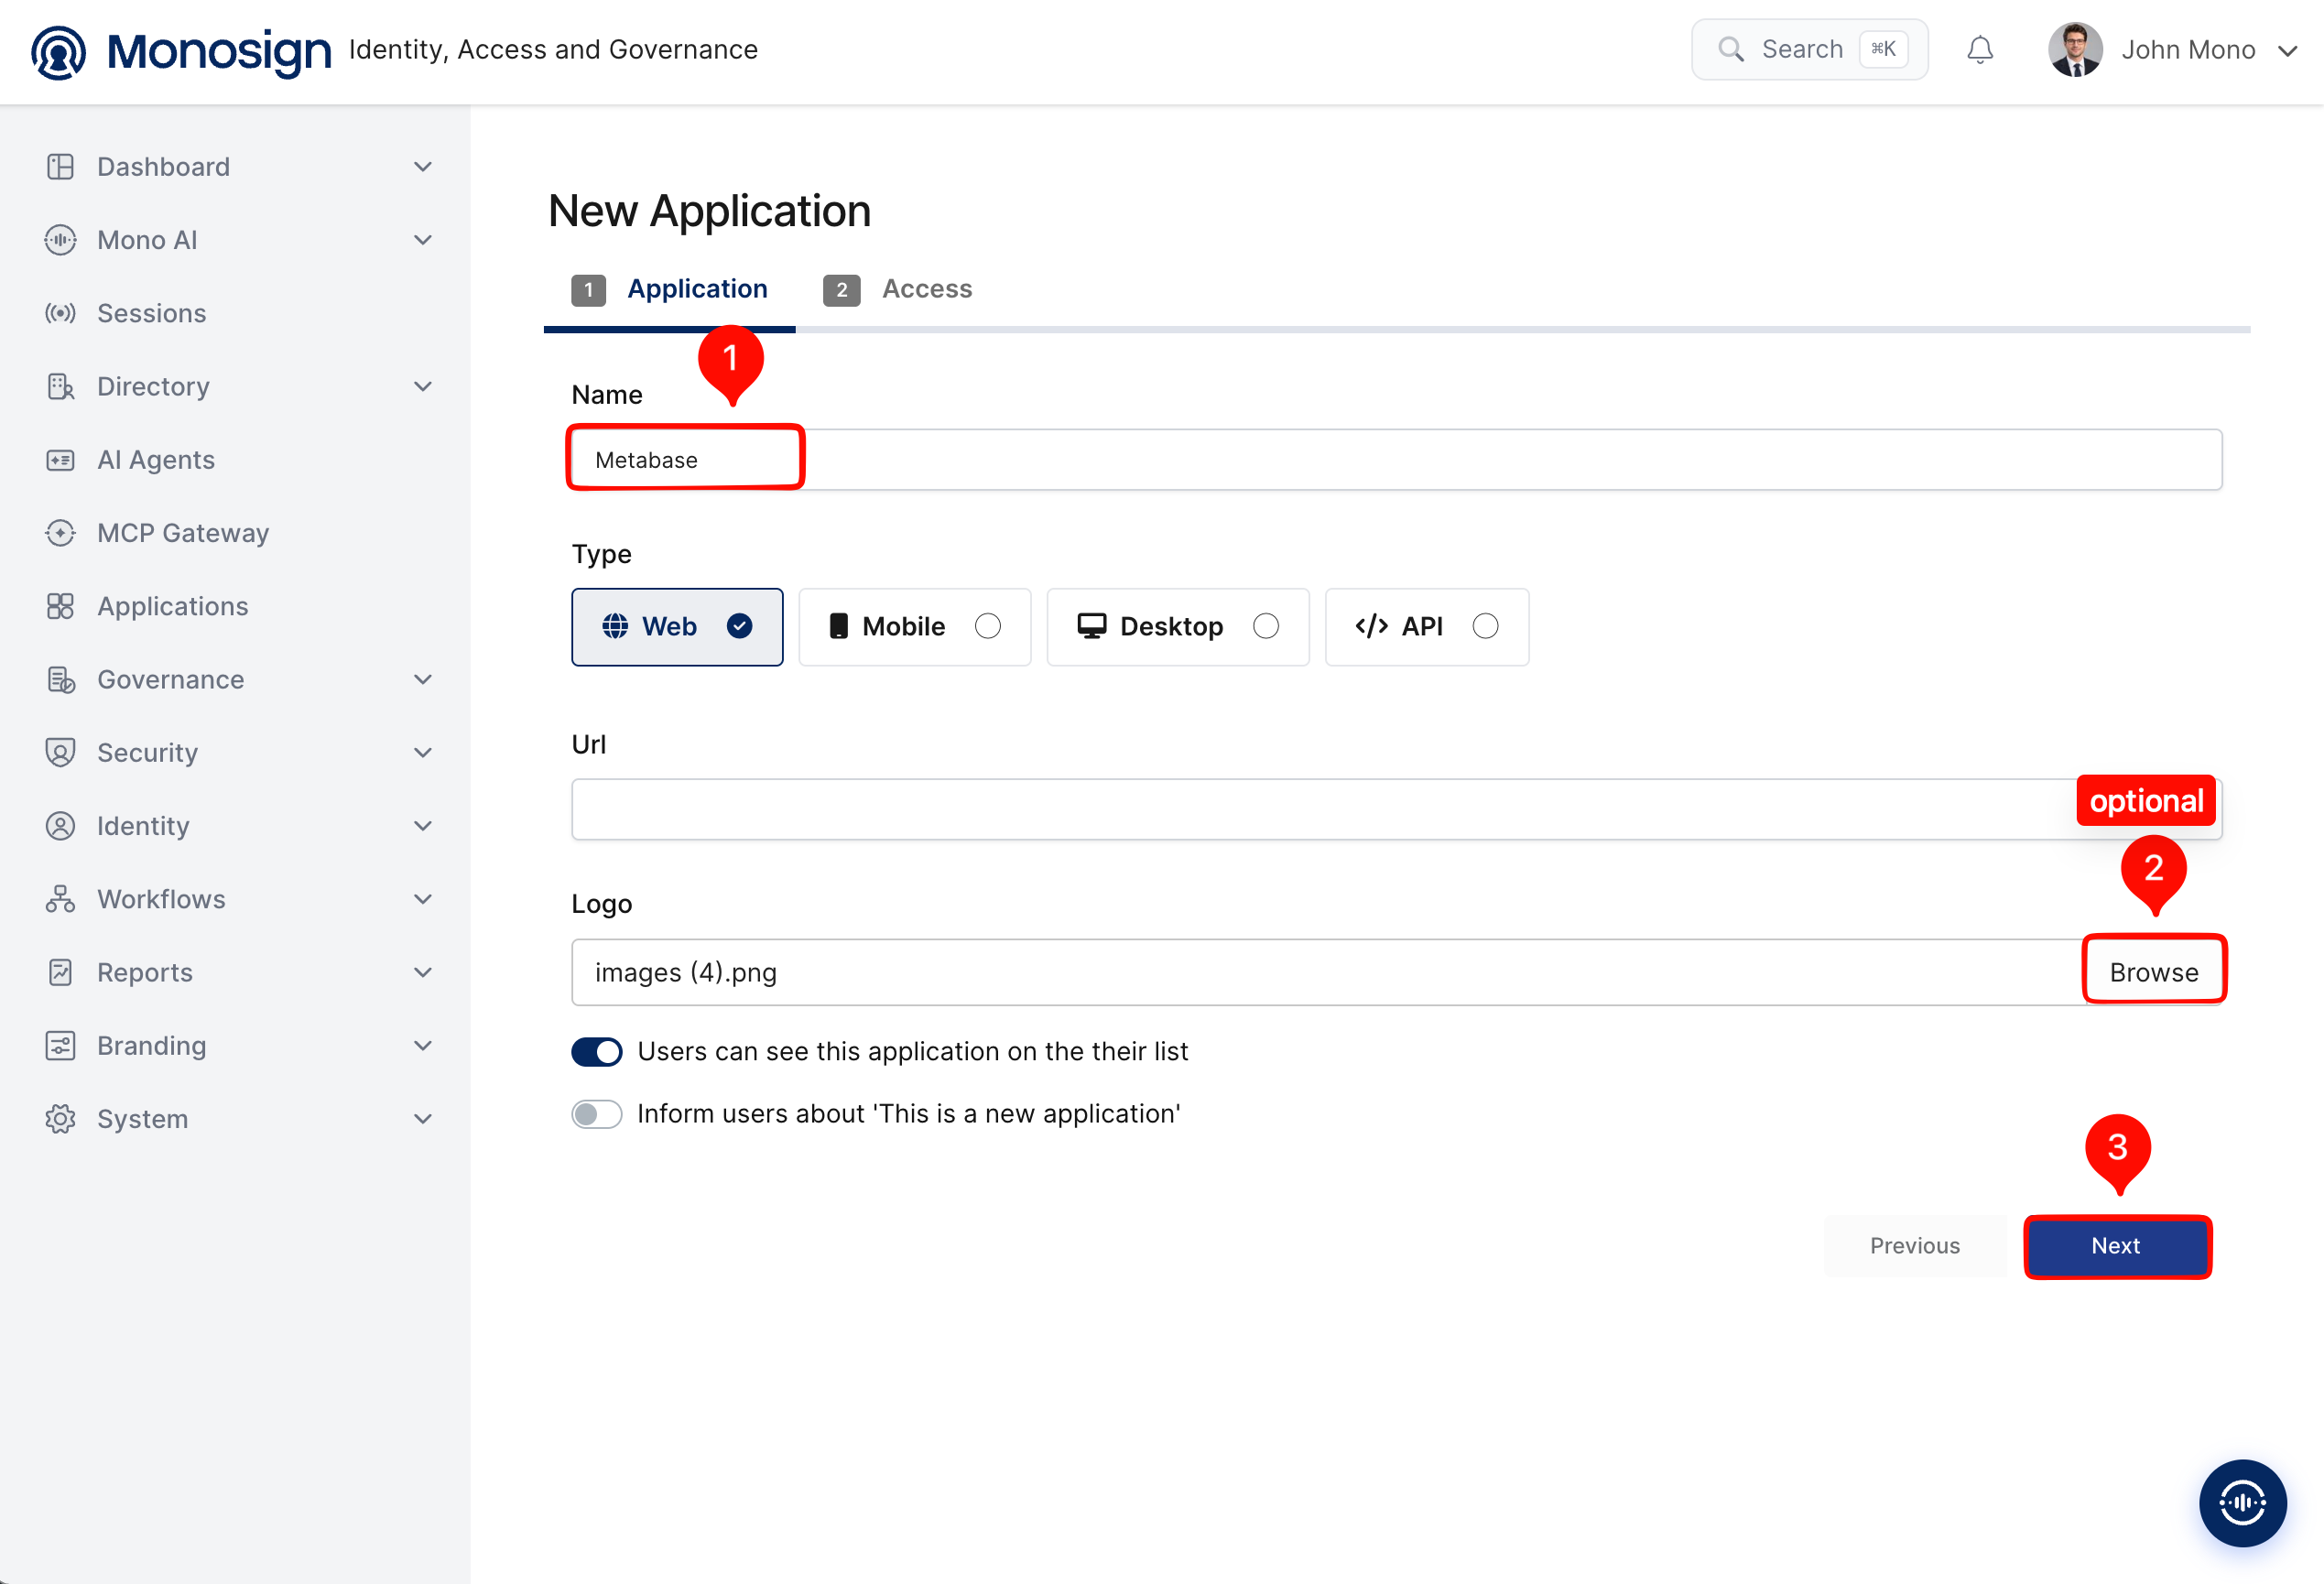
Property | Value | Description |
|---|---|---|
Name |
| Name of the application shown to users on the Monosign portal and on the Monosign sign-in page. |
Type |
| Metabase is accessed through a web browser. Options: Web, Mobile, Desktop, API. |
Url | Optional | Leave empty or enter the Metabase address (for example |
Logo | Optional | Browse and upload a logo; it is also shown on the Monosign sign-in page. |
Users can see this application on their list |
| Displays the application on the user portal. |
On the Access tab define who can reach the application and click Create Application.
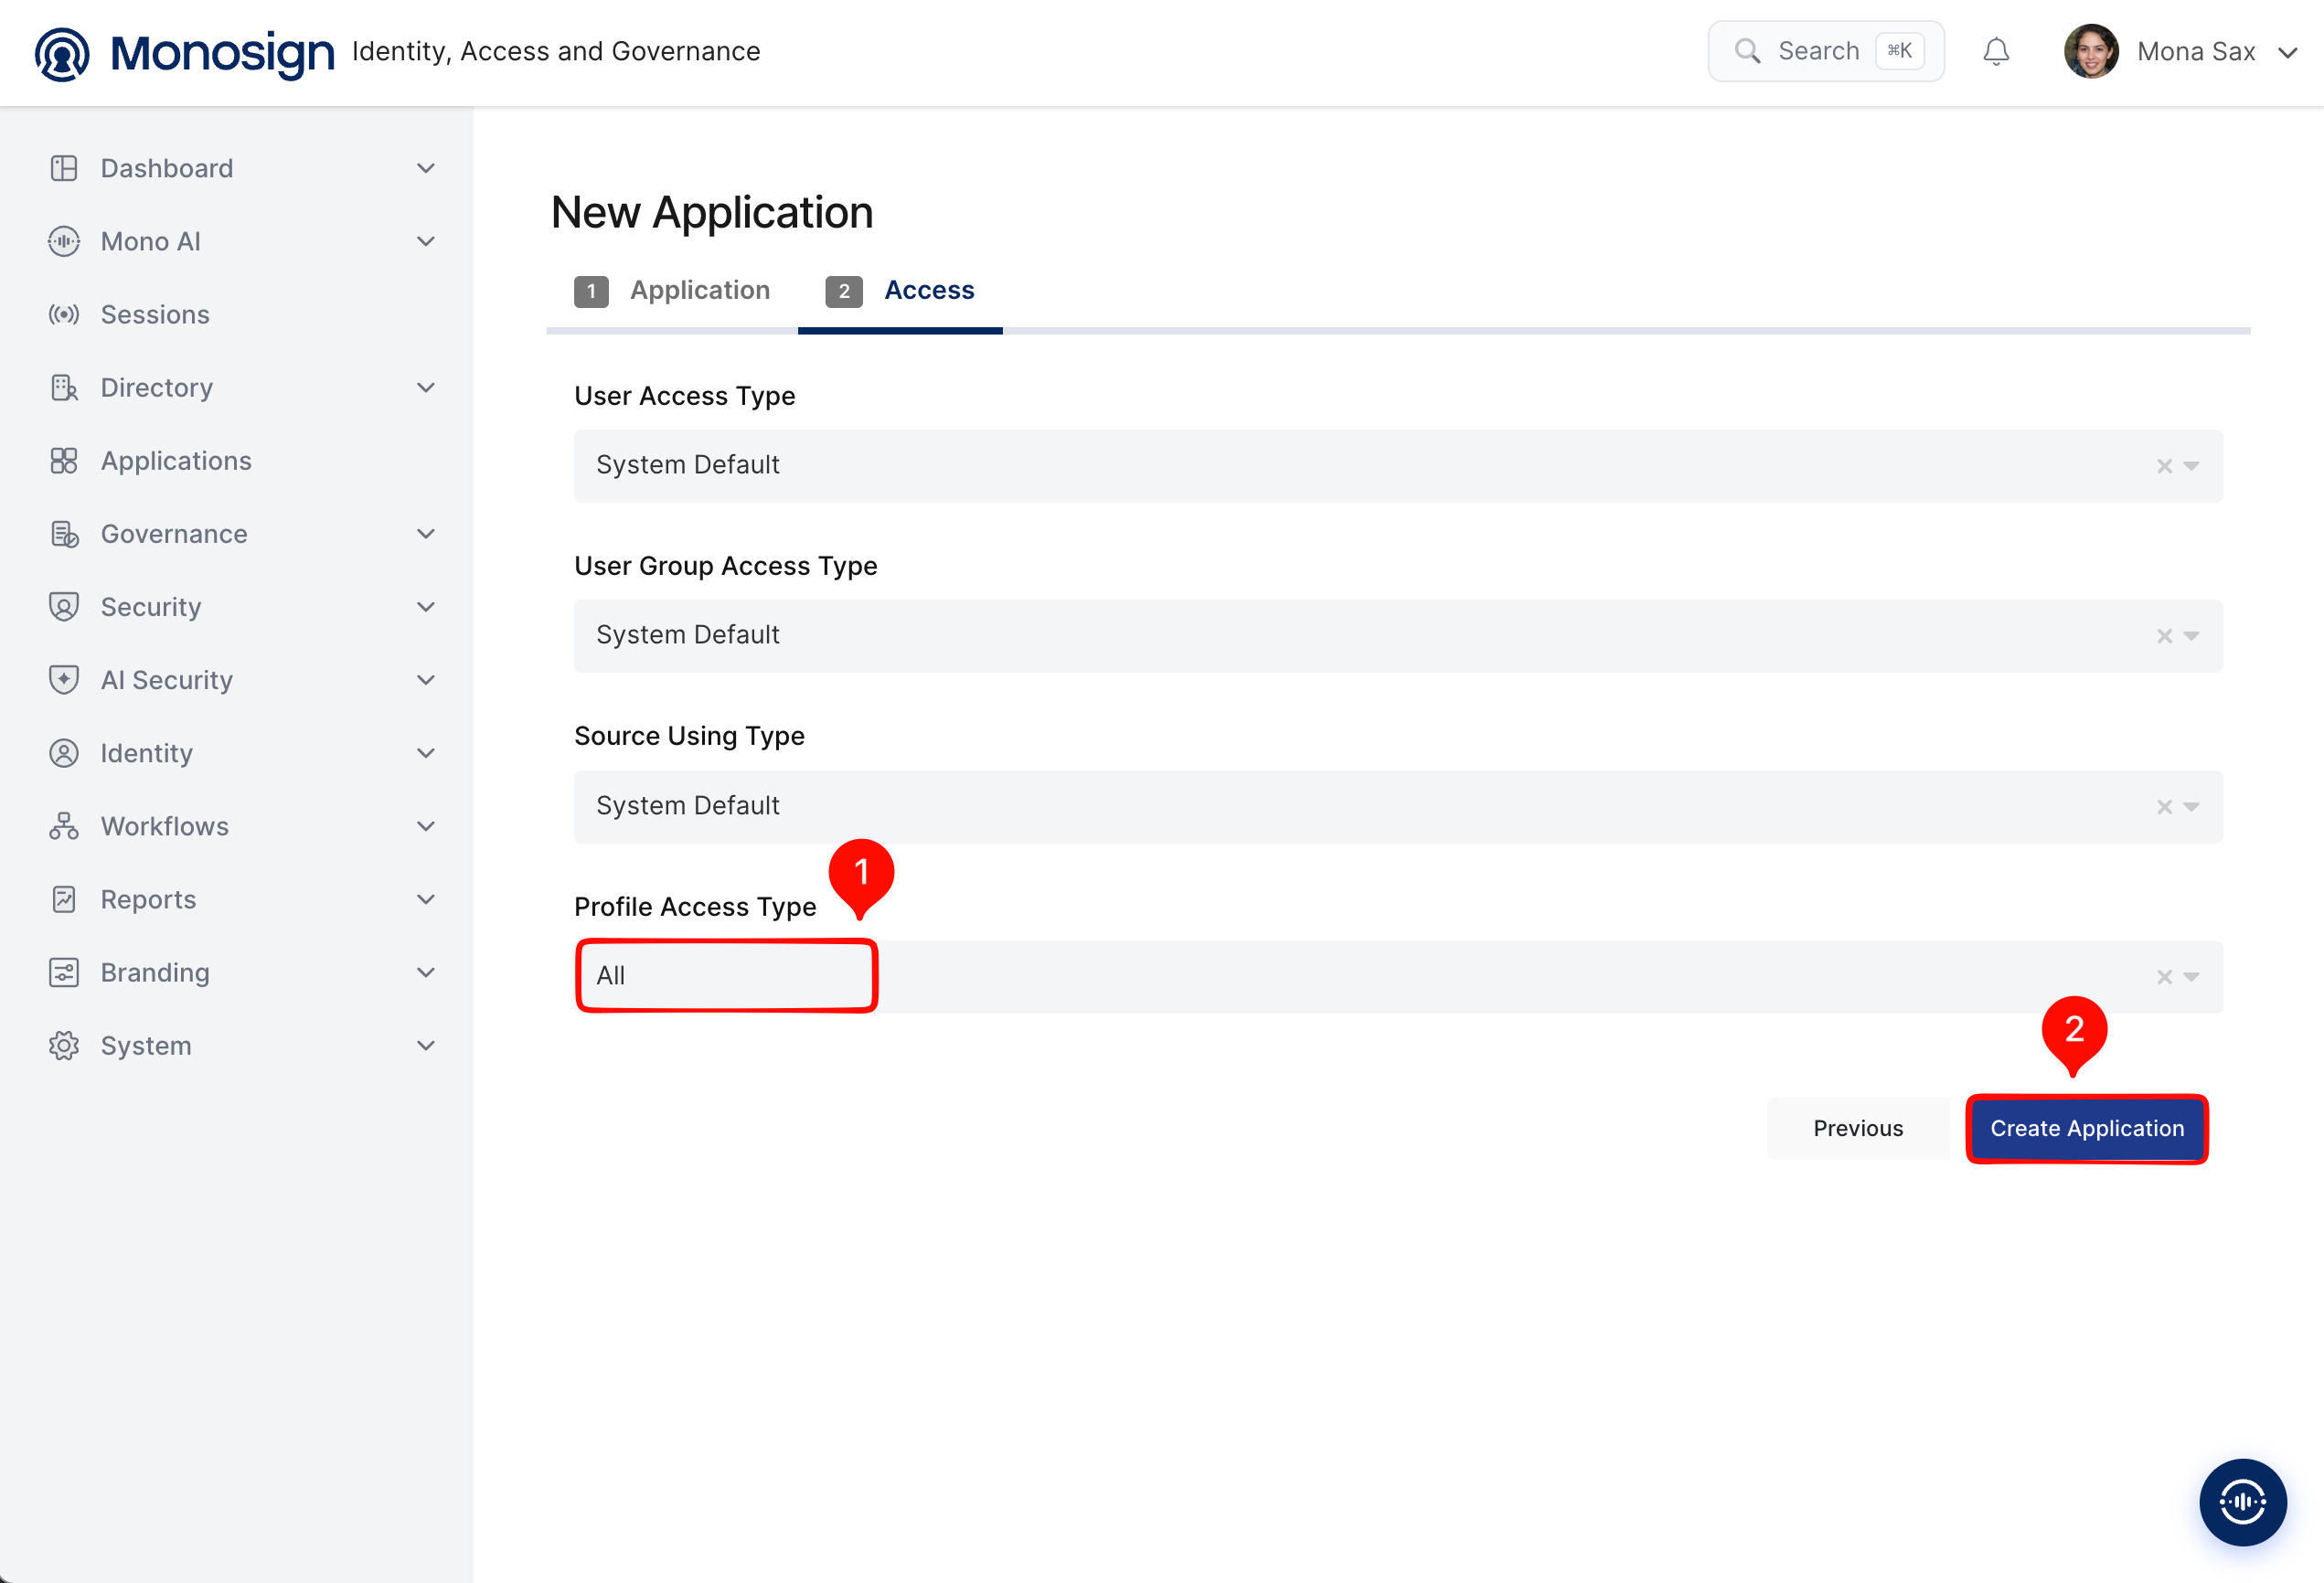
Property | Value | Description |
|---|---|---|
User Access Type |
| Defines which users can access this application. Options: Only Assigned Users, All Users, System Default. Metabase creates an account for every user who signs in, so give access only to the users you assign in step 3. |
User Group Access Type |
| Defines the application’s user group access. |
Source Using Type |
| Defines which user sources the application can use. |
Profile Access Type |
| Defines which user profile attributes are available to the application (Options: Restricted, All). Metabase needs the e-mail address, first name and last name of the user, so the profile must be accessible. |
Metabase creates an account for every Monosign user who signs in for the first time (just-in-time provisioning). Make sure the User Access Type is Only Assigned Users and give access only to the users you assign in step 3.
After the application is created, click Keys and add a new Access Key for OIDC/OpenID access.
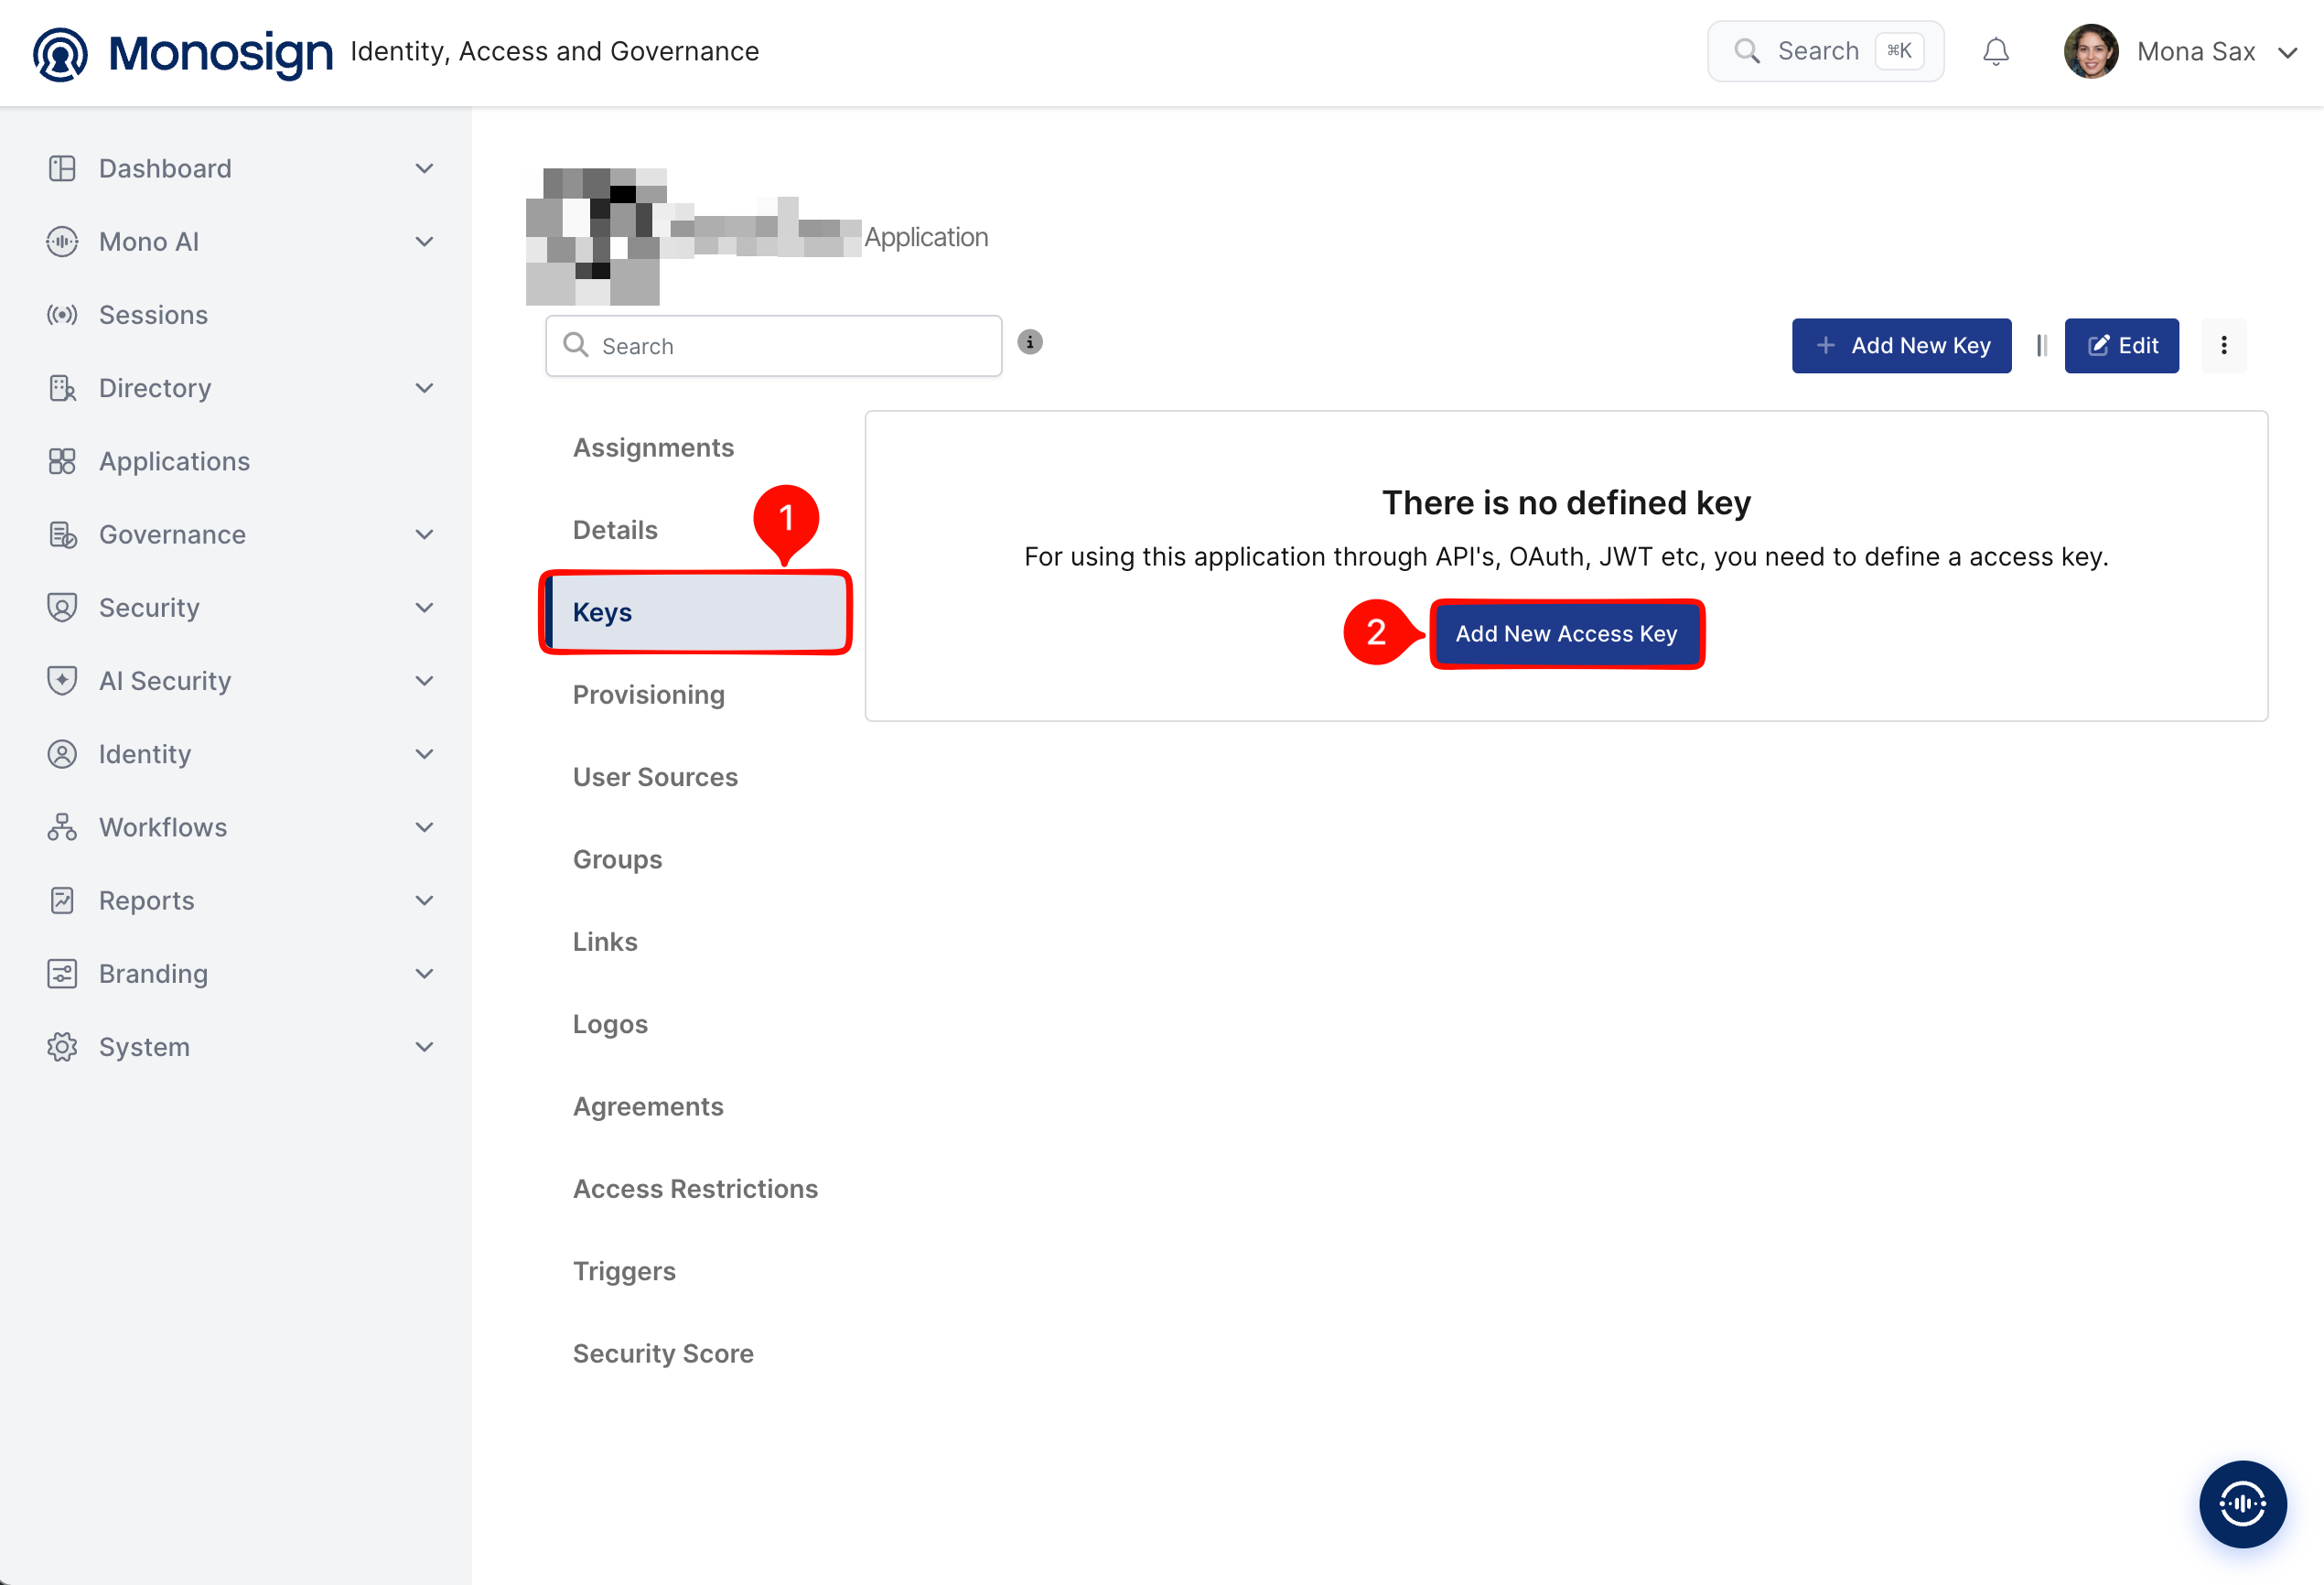
Select OIDC/OpenID as the key type and click Create. Monosign generates the Client Id and Client Secret automatically.
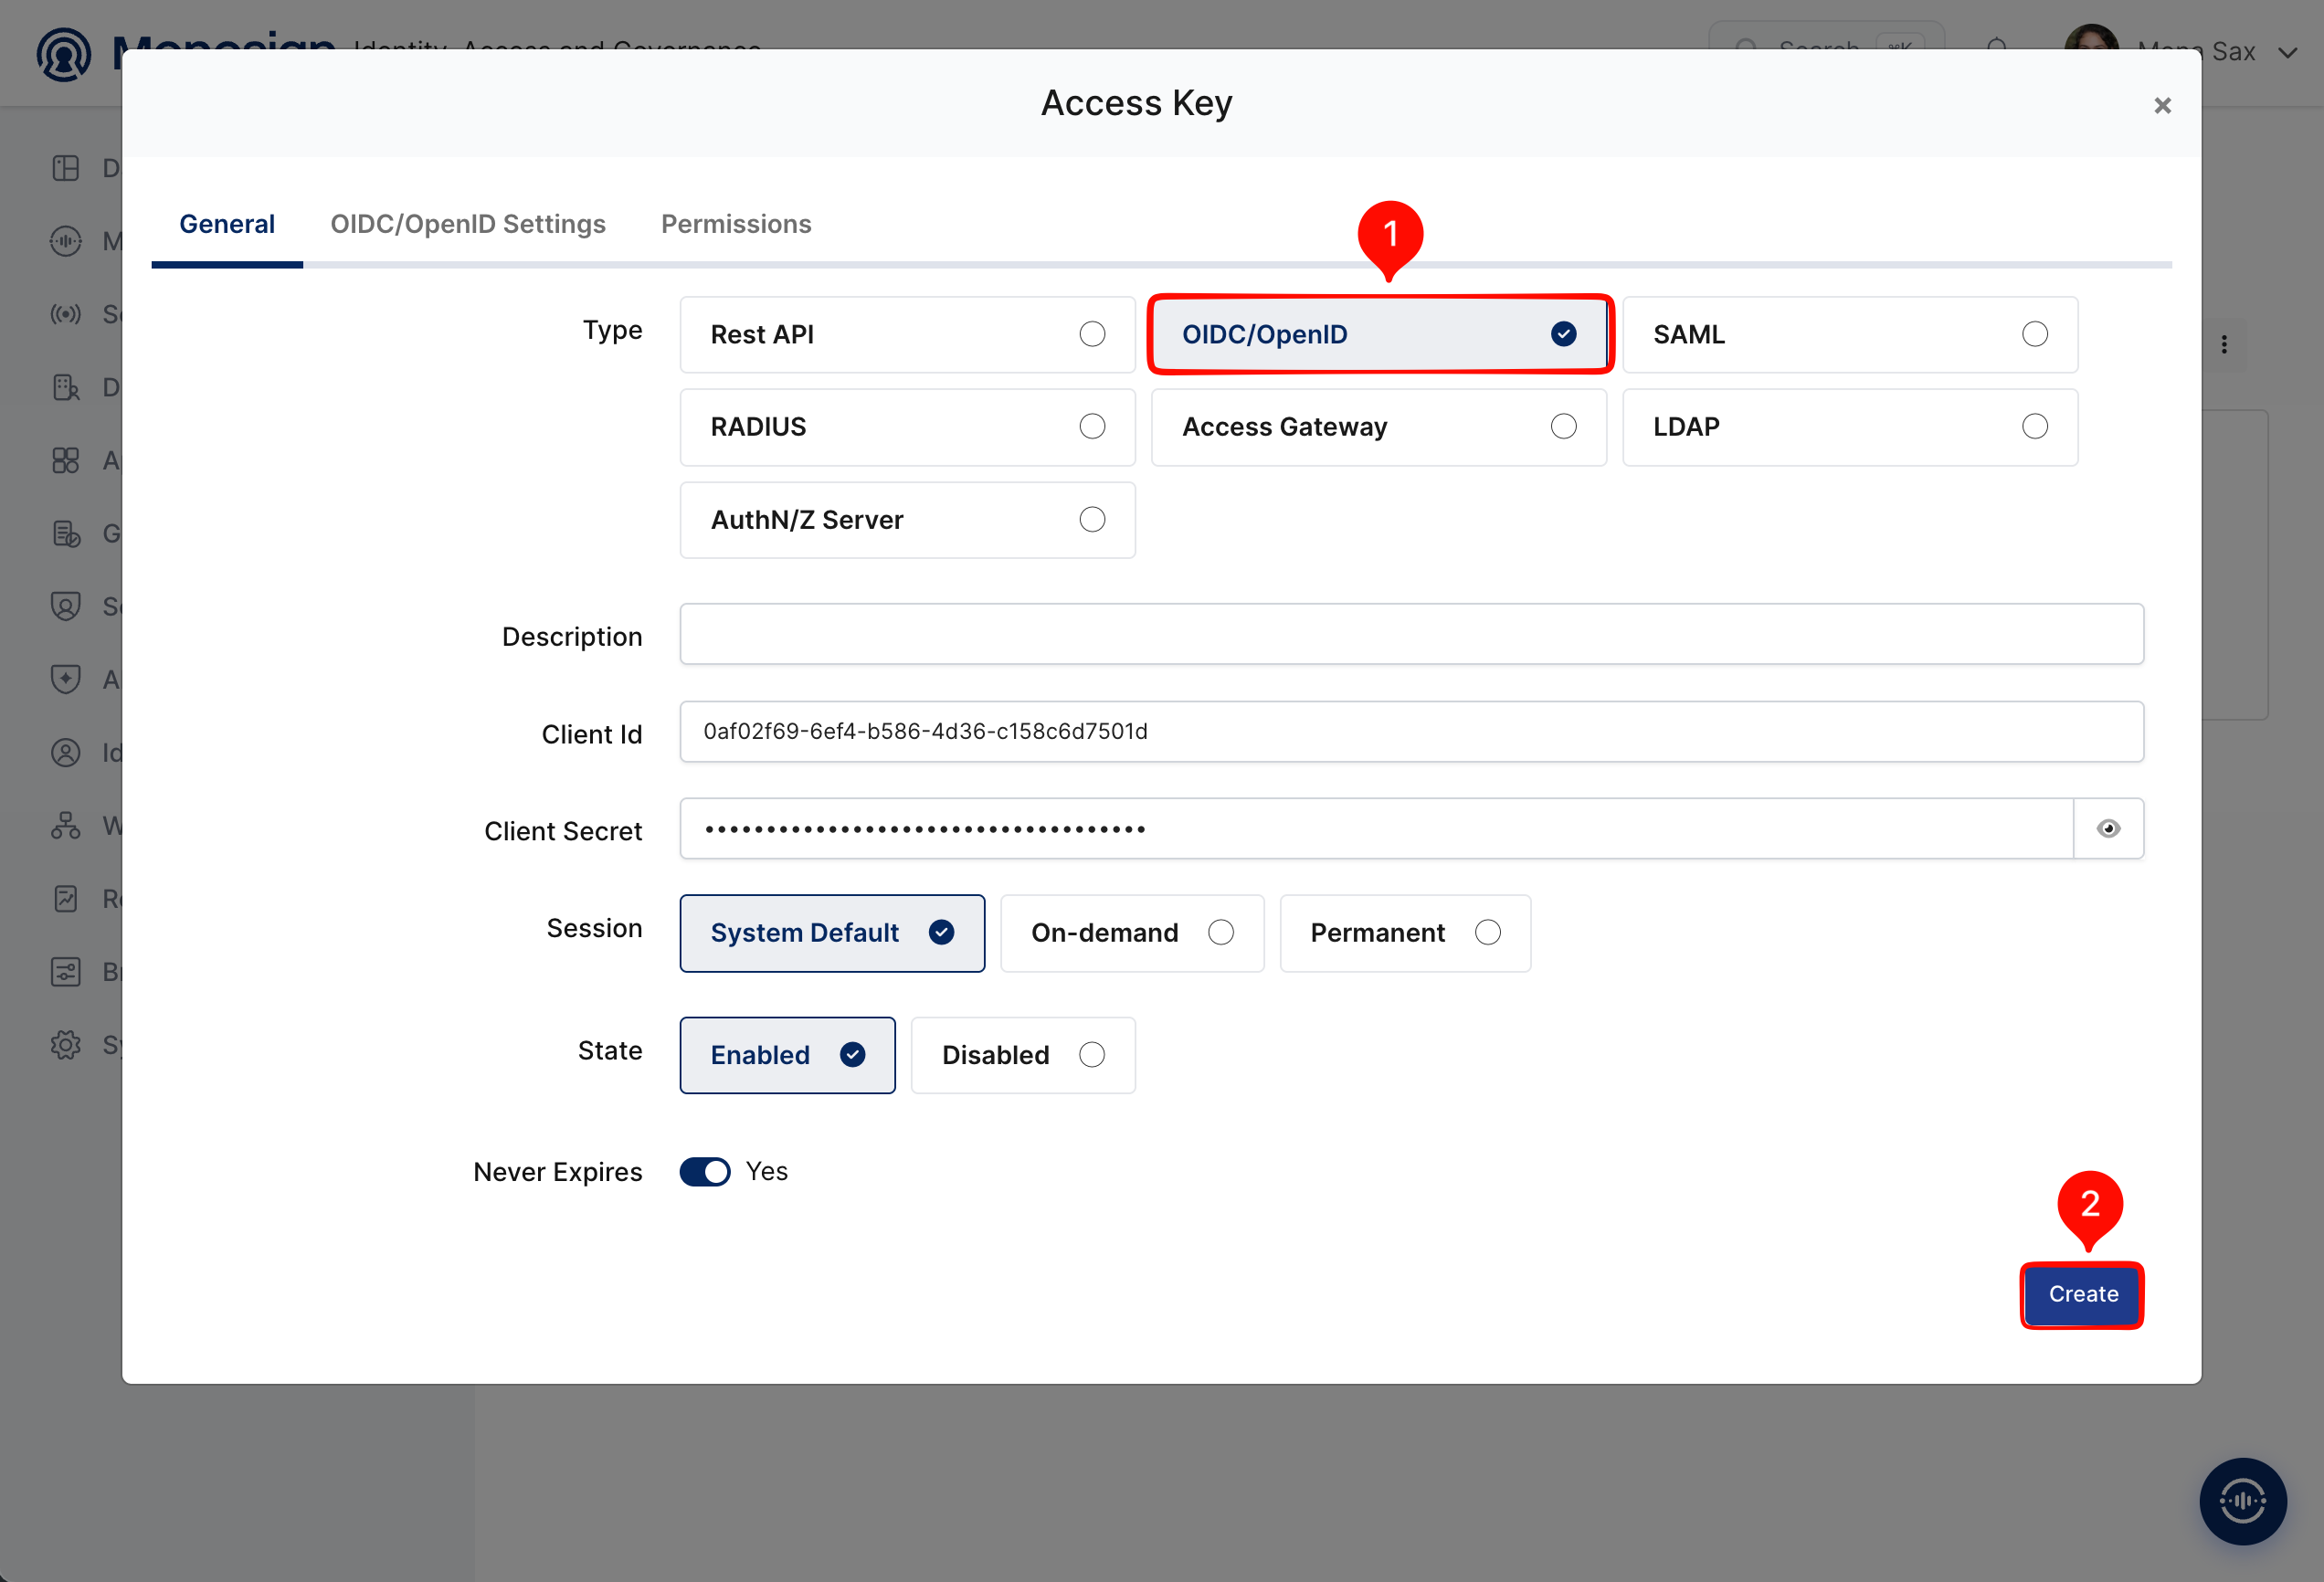
Property | Value | Options |
|---|---|---|
Type |
| Rest API, OAuth 2.0, JWT, OIDC/OpenID, SAML, RADIUS, Access Gateway, LDAP, AuthN/Z Server |
Client Id / Client Secret | Generated automatically | Use the eye icon next to the secret to reveal it. Both values are required in step 4. |
Session |
| System Default, On-demand, Permanent |
State |
| Enabled, Disabled |
Never Expires |
| Turn off to define a specific expiration date for the key. |
The key page shows the Monosign values that are needed in the Metabase OIDC configuration (step 4):
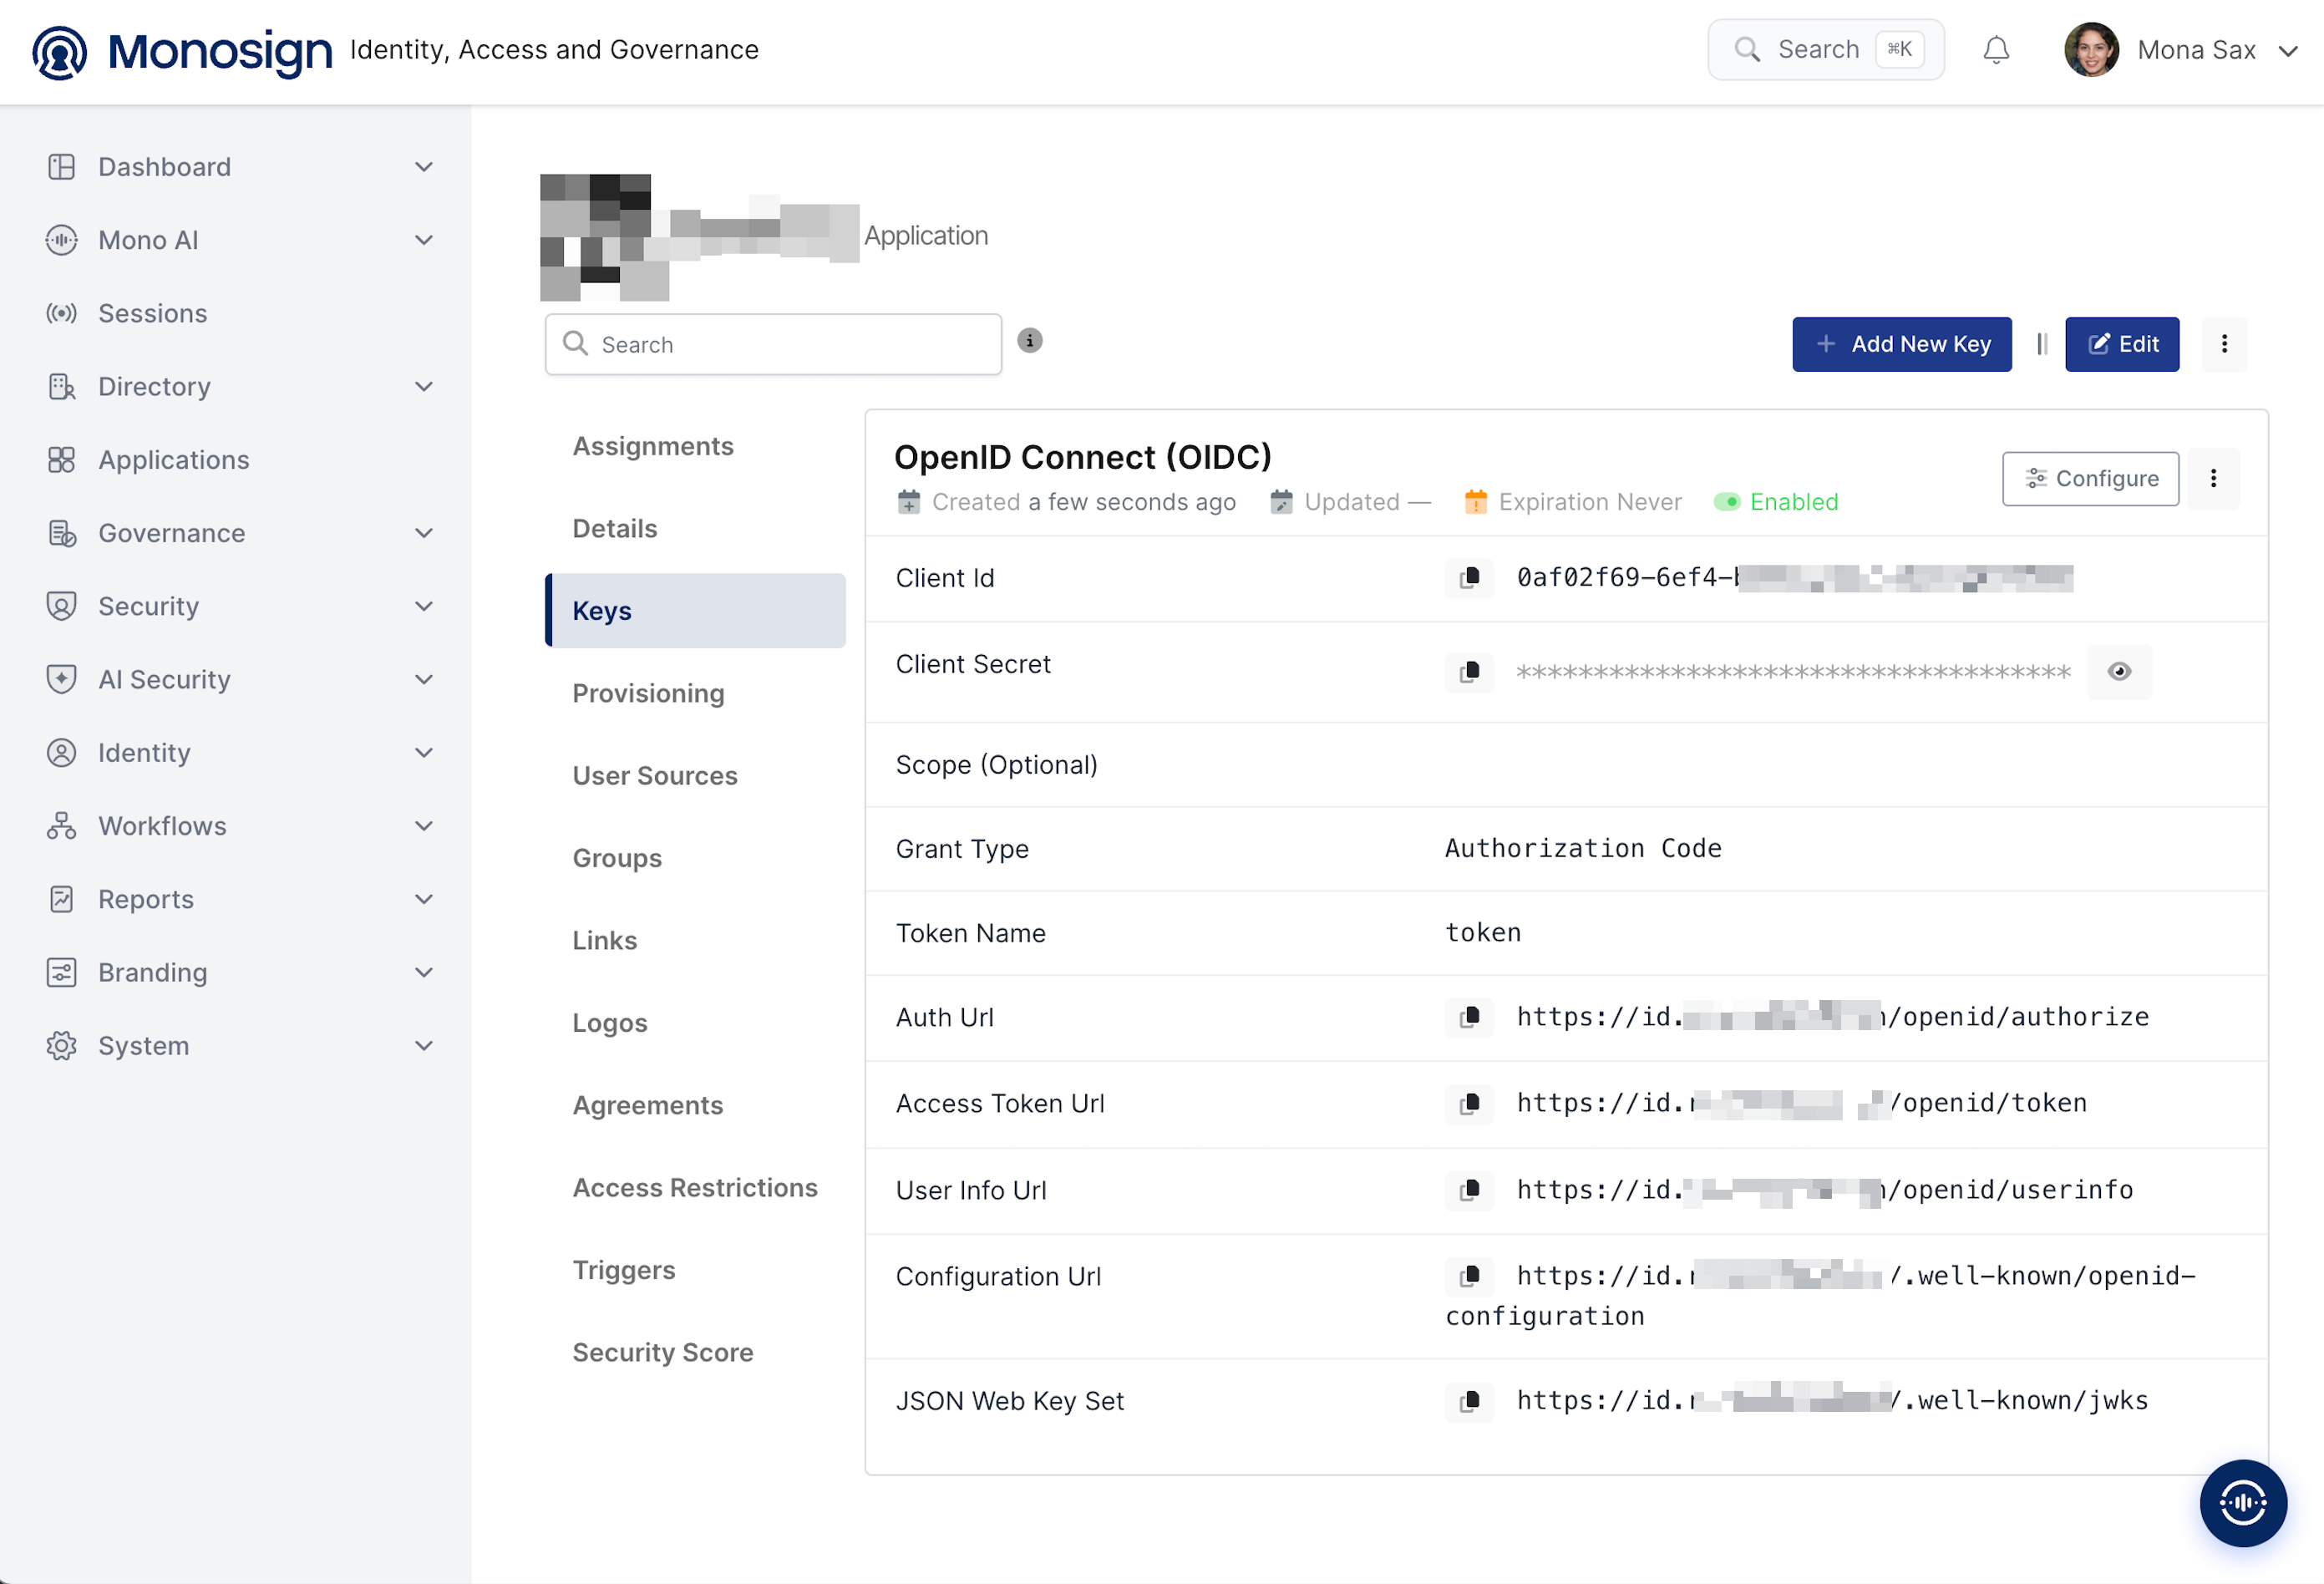
Monosign value | Example | Used in Metabase as |
|---|---|---|
Client Id |
| Client ID |
Client Secret |
| Client Secret |
Configuration Url |
| Issuer URI (enter |
2- Configuring the OIDC/OpenID Settings on Monosign
Click the Configure button of the OIDC/OpenID key. Enter the scopes that Metabase requests and add the callback address of Metabase to Allowed Redirect URIs, then press Update.
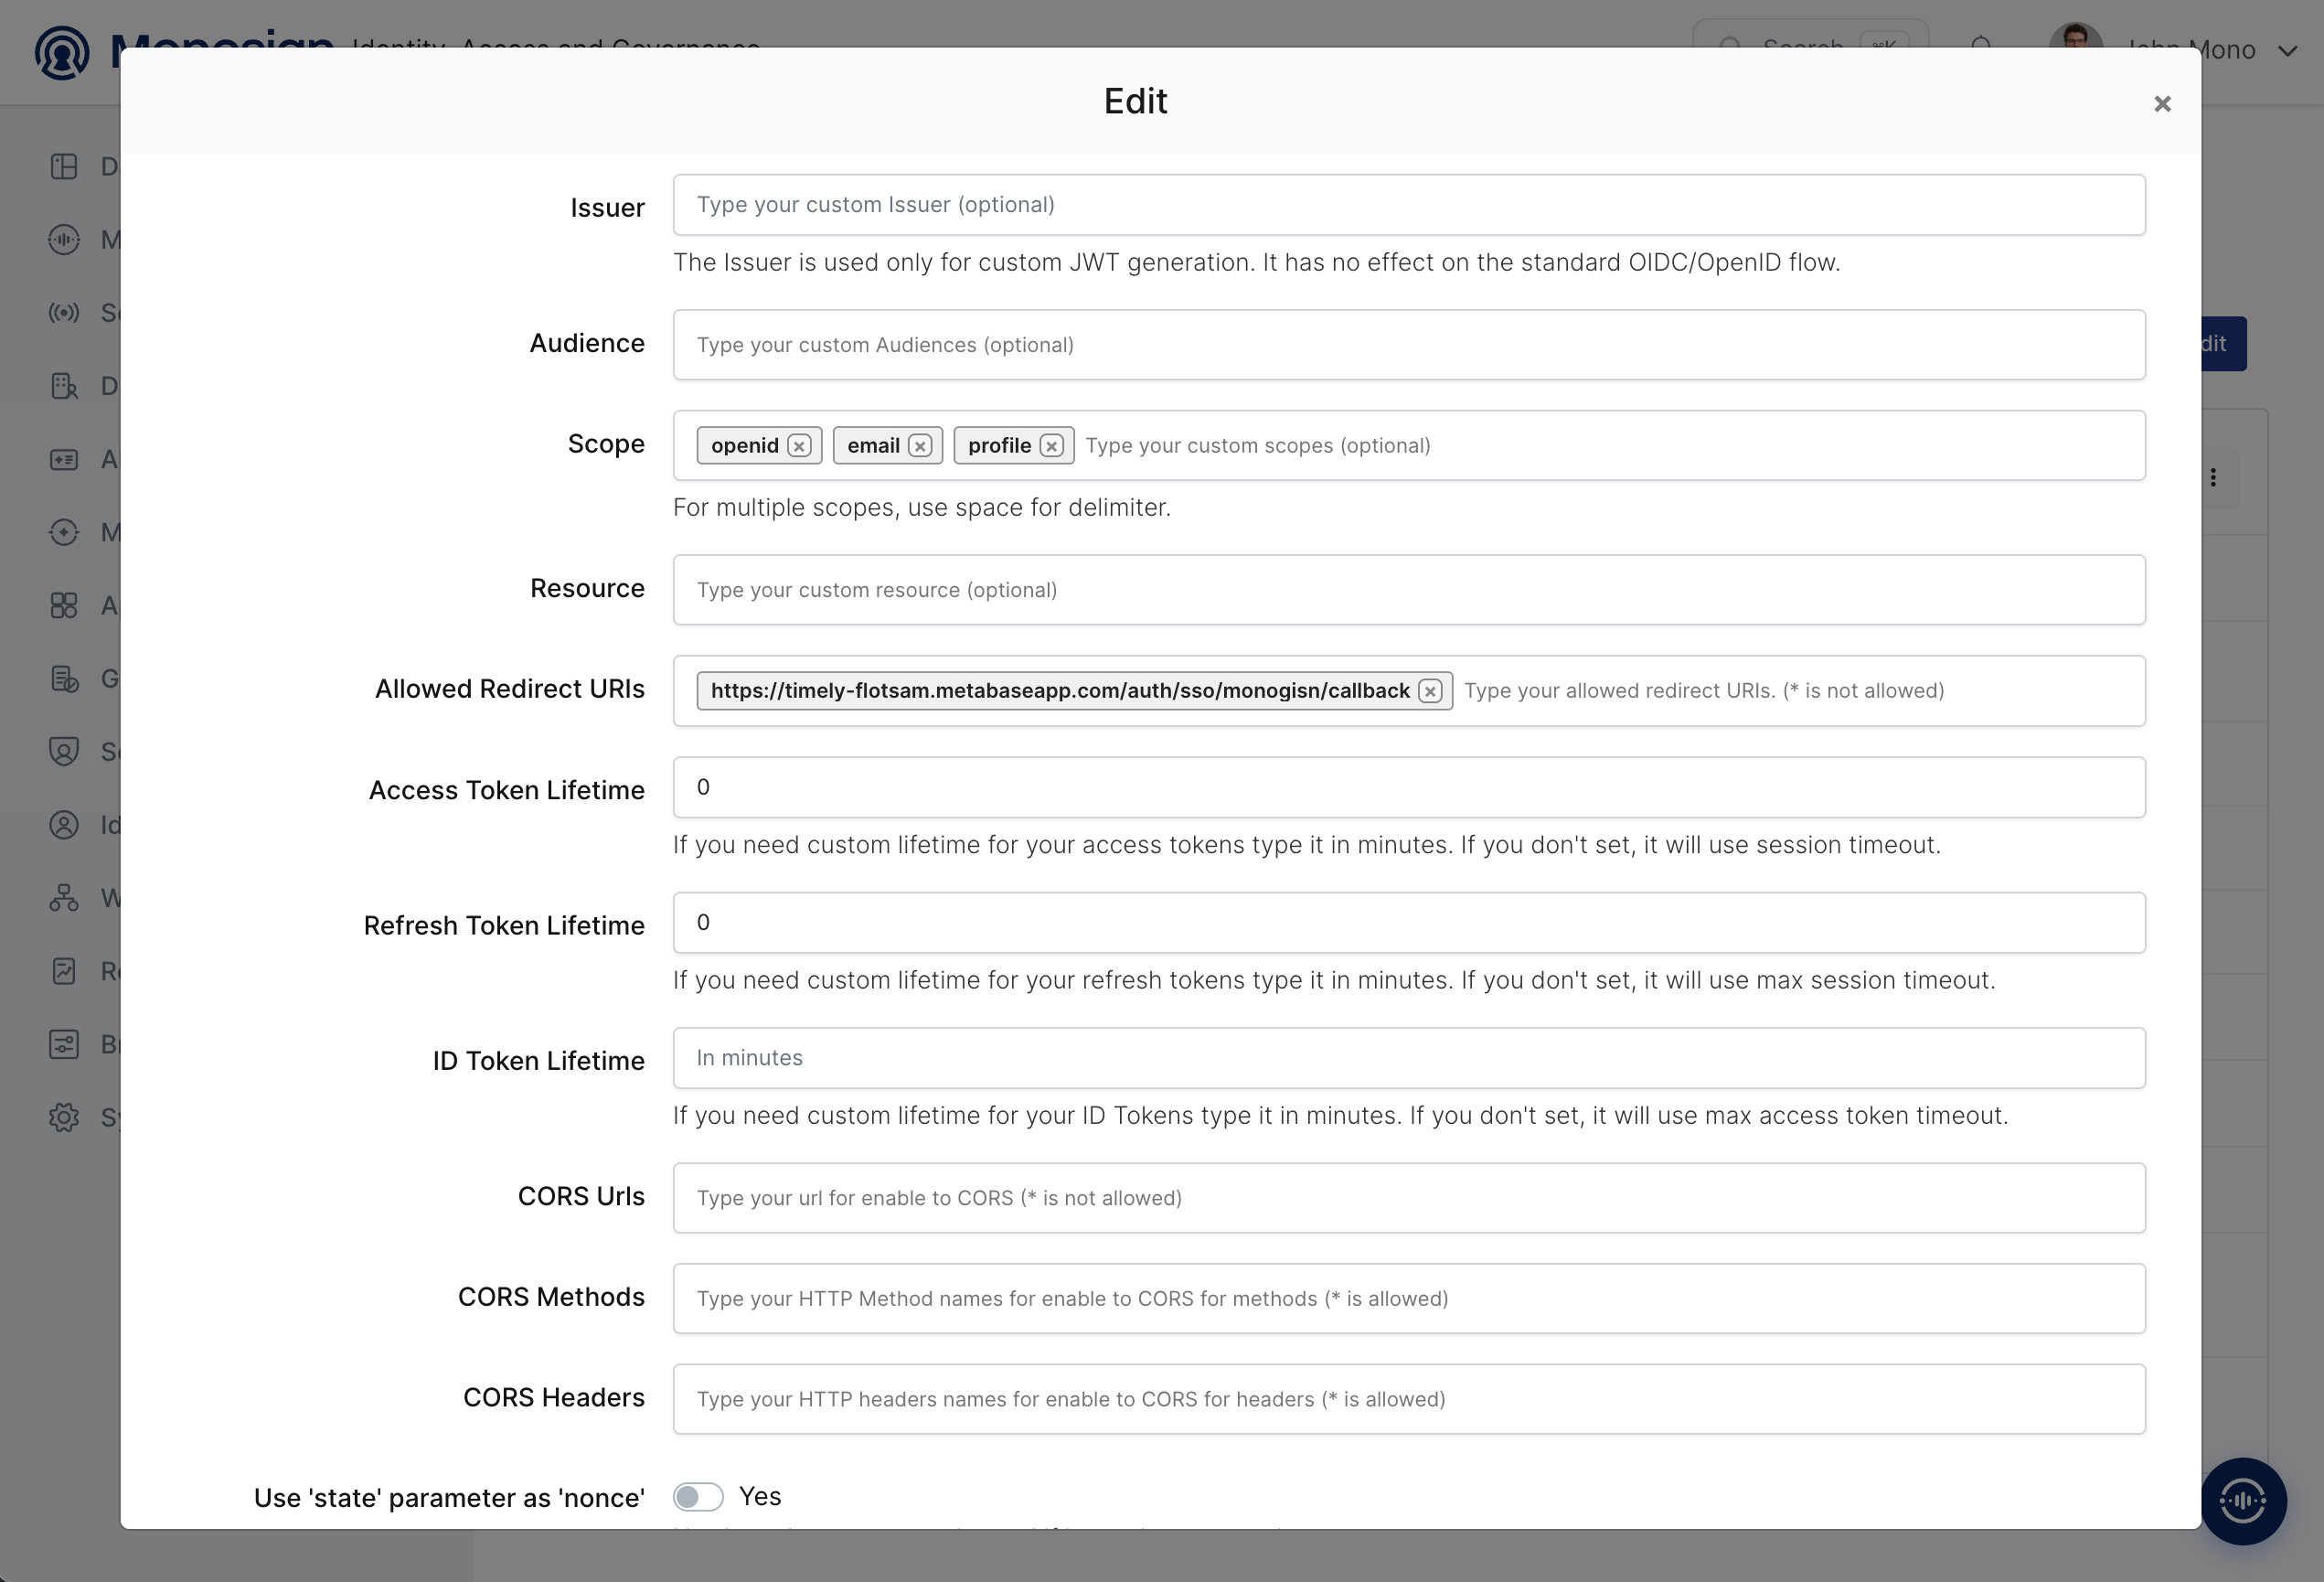
Property | Value | Description |
|---|---|---|
Scope |
| The scopes that Metabase sends in the authorization request. Add each scope separated by space. |
Allowed Redirect URIs |
| The address where Monosign sends the user back after sign-in. Metabase builds it as |
Signing Key / Issuer / Audience / Resource | Empty | Optional custom JWT settings. They are not needed. |
Metabase reads the user with the standard OIDC claims email, given_name and family_name. Monosign returns email and name by default, so open the Claim Mapping tab, add the first and last name claims and press Update.
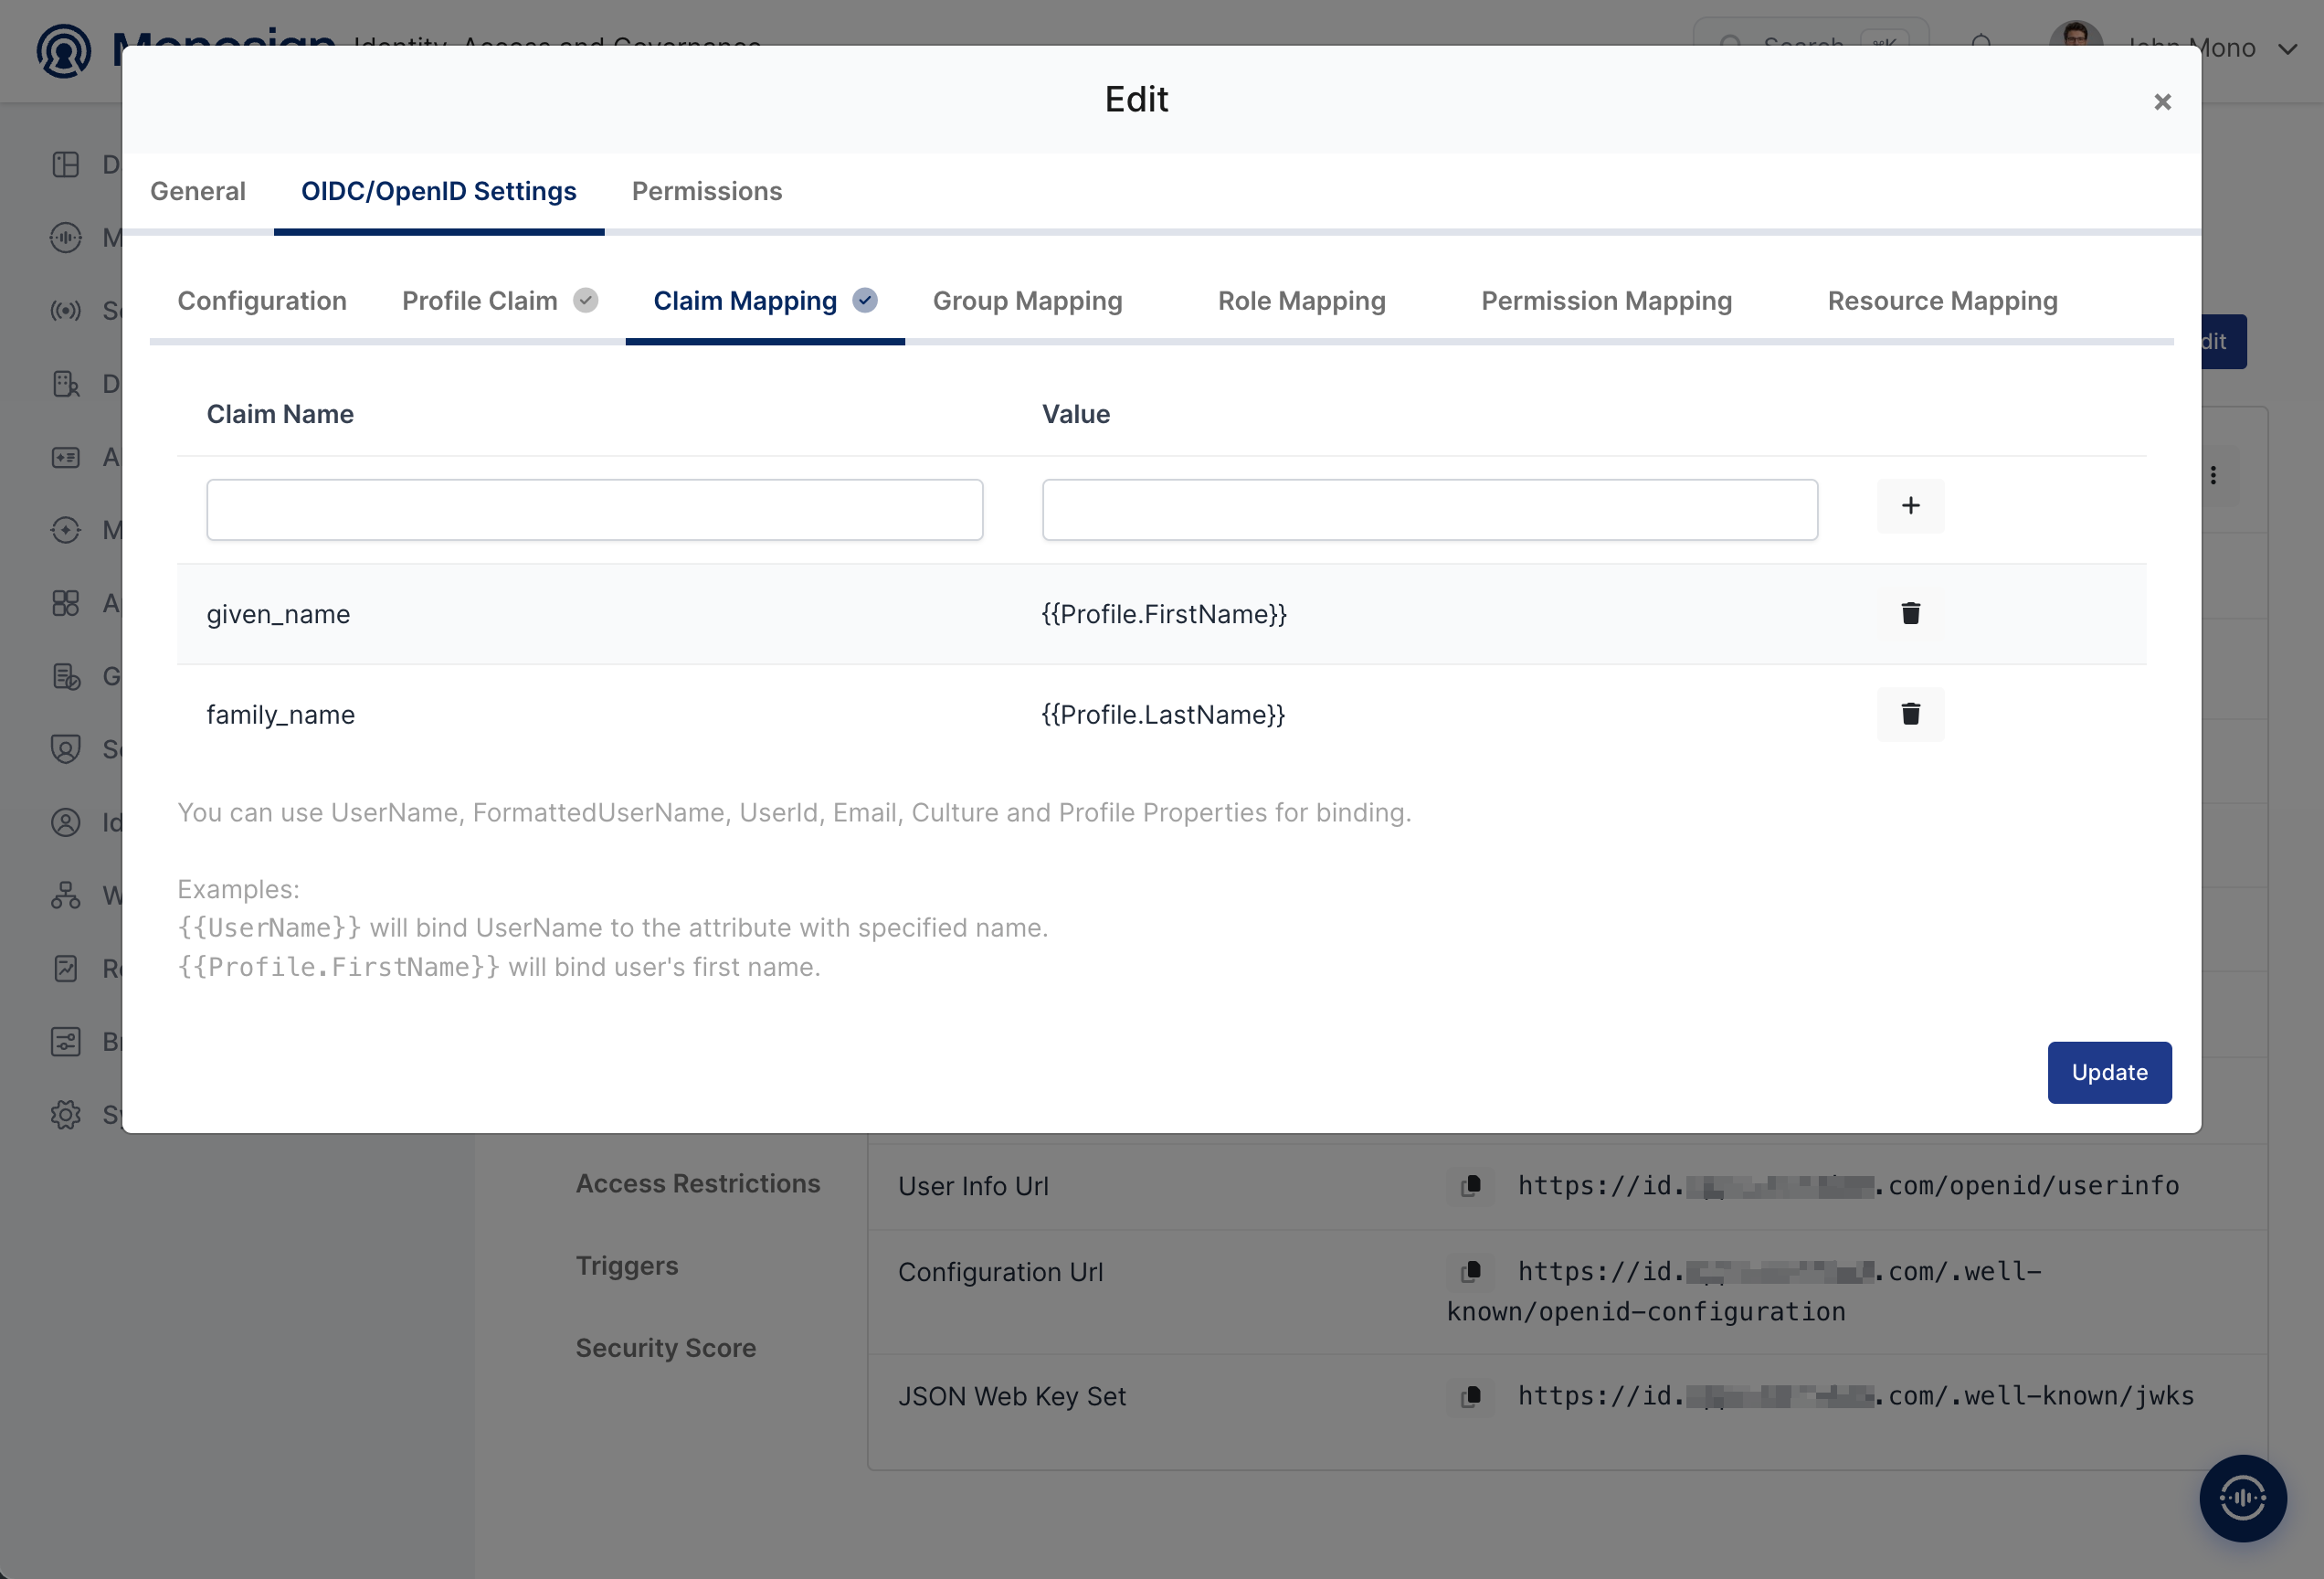
Claim | Value | Description |
|---|---|---|
|
| First name of the user. Metabase reads the first name from the |
|
| Last name of the user. Metabase reads the last name from the |
The email claim is returned by Monosign by default, so it does not need a Claim Mapping. Press Update after adding the claims. The {{...}} value templates read the fields from the Monosign user profile.
3- Assign a User to the Metabase Application
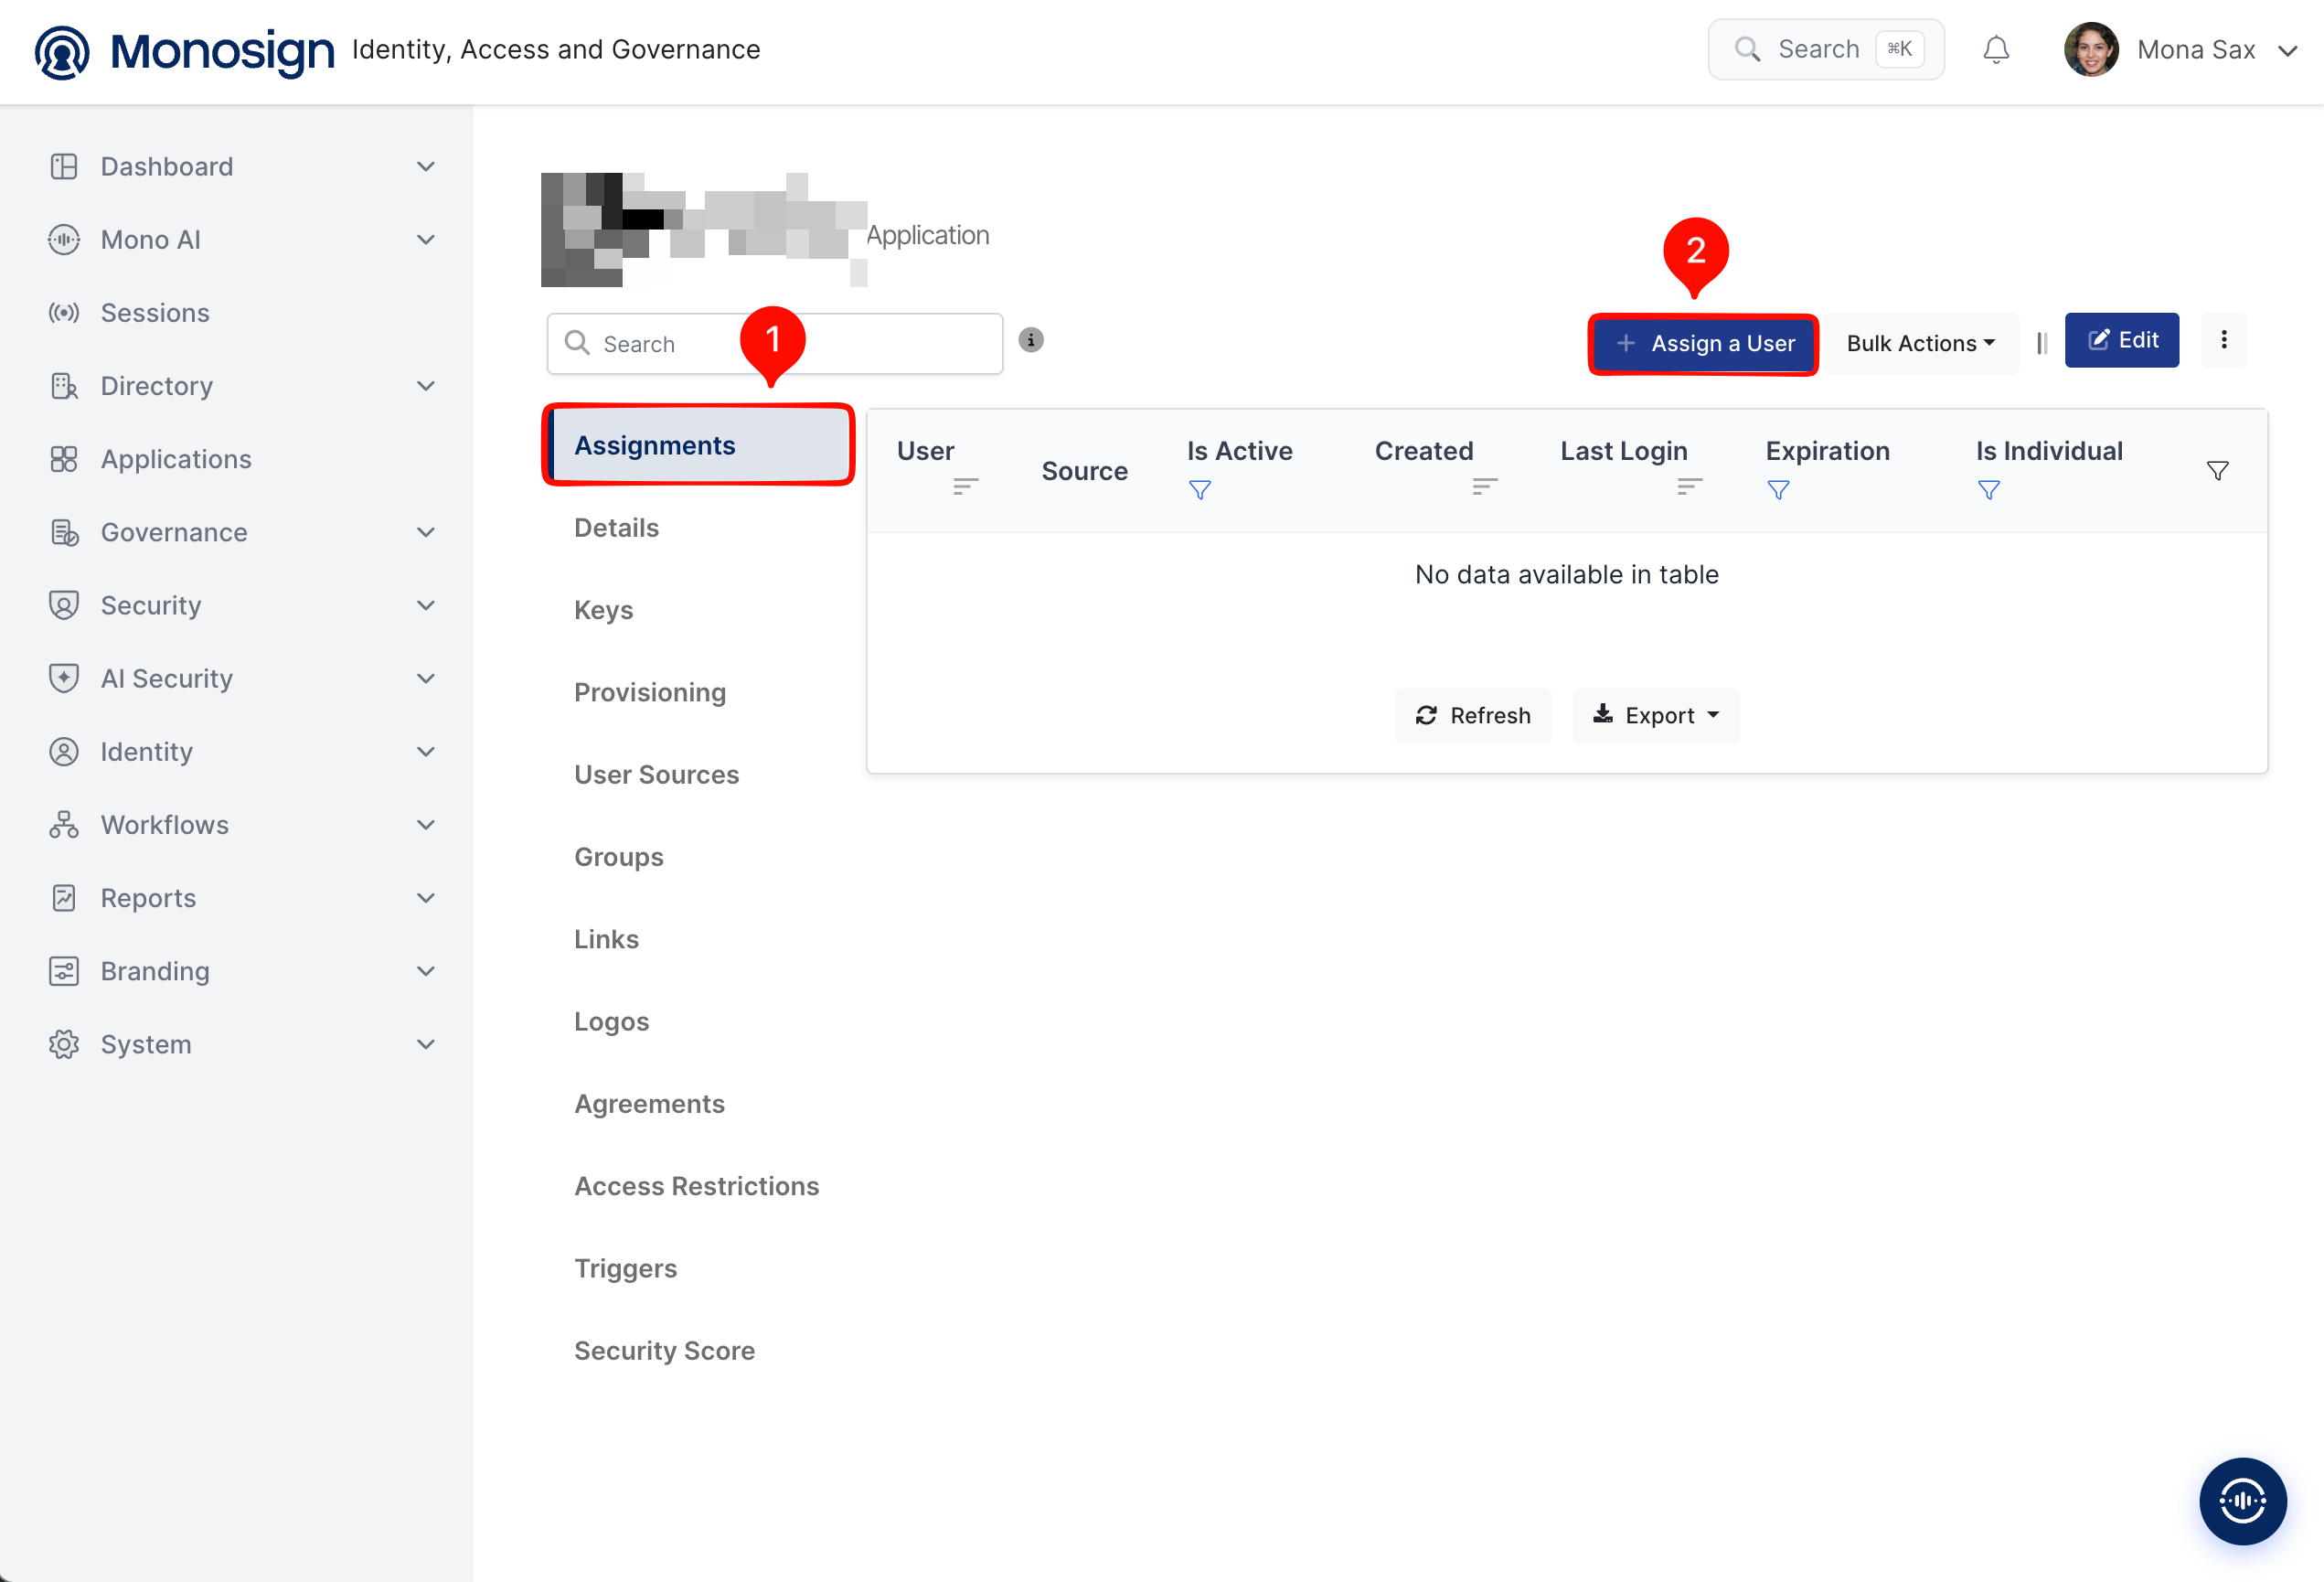
Please follow the below instructions on how to assign a user to the application. Open the application, click the Assignments tab and click Assign a User.
Search and select the users who can sign in to Metabase, check the Expiration Date and save. You can select more than one user.
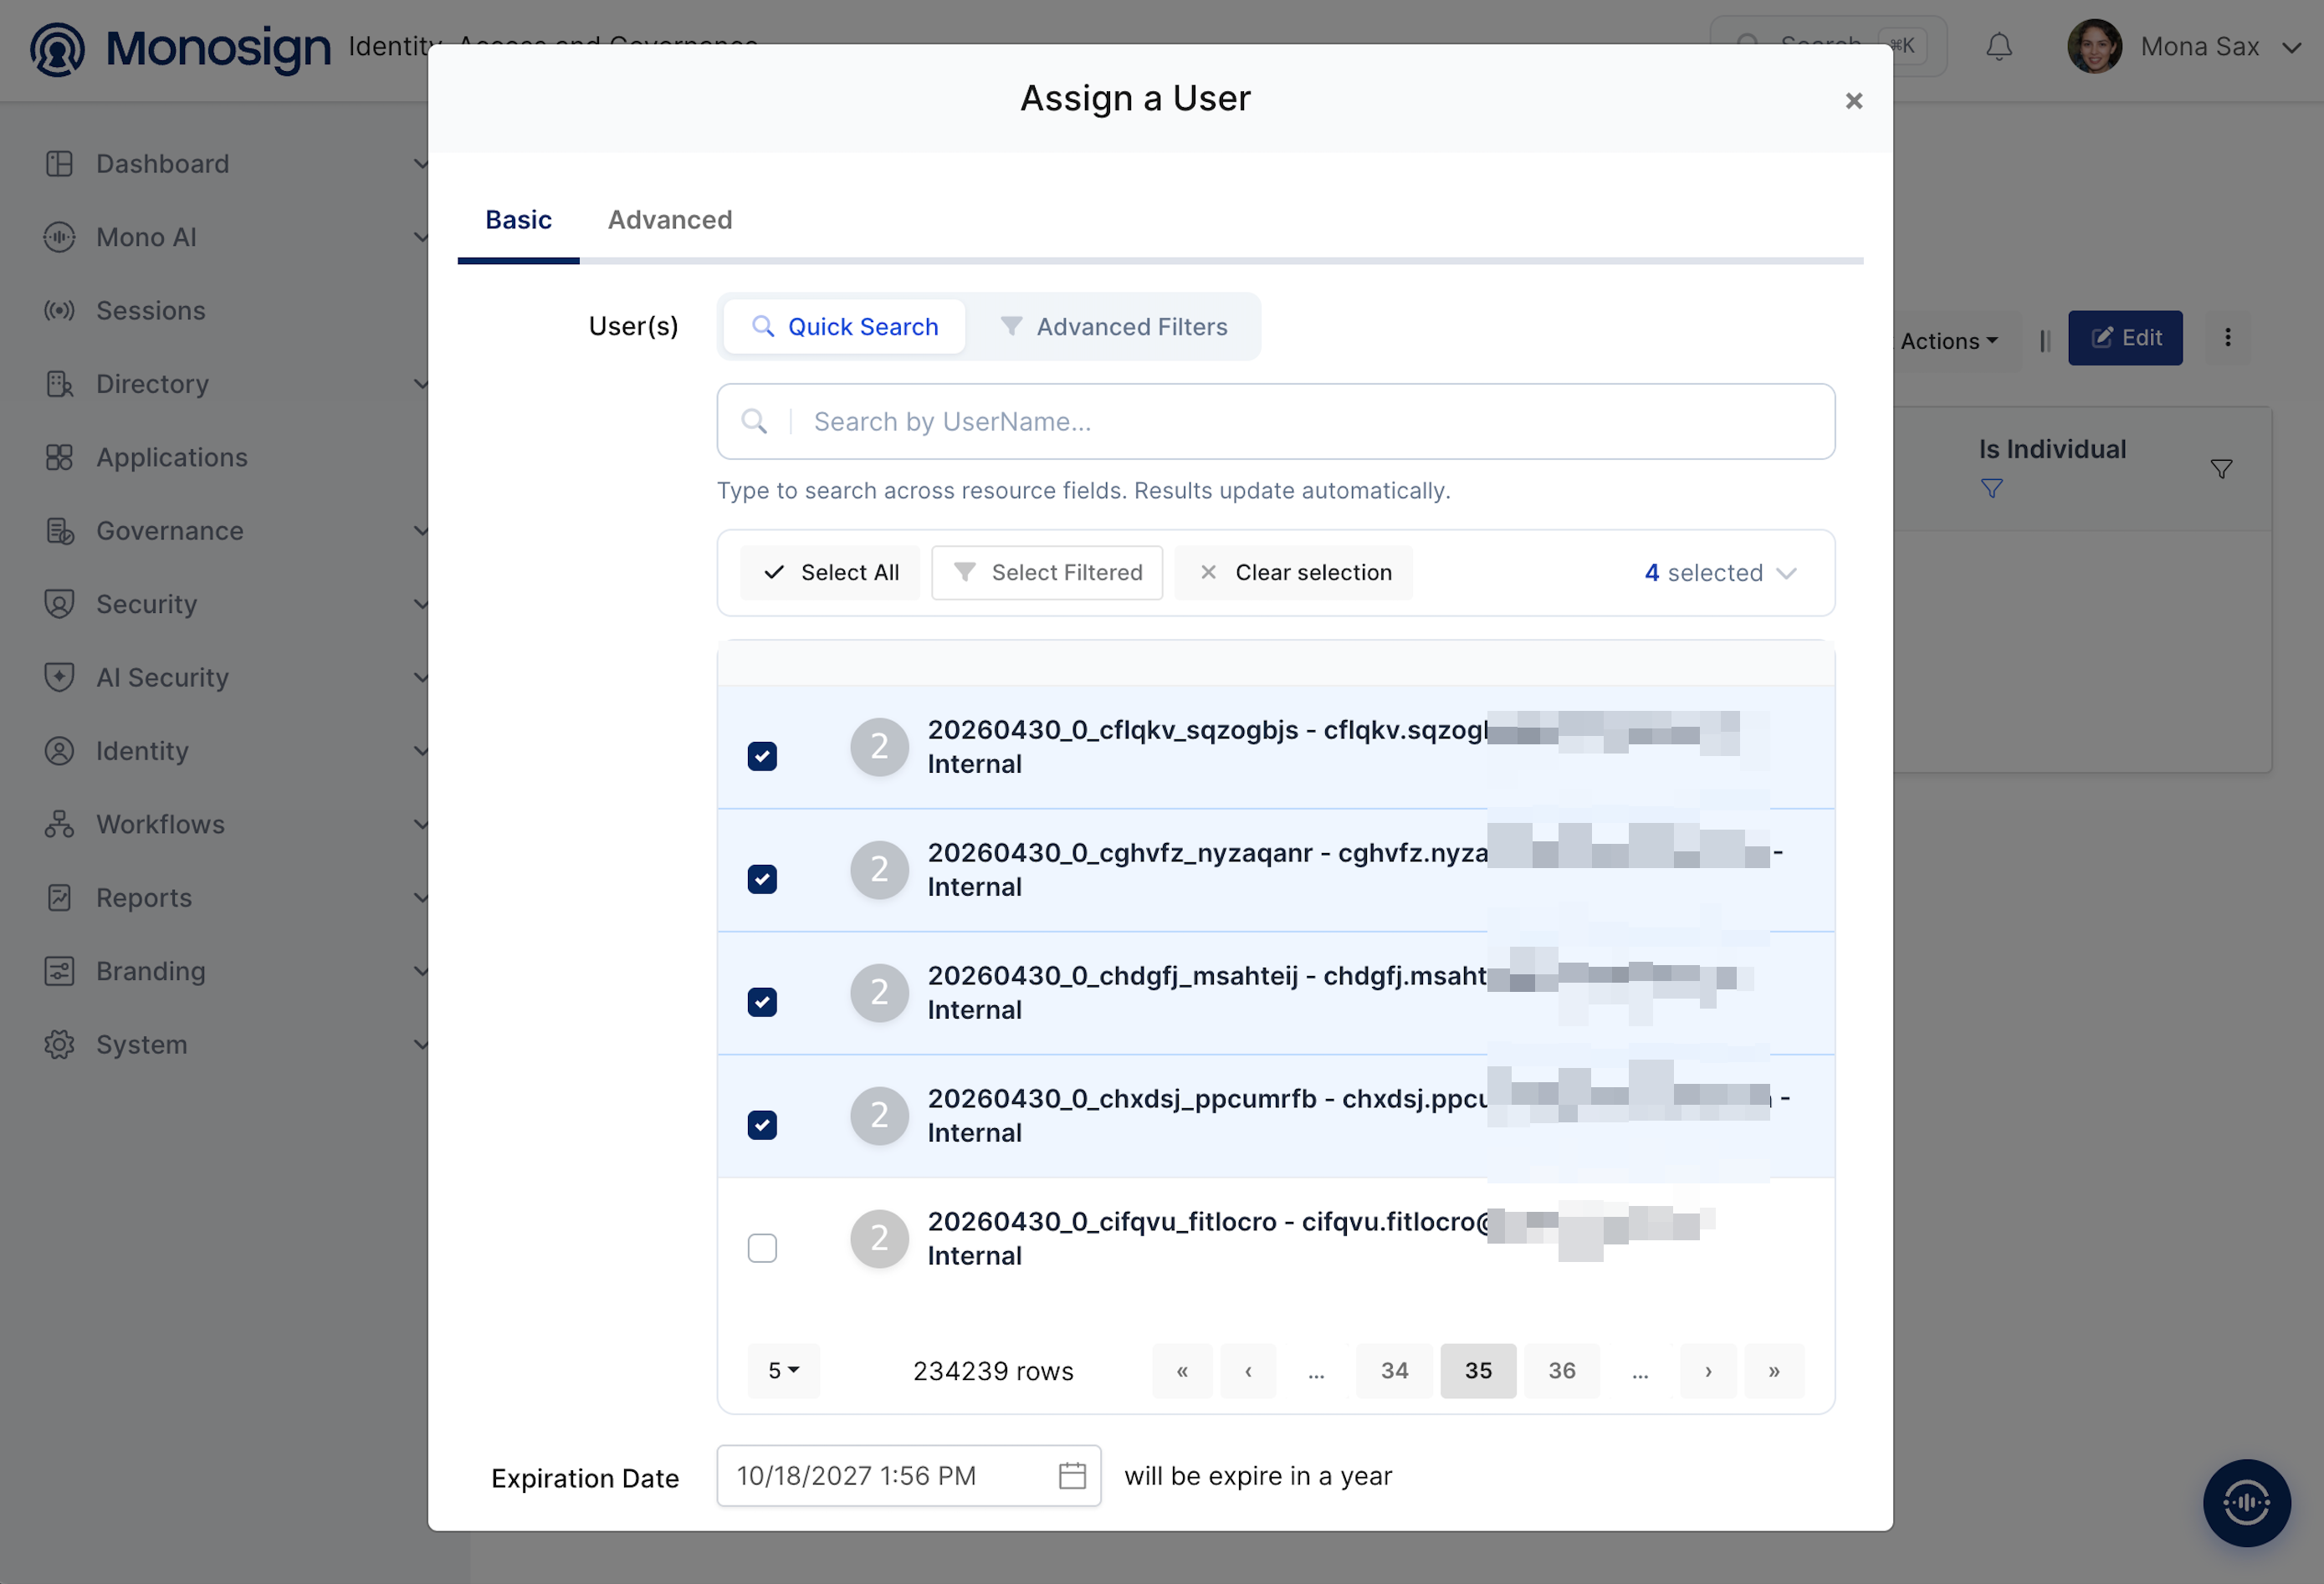
Property | Value | Description |
|---|---|---|
User(s) | Selected users | Users who can sign in to Metabase with Monosign. |
Expiration Date | Default one year | The assignment expires on this date. |
4- Configuration Single Sign-On for Metabase
As we mentioned at the start, please check out the Metabase documentation first. OIDC is an Enterprise / Pro feature, so a license token must be active. Open Admin → Settings → Authentication → OIDC and click Set up, then fill in the Monosign values.
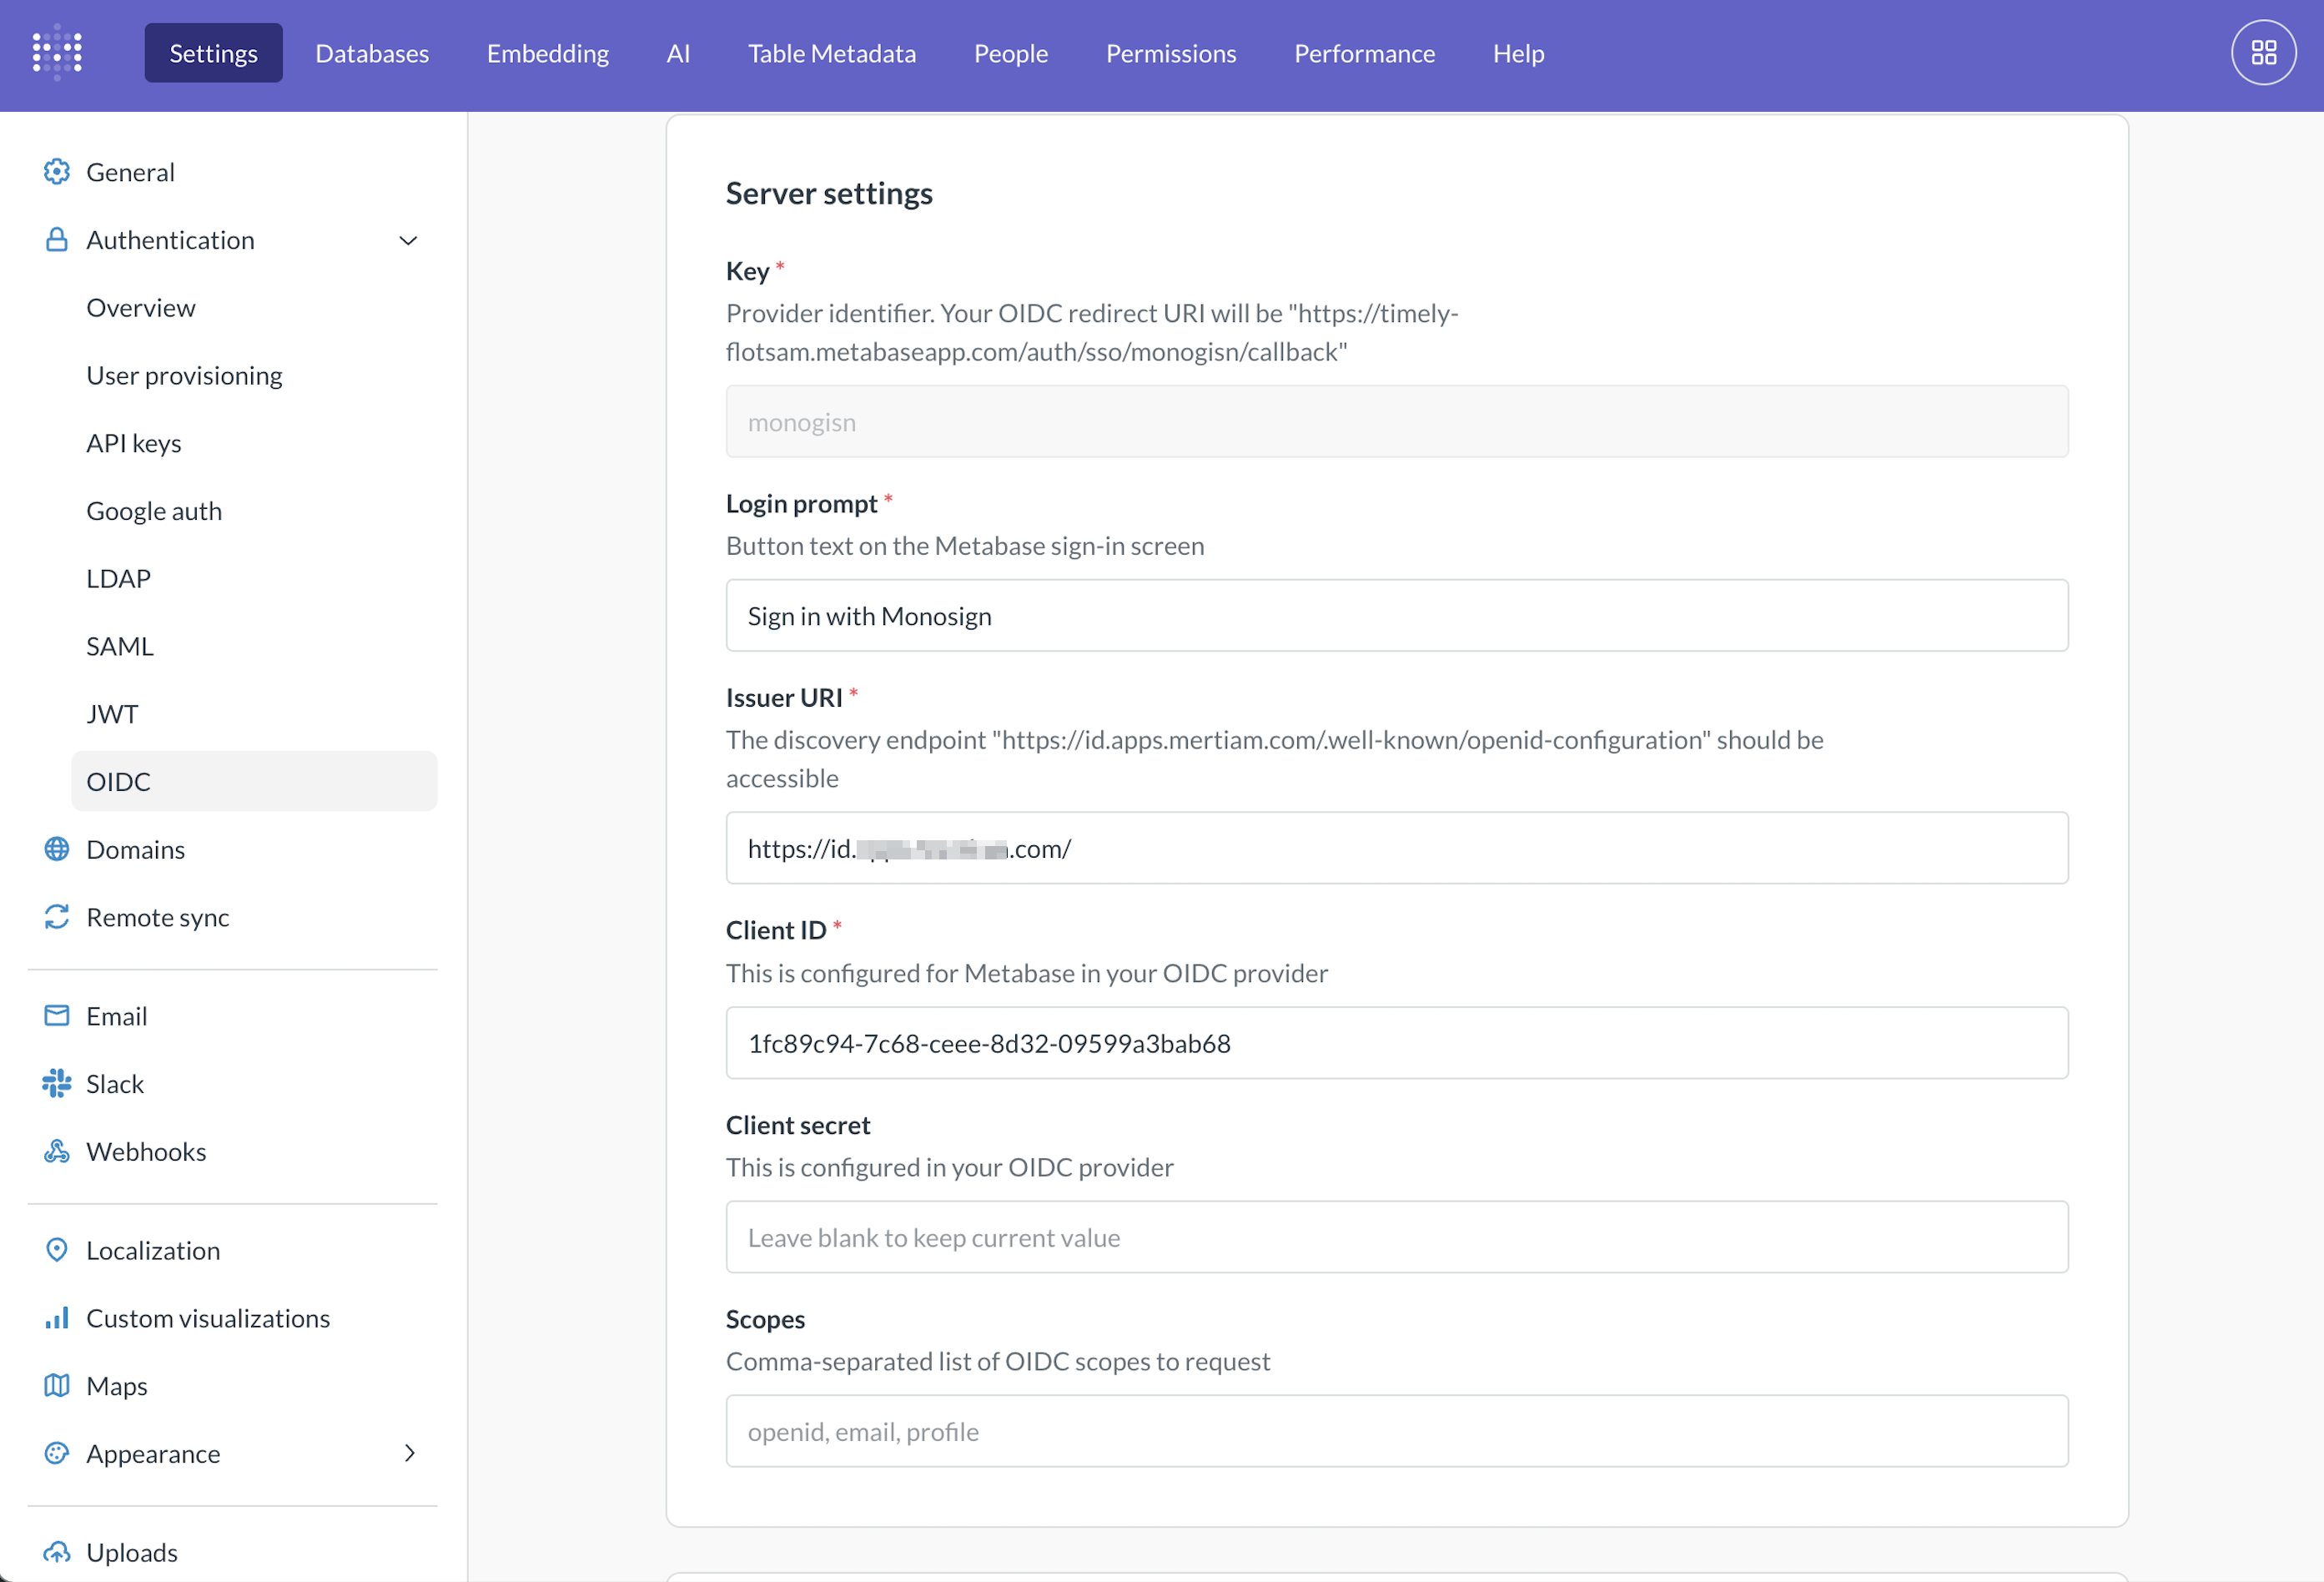
Metabase field | Value | Description |
|---|---|---|
Key |
| A unique identifier for this provider (lowercase letters, numbers and hyphens). It becomes part of the callback address |
Issuer URI |
| Metabase fetches the discovery document from |
Client ID |
| The Client Id of the Monosign OIDC/OpenID access key (step 1). |
Client Secret |
| The Client Secret of the Monosign OIDC/OpenID access key (step 1). |
Login prompt |
| The label of the button on the Metabase sign-in screen. |
Scopes |
| Default. Most providers do not need a change here. |
The default claim mapping of Metabase reads email, given_name (first name) and family_name (last name), which matches the Monosign claims from step 2, so no change is needed. Save the settings and make sure OIDC authentication is enabled.
Metabase creates the user on the first OIDC sign-in (just-in-time provisioning) and matches an existing user by e-mail address. Mapping Monosign groups to Metabase groups is optional and is done with the Synchronize group memberships option and the groups attribute; it is not required for sign-in.
Keep an administrator account that can still sign in with e-mail and password, and do not close your own session before the sign-in test is successful. If the single sign-on fails, you can still sign in at https://<metabase-host>/auth/login with the local password.
5- Sign In Test
Now try to log in to Metabase using Monosign SSO.
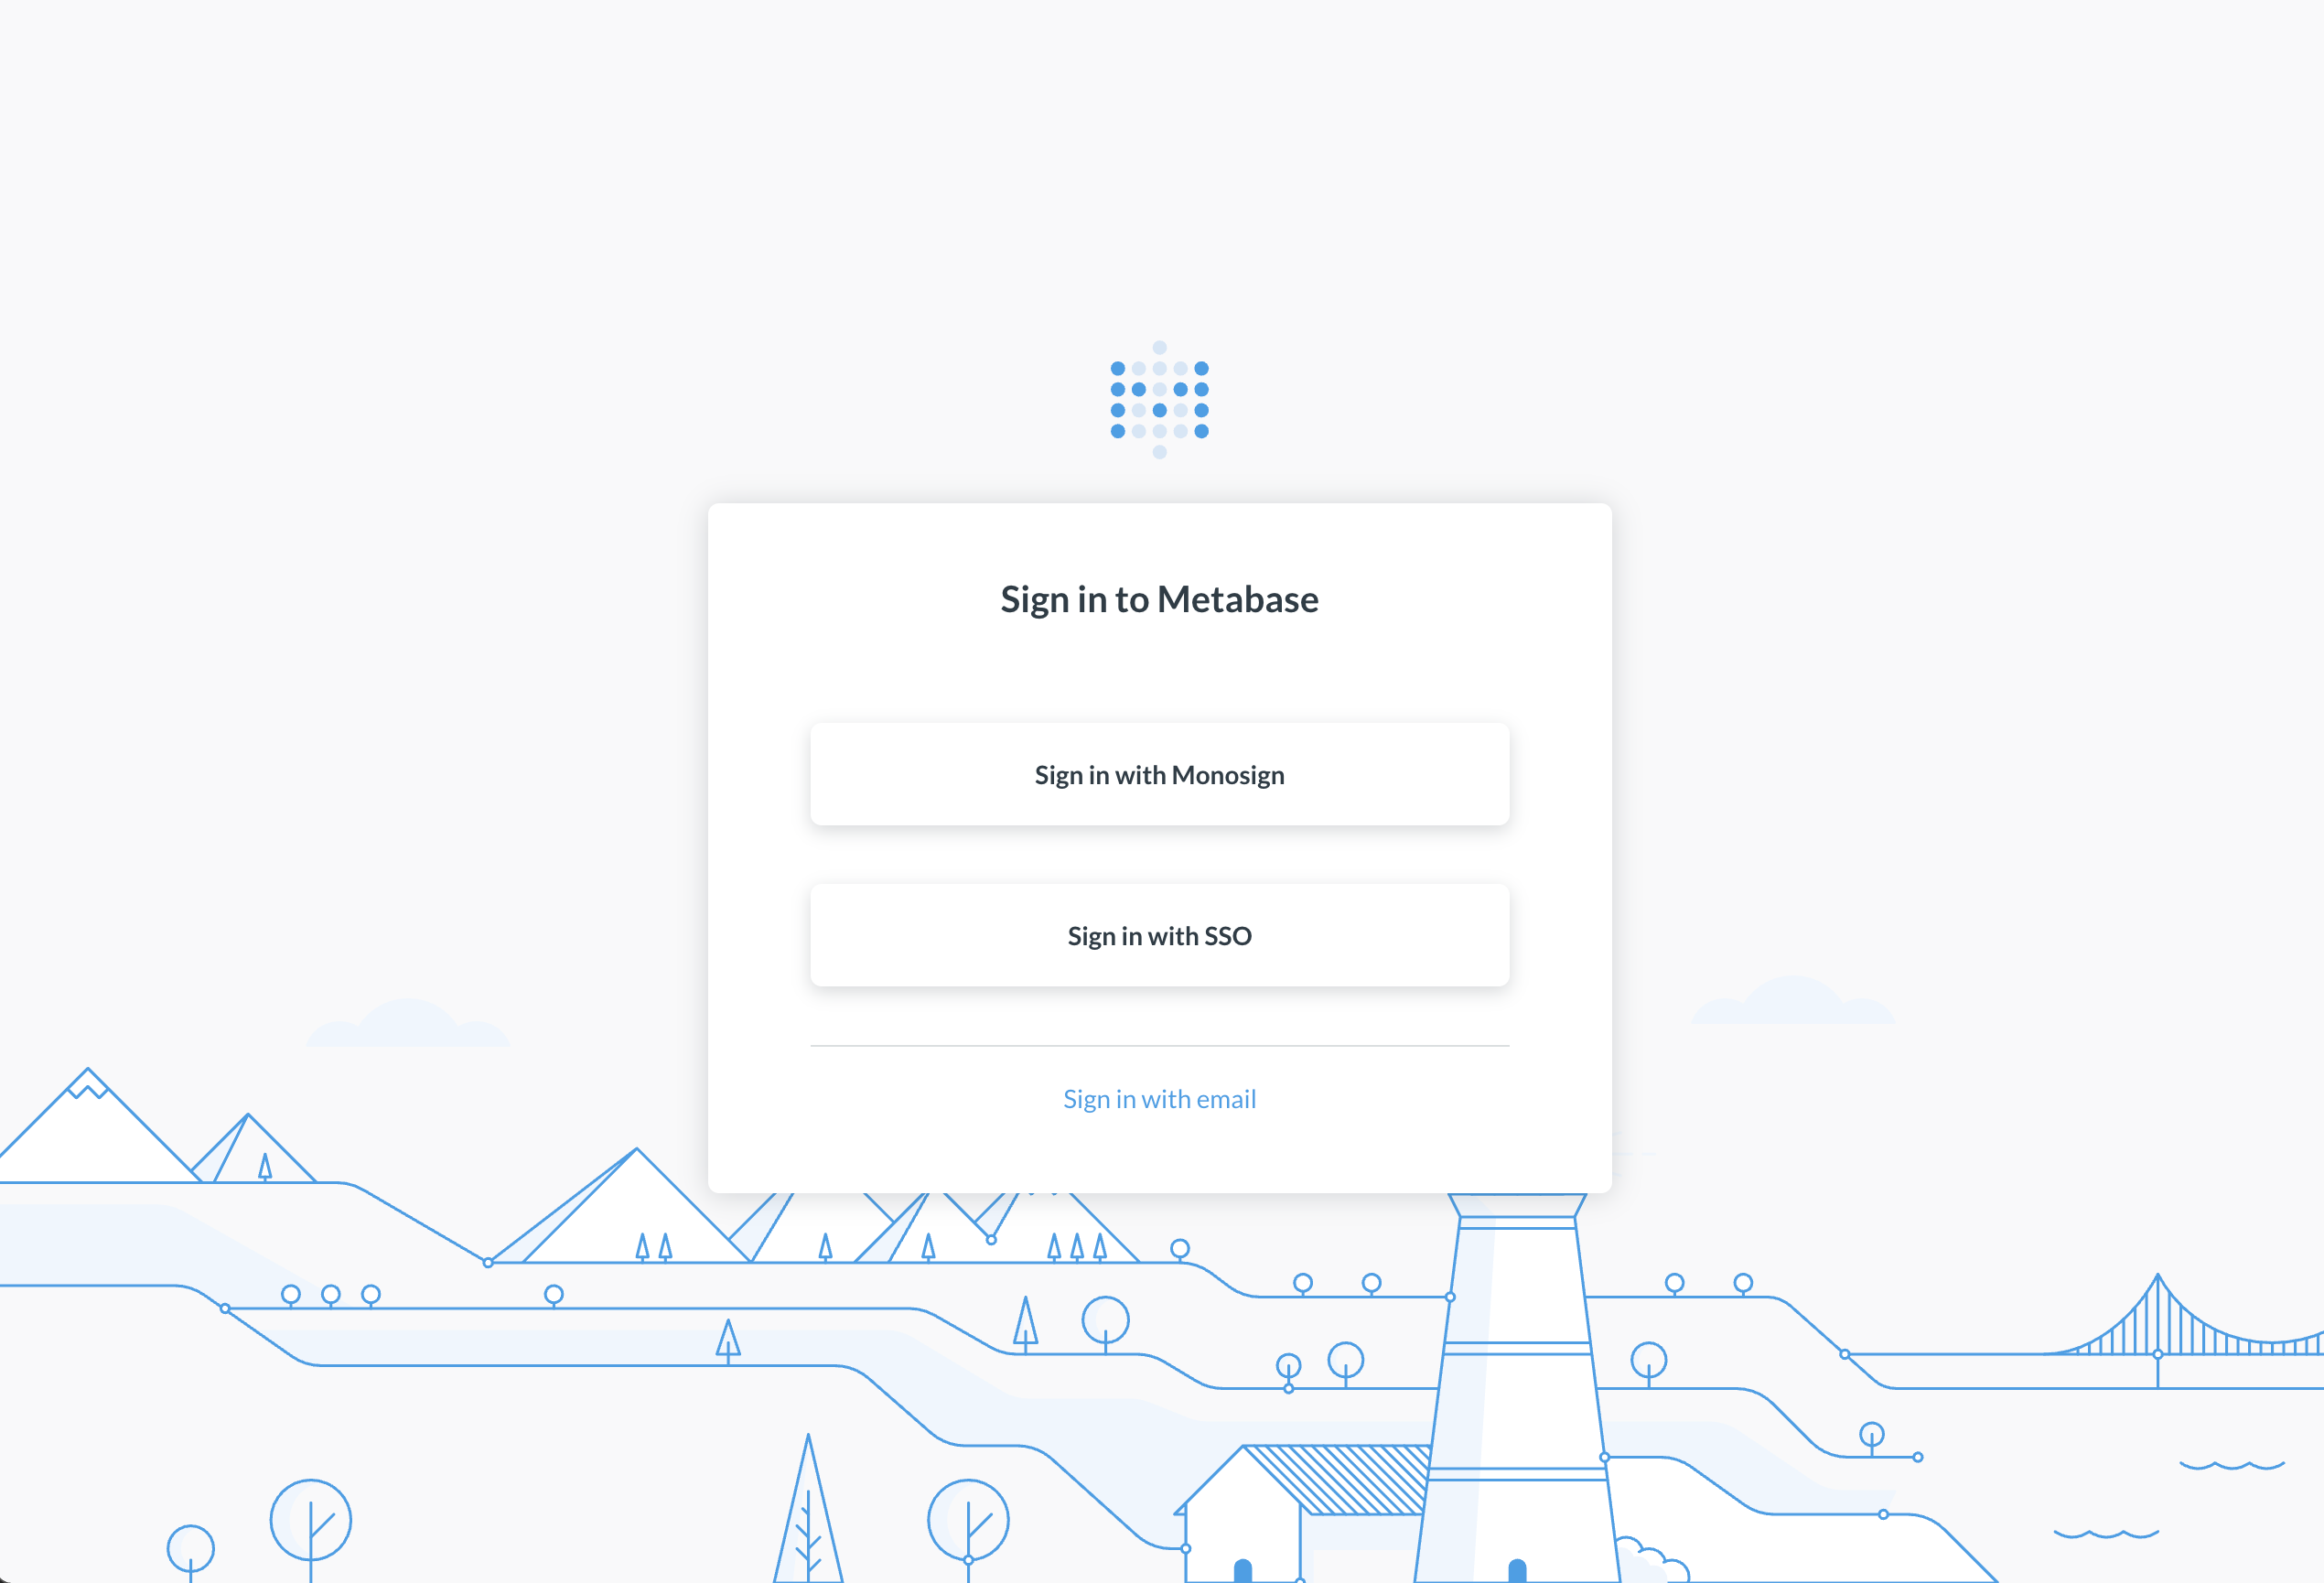
Open a new browser window (or a private window) and type the Metabase address, for example
https://<metabase-host>. The login page shows the Sign in with Monosign button (the Login prompt from step 4) and the local e-mail and password login.Click Sign in with Monosign. Metabase redirects the browser to the Monosign sign-in page of the application. You can log in passwordless with your QR code (Monofor Identity), with a Passkey or with your user name and password (Sign in with Password). If you are already signed in to Monosign, the page is skipped.
After the sign-in Monosign redirects the browser back to Metabase (
/auth/sso/<key>/callback) and the user is logged in to Metabase.
Troubleshooting
Symptom | Cause | Solution |
|---|---|---|
The Sign in with Monosign button is not shown | The Enterprise / Pro license is not active, or OIDC authentication is not enabled. | Activate the license token (Admin → Settings → License) and enable OIDC (step 4). |
Monosign shows a redirect URI error | The callback address does not exactly match the Allowed Redirect URIs, for example because the Key or the Site URL is different. | Add |
Metabase cannot read the discovery document or reports an issuer mismatch | The Issuer URI is wrong, or Metabase cannot reach the Monosign discovery endpoint. | Check the discovery endpoint Metabase shows under the Issuer URI field ( |
The name of the user is empty or wrong | The | Add the Claim Mapping in step 2 and set Profile Access Type to All (step 1). |
A user cannot sign in | The user is not assigned to the application. | Assign the user in step 3. |
OIDC cannot be enabled on a self-hosted instance |
| Set |
After completing the configuration on Metabase and Monosign, it is better to test in a new private browser window if the OIDC SSO doesn’t work, because old session cookies may cause errors.